
 #1
Tools for identifying, assessing, and prioritizing security weaknesses in systems and applications.
Kitploit recommended
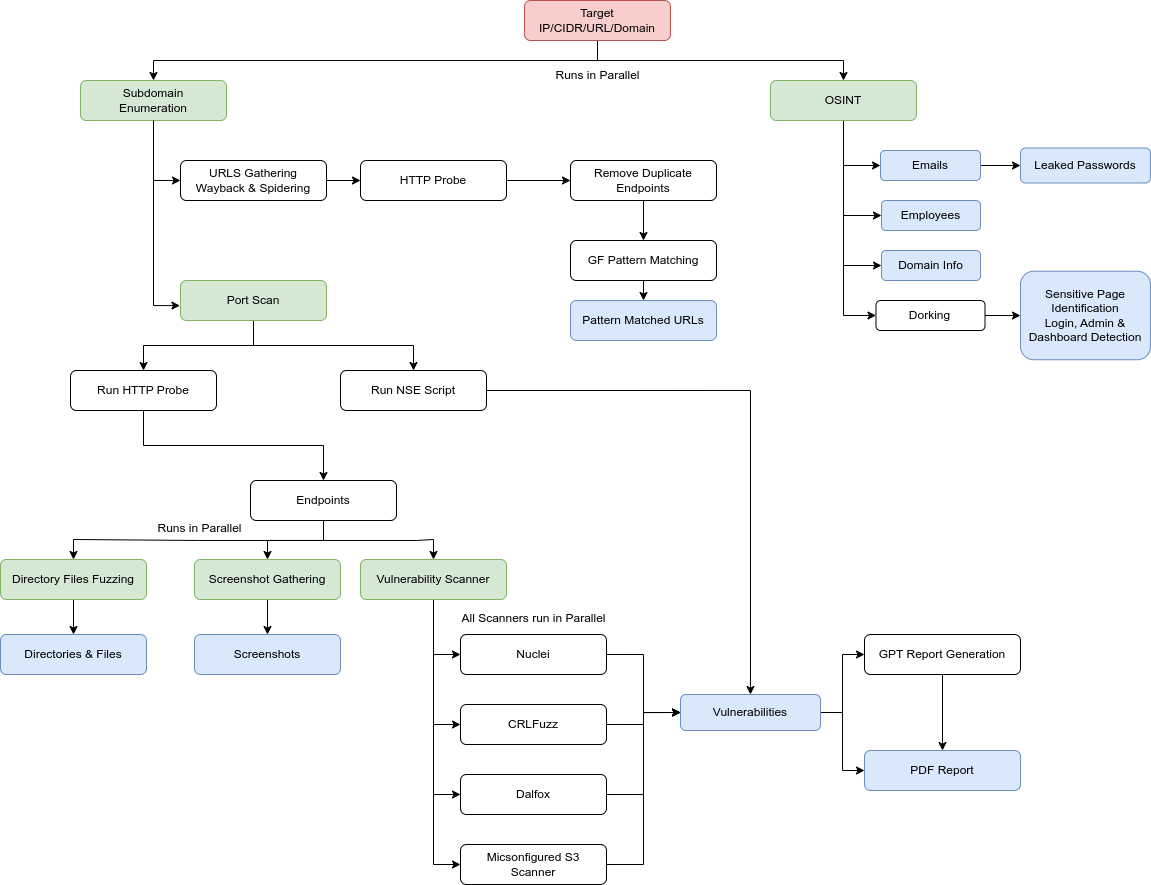
 yogeshojha/rengine
reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
 owasp/asvs
Application Security Verification Standard
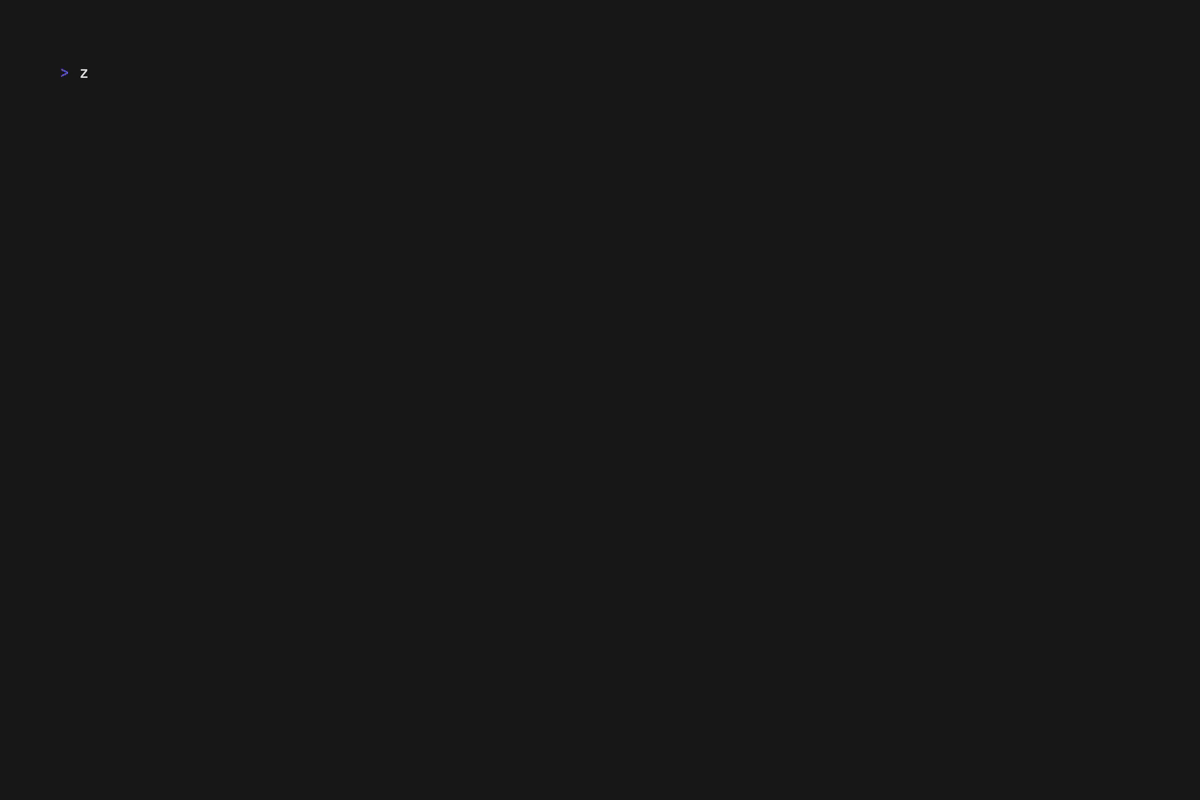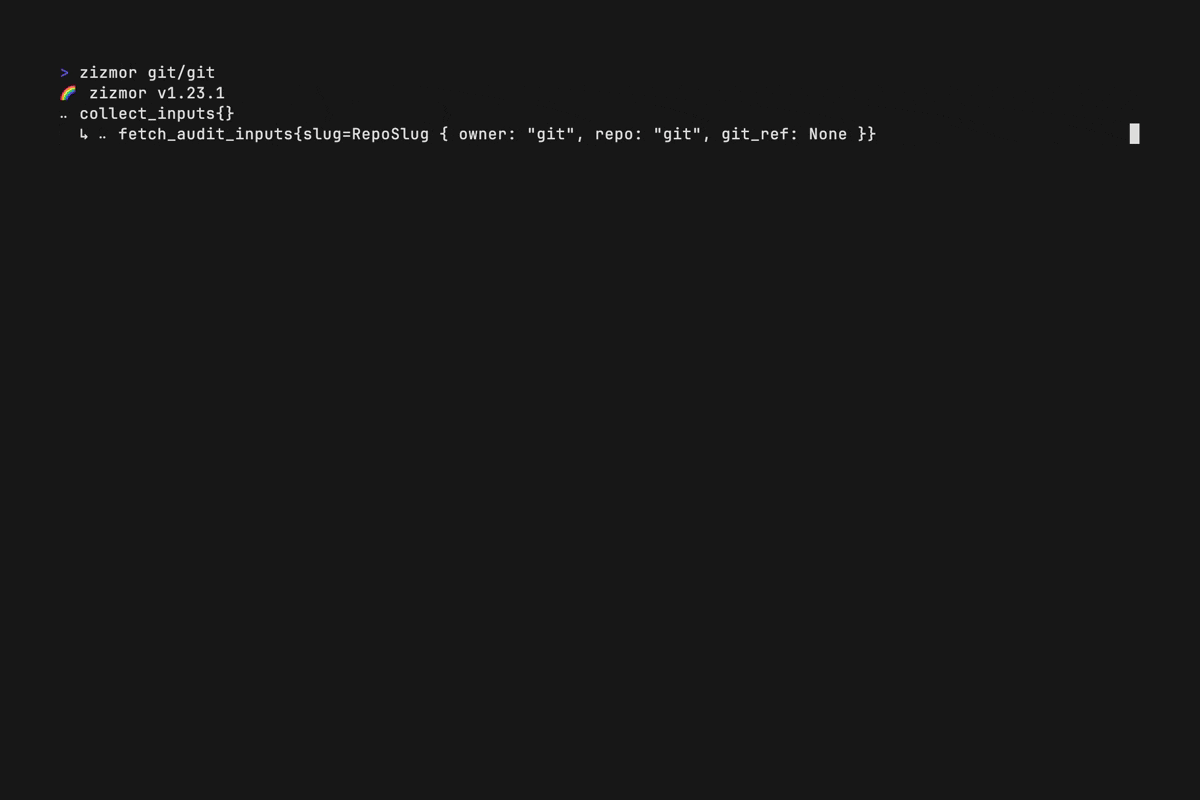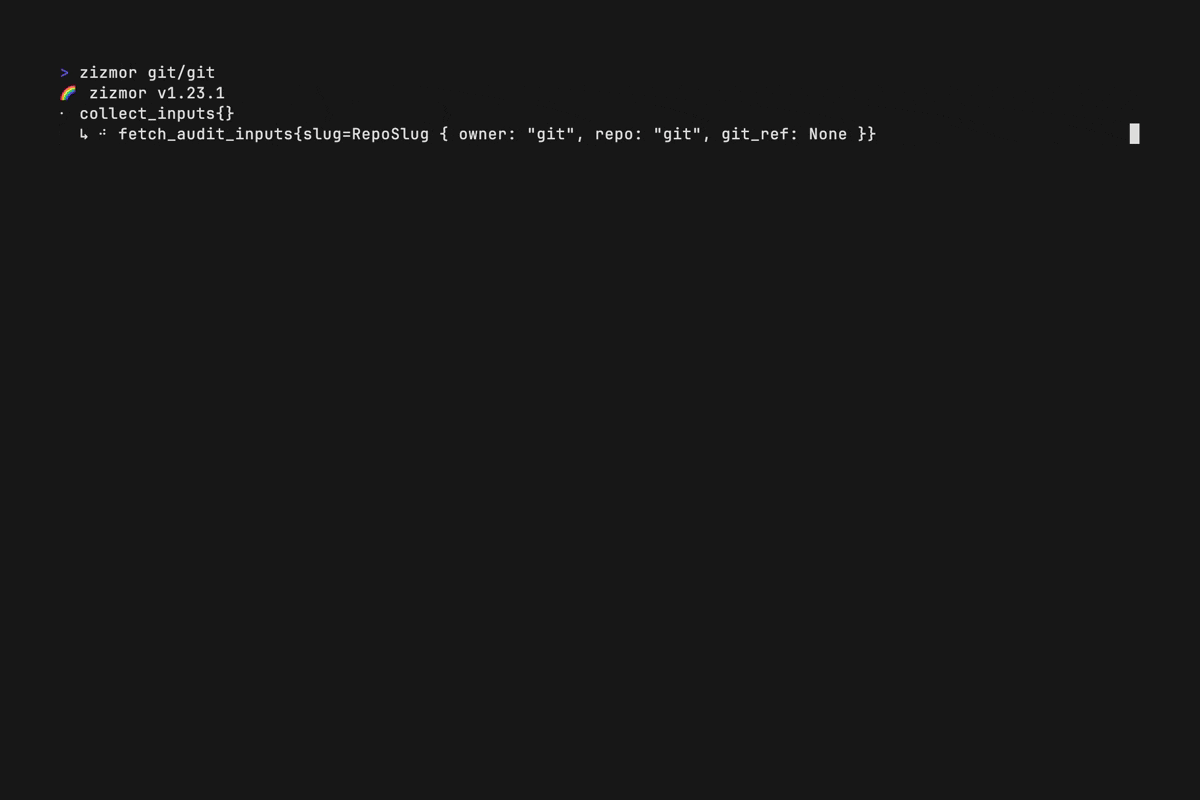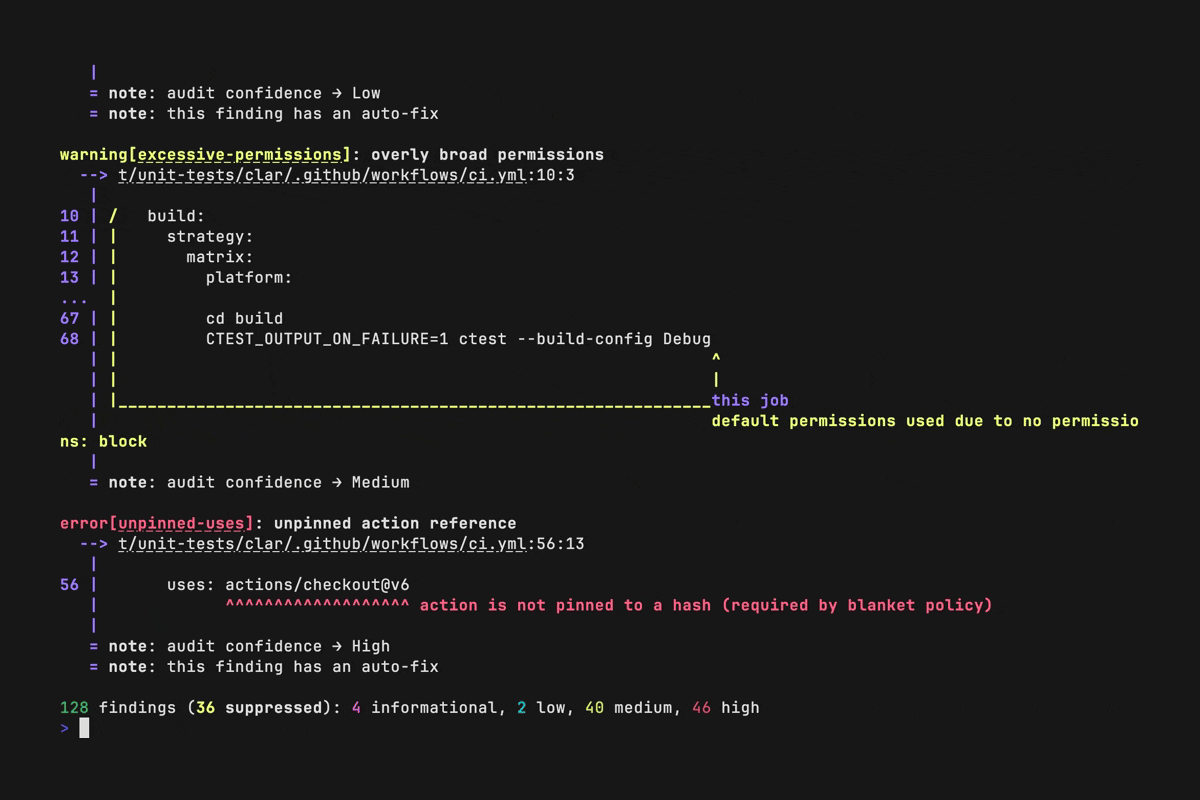 zizmorcore/zizmor
Static analysis tool for CI/CD systems that detects and fixes security issues in GitHub Actions, Dependabot, and pre-commit configurations, including…
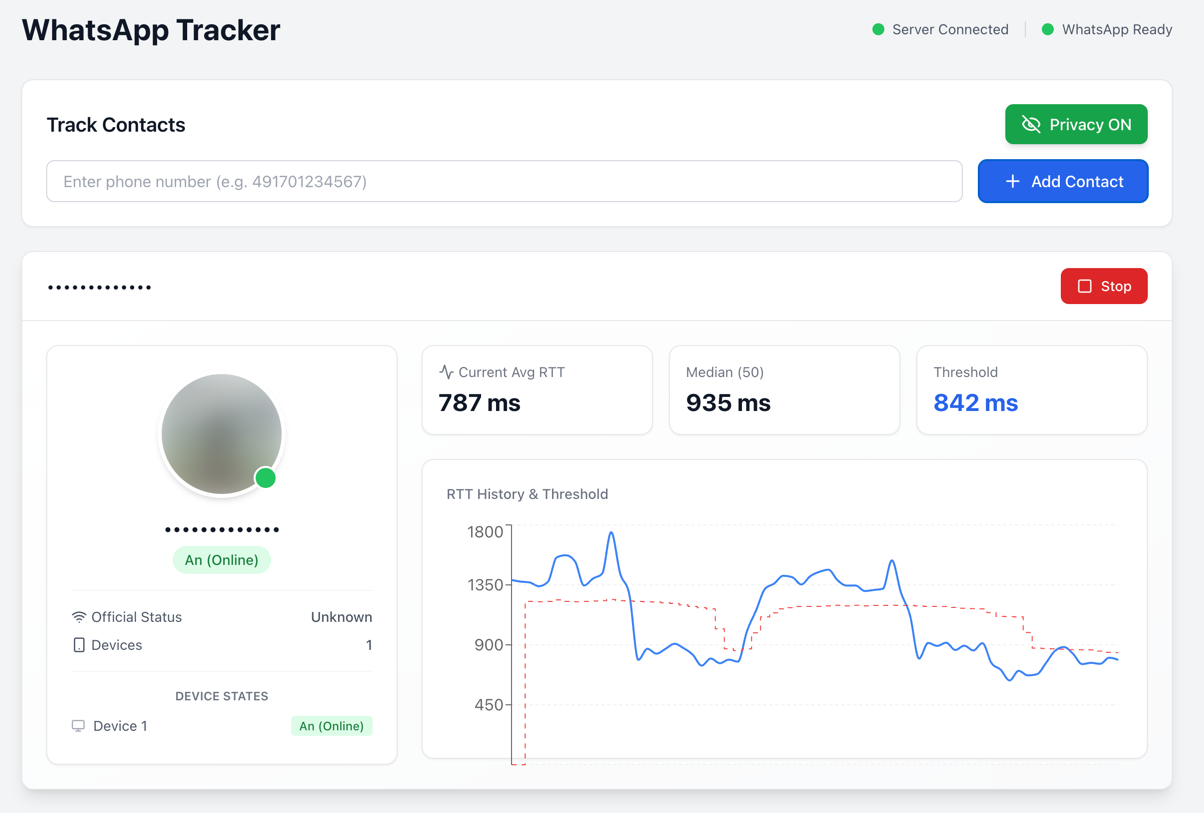 gommzystudio/device-activity-tracker
A phone number can reveal whether a device is active, in standby or offline (and more). This PoC demonstrates how delivery receipts + RTT timing leak…
 ljagiello/ctf-skills
Agent skills for solving CTF challenges - web exploitation, binary pwn, crypto, reverse engineering, forensics, OSINT, and more
 elementalsouls/claude-bughunter
A Claude Code skill bundle for bug hunting and external red-team work - 82 skills, 15 slash commands, 681 disclosed-report patterns curated across 24…
 microsoft/detours
Runtime Windows API interception library for hooking, monitoring, and instrumenting function calls. Supports binary rewriting and DLL injection,…
 anthropics/oss-scanner
Service that builds enrolled open-source repositories in isolated offline VMs and scans them for security vulnerabilities, emailing findings with…
 zan8in/afrog
A Security Tool for Bug Bounty, Pentest and Red Teaming.
 swisskyrepo/ssrfmap
Automatic SSRF fuzzer and exploitation tool
 gtworek/psbits
Simple (relatively) things allowing you to dig a bit deeper than usual.
 hahwul/dalfox
Fast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…
 owasp/www-community
OWASP Community Pages are a place where OWASP can accept community contributions for security-related content.
 pedramamini/awesome-yara
A curated list of awesome YARA rules, tools, and people.
 strongswan/strongswan
strongSwan - IPsec-based VPN
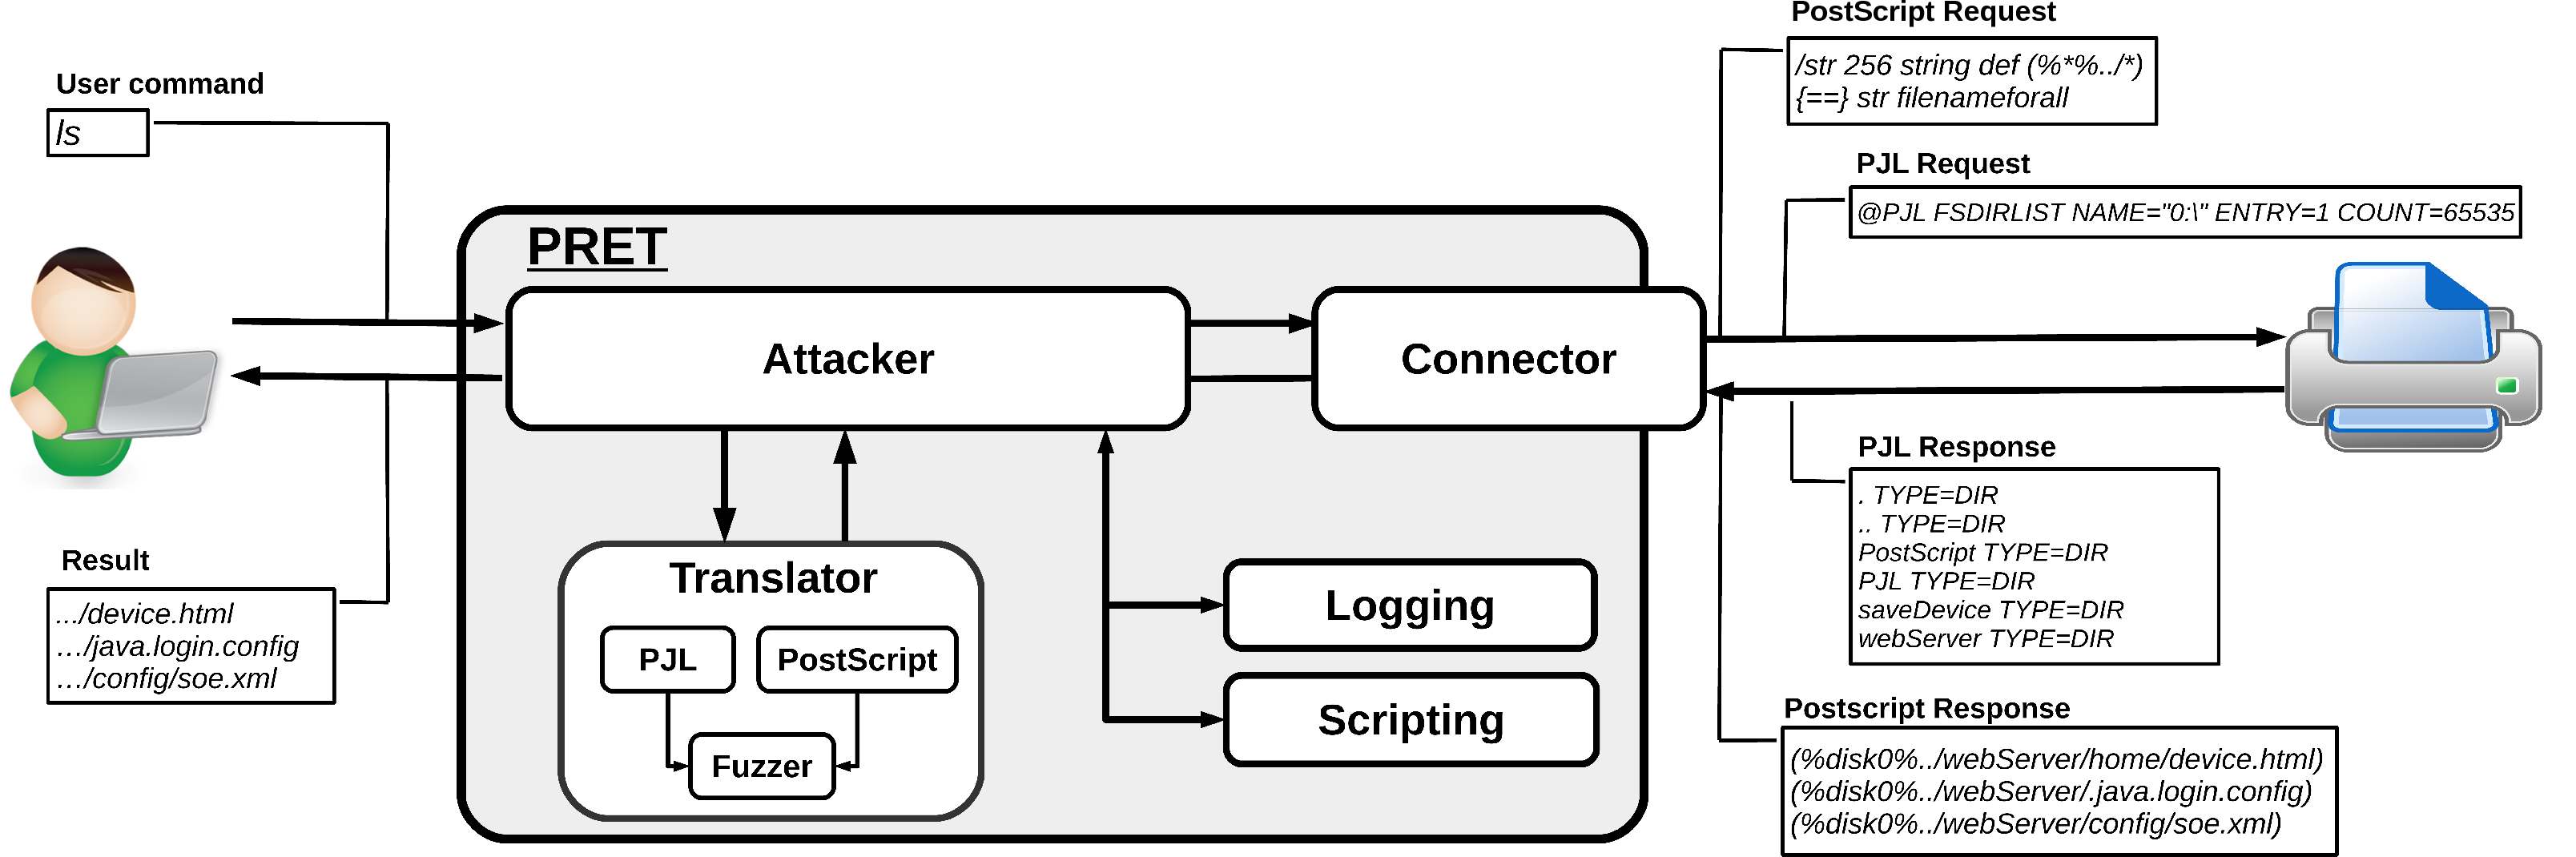 rub-nds/pret
Printer Exploitation Toolkit - The tool that made dumpster diving obsolete.
 joxeankoret/diaphora
Diaphora, the most advanced Free and Open Source program diffing tool.
 jonaslejon/malicious-pdf
Generate malicious PDF test files for penetration testing, bug bounty hunting, and red teaming. Tests SSRF, XSS, XXE, NTLM credential theft, and data…








