
 #1
General-purpose tools, frameworks, and environments supporting various cybersecurity workflows and tasks.
Kitploit recommended

 bishopfox/joro
A collaborative web exploitation framework.
 owasp/owasp-ctf-in-a-box
Self-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies
 dev-sec/chef-mysql-hardening
This chef cookbook provides security configuration for mysql.
 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 guneykabel/cve-2026-85706
Python PoC exploit for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab CE/EE via Workhorse path-encoding bypass, with writeup and…
 n0qword/mythic_ornn
LLM-driven generator for Mythic Agents, Payload-Type and C2 Profiles.
 averagesecurityguy/c2
A simple, extensible C&C beaconing system.
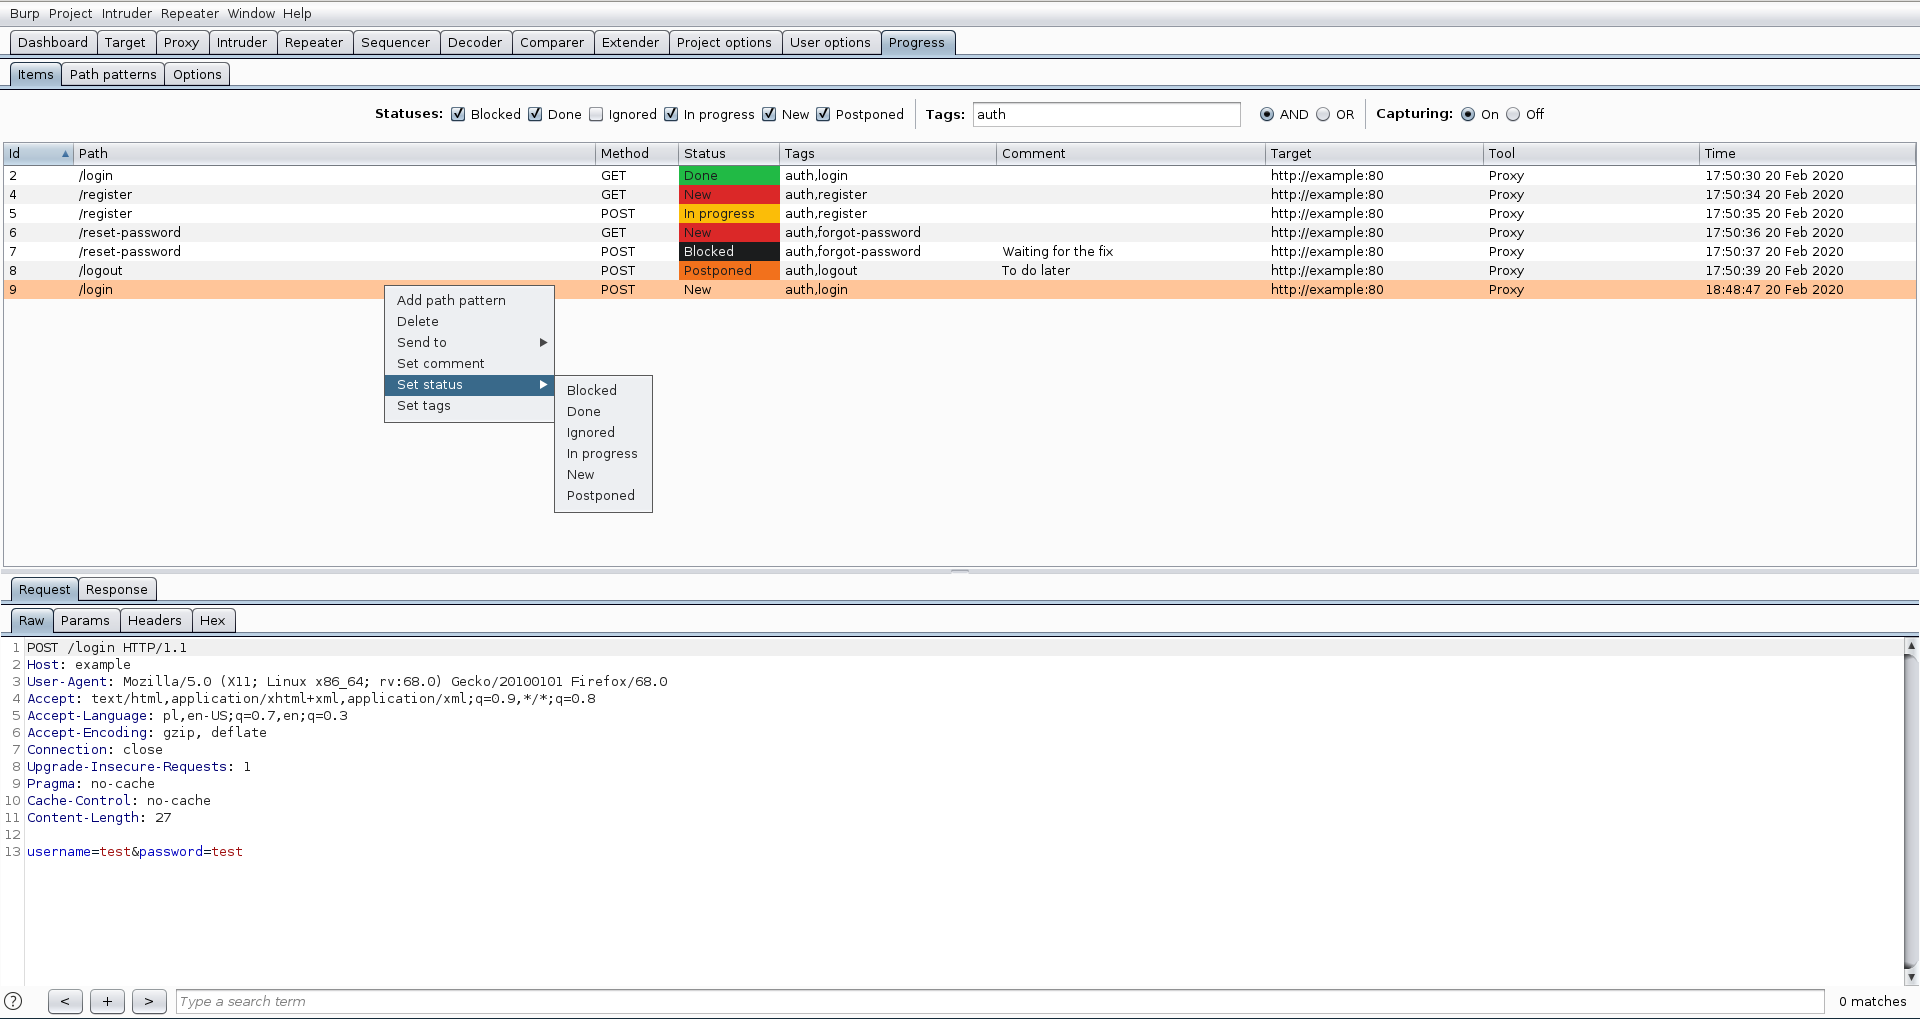 dariusztytko/progress-burp
Burp Suite extension to track vulnerability assessment progress
 onescripter/wmiexec
Execute Windows commands remotely and capture output using only WMI and PowerShell (not remoting).
 xenoncyber/envy
A terminal based tool for managing secrets with both tui and cli support
 pho5nix/red-team-goad-lab-proxmox
Build guide for Red Teaming home lab. GOAD lab setup in Proxmox and pfSense, Operator/C2 and Redirectors.
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 n1ght-w0lf/uchihash
A small utility to deal with malware embedded hashes.
 nybaywatch/agrusscanner
Windows network reconnaissance scanner with ping sweeps, TCP port scanning, and deep AI/ML service detection for finding shadow AI, rogue LLM…
 v9mirza/lazyports
lazyports is a terminal UI tool to visualize and manage network ports. It provides an interactive table to inspect listening processes and kill them…

 kalilinux/build-scripts/kali-packer
Create and configure lightweight, reproducible, and portable development environments Kali's HashiCorp Packer configurations to create Kali…
 fabiobaroni/cve-2024-3094-checker
Quick and dirty PoC for checking whether a vulnerable version of xz-utils is installed (CVE-2024-3094)
 charmve/pystegosploit
PoC - Exploit Delivery via Steganography and Polyglots, CVE-2014-0282








