
 #1
General-purpose tools, frameworks, and environments supporting various cybersecurity workflows and tasks.
Kitploit recommended
 abdullahaligun/reachability-check
Browser-based network connectivity checker for testing firewall rules, access restrictions, and corporate policy compliance. Supports HTTP Fetch and…
 nasawyer7/iobitunlockerunlocker
(0 day) CVE-2026-37334 Moves or Copies any file. Bypasses previous patch with a checksum trick. IObit Unlocker v. 1.3.0
 kubernetes/ingress-nginx
Ingress NGINX Controller for Kubernetes
 thecybergeek/cve-2026-3888-snap-confine-systemd-tmpfiles-lpe
Local privilege escalation exploit for CVE-2026-3888 targeting snap-confine and systemd-tmpfiles on Ubuntu, providing SUID and capabilities variants…
 prophetcraft/jarhunter
JAR analysis tool for exploring, searching, and extracting specific classes from large JAR files with bytecode search, multi-selection extraction,…
 thodoristsampouris/agentguard
Zero-trust sandbox for AI agents with kernel-level filesystem jail, transparent network proxy, and YAML-based policy engine to intercept and control…
 fleralex/enseal
Secure, ephemeral secret sharing for developers.
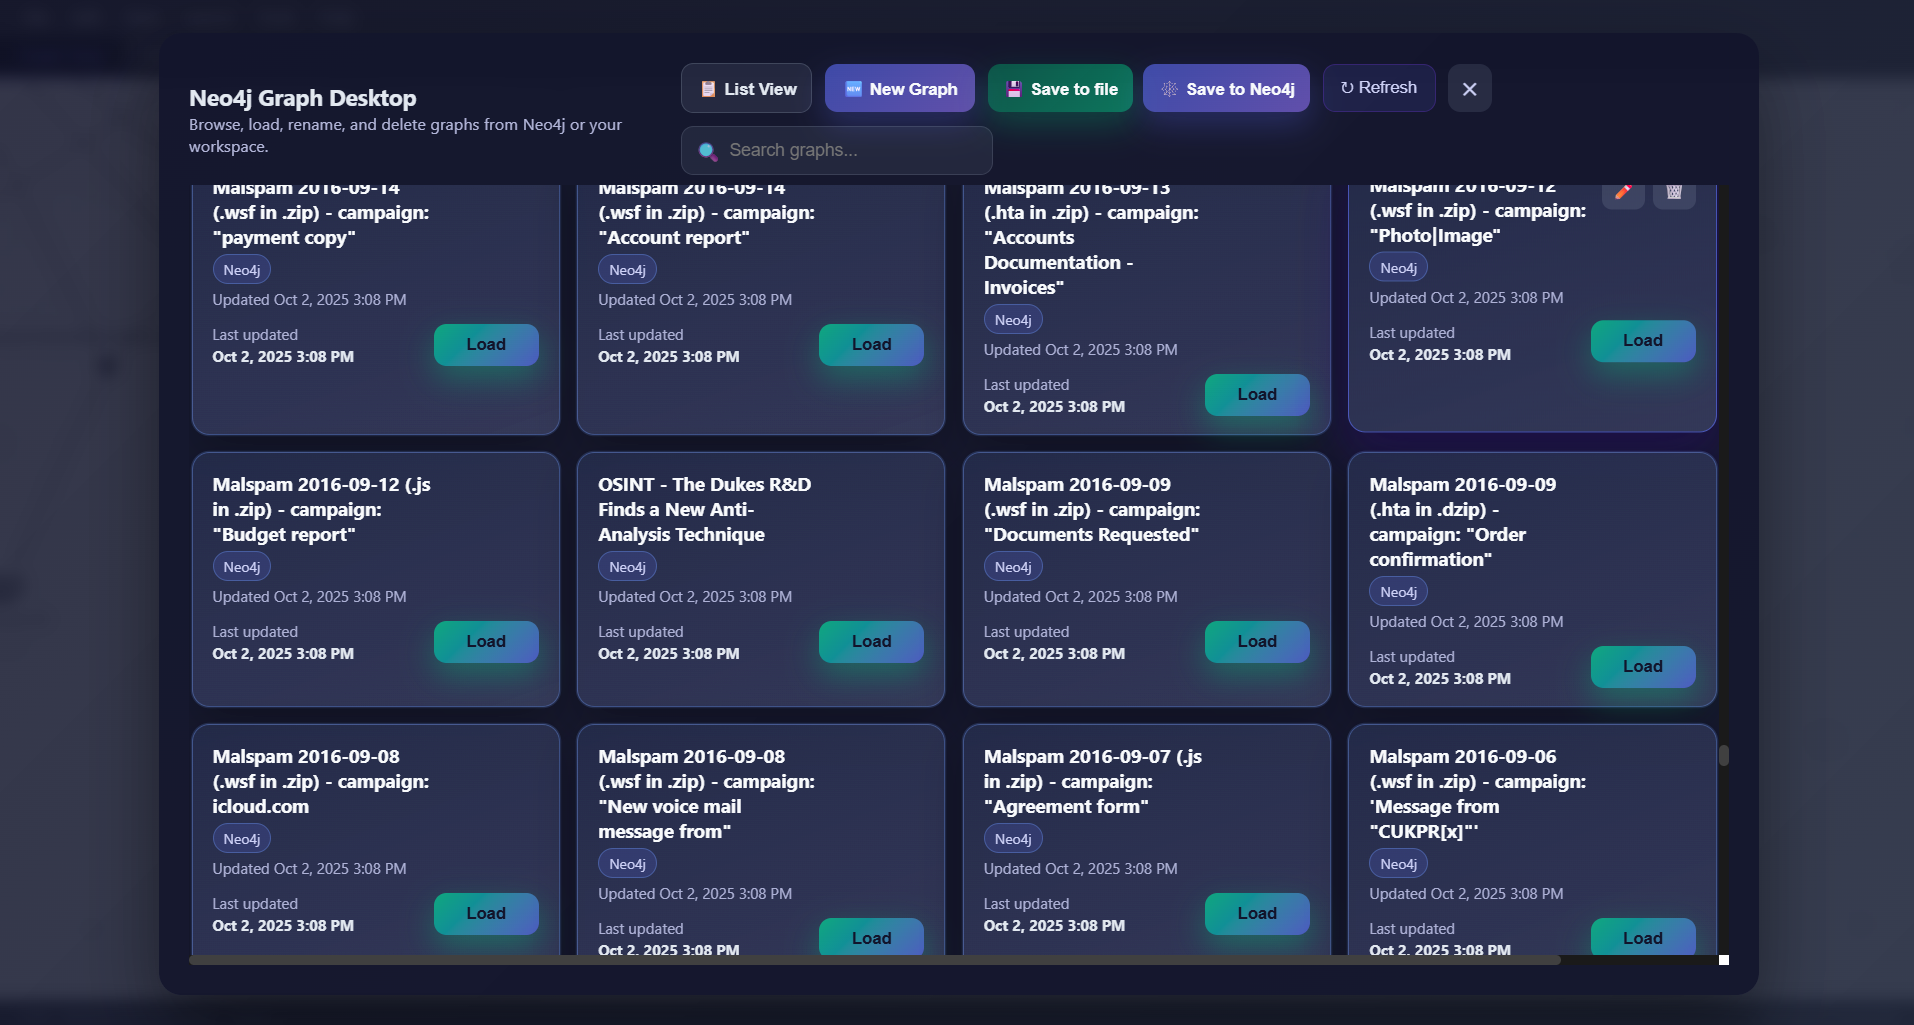 rsac-labs/quantickle
A graphing toolkit for threat research - and other things
 leviticus-triage/cerebro-red-v2
CEREBRO-RED v2: Advanced LLM Red Team Research Platform with PAIR Algorithm and LLM-as-a-Judge Evaluation
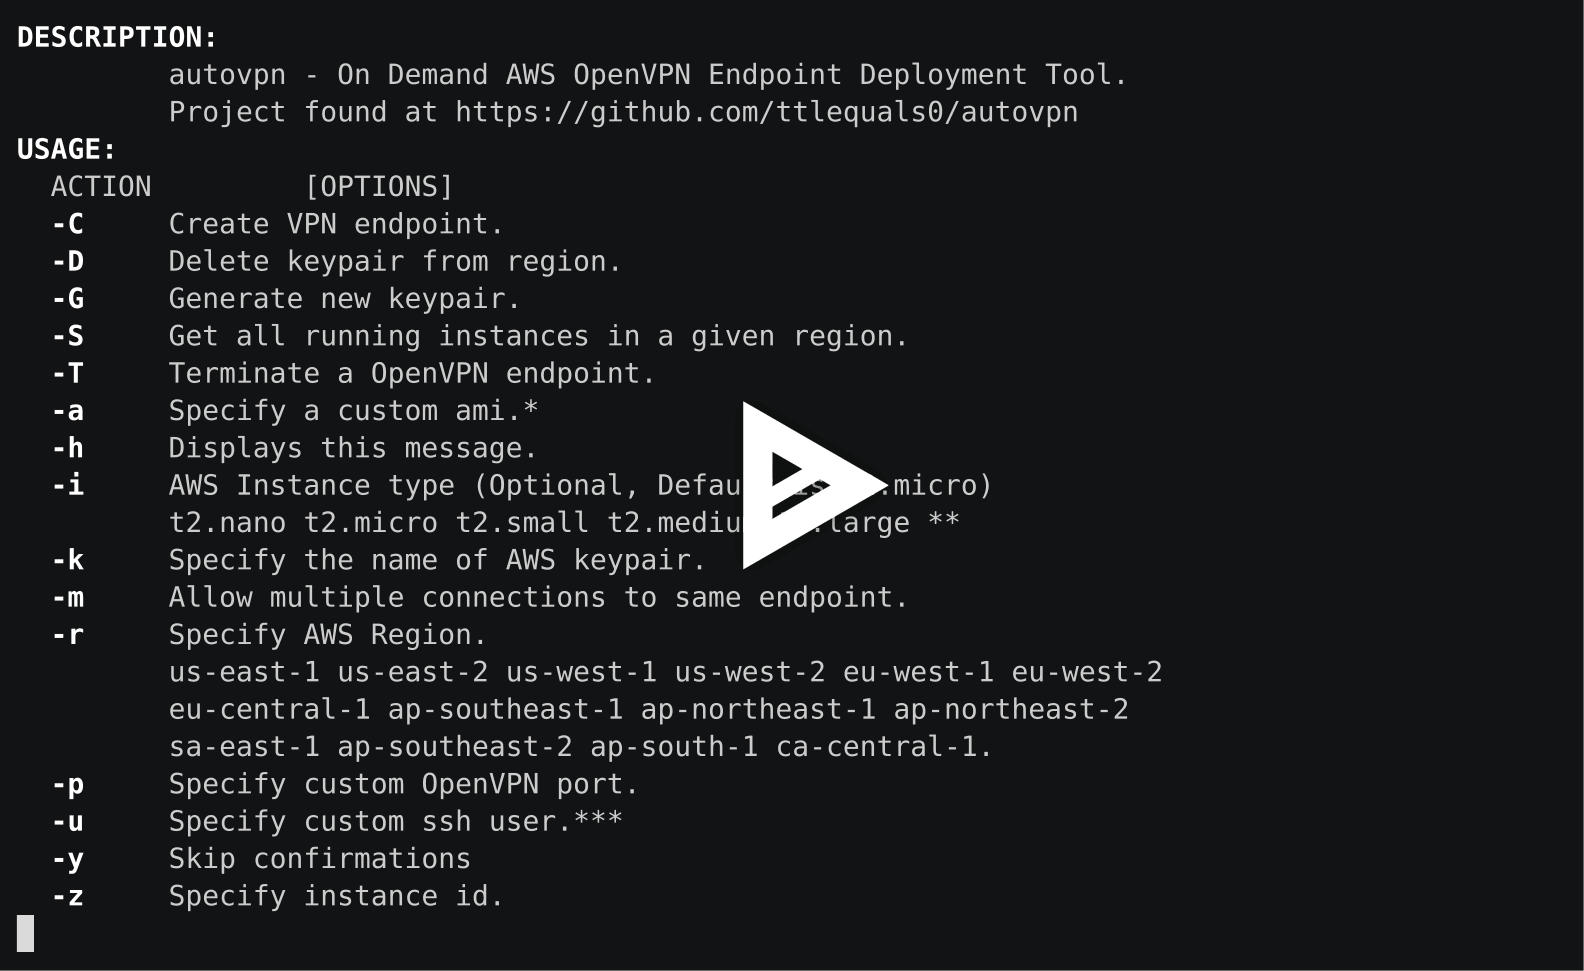 ttlequals0/autovpn
Create On Demand Disposable OpenVPN Endpoints on AWS.
 rizinorg/rizin-notebook
A notebook where to writes notes while using rizin!
 danindiana/cve-2026-32746-mitigation
Automated mitigation tool for CVE-2026-32746, providing atomic rollback, multi-firewall support (UFW, firewalld, nftables, iptables), and…
 d4em0n/exrop
Automated ROP chain generator for x86-64 binaries using symbolic execution. Supports register/memory writes, function calls, syscalls, badchar…
 mimi89999/webauthn_tpm_portable
Portable, hardware-backed WebAuthn credentials using TPM 2.0. Deterministic parent key derived from a master seed enables cross-device credential…
 bombadil-systems/zombie-zip
Malformed ZIP archive that evades antivirus detection by declaring Method=0 (stored) while containing DEFLATE-compressed payload.
 uname1able/cve-2026-2636
Proof-of-concept exploit for CVE-2026-2636 targeting Windows 11 23H2 x64, built with Visual Studio 2022 and Windows SDK 10.0.
 many-hat-group/ubuntu-cve-2026-3888-patcher
This is a script designed for deployment on ubuntu instances patching the CVE-2026-3888 exploit
 avilum/secimport
Library-Level eBPF Sandbox for Python (Linux & macOS): syscall-level control per module.








