
 #1
General-purpose tools, frameworks, and environments supporting various cybersecurity workflows and tasks.
Kitploit recommended
 backline-playground/gogs
Fork of gogs/gogs for reachability benchmark testing (CVE-2024-45337)
 zayan-mohamed/orb
Orb is a secure, terminal-first utility that allows you to share a local folder across the internet using end-to-end encryption. No accounts, no…
 pandaadir05/snoop
A modern syscall tracer built on eBPF. Think strace, but with a real TUI, smart filters, TLS decryption, and output that's actually readable.
 bogdanticu88/ratrace
A lightweight CLI tool for systematically detecting and exploiting race conditions in web applications, APIs, and modern services.
 librewolf-community/browser/source
Development has moved to https://codeberg.org/librewolf/source
 indalok/rizin-notebook
A notebook where to writes notes while using Rizin & Cutter!
 momenbasel/autowifi
Wireless penetration testing framework. Automates WPA/WPA2/WEP/WPS attacks - recon to exploitation in one command. aircrack-ng + hashcat + PMKID.
 kaleth4/cve-2026-4747-
Remote kernel exploit for FreeBSD CVE-2026-4747, leveraging a stack buffer overflow in kgssapi.ko to achieve RCE with a reverse shell. Includes…
 mxrch/ghunt
Async offensive Google framework for OSINT, enabling email/Gaia ID/Drive/geolocation reconnaissance via CLI or Python library with JSON export.
 fabric/fabric
Simple, Pythonic remote execution and deployment.
 x1o3/cve-2025-50286
Metasploit exploit for the CVE-2025-50286.
 kaleth4/cve-2026-4747
Remote kernel RCE exploit for FreeBSD CVE-2026-4747, a stack buffer overflow in kgssapi.ko leading to root shell via ROP chain and shellcode.
 mailgun/flanker
Python email address and Mime parsing library
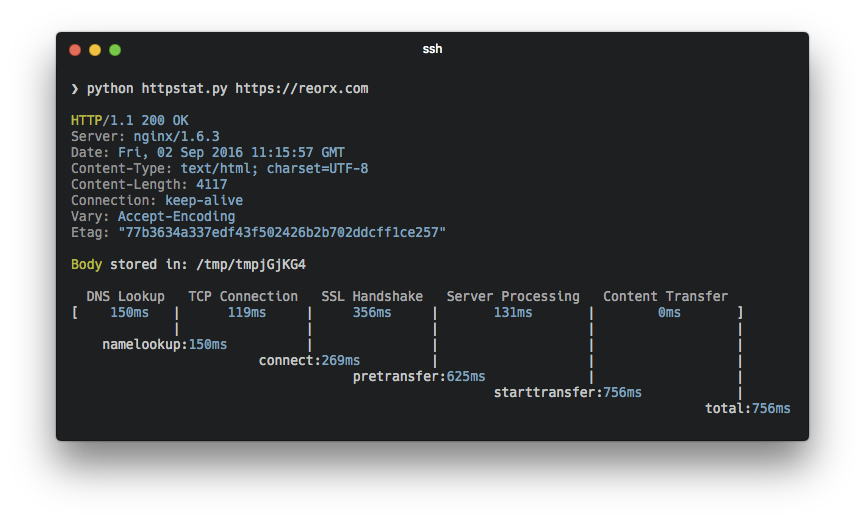 reorx/httpstat
CLI tool that wraps curl to visualize HTTP request timing breakdowns (DNS, TCP, TLS, server processing) with structured JSON output and SLO threshold…
 reverseclabs/drozer
The Leading Security Assessment Framework for Android.
 pion/handoff
Start WebRTC in the browser—run it somewhere else
 wkoszek/emuko
RISC-V emulator in Rust that boots Linux with JIT on ARM64/x86_64 and Sv39 virtual memory
 wostgit/cve-2025-15467-crash
Proof-of-concept for CVE-2025-15467, demonstrating a crash condition for vulnerability analysis and exploitation research.








