
 #1
General-purpose tools, frameworks, and environments supporting various cybersecurity workflows and tasks.
Kitploit recommended

 shadowabi/cve-2026-31431-copyfail-universal-lpe
CVE-2026-31431 Copy Fail — Universal LPE exploit. Dynamic ELF offset + full-binary overwrite, Python 2/3 compatible with ctypes splice fallback
 tailwindrg/cve-2026-0300-audit
Read-only audit tooling for CVE-2026-0300 (PAN-OS User-ID Authentication Portal exposure)
 iblamenear/cve-2026-31431-copy-fail---advanced-lpe-proof-of-concept---c-rewrite
Copy Fail (CVE-2026-31431) is a logic bug in the Linux kernel's authencesn cryptographic template. It lets an unprivileged local user trigger a…
 dinosn/cve-2026-32710
Heap OOB write in MariaDB JSON_SCHEMA_VALID() → persistent privilege escalation (lab-assisted)
 razvanduda/ghostshell
CVE-2026-31431 — Local Privilege Escalation via Linux Kernel Page Cache Corruption
 0xn7y/cve-2026-31431
Logic bug in the kernel's authencesn cryptographic template that escalate privilege
 adityabhatt3010/cve-2026-31431
Local privilege escalation exploit for CVE-2026-31431, abusing AF_ALG AEAD socket handling to achieve root shell access on vulnerable Linux kernels.
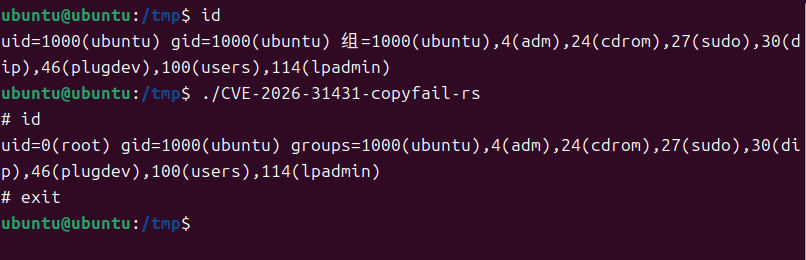 kanbaraakihito/cve-2026-31431-copyfail-rs
Pure Rust proof-of-concept for CVE-2026-31431, targeting Linux x86_64 kernels with AF_ALG AEAD support. Static musl build, no runtime dependencies,…
 onedemobird/copy-fail-cve-2026-31431-pythonlower3.10
Python 3.10-compatible implementation of the CVE-2026-31431 exploit, providing a workaround for missing os.splice in older Python versions.
 darioomatos/cve-2026-31431-copyfail
Educational analysis of CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG AEAD in-place operation, including technical root cause,…
 rat5ak/cve-2026-31431-copyfail-static-elf--poc
Minimal 587-byte static ELF exploit for CVE-2026-31431, achieving local privilege escalation via AF_ALG splice page cache corruption. No libc or…
 facundomfernandez/pentesting-obioba
Pentesting caja negra: Shellshock (CVE-2014-6271) + Log4Shell (CVE-2021-44228). Escalada a root. Informe ejecutivo y técnico
 borealisai/stepjack
Benchmarking framework for evaluating computer-use AI agents against multi-step indirect prompt injection, with automatic adversarial goal…
 ozergoker/cve-2026-31431-copy-fail
Exploit for CVE-2026-31431: a 732-byte Python script that exploits a straight-line logic flaw to gain root on all Linux distributions since 2017.
 jgoyd/ios-attack-chain-cve-2025-31200-cve-2025-31201
CVE-2025-31200 is a zero-day, zero-click RCE in iOS CoreAudio’s AudioConverterService, triggered by a malicious audio file via iMessage/SMS.…
 avprince26/copy-fail-cve-2026-31431-python-golfing
Python golfing challenge for copy.golf, focusing on crafting minimal code to replicate a specific CVE-related behavior.
 threat9/routersploit
Exploitation Framework for Embedded Devices
 zhanghangorg/cve-2026-31431
Detector and proof-of-concept for a Linux kernel page-cache write vulnerability (CVE-2026-31431) in algif_aead, including a non-destructive scanner…








