
 #1
General-purpose tools, frameworks, and environments supporting various cybersecurity workflows and tasks.
Kitploit recommended

 xhyumiracle/sudp
Secret-Use Delegation Protocol — protocol-level secret use for agentic systems
 gopasteverything/gpewebdefender
Lightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.
 vulnerscom/getsploit
Search and download public exploits from the Vulners database — online, or fully offline from a local SQLite FTS5 index.
 katekeiroz-dev/golang-x-text
golang.org/x/text v0.33.0 backport of CVE-2026-56852 (GO-2026-5970) for Go 1.24
 0xsteph/pentest-ai-agents
Turn Claude Code into your offensive security research assistant. Specialized AI subagents for authorized penetration testing plan engagements,…
 vincentkaufmann/noapi-google-search-mcp
MCP server for Google search and page fetching using headless Chromium
 harshiys/cve-2007-2447-exploitation-siem-detection-lab
Isolated AD/Linux attack lab: exploited CVE-2007-2447 via Metasploit, detected with Wazuh SIEM mapped to MITRE ATT&CK (T1190, T1059)
 amibhai/spoofed
A professional-grade, fully async Python network spoofing suite for authorized security auditing. Features full IPv4/IPv6 interception, 802.11…
 bugbasesecurity/pentest-copilot
AI-driven penetration testing agent that connects to a Kali box, autonomously runs security tools, analyzes results, and iterates through…
 horkimhab/cve-2026-53365
CVE-2026-53365
 oisf/libhtp
Security-aware HTTP protocol parser library used by IDS/IPS engines to inspect and normalize HTTP traffic for threat detection.
 ejfkdev/jd
Go CLI that deobfuscates javascript-obfuscator (obfuscator.io) output and unminifies JavaScript using AST transforms, static decoding, and a goja…
 pimpamebanihah/cve-2026-43499-app.s0
Placeholder repository referencing CVE-2026-43499; no source code, documentation, or security functionality is evidenced in the available metadata.
 sonalisarkar-2003/ftp-vsftpd-cve-2011-2523-vapt-report
VAPT report for vsFTPd 2.3.4 backdoor CVE-2011-2523, covering Nmap vulnerability scanning, Metasploit exploitation, post-exploitation root access,…
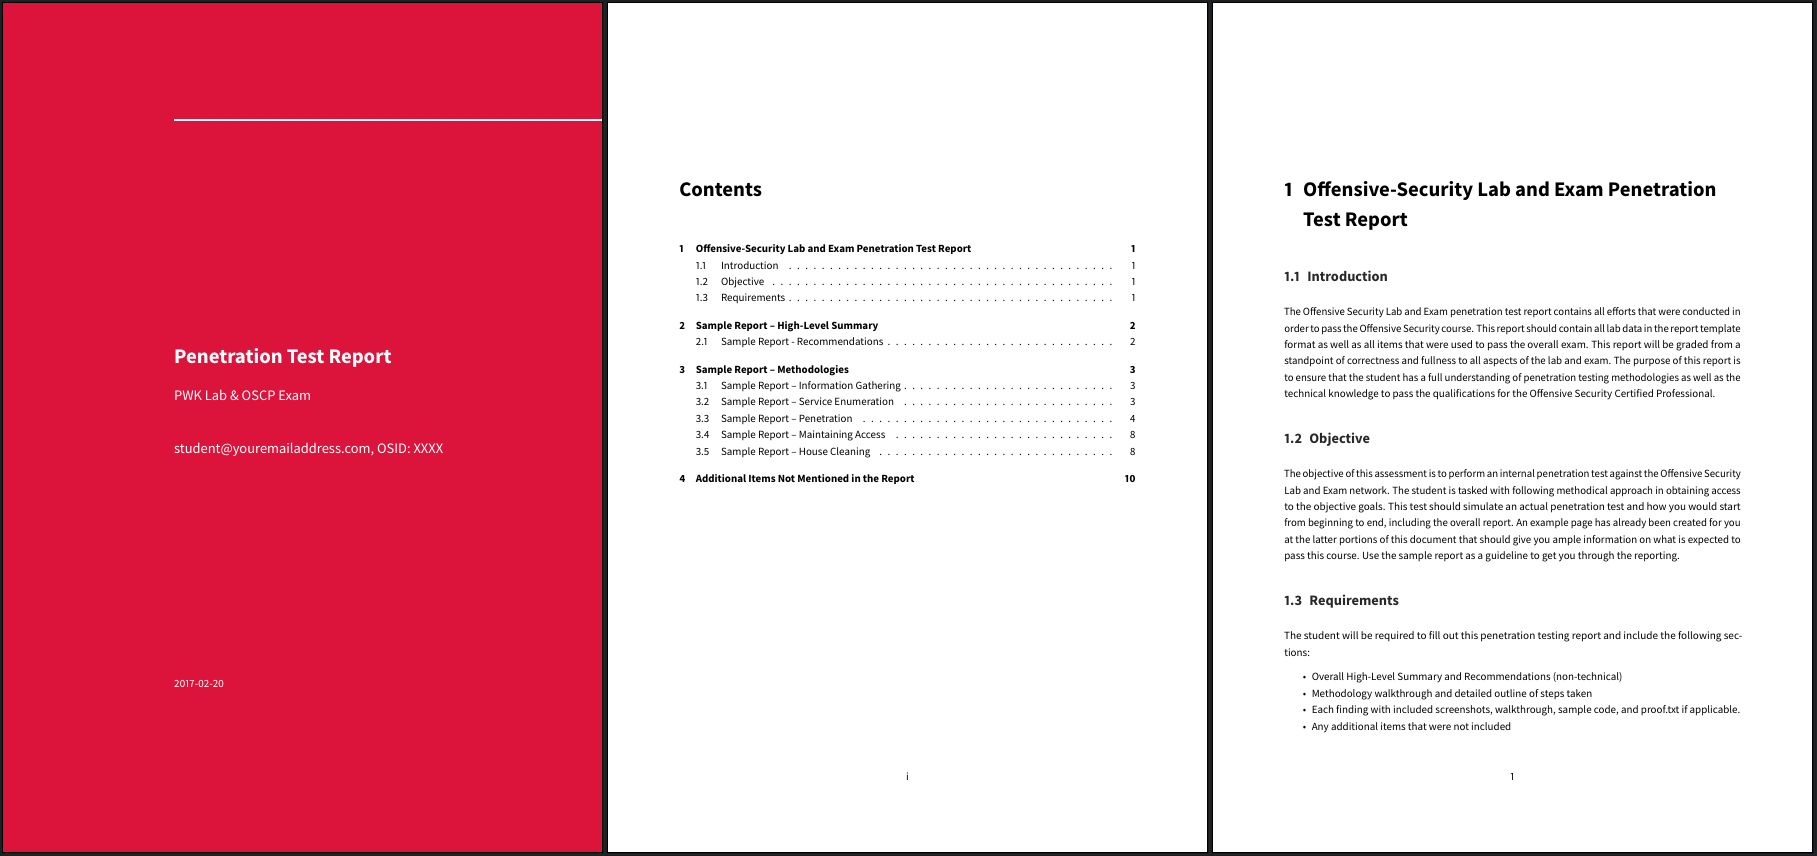 noraj/oscp-exam-report-template-markdown
:orange_book: Markdown Templates for Offensive Security OSCP, OSWE, OSCE, OSEE, OSWP exam report
 clawkwork/clawk
Give coding agents a disposable Linux VM, not your laptop
 ninedeadeyes/s.p.a.r.k--standard-python-ascii-rpg-kit-
Light Weight 2d Ascii RPG Python Game Engine
 thelicato/secbutler
The perfect butler for pentesters, bug-bounty hunters and security researchers








