
 #1
General-purpose tools, frameworks, and environments supporting various cybersecurity workflows and tasks.
Kitploit recommended
 bl0odz/cve-2021-40449-ntgdiresetdc-uaf
Proof-of-concept exploit for CVE-2021-40449, a Windows kernel use-after-free in NtGdiResetDC, demonstrating privilege escalation via user-space…
 ayrx/cve-2021-4034
Exploit for CVE-2021-4034 (PwnKit) that leverages a race condition in pkexec to escalate privileges to root on Linux systems.
 audiobahn/cve-2021-4034
Local privilege escalation exploit for CVE-2021-4034 targeting pkexec, providing proof-of-concept code for security testing and research.
 anonymous-family/cve-2021-4034
Exploit for CVE-2021-4034 (PwnKit) in Polkit's pkexec, providing local privilege escalation to root on Linux systems. Includes build instructions and…
 ankit-ojha16/cve-2021-4034
Local privilege escalation exploit for CVE-2021-4034 targeting pkexec, enabling unprivileged users to gain root access on vulnerable Linux systems.
 andrewtrube/cve-2021-1675
Local privilege escalation exploit for CVE-2021-1675 (PrintNightmare) that installs a malicious DLL to gain SYSTEM access on vulnerable Windows…
 almorabea/pkexec-exploit
pwnkit: Local Privilege Escalation in polkit's pkexec (CVE-2021-4034)
 ak777177/dirty-frag-analysis
Dirty Frag (CVE-2026-43284/43500) - Linux Kernel LPE Deep Technical Analysis by Bomb
 0xshe/cve-2026-31431
Kernel privilege escalation exploit for CVE-2026-31431, abusing AF_ALG interface to overwrite /bin/su and spawn a root shell. Includes C…
 0x4ndy/cve-2021-4034-poc
Proof-of-concept exploit for CVE-2021-4034, a local privilege escalation vulnerability in polkit's pkexec, allowing unprivileged users to gain root…
 0x05a/my-cve-2021-4034-poc
Proof-of-concept exploit for CVE-2021-4034, a local privilege escalation in polkit's pkexec, demonstrating exploitation on Ubuntu systems.
 0x01-sec/cve-2021-4034-
Proof-of-concept exploit for CVE-2021-4034 (PwnKit), a local privilege escalation vulnerability in polkit's pkexec, allowing unprivileged users to…
 zenyxx-xd/rootmyvivo
One-click root for vivo/iQOO devices on locked bootloader | CVE-2026-43499 + KernelSU
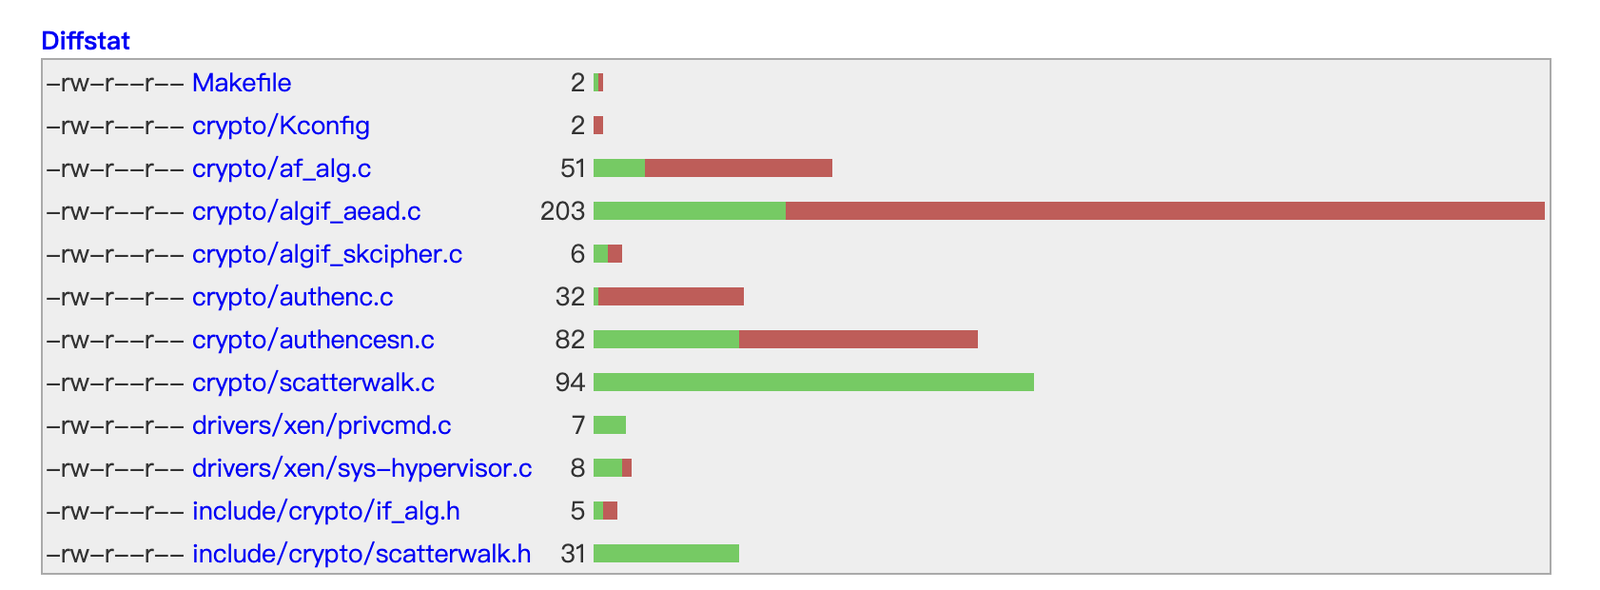 yuspring/cve-2026-31431-poc
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel privilege escalation via AF_ALG authenc length check bypass, achieving root by modifying…
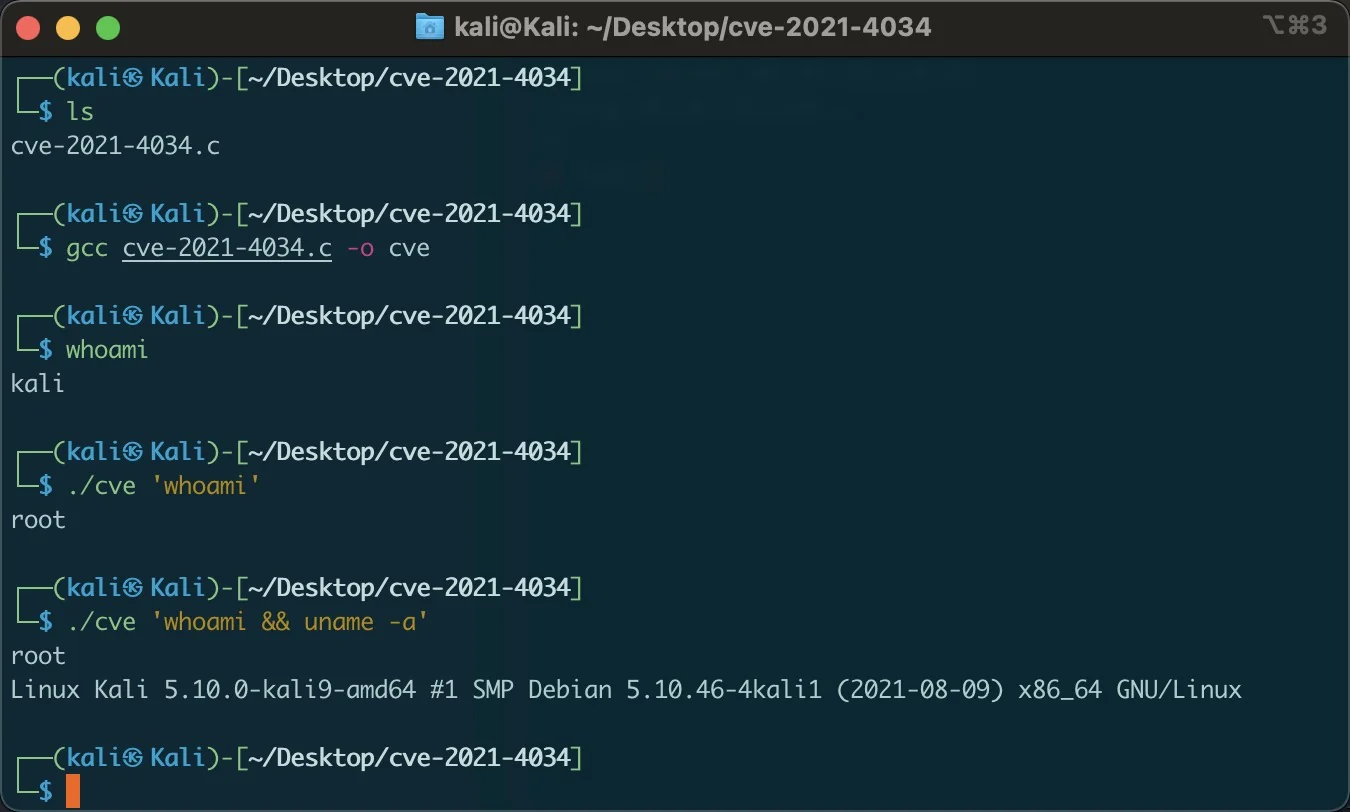 zhzyker/cve-2021-4034
polkit pkexec Local Privilege Vulnerability to Add custom commands
 zmkeh/cve-2025-29824-clfs-local-privilege-escalation
Local privilege escalation exploit for CVE-2025-29824 targeting the Windows Common Log File System (CLFS) driver, providing proof-of-concept code for…
 qingizi7/cve-2025-21479_iqooneo8
Local root exploit for CVE-2025-21479 (Adreno KGSL) on iQOO Neo8 (SM8475) - physical memory r/w, disables SELinux, spawns root shell
 begitdj/cve-2019-2215-markw
Exploit for CVE-2019-2215 to gain temporary root on Xiaomi MIUI devices, enabling bootloader unlock and system modifications.








