
 #1
General-purpose tools, frameworks, and environments supporting various cybersecurity workflows and tasks.
Kitploit recommended
 px4/px4-autopilot
Open-source autopilot stack for drones and unmanned vehicles, supporting multirotors, fixed-wing, VTOL, and rovers with modular architecture and…
 oxdbxkxo/ez-pwnkit
Go implementation of the PwnKit Linux Local Privilege Escalation exploit (CVE-2021-4034)
 nis3x/cve-2021-4034
Proof-of-concept exploit for CVE-2021-4034 (PwnKit), a local privilege escalation vulnerability in polkit's pkexec, allowing unprivileged users to…
 nero22k/cve-2021-4034
Proof-of-concept exploit for CVE-2021-4034 (Pwnkit), a local privilege escalation vulnerability in polkit's pkexec, allowing unprivileged users to…
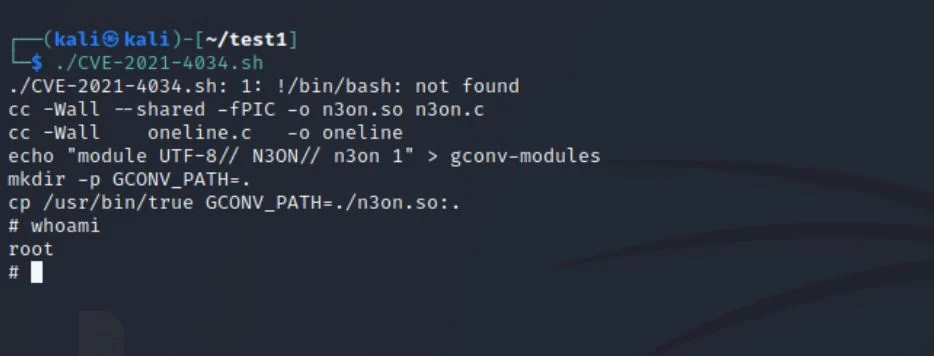 neonwhiterabbit/cve-2021-4034
Bash script exploiting CVE-2021-4034 (Pwnkit) for local privilege escalation on vulnerable Linux systems. Copy-paste execution for quick testing.
 kaleth4/cve-2026-4747
Remote kernel RCE exploit for FreeBSD CVE-2026-4747, a stack buffer overflow in kgssapi.ko leading to root shell via ROP chain and shellcode.
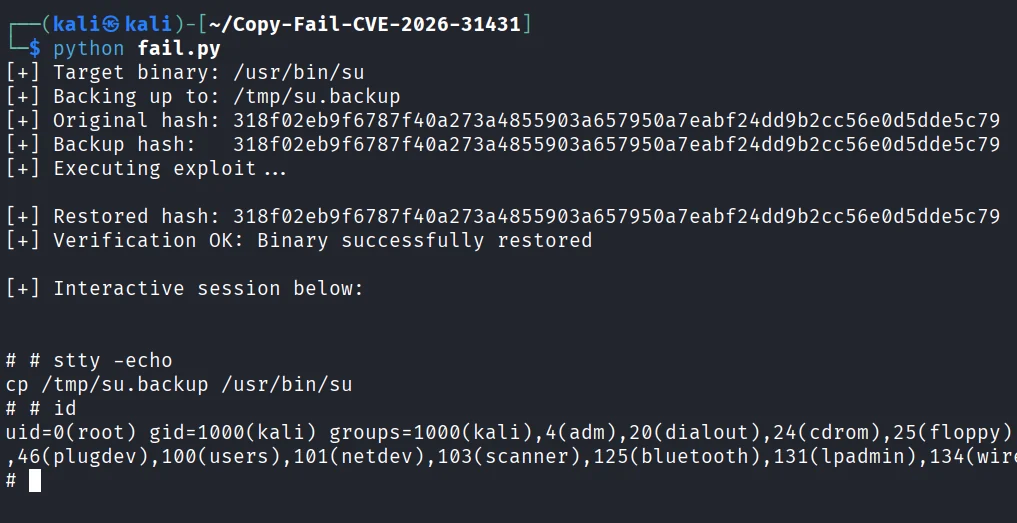 mohamedkarrab/copy-fail-cve-2026-31431
Proof-of-concept exploit for Linux kernel CVE-2026-31431 (Copy Fail) that abuses AF_ALG to corrupt setuid-root binaries in page cache, achieving…
 hori0729/cve-2026-31431-verificador-exploit
Local privilege escalation exploit for Linux kernel CVE-2026-31431, exploiting AF_ALG and splice() to modify page cache and gain root shell.
 many-hat-group/ubuntu-cve-2026-3888-patcher
This is a script designed for deployment on ubuntu instances patching the CVE-2026-3888 exploit
 linux-zs/cve-2026-31431-mitigation
Seccomp-based mitigation for CVE-2026-31431, a Linux kernel LPE. Blocks AF_ALG socket via PAM module and standalone wrapper, with auto-detection of…
 zhanghangorg/cve-2026-31431
Detector and proof-of-concept for a Linux kernel page-cache write vulnerability (CVE-2026-31431) in algif_aead, including a non-destructive scanner…
 ljp-tw/cve-2021-4034
Exploit for CVE-2021-4034, a local privilege escalation in pkexec, providing proof-of-concept code and a detailed writeup.
 kirill89/cve-2021-4034
Dockerized exploit for Polkit privilege escalation (CVE-2021-4034) that grants root access via pkexec, with a simple script to run and verify.
 pvpaulo01/cve-2026-31431
Esse documento descreve o Exploit publico em python
 kaleth4/cve-2026-31431
Exploit and detector for a Linux kernel local privilege escalation (CVE-2026-31431) that corrupts page cache to gain root, with mitigation guidance.
 juguitos/copy-fail
Python proof-of-concept for CVE-2026-31431, exploiting kernel AF_ALG to modify SUID binary page cache and spawn a root shell on Linux systems.
 joyghoshs/cve-2021-4034
Exploit for Local Privilege Escalation Vulnerability in polkit’s pkexec
 darioomatos/cve-2026-31431-copyfail
Educational analysis of CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG AEAD in-place operation, including technical root cause,…








