
 #1
General-purpose tools, frameworks, and environments supporting various cybersecurity workflows and tasks.
Kitploit recommended

 luotian2/cve-2026-31431
Exploit for CVE-2026-31431, a Linux kernel authencesn bug enabling local privilege escalation and container escape via a 4-byte page cache write.
 luckythandel/cve-2021-4034
This is a POC for the vulnerability found in polkit's pkexec binary which is used to run programs as another users.
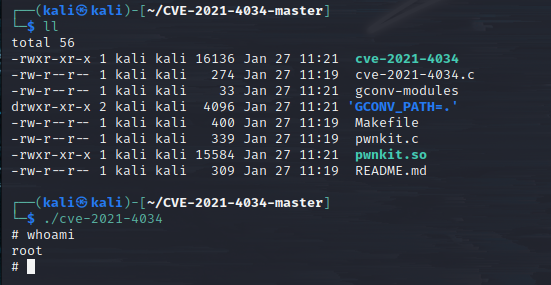 locksec/cve-2021-4034
Exploit PoC for the polkit pkexec (PWNKIT) vulnerability
 ksk-itdk/ksk-itdk-cve-2026-21509-mitigation
Powershell script with Detection and Remediation for CVE-2026-21509
 krn966/cve-2025-27591
Local privilege escalation exploit for CVE-2025-27591, abusing insecure symlink handling in the below utility's logging to overwrite arbitrary files…
 kernelzeroday/cve-2026-29000
Forge JWE-wrapped unsigned JWTs to bypass pac4j-jwt signature verification (CVE-2026-29000) and authenticate as any user; includes Python CLI,…
 kalibb/cve-2026-28372-gnu-inetutils-telnetd-privilege-escalation-main
Proof-of-concept exploit for CVE-2026-28372, demonstrating local privilege escalation in GNU inetutils telnetd via environment variable injection to…
 jwde/automerge-test
A minimal test repository for auto-merge functionality, referencing a CVE variant.
 jrocia/search-log4jvuln-appscanstd
This Pwsh script run AppScan Standard scans against a list of web sites (URLs.txt) checking for Log4J (CVE-2021-44228) vulnerability
 jpmcb/pwnkit-go
Exploit for the PwnKit vulnerability, CVE-2021-4034, written in Go
 jostmart/-cve-2021-4034
Exploit for CVE-2021-4034, a local privilege escalation in polkit's pkexec, providing root access on Linux systems.
 jcatala/f_poc_cve-2021-4034
Proof-of-concept exploit for CVE-2021-4034, a local privilege escalation in polkit's pkexec, demonstrating exploitation via shared library injection.
 jbaines-r7/blankspace
Proof of Concept for EFSRPC Arbitrary File Upload (CVE-2021-43893)
 jaf0rk/cve-2026-5281-cve-2026-11057-fullchain
Full-chain exploit for Android Chromium combining CVE-2026-11057 info leak and CVE-2026-5281 use-after-free to achieve vtable hijack and arbitrary…
 iss4cf0ng/cve-2026-31431-linux-copy-fail
Rust-based local privilege escalation exploit for CVE-2026-31431, enabling execution of custom shellcode such as Meterpreter on Linux systems.
 galoryber/cve-2026-31431-cleaned
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation via splice() and crafted socket options, enabling arbitrary…
 foxtrot/cve-2021-1965
Proof-of-concept exploit for CVE-2021-1965, a Wi-Fi vulnerability, leveraging libwifi for packet parsing and crafted for educational purposes.
 fnknda/cve-2021-4034_poc
Proof Of Concept for the 2021's pkexec vulnerability CVE-2021-4034








