
 #1
General-purpose tools, frameworks, and environments supporting various cybersecurity workflows and tasks.
Kitploit recommended
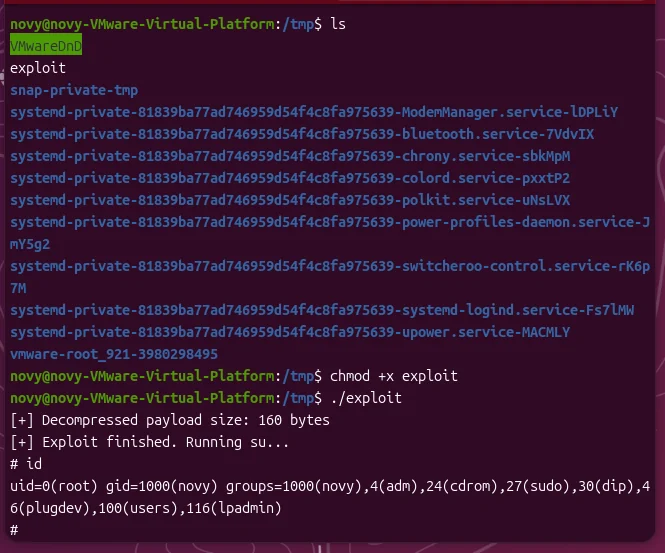
 novysodope/copy-fail-cve-2026-31431-c
CVE-2026-31431 - standalone binary exploit (no Python required)
 nisec-eric/cve-2026-31431
Linux kernel local privilege escalation exploit for CVE-2026-31431, providing a reliable single-shot PoC with multiple language implementations,…
 nightcorefan94/cve-2026-6770
Proof-of-concept exploit for CVE-2026-6770 targeting Firefox and Tor browsers, demonstrating the vulnerability and enabling security researchers to…
 nel0x/pwnkit-vulnerability
Local privilege escalation exploit for CVE-2021-4034 (PWNKIT) targeting Polkit's pkexec, allowing unprivileged users to gain root on vulnerable Linux…
 navisec/cve-2021-4034-pwnkit
Nim-based proof-of-concept for CVE-2021-4034 (PwnKit), a local privilege escalation in polkit's pkexec, with embedded payload library for standalone…
 nasawyer7/iobitunlockerunlocker
(0 day) CVE-2026-37334 Moves or Copies any file. Bypasses previous patch with a checksum trick. IObit Unlocker v. 1.3.0
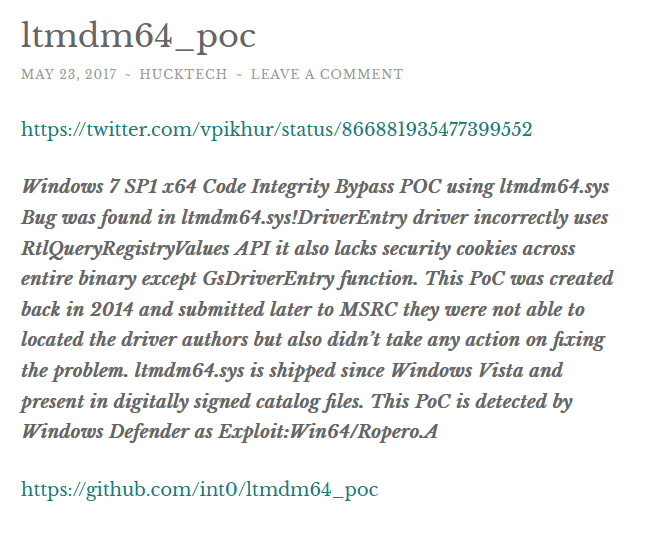 moiz-2x/cve-2025-24990_poc
Proof of Concept CVE-2025-24990 (Agere Systems's driver)
 moisei-dev/go-dbmigrate
Go library and CLI for managing database schema migrations with support for PostgreSQL, MySQL, SQLite, and Cassandra, including up/down migration…
 mishl-dev/cve_2026_31431
Exploit for CVE-2026-31431, a Linux kernel page-cache write primitive enabling local privilege escalation and container escape via AF_ALG and…
 mfloresdacunha/cve-2026-31431
Local privilege escalation exploit for CVE-2026-31431 in Linux kernel's algif_aead, using splice to overwrite page cache and gain root. Includes a…
 mebeim/cve-2021-4034
Proof-of-concept exploit for CVE-2021-4034, a local privilege escalation in polkit's pkexec, demonstrating exploitation with simple C helpers and a…
 mbanyamer/cve-2026-32743-px4-autopilot-mavlinkloghandler-stack-buffer-overflow-dos-
A remote Denial of Service (DoS) exploit for PX4 Autopilot versions ≤1.17.0-rc2 via a stack‑based buffer overflow in the MavlinkLogHandler.
 mbanyamer/cve-2026-28372-gnu-inetutils-telnetd-privilege-escalation
Proof-of-concept exploit for CVE-2026-28372, demonstrating local privilege escalation in GNU inetutils telnetd via CREDENTIALS_DIRECTORY and…
 luotian2/cve-2026-31431
Exploit for CVE-2026-31431, a Linux kernel authencesn bug enabling local privilege escalation and container escape via a 4-byte page cache write.
 luckythandel/cve-2021-4034
This is a POC for the vulnerability found in polkit's pkexec binary which is used to run programs as another users.
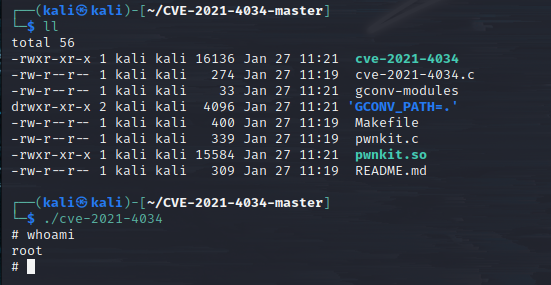 locksec/cve-2021-4034
Exploit PoC for the polkit pkexec (PWNKIT) vulnerability
 ksk-itdk/ksk-itdk-cve-2026-21509-mitigation
Powershell script with Detection and Remediation for CVE-2026-21509
 krn966/cve-2025-27591
Local privilege escalation exploit for CVE-2025-27591, abusing insecure symlink handling in the below utility's logging to overwrite arbitrary files…








