
 #1
General-purpose tools, frameworks, and environments supporting various cybersecurity workflows and tasks.
Kitploit recommended
 shi10587s/sauercloude
0day VirtualBox 6.1.2 Escape for RealWorld CTF 2020/2021 CVE-2021-2119
 shazed-x/cve-2025-32463
- Vulnerable: sudo 1.9.14, 1.9.15, 1.9.16, 1.9.17 - Patched in: sudo 1.9.17p1 and later - Legacy versions older than 1.9.14 are not affected, as they…
 shadowabi/cve-2026-31431-copyfail-universal-lpe
CVE-2026-31431 Copy Fail — Universal LPE exploit. Dynamic ELF offset + full-binary overwrite, Python 2/3 compatible with ctypes splice fallback
 san3ncrypt3d/cve-2021-4034-poc
Proof-of-concept exploit for CVE-2021-4034 (PwnKit), a local privilege escalation vulnerability in polkit's pkexec, demonstrating exploitation on…
 sammwyy/copyfail-rs
Copy Fail exploit (CVE-2026-31431) but in Rust.
 ryan2929/cve-2026-43284-
Local privilege escalation exploit for Linux kernel CVE-2026-43284 (Dirty Flag), providing root access on vulnerable systems.
 rvzsec/cve-2026-31431
PoC exploits for CVE-2026-31431, a Linux kernel LPE via authencesn page cache write, providing unprivileged user to root escalation on most distros…
 rio128128/copy-fail-cve-2026-31431
Copy Fail: 732 Bytes to Root on Every Major Linux Distribution.
 puckiestyle/cve-2021-3156
Exploit for CVE-2021-3156 (Sudo Baron Samedit) targeting Linux x64 with multiple variants for different glibc and sudo versions.
 plutosecurity/mcpwnfluence
Information about CVE-2026-27825 & CVE-2026-27826 discovered by Pluto Security and a bash script for identifying vulnerable mcp-atlassian instances…
 phvilasboas/cve-2021-4034
Exploit for CVE-2021-4034, a local privilege escalation in polkit's pkexec, providing a root shell via a shared library and GCONV_PATH manipulation.
 pengalaman-1t/cve-2021-4034
Exploit for CVE-2021-4034 (PwnKit) that provides a root shell via polkit pkexec vulnerability. Includes source code and build instructions.
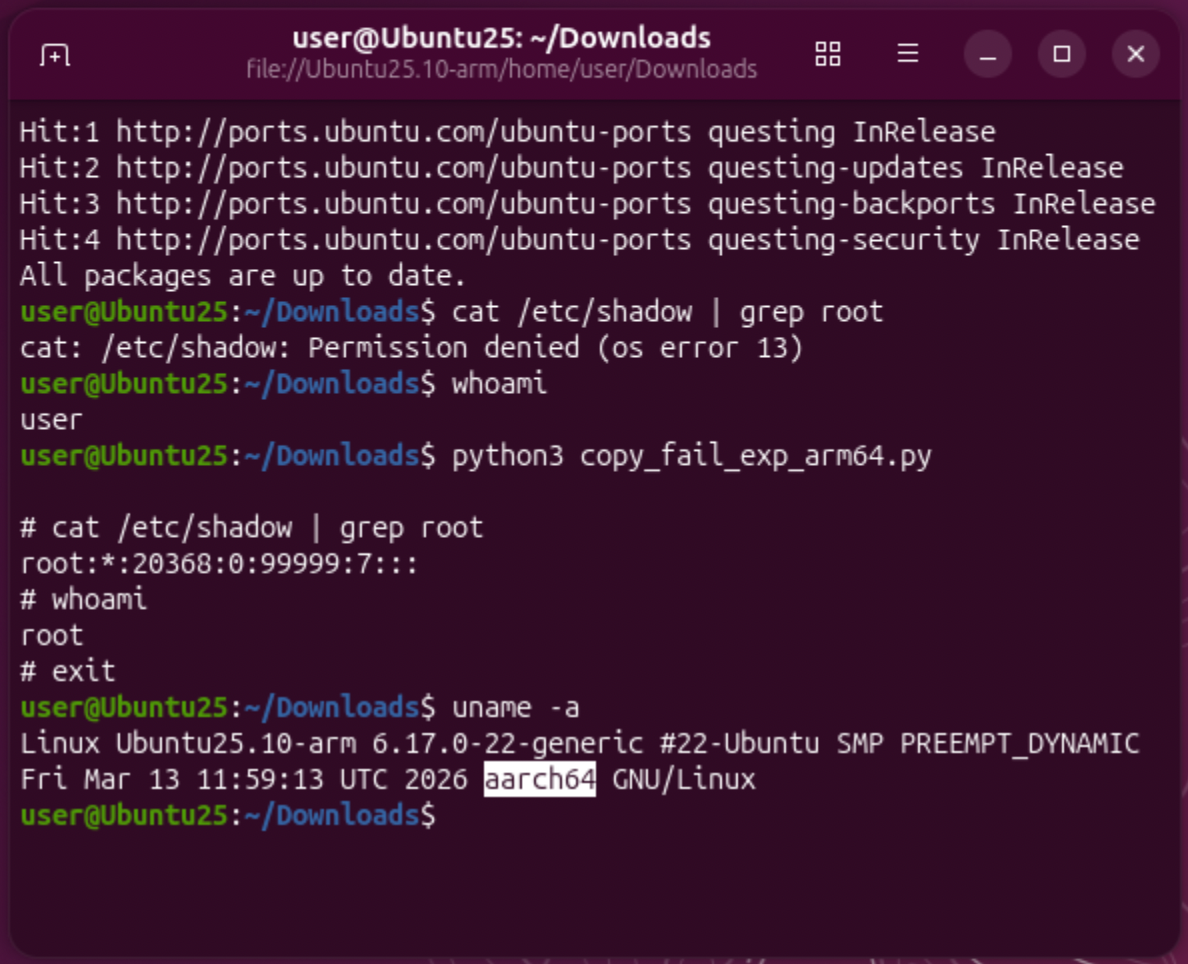 pascal-gujer/cve-2026-31431
Proof-of-concept exploit for CVE-2026-31431, a Linux local privilege escalation via authencesn logic bug, with ARM64 variant for authorized lab…
 painoob/copy-fail-exploit-cve-2026-31431
Most Linux LPEs need a race window or a kernel-specific offset. Copy Fail is a straight-line logic flaw, it needs neither. The same 732-byte Python…
 oxfemale/cve-2026-2636_poc
Proof-of-concept for CVE-2026-2636, a Windows CLFS.sys vulnerability causing BSoD via ReadFile on CreateLogFile handle, enabling unprivileged denial…
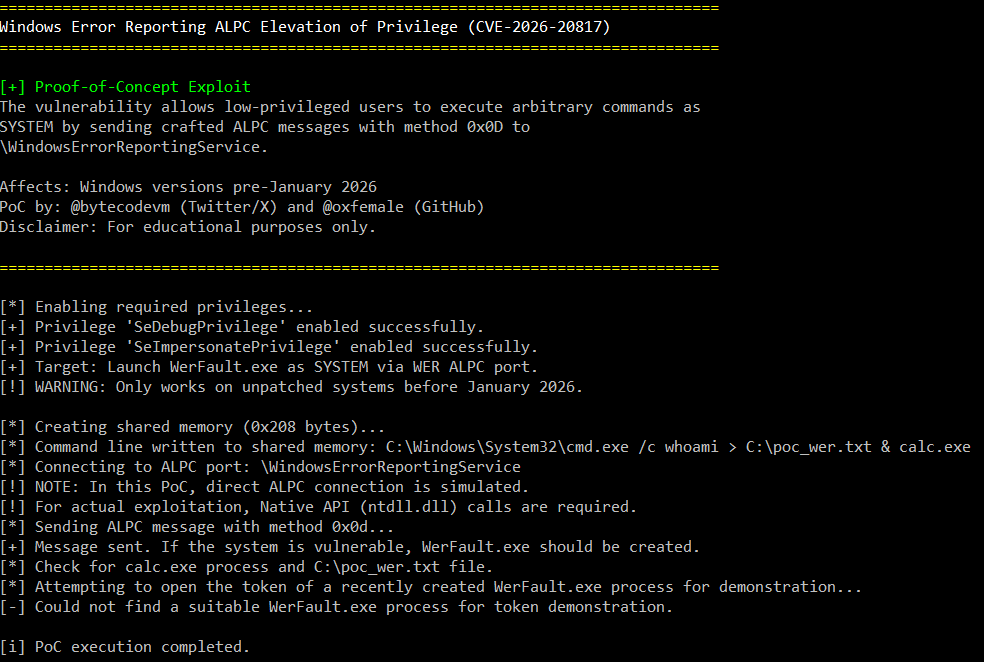 oxfemale/cve-2026-20817
Proof-of-concept exploit for CVE-2026-20817, a local privilege escalation in Windows Error Reporting (WER) via ALPC, allowing low-privileged users to…
 oreosec/pwnkit
Exploit for CVE-2021-4034, a memory corruption vulnerability in pkexec of polkit, enabling local privilege escalation to root on Linux systems.
 nrnw/cve-2026-24061-gnu-inetutils-telnet-detector
A passive detection tool for identifying potential exposure to CVE-2026-24061 in GNU inetutils telnet installations








