
 #1
General-purpose tools, frameworks, and environments supporting various cybersecurity workflows and tasks.
Kitploit recommended

 3jee/copy-fail-go
Go port of the CVE-2026-31431 (copy-fail) Linux kernel privilege escalation PoC, with automatic SUID binary enumeration and interactive target…
 0xn7y/cve-2026-31431
Logic bug in the kernel's authencesn cryptographic template that escalate privilege
 x04000/cve-2021-4034
Pre-built PWNKIT exploit for CVE-2021-4034, a local privilege escalation vulnerability, providing a ready-to-use payload for educational testing.
 wongwaituck/cve-2021-4034
Proof-of-concept exploit for CVE-2021-4034 (PwnKit) that escalates privileges to root on vulnerable Linux systems.
 whokilleddb/cve-2021-4034
Local privilege escalation exploit for CVE-2021-4034 (PwnKit) targeting polkit's pkexec, providing root shell access on vulnerable Linux systems.
 wgnet/wg.copyfail.patch
eBPF-based workaround for CVE-2026-31431 (Copy.Fail) that filters or kills AF_ALG socket creation to prevent local privilege escalation and container…
 weirdindiankid/copy-fail
Proof-of-concept exploit for CVE-2026-31431 that elevates a regular user to root on most Linux distributions and CPUs.
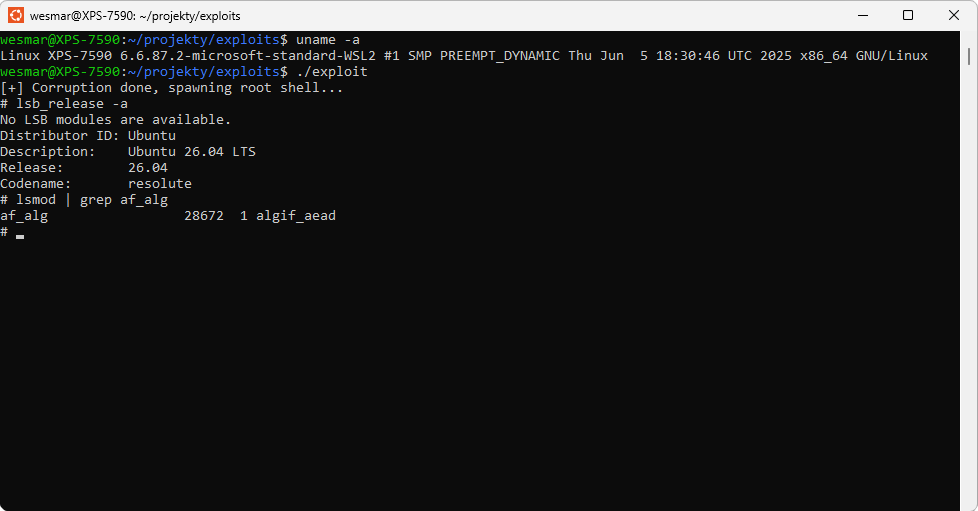 wesmar/cve-2026-31431
Working proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG AEAD page cache corruption, granting root…
 websecnl/cve-2026-31431
Linux algif_aead page-cache write to root - Local Privilege Escalation Exploit
 w3llr00t3d/cve-2026-31431-poc
LPE exploit for CVE-2026-31431 CopyFail. Compatible with Python 3.9.
 vorkampfer/copy_fail_mitigation
This script will attempt to mitigate the copy_fail attack. CVE-2026-31431
 v-rzh/cve-2021-4034
Root exploit for CVE-2021-4034 (PwnKit) that abuses pkexec's out-of-bounds write to escalate privileges to root on Linux systems.
 uname1able/cve-2026-24291
Proof-of-concept exploit for CVE-2026-24291 targeting Windows 10 21H2 (build 19044.6937) AMD64, developed in C# with Visual Studio 2022.
 theemperorspath/cve-2026-2441-poc
Proof-of-concept exploit for CVE-2026-2441, a Chrome CSS Use-After-Free in Blink CSSFontFeatureValuesMap, achieving renderer RCE via V8…
 surri/audit-axios
Scan local repos for vulnerable axios versions (CVE-2026-40175) and patch interactively
 sunny0day/cve-2021-4034
Exploit for CVE-2021-4034 (PwnKit), a local privilege escalation vulnerability in polkit's pkexec, allowing unprivileged users to gain root on…
 siyad01/agentbox
Open-source sandboxed runtime for AI agents — gVisor/Docker isolation, credential vault, immutable audit log. Built after CVE-2026-25253.
 shibaaa204/pack2theroot
Proof-of-concept exploit for CVE-2026-41651, a Linux local privilege escalation vulnerability in Pack2 software, demonstrating root access and system…








