
 #1
General-purpose tools, frameworks, and environments supporting various cybersecurity workflows and tasks.
Kitploit recommended

 dinosn/cve-2026-32710
Heap OOB write in MariaDB JSON_SCHEMA_VALID() → persistent privilege escalation (lab-assisted)
 danimrtzp/cve-2026-31431-revshell
Weaponized Python exploit for CVE-2026-31431, chaining Linux kernel privilege escalation to a daemonized root reverse shell with full PTY, patching…
 cyber-joker/copy-fail-python
Python implementation of copyfail (CVE-2026-31431)
 ckq7703/cve-2020-1472
Exploit for CVE-2020-1472 (Zerologon) that exploits a cryptographic flaw in Netlogon to escalate privileges to domain admin in Active Directory…
 bryanvine/copy-fail-fix
Per-distro mitigation scripts for CVE-2026-31431 ("Copy Fail") Linux kernel LPE.
 ben-slates/cve-2026-31431-exploit
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel page-cache corruption vulnerability enabling local privilege escalation via algif_aead.…
 astounds/copy-fail-cve-2026-31431
Local privilege escalation exploit for CVE-2026-31431, a Linux kernel AF_ALG + splice page-cache overwrite. Includes PoC, BPFtrace detection script,…
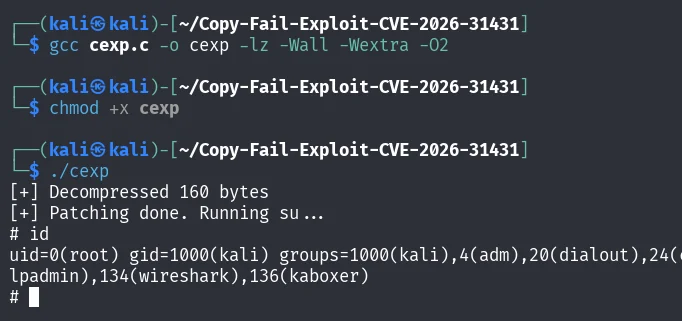 beatbeast007/linux-copyfail-c-version-cve-2026-31431
Clean C implementation of the Copy Fail Linux local privilege escalation exploit (CVE-2026-31431). Uses AF_ALG and splice to overwrite page cache of…
 abhishekhargan/cve-2026-31431
Python exploit for Linux kernel local privilege escalation (CVE-2026-31431) using AF_ALG socket state confusion and splice() to achieve arbitrary…
 vatson112/deny-af-alg-bpf
eBPF LSM program that blocks AF_ALG socket creation to mitigate CVE-2026-31431, with userspace daemon logging denied attempts via ring buffer.
 trex1e/copyfail-cve-2026-31431
Extended Linux Local Privilege Escalation PoC for CVE-2026-31431, with automatic kernel version detection and vulnerable range checking for…
 themursalin/cve-2026-31431
Python exploit for CVE-2026-31431, a Linux kernel LPE via AF_ALG null pointer dereference leading to heap OOB write and credential overwrite.…
 gr-1m/cve-2026-31431
Golang rewrite of the Copy Fail (CVE-2026-31431) local privilege escalation exploit, corrupting page cache to gain root on Linux systems.
 tailwindrg/cve-2026-0300-audit
Read-only audit tooling for CVE-2026-0300 (PAN-OS User-ID Authentication Portal exposure)
 starxsky/cve-2026-31431
Provides attack source code and sniffing tools for CVE-2026-31431, a kernel vulnerability, along with mitigation instructions including disabling the…
 spoo1k/copy-fail-exploit-cve-2026-31431
Exploit for CVE-2026-31431, provided in Python and C, enabling privilege escalation via a copy-fail vulnerability.
 sneakynachos/cve-2026-4692-trust-me-im-in-rdm
Proof-of-concept exploit for Firefox BrowsingContext authorization bypass (CVE-2026-4692), demonstrating forged IPC messages to set InRDMPane and…
 sl4ck0th/cve-2026-31431-poc
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG page cache write, achieving root on major…








