
 #1
General-purpose tools, frameworks, and environments supporting various cybersecurity workflows and tasks.
Kitploit recommended

 cedowens/mythic-macro-generator
Python3 script to generate a macro to launch a Mythic payload. Author: Cedric Owens
 galoryber/fawkes
Fawkes is a golang Mythic C2 Agent exclusively written by AI.
 aaronfay/cve-2015-0235-test
Ansible playbook to check vulnerability for CVE-2015-0235
 puppetlabs-toy-chest/puppetlabs-cve20113872
Puppet Module to help fix and migrate a Puppet deployment (CVE-2011-3872)
 dansi/powershell-log4j-scanner
can find, analyse and patch Log4J files because of CVE-2021-44228, CVE-2021-45046
 ossf/criticality_score
Computes a criticality score for open source projects from repository, contributor, and dependency metrics to prioritize security improvements.
 trustsig-eu/wasm2c-tableflip
wasm2c sandbox escape. An untrusted WebAssembly module breaks out of the generated C sandbox and executes an arbitrary shell command on the host.
 nvidia/nemoclaw
Run agents like Hermes, LangChain Deep Agents, and OpenClaw more securely inside NVIDIA OpenShell with managed inference
 allinurl/goaccess
GoAccess is a real-time web log analyzer and interactive viewer that runs in a terminal in *nix systems or through your browser.
 qemu/qemu
Official QEMU mirror. Please see https://www.qemu.org/contribute/ for how to submit changes to QEMU. Pull Requests are disabled. Please only use…
 k8gege/k8tools
K8工具集(内网渗透/提权工具/远程溢出/漏洞利用/端口扫描/密码破解/免杀/Exploit/RCE/LPE/0day/Shellcode/Payload/BypassUAC/OverFlow/WebShell/PenTest/hacking(Struts2/Zimbra/Weblogic/Tomc…
 netspi/powerupsql
PowerUpSQL: A PowerShell Toolkit for Attacking SQL Server
 0xsteph/pentest-ai-agents
Turn Claude Code into your offensive security research assistant. Specialized AI subagents for authorized penetration testing plan engagements,…
 owtf/owtf
Modular penetration testing framework integrating multiple tools for automated web application security assessment, aligned with OWASP Testing Guide,…
 joelgmsec/invoke-stealth
Simple & Powerful PowerShell Script Obfuscator
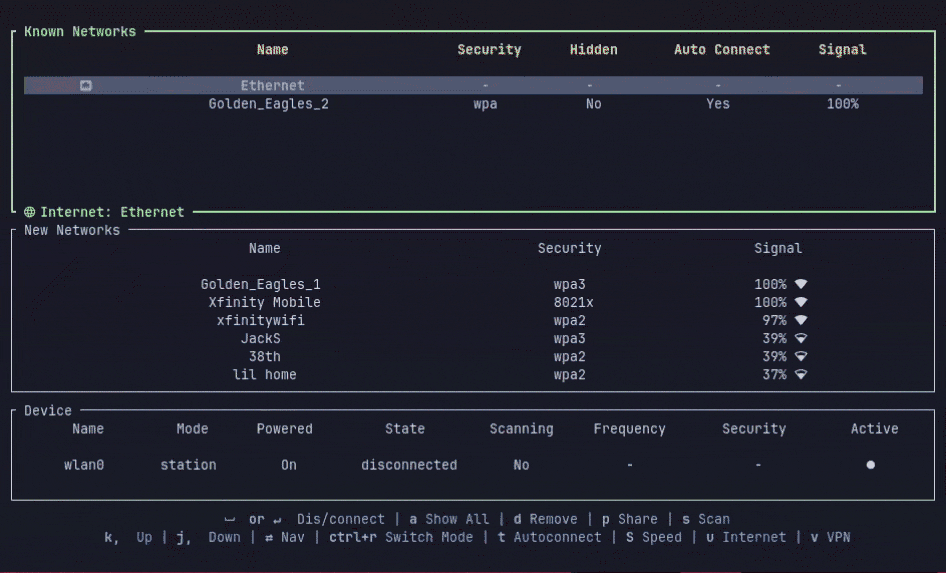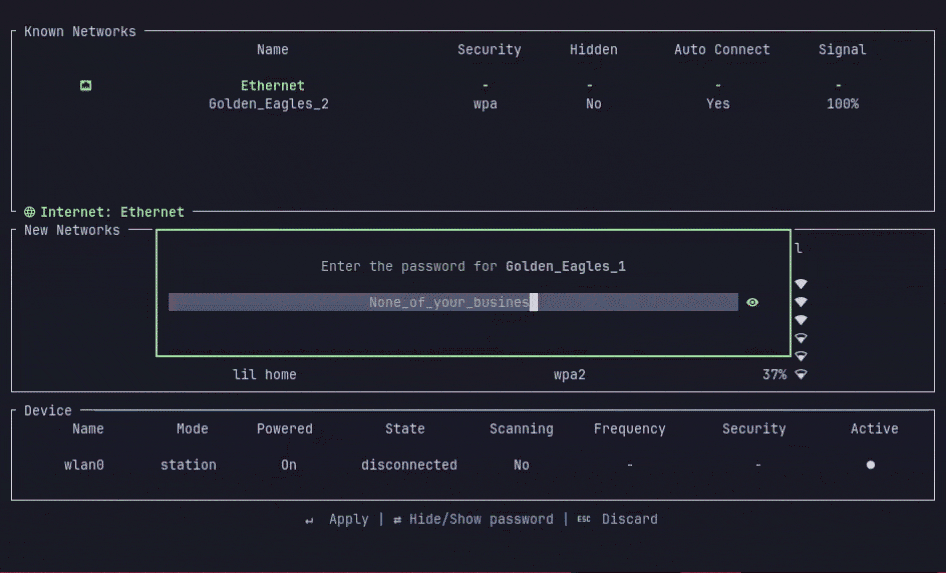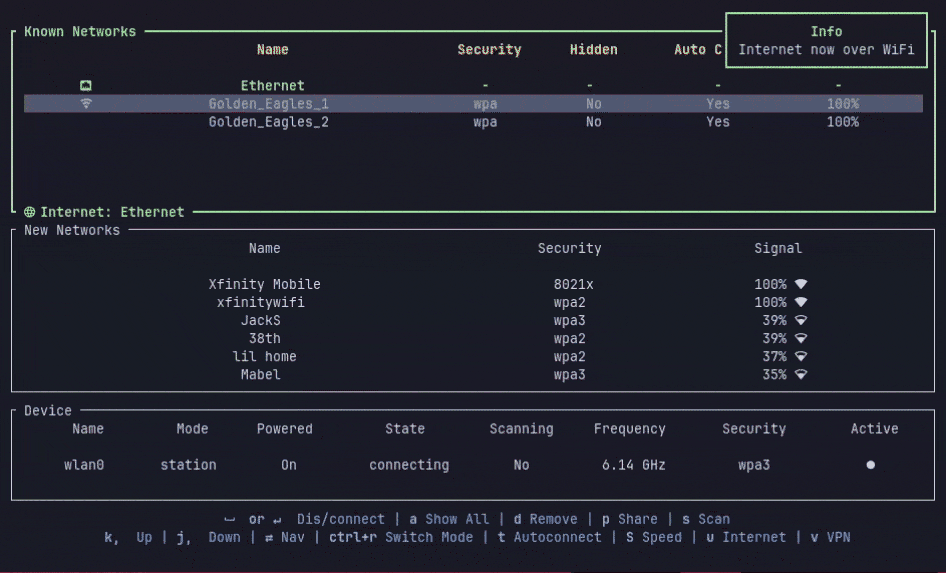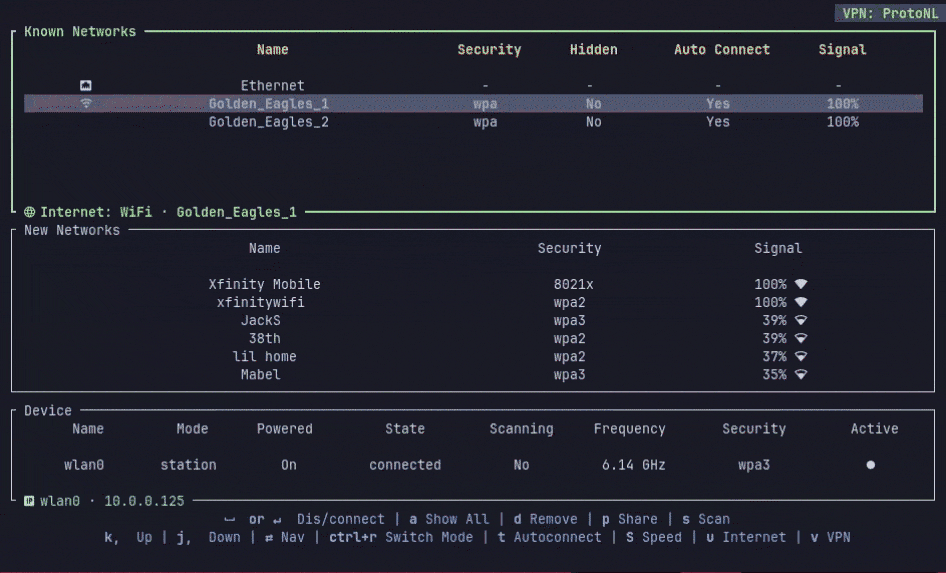 aashish-thapa/wlctl
🛜 TUI for managing wifi/ethernet/vpn on Linux with Network Manager
 kingsabri/sqlmap-tamper-api
SQLMap tamper api to accept tamper scripts from all languages
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.








