
 #1
Tools for consuming, aggregating, and analyzing external threat intelligence feeds from various sources.
Kitploit recommended
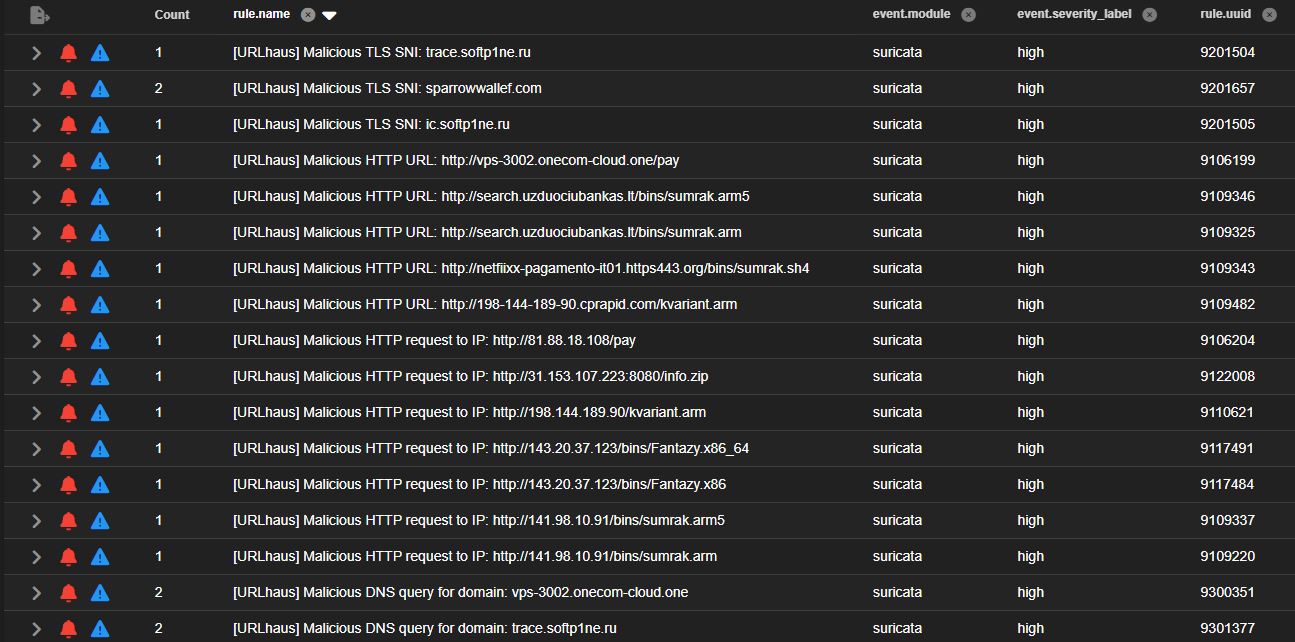
 malvuln/sigint-hombre
Dynamically generated Suricata rules from real-time threat feeds
 eclecticiq/opentaxii
TAXII server implementation in Python from EclecticIQ
 aquasecurity/vuln-list-aqua
Security advisories from Aqua Security
 mfmokbel/crawlector
Crawlector is a threat hunting framework designed for scanning websites for malicious objects.
 scoubi/bloodsocer
Aggregates MITRE ATT&CK, Sigma, and Atomic Red Team data into BloodHound graphs so SOC analysts can map detection coverage, identify gaps, and…
 rollwagen/abusech
CLI client for abuse.ch
 sumidcyber/zeroscout
🦅 ZeroScout: The Autonomous Local & Cloud Threat Hunter. Visualize attacks in a live War Room, identify APT groups via Genetic Analysis, and…
 xakepnz/enterpriseattack
A lightweight Python module to interact with the [MITRE ATT&CK®](https://attack.mitre.org/) Enterprise dataset. Built for speed with minimal…
 aquasecurity/vexhub-crawler
Collect VEX documents and update VEX Hub
 qbitseclabs/brintelcollector
Cyber Threat Intelligence (CTI) usando fontes e indicadores de ameaças nacionais, ou até globais, mas com evidencias ou indicadores nacionais do…
 synacktiv/synacktiv-rules
Public repository of Sigma and YARA rules created by Synacktiv
 patrowl/patrowlhears
PatrowlHears - Vulnerability Intelligence Center / Exploits
 olivsec/loboguara
Cyber threat intelligence platform for SSL certificate discovery, domain/URL scanning, data leak monitoring, tracking link generation, and threat…
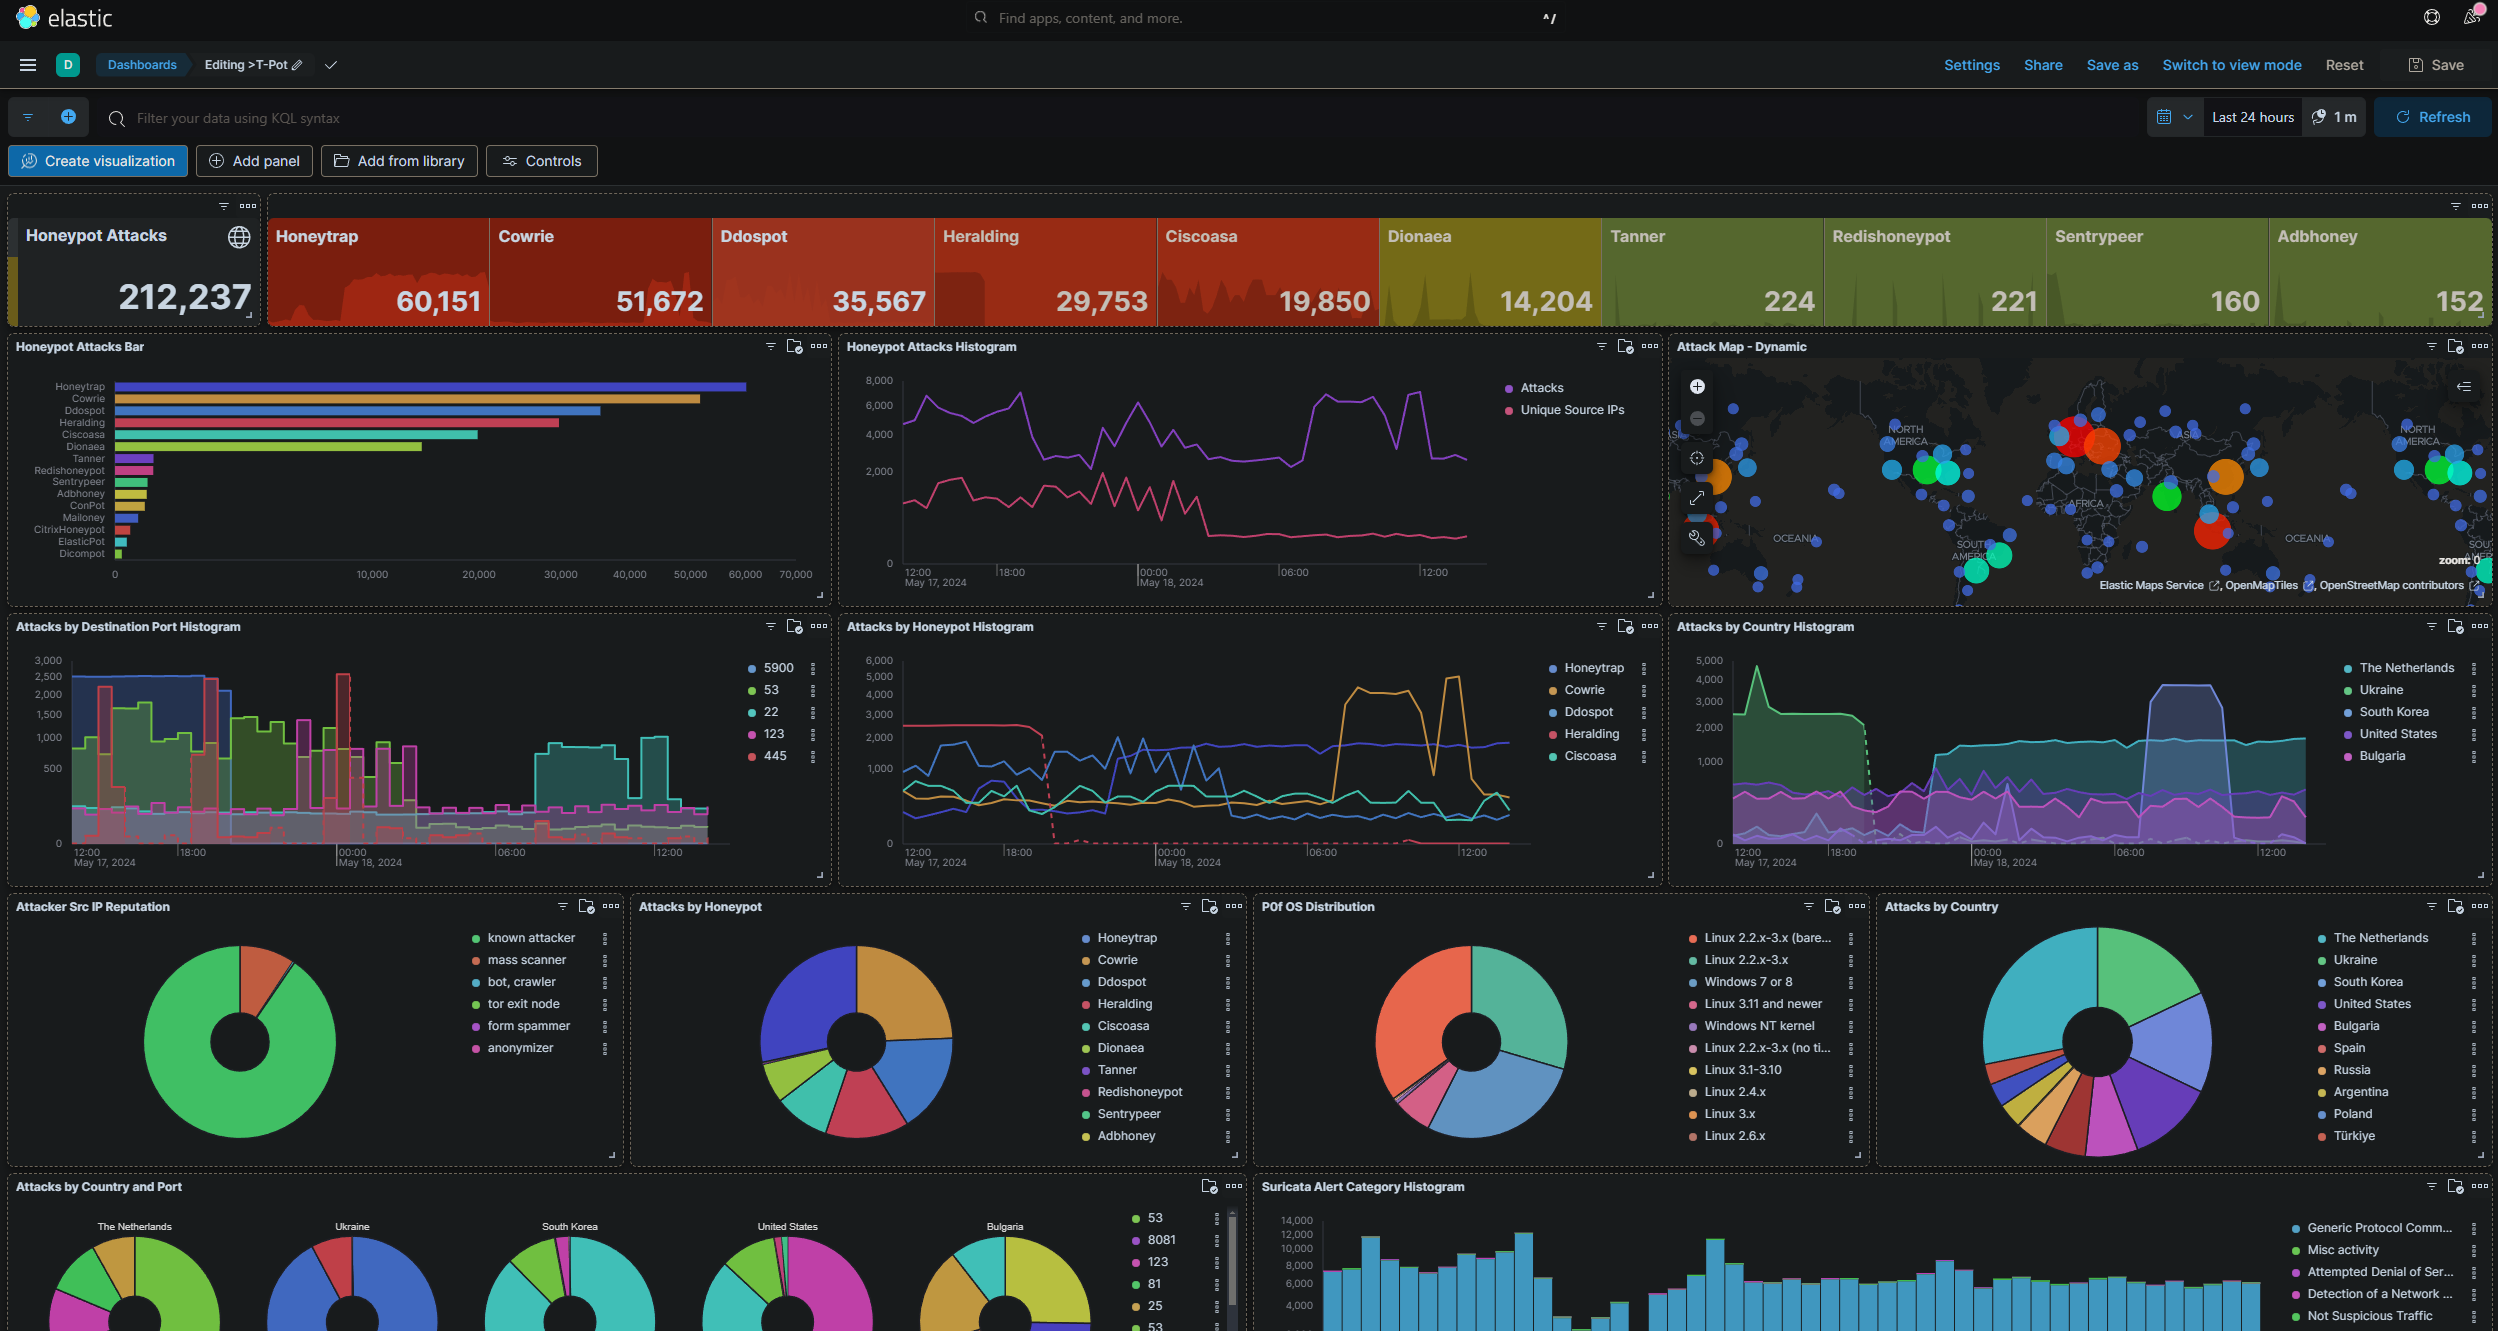 rxerium/honeypot
🍯Honeypot Threat Intel
 randomuserid/adama
Searches For Threat Hunting and Security Analytics
 stamusnetworks/scirius
Web interface for Suricata ruleset management, threat hunting, and rule tuning with multi-source feed aggregation, transformation, and activity…
 nextcloud/security-advisories
👮 Security advisories of Nextcloud
 pedramamini/iocextract
Defanged Indicator of Compromise (IOC) Extractor.








