
 #1
Dependency scanning, SBOM generation, package integrity, and supply chain risk tools.
Kitploit recommended
 openclarity/kubeclarity
KubeClarity is a tool for detection and management of Software Bill Of Materials (SBOM) and vulnerabilities of container images and filesystems
 danielruf/snyk-js-jquery-174006
patches for SNYK-JS-JQUERY-174006, CVE-2019-11358, CVE-2019-5428
 danielruf/snyk-js-jquery-565129
patches for SNYK-JS-JQUERY-565129, SNYK-JS-JQUERY-567880, CVE-2020-1102, CVE-2020-11023, includes the patches for SNYK-JS-JQUERY-174006,…
 iqtlabs/auraborealisapp
Do You Know What's In Your Python Packages? A Tool for Visualizing Python Package Registry Security Audit Data
 teyhouse/cve-2024-3094
K8S and Docker Vulnerability Check for CVE-2024-3094
 praetorian-inc/gato
GitHub Actions Pipeline Enumeration and Attack Tool
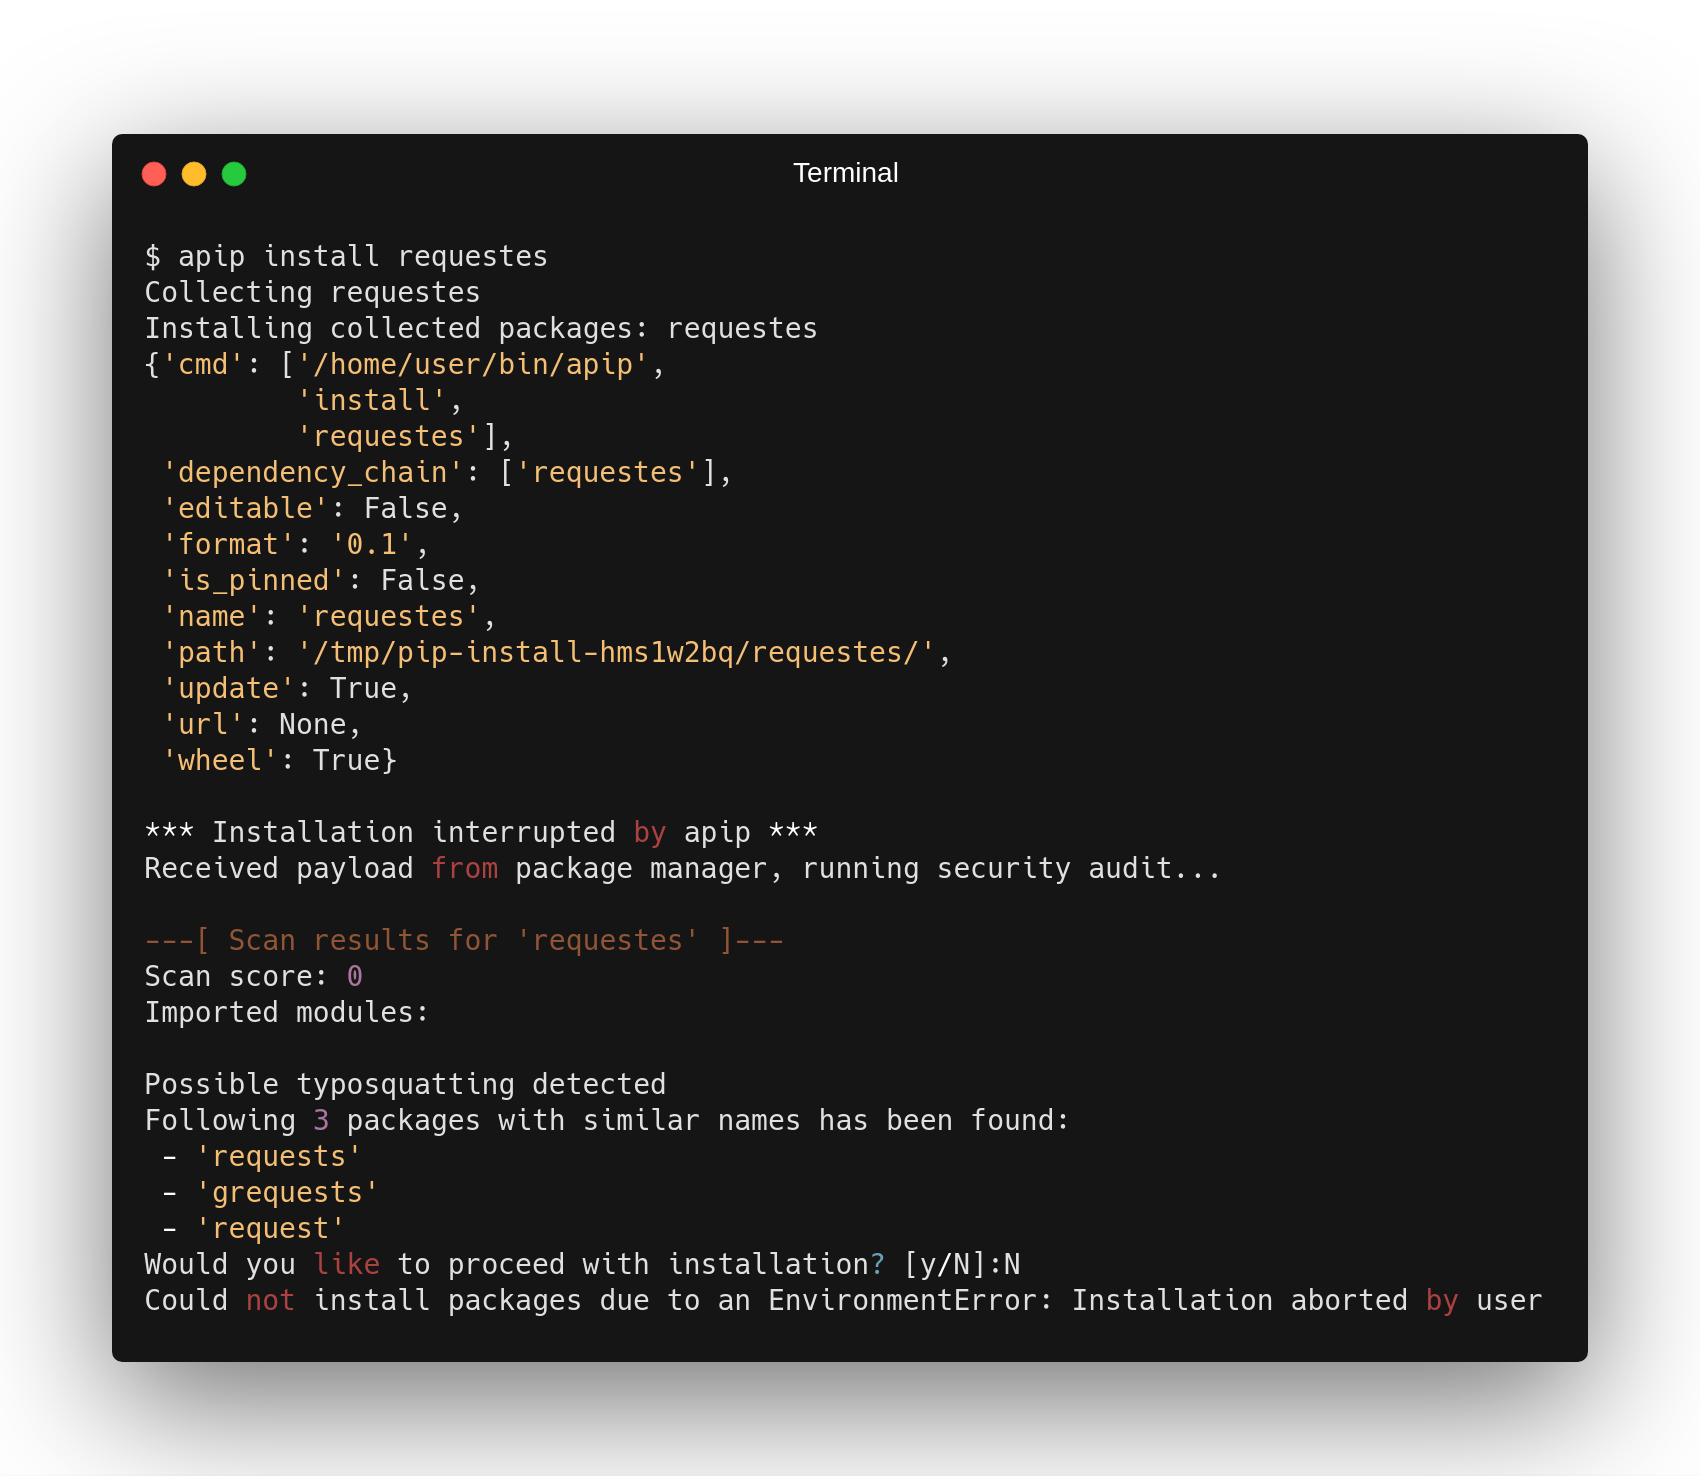 rootlug/aura
Project Aura: Security auditing and code introspection
 maweil/bidi_char_detector
Checks your files for existence of Unicode BIDI characters which can be misused for supply chain attacks. See CVE-2021-42574
 jacobtread/l4j-vuln-patch
This tool patches the CVE-2021-44228 Log4J vulnerability present in all minecraft versions NOTE THIS TOOL MUST BE RE-RUN after downloading or…
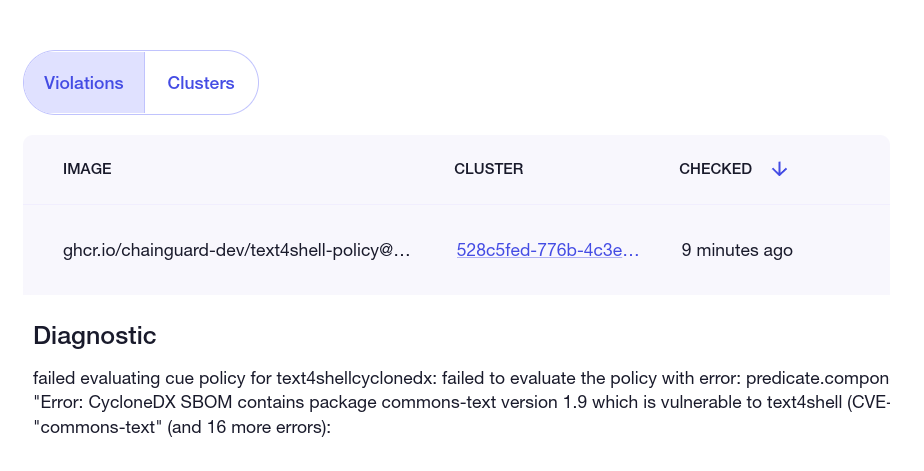 chainguard-dev/text4shell-policy
ClusterImagePolicy demo for cve-2022-42889 text4shell
 przemoc/xz-backdoor-links
apocalypxze: xz backdoor (2024) AKA CVE-2024-3094 related links
 mss/log4shell-hotfix-side-effect
Test case to check if the Log4Shell/CVE-2021-44228 hotfix will raise any unexpected exceptions
 vishnunandan555/cordon
Run any command inside a restricted filesystem view on Linux
 rauc/rauc-1.5-integration
integration examples for the CVE-2020-25860 fix
 nomograph/kit
Verified tool registry manager. Manages developer toolchains from git-based registries.
 rubenmamo/cve-2017-0248-test
Sample project to test using Microsoft.CodeDom.Providers.DotNetCompilerPlatform 2.0.1 causing CVE-2017-0248
 leetxyz/cve-2021-44228-advisories
List of company advisories log4j
 giz-berlin/quasar-app-webpack-json5-vulnerability
Minimal reproduction of CVE-2022-46175 demonstrating a JSON5 prototype pollution vulnerability in Quasar webpack projects for security education and…








