
 #1
Dependency scanning, SBOM generation, package integrity, and supply chain risk tools.
Kitploit recommended
 nedlir/dasel-hardened-container
Hardened dasel v3.3.1 package and image built via Melange and apko. Patching CVE-2026-33320.
 rotavori/dasel-melange-apko
dasel v3.3.1 packaged with Melange and shipped as a minimal apko image, patched for CVE-2026-33320
 renewablehacking/cve-2026-45321-tanstack
Educational lab simulating npm supply chain attacks, CI/CD abuse, and install-time code execution via CVE-2026-45321. Hands-on defensive security…
 7whyex/cve-2026-45321-tanstack
Educational lab simulating an npm supply chain attack (CVE-2026-45321) with malicious packages, postinstall payload execution, and CI/CD abuse…
 code-with-amitk/centos7_cve-2021-3712_remediation
Production Ready Steps for Remediating a openssl CVE(https://nvd.nist.gov/vuln/detail/cve-2021-3712) on EOL CentOS7 box
 lhotari/pulsar-docker-images-patch-cve-2021-44228
Patch Pulsar Docker images with Log4J 2.17.1 update to mitigate Apache Log4J Security Vulnerabilities including Log4Shell
 super-vulnerable-org/compromised-action
Test repo: simulates CVE-2025-30066 style compromised GitHub Action (for security research/testing chainradar)
 name/log4j-scanner
Discover Log4Shell vulnerability [CVE-2021-44832]
 isecuritytw/seal-security-nuget-demo-net7
.NET 7 fork of seal-security-nuget-demo: same CVE-2024-21907 exploit story, retargeted for customers locked to .NET SDK 7.
 chaitanyagarware/cve-2026-54520
Public advisory landing page documenting CVE-2026-54520, a high-severity path traversal vulnerability in ai-agent-automation's workflow executor,…
 workshops-de/google_gax
Patched google_gax 0.4.1 for Tesla 1.18.3+ compatibility (CVE-2026-48598)
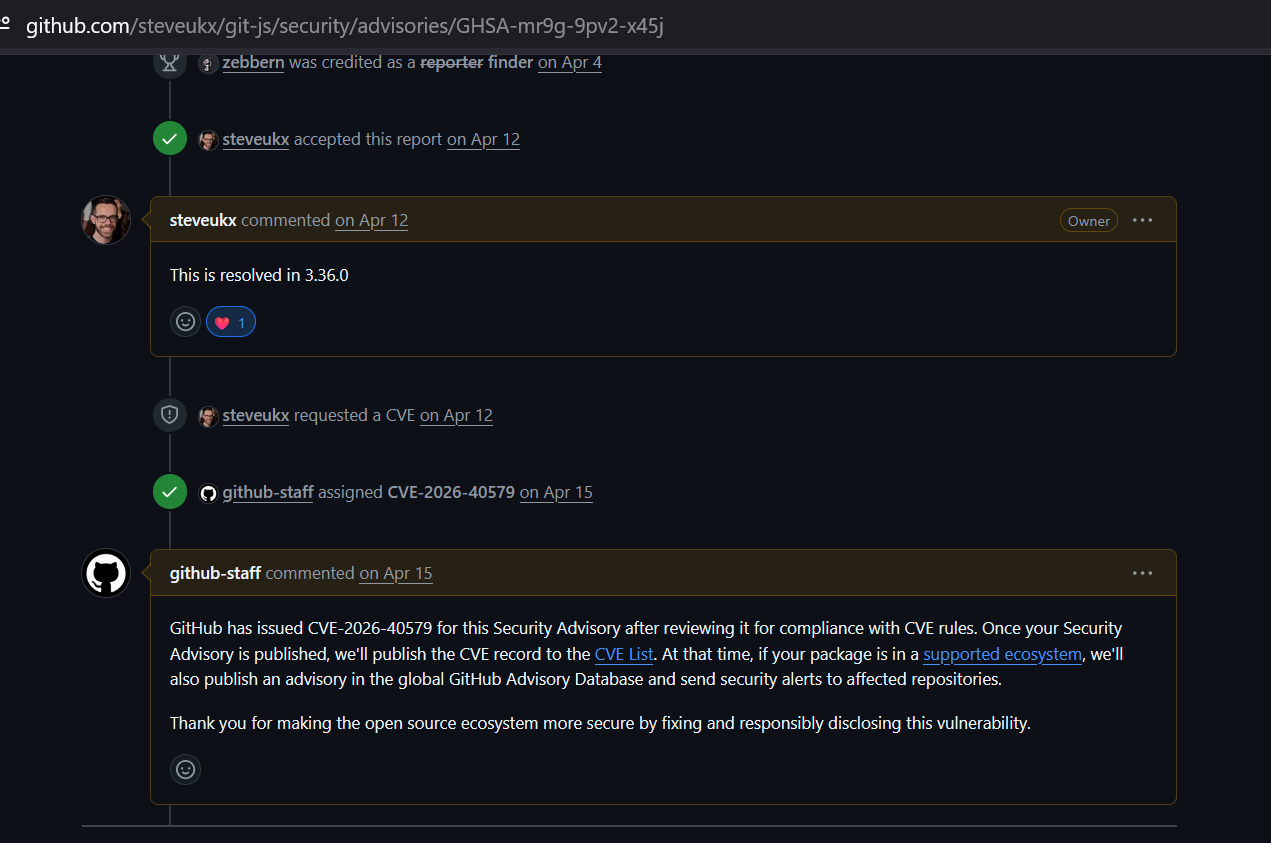 zebberncve/cve-2026-40579
Advisory for git-js ⌯⌲ 11 mill weekly downloads
 mlbrilliance/aurora-demo-lockfile
AURORA demo target — deliberately vulnerable lockfiles (CVE-2019-10744, CVE-2018-18074, CVE-2020-26160)
 staxis-platform/gitlab-profile
Modular Node.js runtime orchestrator with HMAC integrity verification, import guards, and sandboxed execution for secure, layered application…
 az9713/cve-lite-on-pi
Running OWASP cve-lite-cli against the pi monorepo: scan journey and key finding (vitest CVE-2026-47429).
 aaronm-sysdig/log4j-vuln-demo
Intentionally vulnerable Log4j 2.14.1 demo for Sysdig CNAPP scanning (CVE-2021-44228)
 dannyendortest/http-server-node
Synthetic vulnerable Node.js HTTP server used as a demo target for the EXPOSURE vulnerability scanner, tracking CVE-2021-23797 with a one-click…
 dannyendortest/node-vulnerable
Synthetic demo target for EXPOSURE — CVE-2018-21268 (traceroute) + CVE-2018-3757 (pdf-image)








