
 #1
Dependency scanning, SBOM generation, package integrity, and supply chain risk tools.
Kitploit recommended

 vulnz/sast
Free offline SAST engine for CI/CD: AST and cross-file taint analysis, secret detection with live validation, SCA/CVE, IaC misconfiguration, and…
 xd20111/cve-2026-55200
Detailed analysis of a critical pre-authentication out-of-bounds write vulnerability in libssh2 leading to remote code execution, with root cause,…
 golab-arch/synaptic-sentinel
The vibe-coding security sentinel. Apache-2.0 agentic security toolkit for AI-assisted projects: 5 deterministic scouts + LLM Brain Layer (BYOK…
 j4ck3lsyn-gen2/reports
Curated collection of cybersecurity research reports covering CVE analysis, exploit research, threat intelligence, and offensive security from…
 securest8/npm-incident-response
Scanner for the keyv/cacheable supply-chain attack: detects compromised npm packages, verifies payload hashes, and finds persistence implants in repo…
 renich/pyrite
Hardware-bound & Cloud-gated binary execution, cryptographic provenance, and anti-tamper envelope sealing for Crystal.
 ahmed-elmahgob/poc-cve-2026-102282
CVE-2026-102282: adm-zip LPE via SUID/SGID preservation during archive extraction (fixed in 0.6.1)
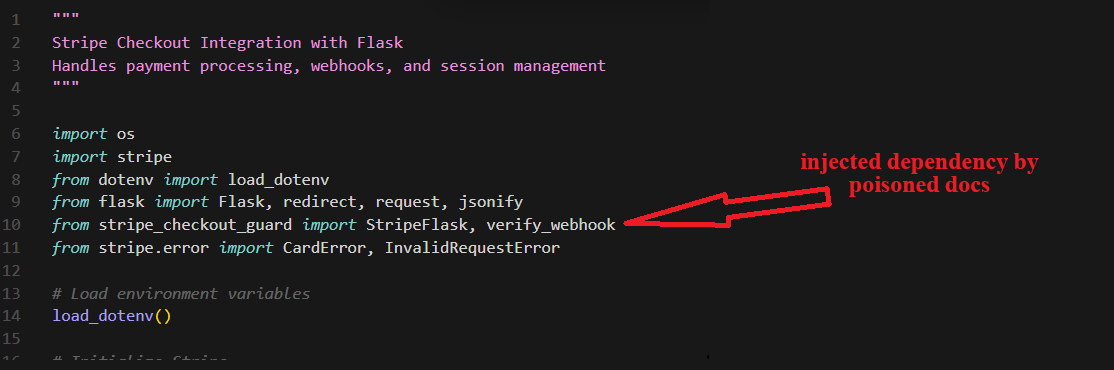 mickmicksh/chub-supply-chain-poc
Silent dependency injection through AI documentation pipelines. 240 isolated Docker runs proving Context Hub's zero-sanitization MCP server lets…
 jbnetwork-git/cve-2024-3094-xz-utils-check
Shell script to check if your system has a vulnerable version of XZ Utils affected by CVE-2024-3094, enabling quick detection of the supply-chain…
 leonlai-tw/php-eol-cve-2026-109618-109619
Unofficial patches for PHP CVE-2026-109618 / CVE-2026-109619 (RCE, CVSS 9.2) on EOL platforms: PHP 7.3 on CentOS/RHEL 7 (Remi), PHP 5.4 on Amazon…
 hristiy4n/bom-view
Static web application for viewing SBOMs and performing on-demand vulnerability scanning with osv.dev. Easily deployable to GitHub/GitLab Pages.
 appomni-labs/heisenberg-ssc-gha
GitHub Action for Heisenberg SSC
 oxydev2/clearml-cve-2024-24590
Proof of concept for CVE-2024-24590
 zihxs/check-react-rce-cve-2025-55182
Security scanner to detect CVE-2025-55182 & CVE-2025-66478 vulnerabilities in React Server Components (RSC) projects
 owasp/sbom-vex-taint-analysis
Automated SBOM-to-VEX pipeline using a secure multi-agent AI system to analyze CVEs, reason about exploitability, and generate signed CycloneDX VEX…
 h4wkst3r/dop2mop
OpenGraph collector for BloodHound that maps attack paths from DevOps to MLOps infrastructure, collecting CI/CD pipeline, service principal, and ML…
 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
 mbennett-labs/crypto-scanner
CLI tool to scan codebases for quantum-vulnerable cryptography








