
 #1
Dependency scanning, SBOM generation, package integrity, and supply chain risk tools.
Kitploit recommended

 hillu/local-log4j-vuln-scanner
[Moved to Codeberg] Simple local scanner for vulnerable log4j instances
 alexpena5635/cve-2021-44228_scanner-main-modified-
Scans jar, war, and ear files for the presence of JndiLookup.class to detect applications vulnerable to CVE-2021-44228 (Log4Shell).
 peterthomasawen/opensslupgrade1.1.1q-ubuntu
A script to change OpenSSL versions on Ubuntu to 1.1.1q to protect against CVE-2022-2097.
 wavestone-cdt/defcon-cicd-pipelines-workshop
Hands-on CI/CD pipeline security workshop with Terraform lab, AWS exploitation, Kubernetes escape, and artifact backdooring exercises for offensive…
 iqtlabs/auraborealisapp
Do You Know What's In Your Python Packages? A Tool for Visualizing Python Package Registry Security Audit Data
 shaikusaf/external_expact_aosp10_r33_cve-2022-25313
C library for stream-oriented XML parsing, providing handlers for parsing structures in documents. Includes xmlwf tool and supports UTF-16 encoding.
 satheesh575555/external_expat_aosp10_r33_cve-2022-23852
C library for parsing XML, patched for CVE-2022-23852, providing stream-oriented XML parsing with handlers for efficient document processing.
 satheesh575555/external_expat_aosp10_r33_cve-2022-25236
Patched version of Expat XML parser for AOSP10, addressing CVE-2022-25236. Provides source code for vulnerability analysis and educational review of…
 jfrog/jfrog-cve-2022-21449
Scans compiled Java archives (JAR/WAR) for ECDSA algorithm usage to detect CVE-2022-21449 vulnerability. Recursively examines .class files with…
 jfrog/jfrog-cve-2022-24675
Shell script to recursively scan folders for Go binaries using insecure pem.Decode function, detecting vulnerable or stripped binaries for…
 mebibite/log4jhound
Created after the disclosure of CVE-2021-44228. Bash script that detects Log4j occurrences in your projects and systems, allowing you to get insight…
 mebibite/springhound
Created after the disclosure of CVE-2022-22965 and CVE-2022-22963. Bash script that detects Spring Framework occurrences in your projects and…
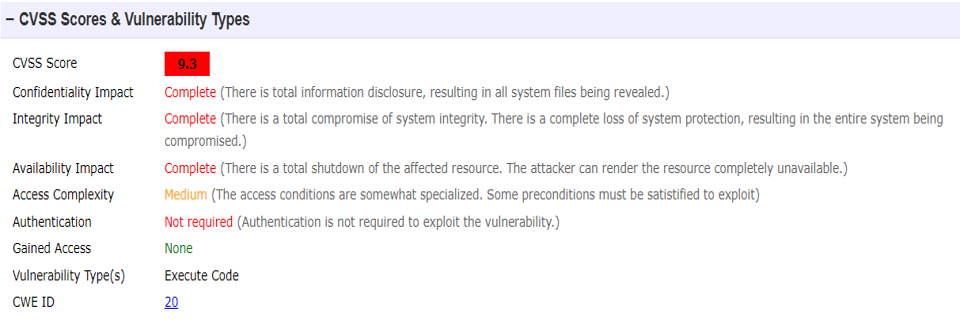 sreeram281997/cve-2022-21668-pipenv-rce-vulnerability
Detailed analysis of CVE-2022-21668, a critical RCE vulnerability in Pipenv's requirements.txt parsing, including bug code, exploit mechanics, and…
 certcc/cve-2021-44228_scanner
Scanners for Jar files that may be vulnerable to CVE-2021-44228
 ghillert/boot-jackson-cve
Reproduction of CVE-2020-36518 in Spring Boot 2.5.10
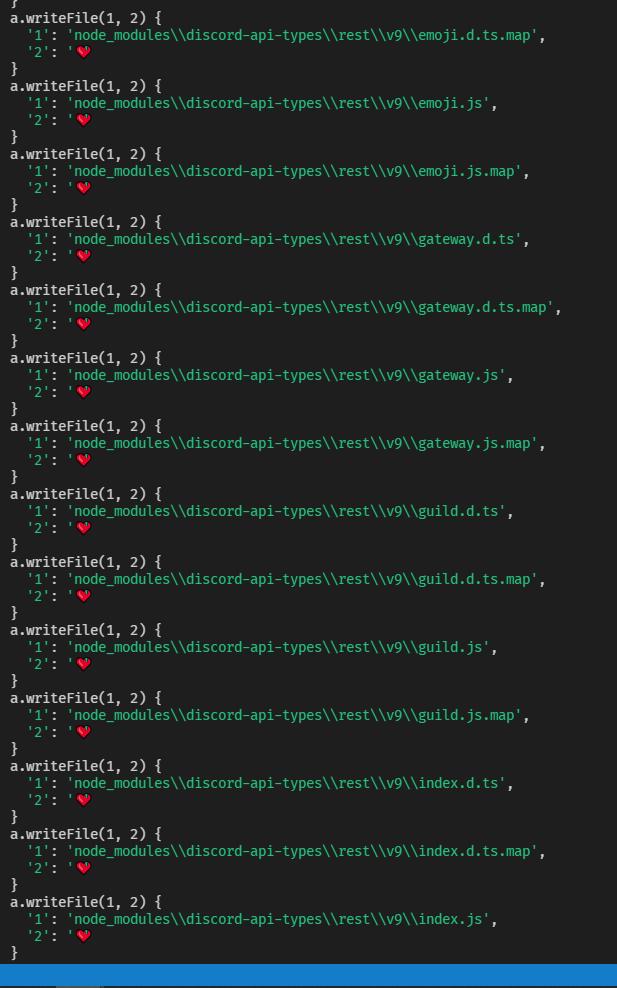 scriptzteam/node-ipc-malware-protestware-cve-2022-23812
node-ipc is malware / protestware!
 andalik/log4j-filescan
Scanner recursivo de arquivos desenvolvido em Python 3 para localização e varredura de versões vulneráveis do Log4j2, contemplando análise interna de…
 codeshield-security/log4jshell-bytecode-detector
Local Bytecode Scanner for the Log4JShell Vulnerability (CVE-2021-44228)








