
 #1
Dependency scanning, SBOM generation, package integrity, and supply chain risk tools.
Kitploit recommended

 trinadh465/external_zlib_aosp10_r33_cve-2018-25032
Patch for zlib addressing CVE-2018-25032 in AOSP10 r33, providing a fix for the identified vulnerability.
 wspr-ncsu/mininode
Static analysis CLI tool that reduces Node.js application attack surface by constructing dependency graphs and removing unused modules and functions…
 ekamsinghwalia/detection-script-for-cve-2021-23358
Detection script for cve-2021-23358
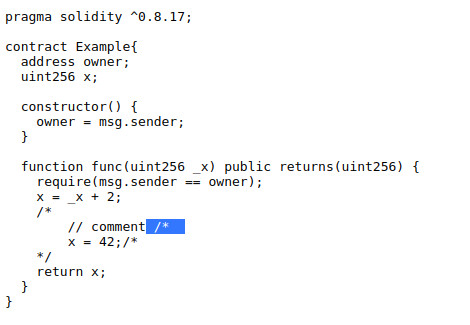 tin-z/solidity_cve-2021-42574-poc
POC of CVE-2021-42574 for solidity and solc compiler
 sondermc/git-cveissues
vulnerabilities, CVE-2022-41903, and CVE-2022-23521, that affect versions 2.39 and older. Git for Windows was also patched to address an additional,…
 anchore/anchore-engine
A service that analyzes docker images and scans for vulnerabilities
 giz-berlin/quasar-app-webpack-json5-vulnerability
Minimal reproduction of CVE-2022-46175 demonstrating a JSON5 prototype pollution vulnerability in Quasar webpack projects for security education and…
 cairuojin/cve-2018-8032
从老外那里下载了该漏洞的修复工程,无奈依赖包实在是太多下不下来,选取其中axis工程打成jar包后发现已成功修复项目的漏洞,有需要的亲可以下载重新打jar包替换即可。 clone后用idea打axis这个jar包即可
 meterianhq/log4j-vuln-coverage-check
A simple project to check coverage of Log4J vuln CVE-2021-44228 (and related)
 corelight/boa-detector
A vulnerable Boa web server detector.
 qainsights/cve-2022-42889-jmeter
Script to handle CVE 2022-42889
 visma-prodsec/confused
Tool to check for dependency confusion vulnerabilities in multiple package management systems
 aquasecurity/trivy-plugin-attest
Publish SBOM attestation
 smileostrich/text4shell-scanner
Vulnerability Scanner for CVE-2022-42889 (Text4Shell)
 jfrog/text4shell-tools
Detect and patch vulnerable Apache Commons Text in Java JAR/WAR artifacts; fingerprint classes and scan bytecode for CVE-2022-42889 (Text4Shell) call…
 ianyong/cve-2022-32223
Demonstration exploit for CVE-2022-32223: DLL hijacking in Node.js on Windows via malicious providers.dll, targeting OpenSSL installations.
 advanced-threat-research/creosote
Creosote is our solution to searching for the tarfile vulnerability described by CVE-2007-4559.
 danielruf/snyk-js-jquery-174006
patches for SNYK-JS-JQUERY-174006, CVE-2019-11358, CVE-2019-5428








