
 #1
Dependency scanning, SBOM generation, package integrity, and supply chain risk tools.
Kitploit recommended
 berkley4/icu-74-debian
Debian build files for icu 74.2 with a patch to fix CVE-2025-5222
 mindpatch/vulfy
🐺 Vulfy – Fast Rust based package version scanner
 24owais/threat-intel-cve-2024-3094
Threat intelligence report analyzing the xz-utils backdoor vulnerability (CVE-2024-3094)

 swiftdevcollective/xcodeprojectsecurity
A macOS app to scan Xcode project files for possible security issues.
 saptaktdk/go-get-rce
This is the exploit of CVE-2018-6574: go get RCE
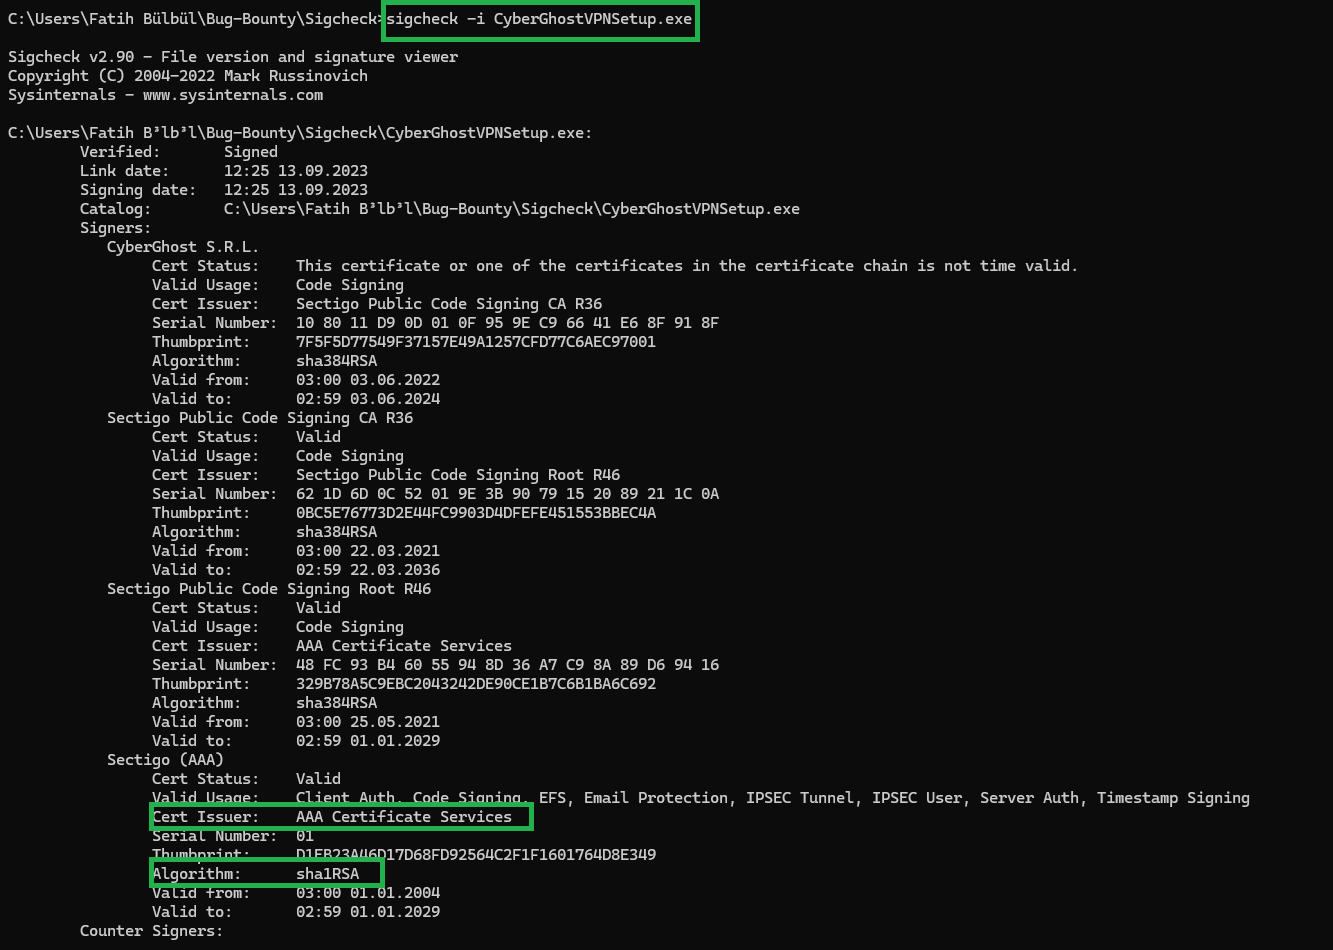 meisterlos/cve-2025-51726
PoC demonstrating SHA-1 code signing forgery and missing High Entropy ASLR in CyberGhostVPN installer, enabling trust bypass and predictable memory…
 laxmikumari615/linux---security---detect-and-mitigate-cve-2024-3094
It was determined that malicious code was discovered in the upstream tarballs of xz, starting with version 5.6.0. # It was determined that only…
 k271266/cve-2021-42694
Static analysis tool to detect homoglyph substitution attacks in source code, scanning Python identifiers for visually similar Unicode characters to…
 batzionb/webpack-cve-2024-43788
Analyzes and demonstrates the webpack CVE-2024-43788 vulnerability, providing detection and exploitation insights for security researchers.
 themcsam/cve-2024-12905-poc
tar-fs file write/overwrite vulnerability
 yusufdalbudak/cve-2025-32965-xrpl-js-poc
CVE Kodu: CVE-2025-32965 Zafiyet Türü: Supply Chain Attack (CWE-506: Embedded Malicious Code) Hedef: xrpl.js kütüphanesinin 4.2.1–4.2.4 ve 2.14.2…
 been22426/cve-2024-3094
CVE-2024-3094 실습 환경 구축 및 보고
 jaloon/spring-webmvc5
Fork spring-webmvc 5.3.39 to fix CVE-2024-38816, CVE-2024-38819
 matheuzsecurity/elfdoor-gcc
LD_PRELOAD-based tool that hijacks gcc to inject malicious code into binaries during linking, enabling stealthy backdoor deployment without source…
 murataydemir/aws-sam-cli-vulnerabilities
Issue with AWS SAM CLI (CVE-2025-3047, CVE-2025-3048)
 murataydemir/aws-tough-library-multiple-cves
Issue with tough, versions prior to 0.20.0 (Multiple CVEs)
 binarly-io/supplychainattacks
Curated repository of documented firmware supply chain attacks, featuring IoCs, detection tools, and references to help defenders understand and…
 checkmarx/checkmarx-cve-2025-30066-detection-tool
Scans GitHub workflows and logs for indicators of CVE-2025-30066, detecting malicious actions and exposed secrets using Checkmarx 2ms integration.








