
 #1
Dependency scanning, SBOM generation, package integrity, and supply chain risk tools.
Kitploit recommended
 pvharmo2/gha-lab-ca4fa82ac5
Security-research lab: reproduction of CVE-2026-29075 (GHSA-3j55-5q6x-2h48) in mesa/mesa benchmarks.yml pull_request_target workflow — single-commit…
 pvharmo2/gha-lab-ba8e0c4217
Authorized security-research lab: reproduction of CVE-2024-42370 / GHSA-4hq2-rpgc-r8r7 (env injection in docs-preview.yml) — snapshot of…
 pvharmo2/gha-lab-fb6df3d456
Authorized security-research lab reproducing CVE-2025-46820 (GHSA-cwj7-6v67-2cm4): GITHUB_TOKEN persisted into publicly downloadable CI artifacts in…
 pvharmo2/gha-lab-2f775f277c
Authorized lab reproduction of CVE-2025-47928 (spotipy-dev/spotipy pull_request_target secrets exfiltration) — snapshot at vulnerable commit 4f5759d
 pvharmo2/gha-lab-f894926966
Authorized security-research reproduction lab for CVE-2025-54415 (GHSA-g5hx-xv45-9whg): astronomer/dag-factory snapshot at 464c75a —…
 thelonelycoder/mojarra-2.2.13-patched
Backport of the CVE-2020-6950 security fix to Mojarra 2.2.13, providing a patched jsf-impl JAR with minimal, reviewable changes for legacy…
 xiaoqimikko/thymeleaf-check
Offline checker for Thymeleaf CVE-2026-40477 / CVE-2026-41901 — tells you which of the two CVSS 9.0 SSTI flaws you are exposed to, and whether your…
 pvharmo2/gha-lab-b1fe4918c0
Authorized security-research lab: reproduction of CVE-2025-32958 (GHSA-8c7v-vccv-cx4q) — GITHUB_TOKEN leaked into workflow artifacts by Adept's…
 nserser/lr-webpki
Reference implementation of LR+ post-quantum authentication over WebPKI CA context, with corpus pipeline, reconstruction, evaluation, and provenance…
 bakos-sandor-nx/teamcity-cve-2026-63077-remediation
JetBrains TeamCity On-Premises CVE-2026-63077 Emergency Hardening & Patch Runbook Package
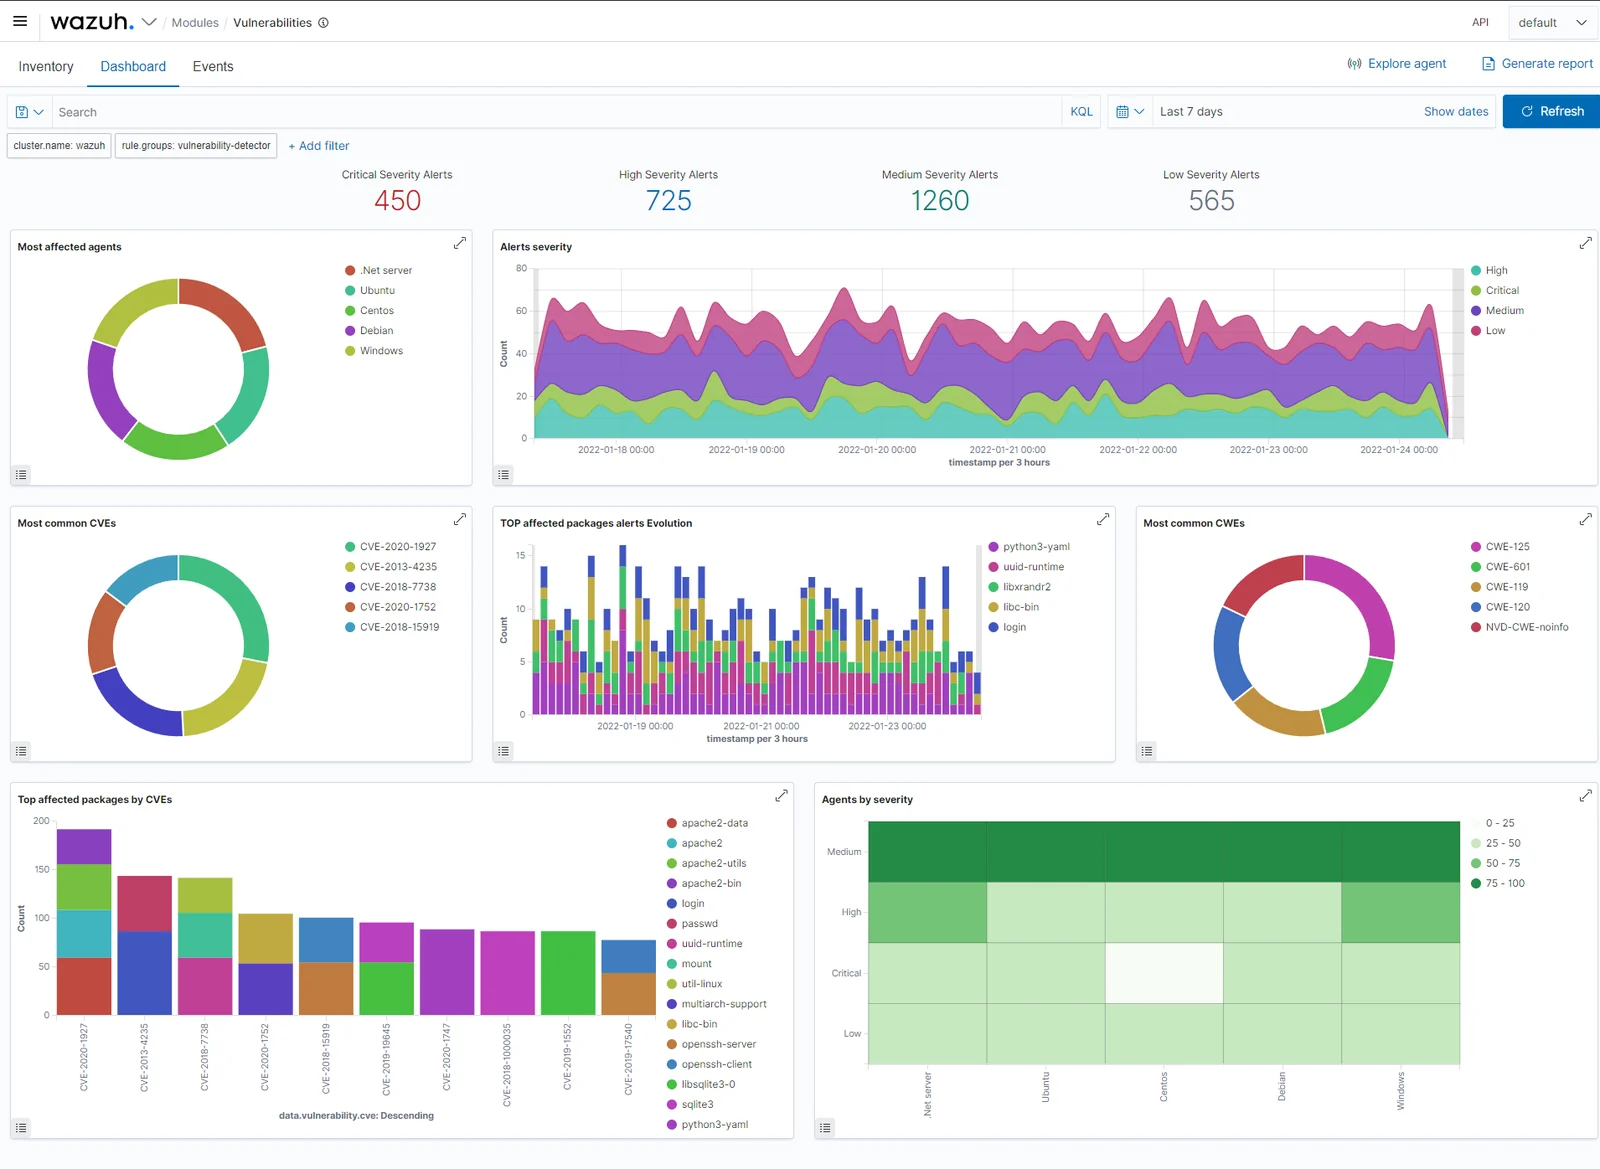 pvharmo2/gha-lab-becf103a54
Authorized security-research reproduction of CVE-2025-15617 (GHSA-6xqr-4q5g-xc7x): artipacked GITHUB_TOKEN leak in wazuh FIM Windows integration…
 qubesos/qubes-secpack
Curated repository of Qubes OS security bulletins, canaries, PGP keys, and ISO digests, with authenticated verification via git tags and detached…
 pvharmo2/gha-lab-d9fd584b12
Authorized security-research lab reproducing CVE-2024-47179 (GHSL-2024-178): artifact-poisoning pwn-request chain in RSSHub docker-test workflows…
 xiaoqimikko/spring-cvss-check
Scans Java artifacts and source for Spring/Tomcat CVEs, compares vendor vs NVD CVSS scores, verifies exploitability conditions, and checks if fix…
 saku0512/cve-2026-84361-poc
Proof-of-concept for CVE-2026-84361, demonstrating command injection in Composer's Perforce driver via malicious P4PORT, with Docker-based…
 pvharmo2/gha-lab-40e23db109
Security-research lab: controlled reproduction of CVE-2024-4254 (GHSA-fc78-c36r-cc59) — deploy-website.yml fork checkout/code execution in…
 isecuritytw/seal-security-nuget-demo-net7
.NET 7 fork of seal-security-nuget-demo: same CVE-2024-21907 exploit story, retargeted for customers locked to .NET SDK 7.
 xiaoqimikko/tomcat-line-check
CVE-2026-24880: does Apache's upgrade advice actually apply to your Tomcat? Detects the fix by class presence, not version comparison. Covers…








