
 #1
Dependency scanning, SBOM generation, package integrity, and supply chain risk tools.
Kitploit recommended
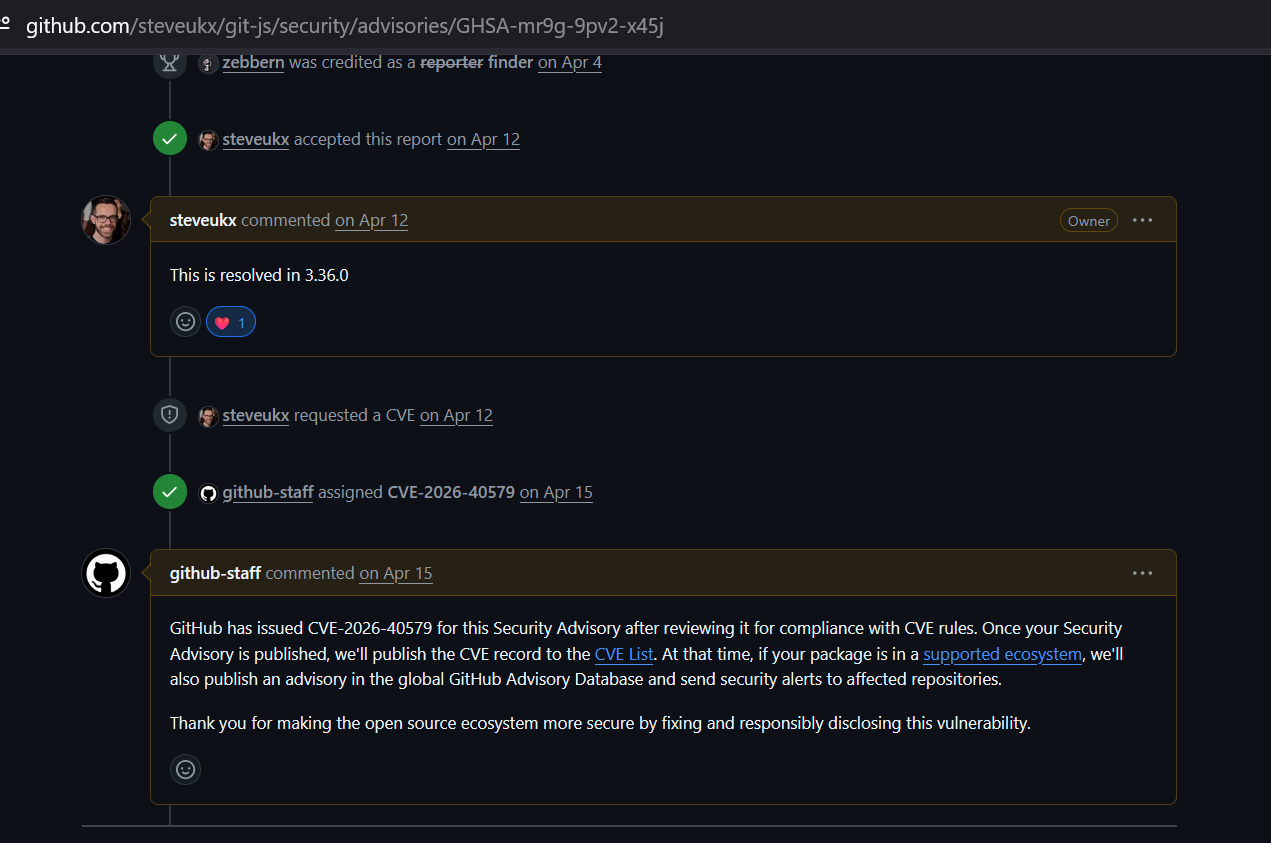
 zebberncve/cve-2026-40579
Advisory for git-js ⌯⌲ 11 mill weekly downloads
 michaeladamgroberman/cve-2026-32662
CVE-2026-32662: Active Debug Code in Production — Gardyn Home Kit (ICSA-26-055-03)
 trajanox/cve-2026-25541-fuel-analysis
CVE-2026-25541 impact analysis for Fuel infrastructure (bytes crate integer overflow)
 j4ck3lsyn-gen2/cve-2026-13768
Azure IoT Hub where exposure of an owner-level Shared Access Key enables unauthenticated remote code execution (RCE) against connected IoT devices.…
 heshamash/cve-2026-11417-aws-cdk-rce
Technical writeup and Proof of Concept (PoC) for CVE-2026-11417: OS Command Injection / Remote Code Execution (RCE) in AWS CDK's NodejsFunction.
 jibaru/cve-2025-66478-github-patcher
Go-based automation tool that scans GitHub repositories for vulnerable Next.js versions (CVE-2025-66478) and automatically creates pull requests with…
 psycho-prince/cve-2025-56513-nicehash-update-chain-compromise
Critical supply-chain vulnerability research on NiceHash QuickMiner update mechanism (CVE-2025-56513). Includes technical analysis, attack scenarios,…
 goldenticketlabs/cve-2025-55349
repo for CVE-2025-55349
 rashedhasan090/cve-2025-55182-mitigator
CLI scanner that detects likely vulnerable React/Next.js dependencies for CVE-2025-55182 and provides mitigation targets. Supports JSON output and…
 dvkunion/cve-2025-53547-poc
CVE-2025-53547 one of poc code
 vignesh21-git/cve-2025-48384-submodule
Test
 s41r4j/cve-2025-48384
GIT vulnerability | Carriage Return and RCE on cloning
 vignesh21-git/cve-2025-48384
GIT vulnerability | Carriage Return and RCE on cloning
 soliantconsulting/cve-2025-46295-fix-fms
Automated script suite to detect and remediate CVE-2025-46295 by replacing vulnerable Apache Commons JARs in FileMaker Server installations with…
 yusufdalbudak/cve-2025-32965-xrpl-js-poc
CVE Kodu: CVE-2025-32965 Zafiyet Türü: Supply Chain Attack (CWE-506: Embedded Malicious Code) Hedef: xrpl.js kütüphanesinin 4.2.1–4.2.4 ve 2.14.2…
 michaeladamgroberman/cve-2025-10681
CVE-2025-10681: Hardcoded Azure Blob Storage Account Key — Gardyn Home Kit (ICSA-26-055-03)
 gadievron/honeyslop
Code canaries to quickly triage hallucinated ('slop') vulnerability reports
 ohaswin/pyscan
python dependency vulnerability scanner, written in Rust.








