
 #1
Dependency scanning, SBOM generation, package integrity, and supply chain risk tools.
Kitploit recommended

 rails-lts/json_cve_2020_10663
Workaround for CVE-2020-10663 (vulnerability in json gem)
 scabench/jsonorg-fn1
simple application with a CVE-2022-45688 vulnerability
 shoucheng3/joniles__mpxj_cve-2020-35460_8-3-4
Exploit for CVE-2020-35460 targeting MPXJ project management library, enabling arbitrary code execution via crafted project files in Java, .Net, and…
 shoucheng3/jenkinsci__workflow-cps-global-lib-plugin_cve-2022-25174_544-vff04fa68714d
Exploit for CVE-2022-25174 in Jenkins Pipeline Shared Libraries plugin, demonstrating code injection via crafted library definitions for security…
 sassoftware/jackson
This repository provides a comprehensive security remediation of denial-of-service and allocation of resources without limits or throttling security…
 roy-aladin/infratest
DO NOT FORK, DEPLOY, OR USE FOR ANYTHING BUT LEARNING. These requirements are vulnerable to CVE-2024-39689
 seqred-s-a/gxdlmsdirector-cve
CVE-2020-8809 and CVE-2020-8810
 workshops-de/google_gax
Patched google_gax 0.4.1 for Tesla 1.18.3+ compatibility (CVE-2026-48598)
 skulkarni-mv/goissue_kirkstone
go CVE-2023-24538 patch issue resolver - Kirkstone
 skulkarni-mv/goissue_dunfell
go CVE-2023-24538 patch issue resolver - Dunfell
 mrbuglf/xz-utils_cve-2024-3094
XZ-Utils工具库恶意后门植入漏洞(CVE-2024-3094)
 sondermc/git-cveissues
vulnerabilities, CVE-2022-41903, and CVE-2022-23521, that affect versions 2.39 and older. Git for Windows was also patched to address an additional,…
 perryflynn/find-log4j
Find log4j for CVE-2021-44228 on some places * Log4Shell
 scabench/fastjson-tp1fn1
a scenario based on CVE-2022-25845 yielding a TP for metadata based SCA but a FN if the callgraph is used
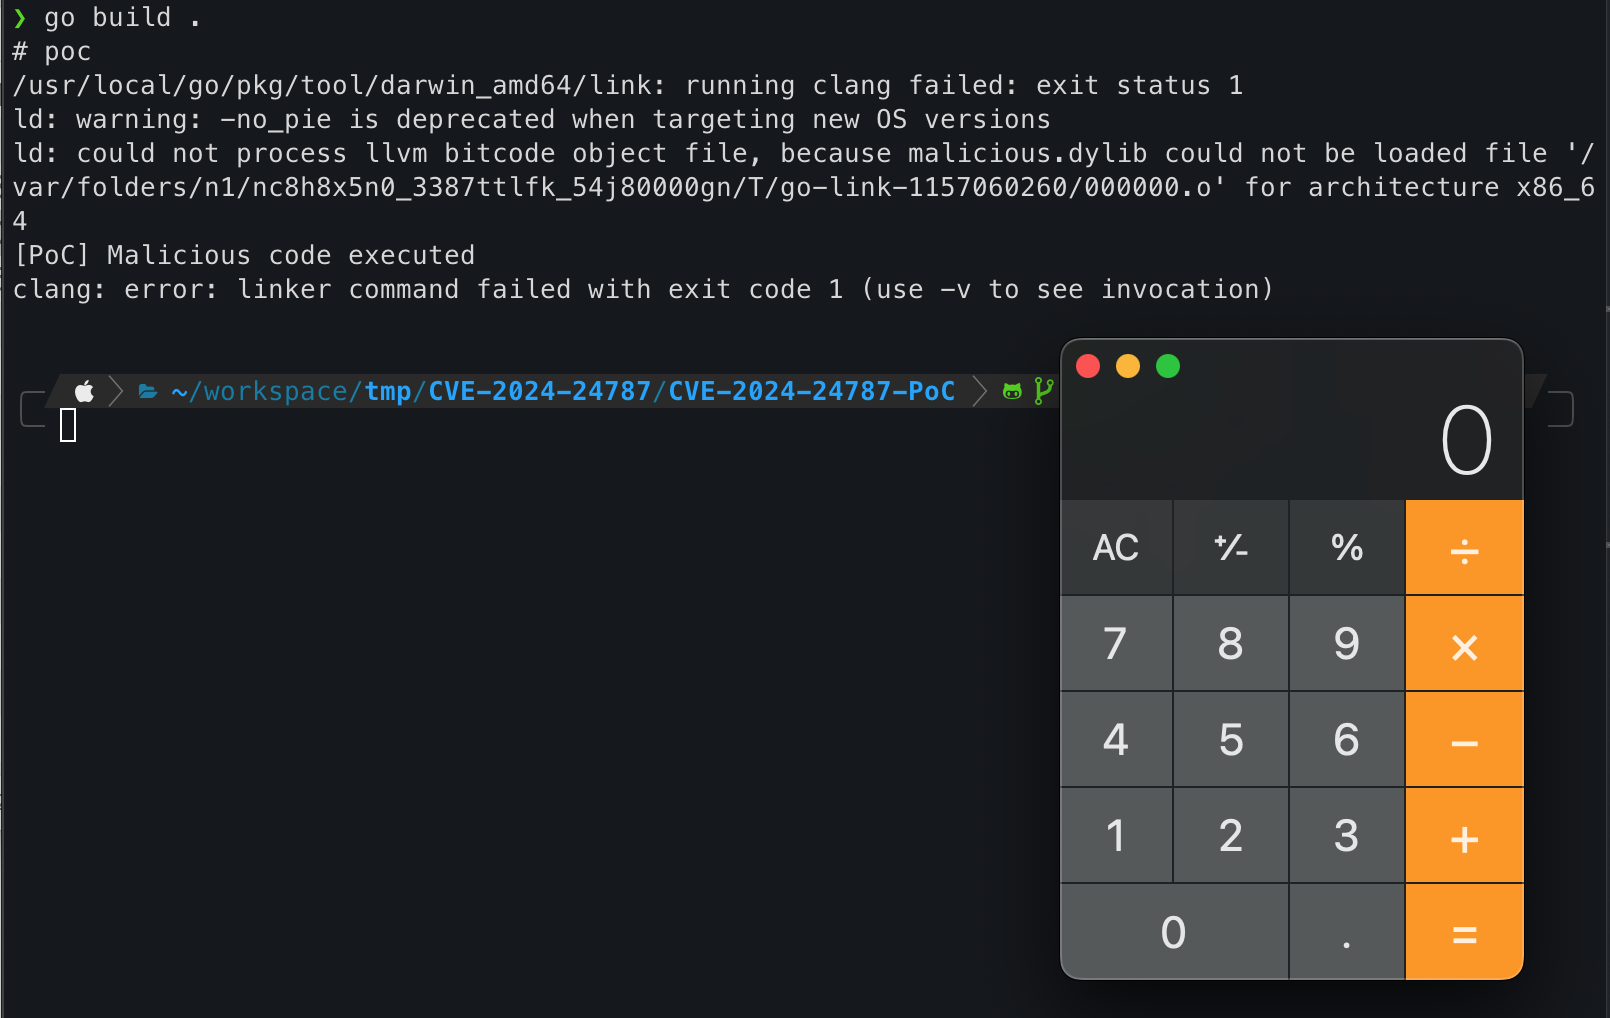 lourc0d3/cve-2024-24787-poc
CVE-2024-24787 Proof of Concept
 rotavori/dasel-melange-apko
dasel v3.3.1 packaged with Melange and shipped as a minimal apko image, patched for CVE-2026-33320
 nedlir/dasel-hardened-container
Hardened dasel v3.3.1 package and image built via Melange and apko. Patching CVE-2026-33320.
 renewablehacking/cve-2026-45321-tanstack
Educational lab simulating npm supply chain attacks, CI/CD abuse, and install-time code execution via CVE-2026-45321. Hands-on defensive security…








