
 #1
Dependency scanning, SBOM generation, package integrity, and supply chain risk tools.
Kitploit recommended
 rusakovichma/cve-2019-10172
CVE-2019-10172 PoC and Possible mitigations
 mrk336/cve-2024-3094
CVE-2024-3094 exposed a backdoor in the XZ compression library, allowing remote SSH access by bypassing authentication. It’s a major supply chain…
 junnythemarksman/cve-2024-24590
Deserialization of untrusted data can occur in versions 0.17.0 to 1.14.2 of the client SDK of Allegro AI’s ClearML platform, enabling a maliciously…
 nichetoolkit/spring-retry-toolkit
spring retry 1.3.x fix with niche toolkit for CVE-2026-41710
 ilhomjonr/cve-2026-67595
CVE-2026-67595 — Embedded malicious JavaScript (spyware) in VaahCMS 2.0.0–2.3.4 official releases. CVSS 8.1. Advisory + detection.
 perufitlife/dotclaude-security
Scan a repo's .claude/ config (settings.json hooks, MCP servers, env, allowed-tools) for the RCE & API-key-exfiltration footguns (CVE-2025-59536,…
 michaeladamgroberman/cve-2026-32662
CVE-2026-32662: Active Debug Code in Production — Gardyn Home Kit (ICSA-26-055-03)
 meterianhq/log4j-vuln-coverage-check
A simple project to check coverage of Log4J vuln CVE-2021-44228 (and related)
 yusufdalbudak/cve-2025-32965-xrpl-js-poc
CVE Kodu: CVE-2025-32965 Zafiyet Türü: Supply Chain Attack (CWE-506: Embedded Malicious Code) Hedef: xrpl.js kütüphanesinin 4.2.1–4.2.4 ve 2.14.2…
 u-maxx/magento-swf-patched-cve-2011-2461
Patched version of the uploader.swf and uploaderSingle.swf to fix CVE-2011-2461
 test-avm-714877d2df585126/vuln-ejs-critical
npm repo with ejs CVE-2022-29078 (CVSS 9.8, EPSS 32%) for Dependabot automerge testing
 shoucheng3/srikanth-lingala__zip4j_cve-2018-1002202_1-3-2
Decompiled source code of zip4j library versions 1.3.2 (vulnerable) and 1.3.3 (fixed) for CVE-2018-1002202 path traversal analysis, part of the…
 shoucheng3/codehaus-plexus__plexus-archiver_cve-2018-1002200_3-5
Java library for creating and extracting archives (ZIP, TAR, JAR) with support for various compression formats. Note: version 3.5 contains a fix for…
 ryancnelson/patched-bash-4.3
patched-bash-4.3 for CVE-2014-6271
 renewablehacking/cve-2026-45321-tanstack
Educational lab simulating npm supply chain attacks, CI/CD abuse, and install-time code execution via CVE-2026-45321. Hands-on defensive security…
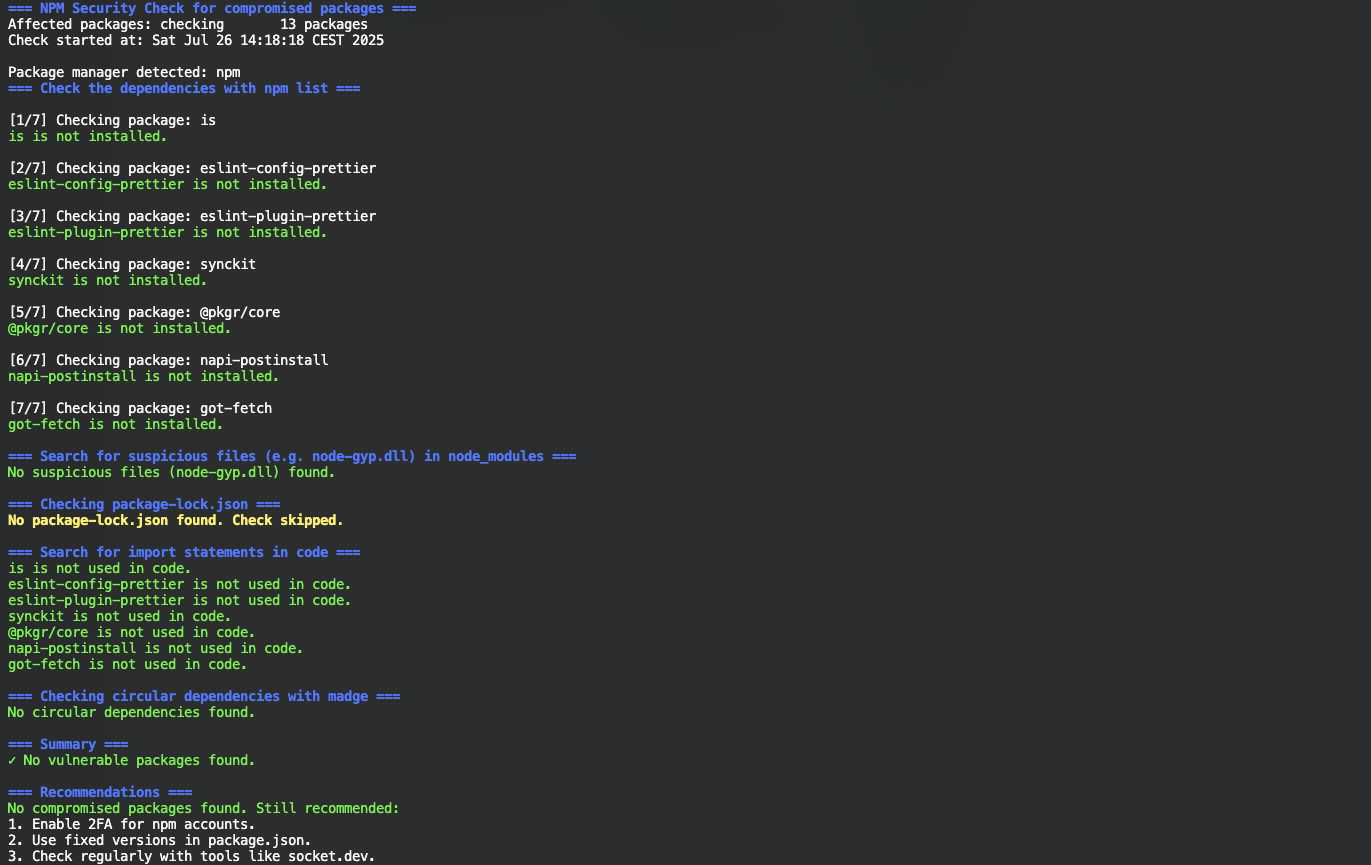 nihilor/cve-2025-54313
Checks projects for compromised packages, suspicious files, and import statements.
 mightysai1997/cve-2024-3094
Shell scripts to detect CVE-2024-3094 backdoor in liblzma5 across Kubernetes pods and Docker containers, with SBOM generation via Trivy for…
 lirantal/cve-2024-21533-poc-ggit
Proof-of-concept exploit for CVE-2024-21533, an argument injection vulnerability in the ggit npm package that allows arbitrary command execution via…








