
 #1
Subdomain discovery, DNS brute-force, certificate transparency, and asset enumeration tools.
Kitploit recommended

 mschwager/fierce
A DNS reconnaissance tool for locating non-contiguous IP space.
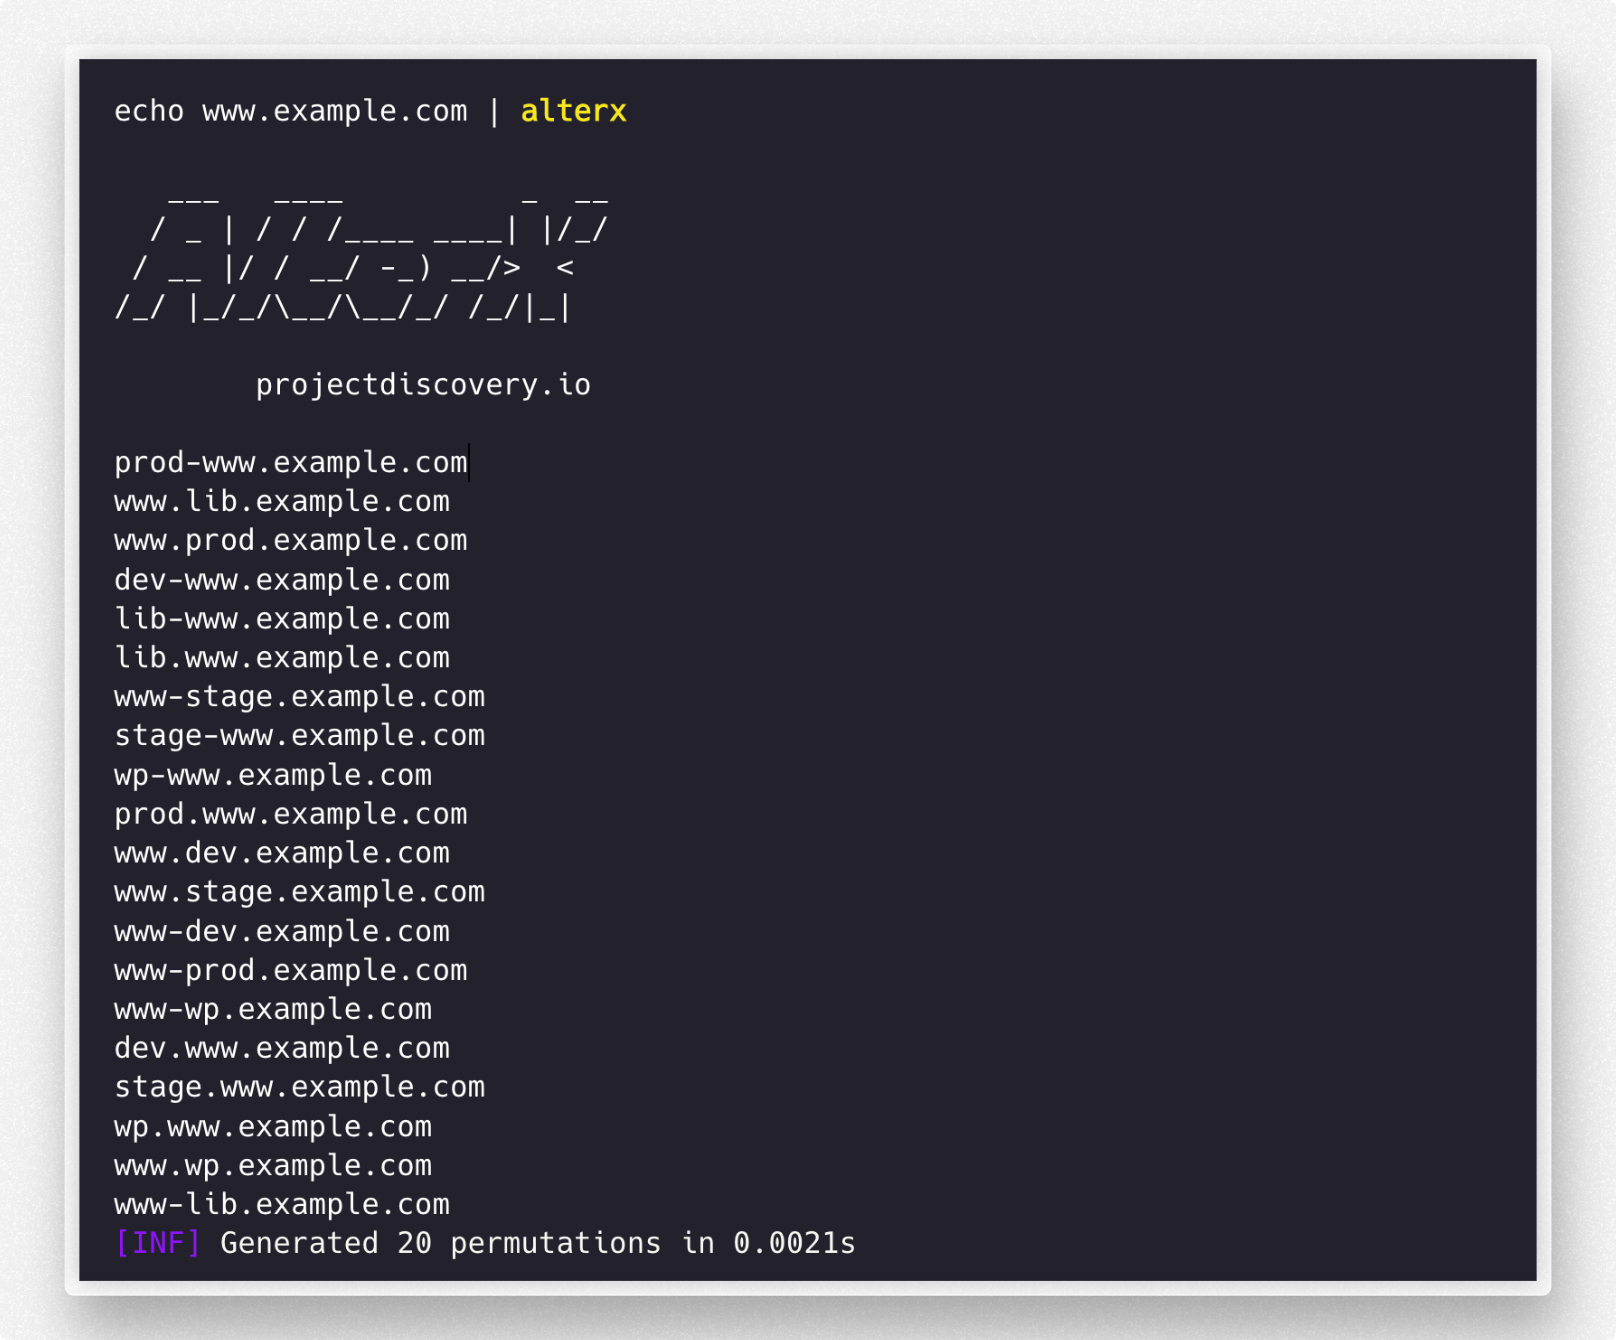 projectdiscovery/alterx
Fast and customizable subdomain wordlist generator using DSL
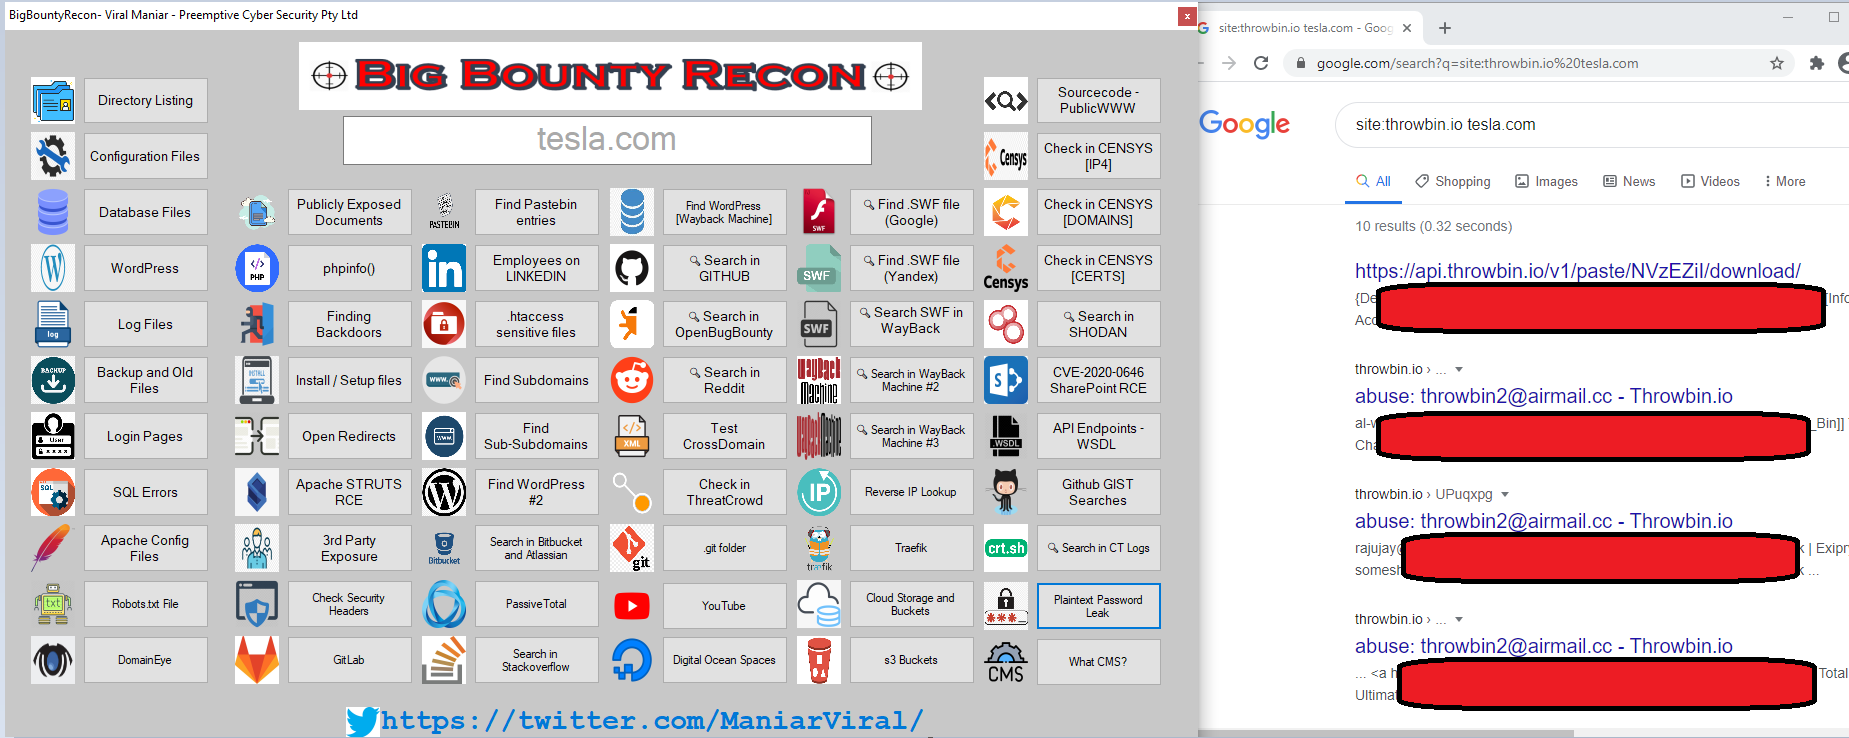 viralmaniar/bigbountyrecon
BigBountyRecon tool utilises 58 different techniques using various Google dorks and open source tools to expedite the process of initial…
 projectdiscovery/shuffledns
MassDNS wrapper written in go to enumerate valid subdomains using active bruteforce as well as resolve subdomains with wildcard filtering and easy…
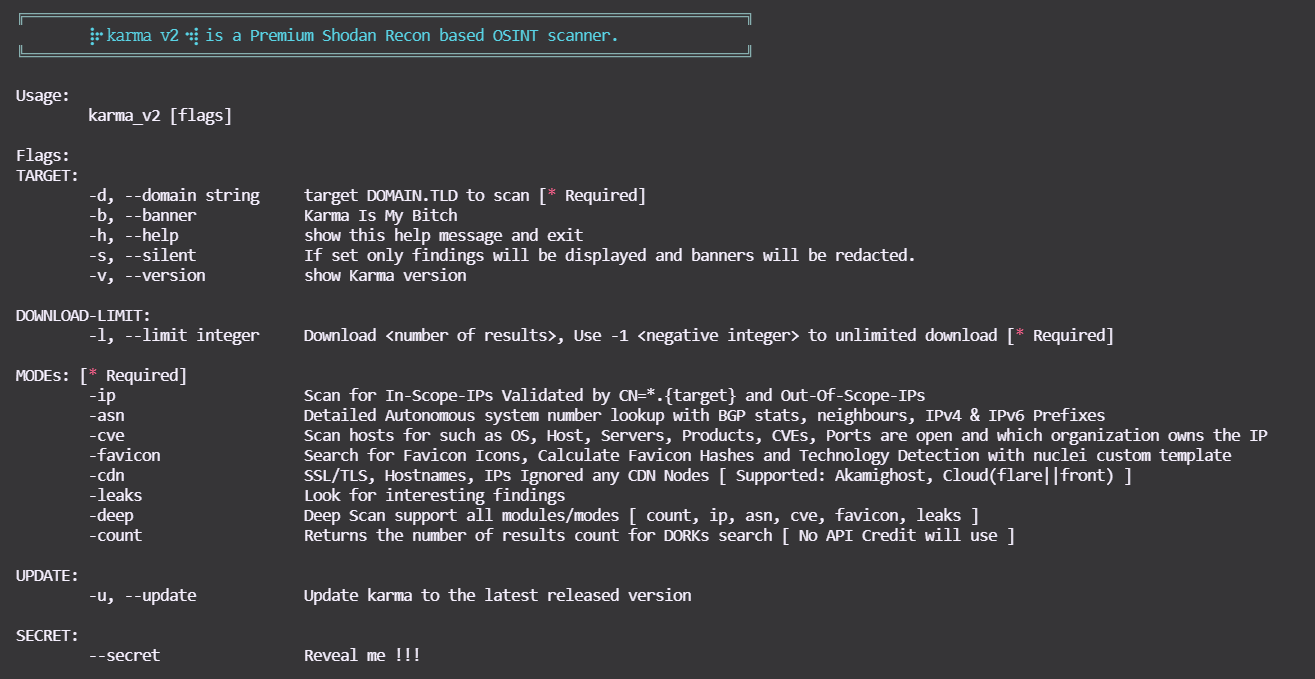 dheerajmadhukar/karma_v2
⡷⠂𝚔𝚊𝚛𝚖𝚊 𝚟𝟸⠐⢾ is a Passive Open Source Intelligence (OSINT) Automated Reconnaissance (framework)
 projectdiscovery/urlfinder
A high-speed tool for passively gathering URLs, optimized for efficient and comprehensive web asset discovery without active scanning.
 franccesco/getaltname
Extract subdomains from SSL certificates in HTTPS sites.
 chvancooten/bugbountyscanner
A Bash script and Docker image for Bug Bounty reconnaissance. Intended for headless use.
 twelvesec/gasmask
Information gathering tool - OSINT
 infobyte/emploleaks
An OSINT tool that helps detect members of a company with leaked credentials
 superhedgy/attacksurfacemapper
AttackSurfaceMapper is a tool that aims to automate the reconnaissance process.
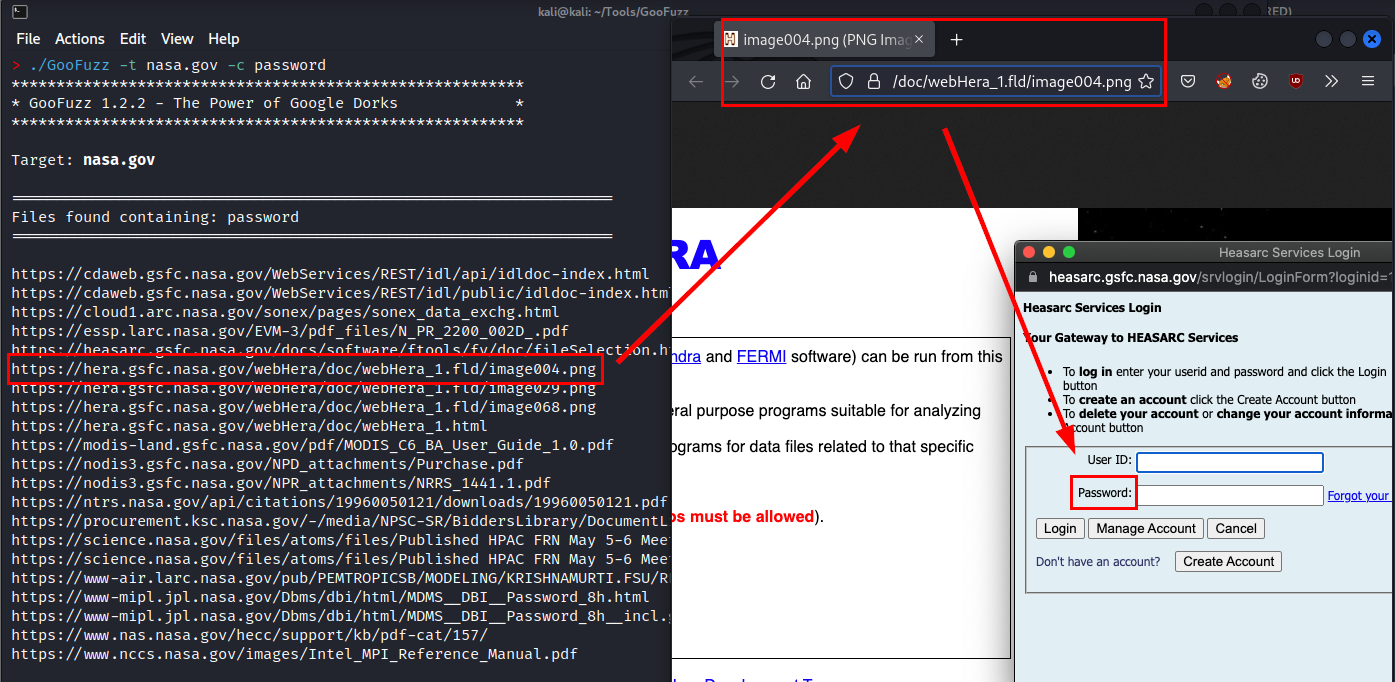 m3n0sd0n4ld/goofuzz
Bash-based fuzzing tool that leverages Google Dorking for stealthy enumeration of directories, files, subdomains, and parameters without direct…
 anshumanbh/tko-subs
A tool that can help detect and takeover subdomains with dead DNS records
 h4r5h1t/webcopilot
An automation tool that enumerates subdomains then filters out xss, sqli, open redirect, lfi, ssrf and rce parameters and then scans for…
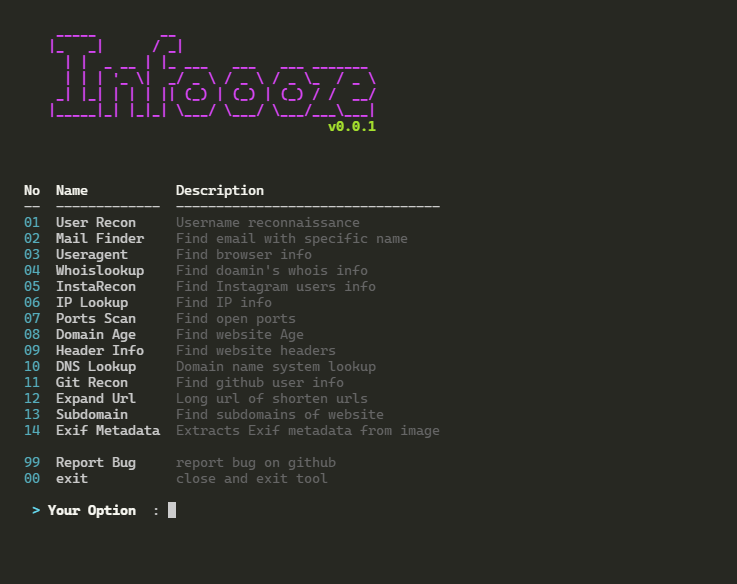 devxprite/infoooze
A OSINT tool which helps you to quickly find information effectively. All you need is to input and it will take take care of rest.
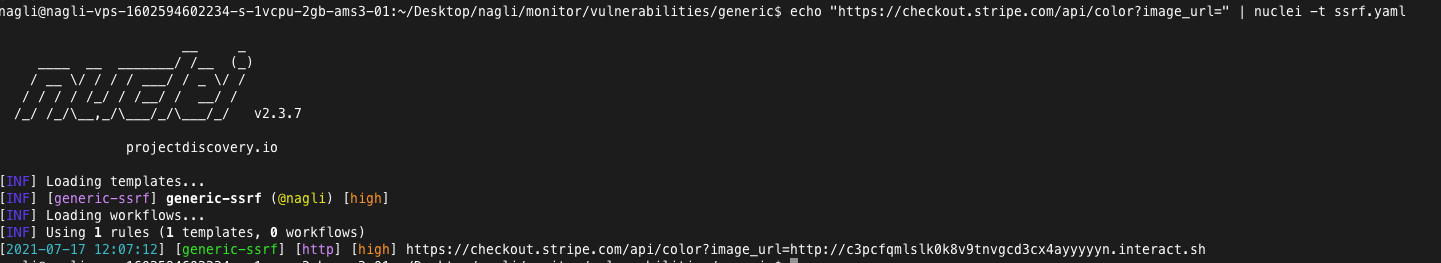 gal-nagli/shockwave-oss
Curated collection of bug bounty tips, one-liners, and automation workflows for recon, fuzzing, and web exploitation, with private nuclei templates…
 anmolksachan/thetimemachine
Weaponizing WaybackUrls for Recon, BugBounties , OSINT, Sensitive Endpoints and what not
 boy-hack/ksubdomain
Subdomain enumeration tool, asynchronous dns packets, use pcap to scan 1600,000 subdomains in 1 second






