
 #1
Tools for assessing and securing Supervisory Control and Data Acquisition (SCADA) and Industrial Control Systems (ICS).
Kitploit recommended
 fofapro/fapro
Multi-protocol honeypot simulator supporting 50+ network services with deep interaction, TCP/UDP/ICMP logging, JA3 fingerprinting, and virtual…
 mitre-attack/attack-stix-data
STIX 2.1 collections of the MITRE ATT&CK knowledge base, providing adversary tactics and techniques for enterprise, mobile, and ICS threat…
 digitalbond/redpoint
Nmap NSE scripts for ICS/SCADA discovery and enumeration—BACnet, EtherNet/IP, CoDeSys, Fox, Modicon, Omron, S7—using protocol queries for security…

 praetorian-inc/nerva
Fast service fingerprinting CLI for 170+ protocols (TCP/UDP/SCTP) - built by Praetorian
 bhdresh/dejavu
DejaVU - Open Source Deception Framework
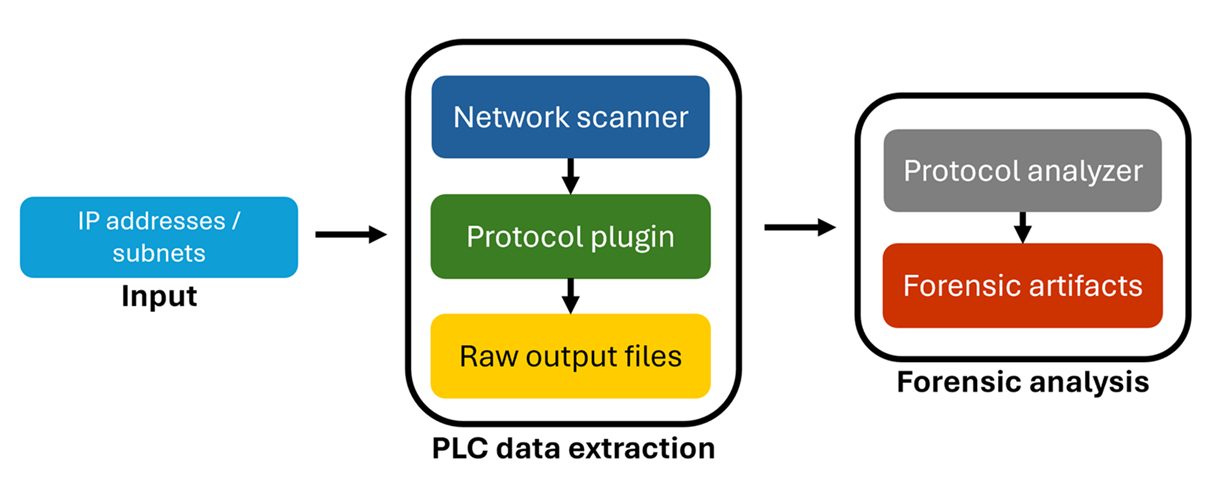 microsoft/ics-forensics-tools
Open-source forensics framework for analyzing Industrial PLC metadata and project files. Scans for suspicious artifacts in ICS environments to…
 exploit-garbage/0day-rubbish
Redefining vulnerability disclosure in the AI era. We mass-produce exploitable 0days and disclose them directly, using event-driven pressure to…
 scy-phy/minicps
Real-time simulation framework for cyber-physical systems with physical process/control device models and Mininet-based network emulation, built for…
 tijldeneut/icssecurityscripts
Python scripts for security assessment of industrial PLCs: scanning, enumeration, control, and exploitation of Beckhoff, Siemens, Schneider,…
 aau-network-security/hostage
Low Interaction Mobile Honeypot
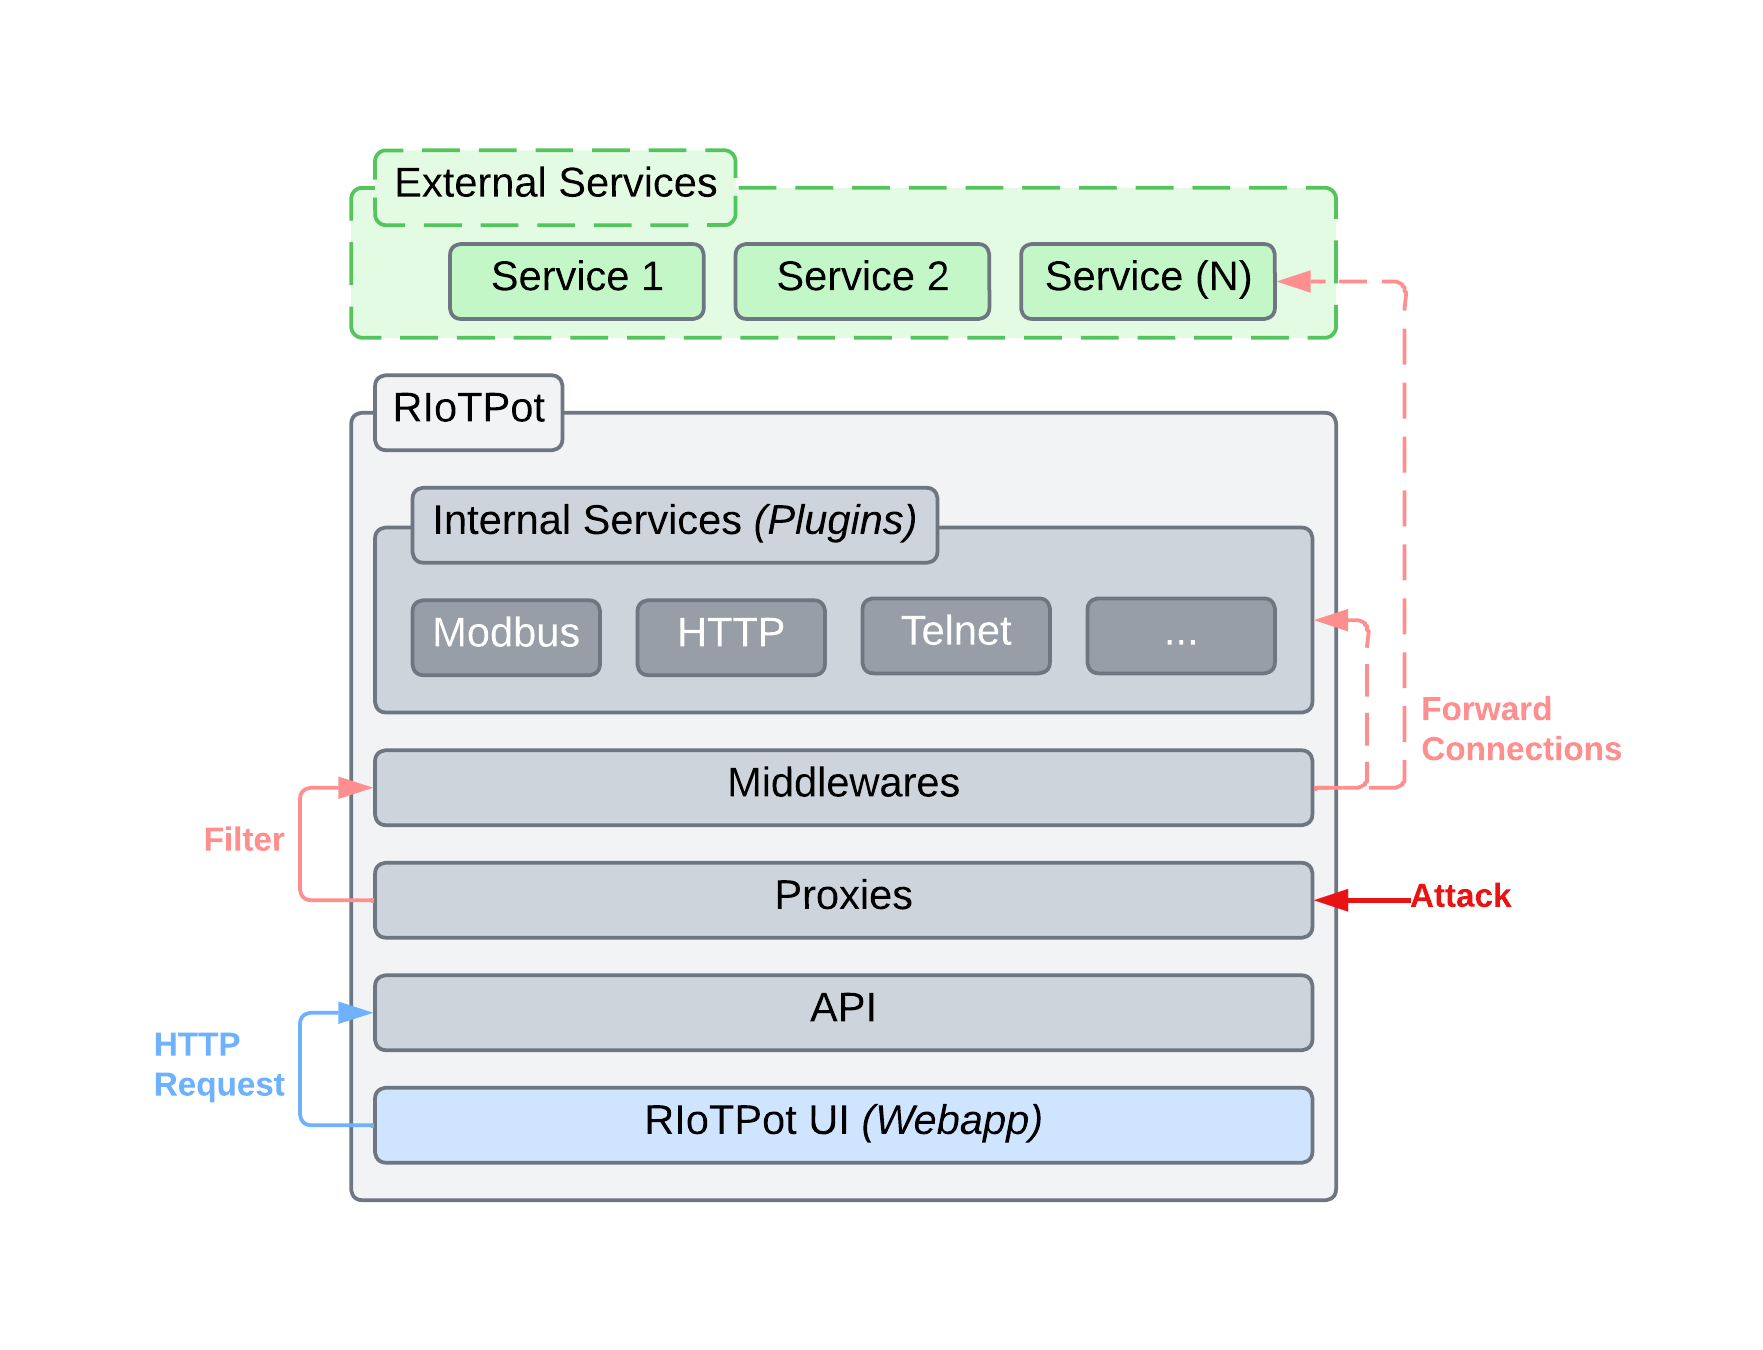 aau-network-security/riotpot
IoT and Operational Technology Honeypot
 0x0mar/smod
MODBUS Penetration Testing Framework
 rdomanski/exploits_and_advisories
Repository that tracks public exploits, vulnerabilities and advisories that I [co-]discovered or [co-]authored.
 sadfud/exploits
Real world and CTFs exploiting web/binary POCs.
 pmaynard/ics-testbed-framework
Deploys realistic virtual SCADA/ICS testbeds with IEC 60870-5-104 and OPC-UA nodes, enabling attack simulations, legitimate packet generation, and…
 orange-cyberdefense/bof
BOF (Boiboite Opener Framework) is a testing framework for industrial protocols implementations and devices.





