
 #1
Tools for assessing and securing Supervisory Control and Data Acquisition (SCADA) and Industrial Control Systems (ICS).
Kitploit recommended

 sourceincite/randy
A pre-authenticated RCE exploit for Inductive Automation Ignition
 gainsec/cve-2017-16744-and-cve-2017-16748-tridium-niagara
Proof of Concept (PoC) for CVE: 2017-16744 and 2017-16748
 corelight/ripple20
A Zeek package for the passive detection of "Ripple20" vulnerabilities in the Treck TCP/IP stack.
 momalab/icsfuzz
Instrumented fuzzer for PLC-based ICS control applications, targeting Codesys runtime on Wago controllers to uncover memory corruption and…
 hev0x/cve-2021-31630-openplc_rce
Exploit for Authenticated Remote Code Execution on OpenPLC v3 Webserver
 aau-network-security/hostage
Low Interaction Mobile Honeypot
 hev0x/cve-2021-26828_scadabr_rce
Proof-of-concept exploit for CVE-2021-26828 enabling authenticated remote code execution on ScadaBR SCADA systems via JSP file upload. Supports…

 d0ubl3g/industrial-security-auditing-framework
ISAF aims to be a framework that provides the necessary tools for the correct security audit of industrial (OT) environments.
 murataydemir/active-scanning-and-information-gathering-in-ics-scada-networks-using-network-mapper-nmap
Active Scanning and Information Gathering in ICS/SCADA Networks using Network Mapper (NMAP) (Turkish)
 murataydemir/purdue-model-for-industrial-control-system-environments
Purdue Model for Industrial Control System (ICS) Environments (Turkish)
 sadfud/exploits
Real world and CTFs exploiting web/binary POCs.
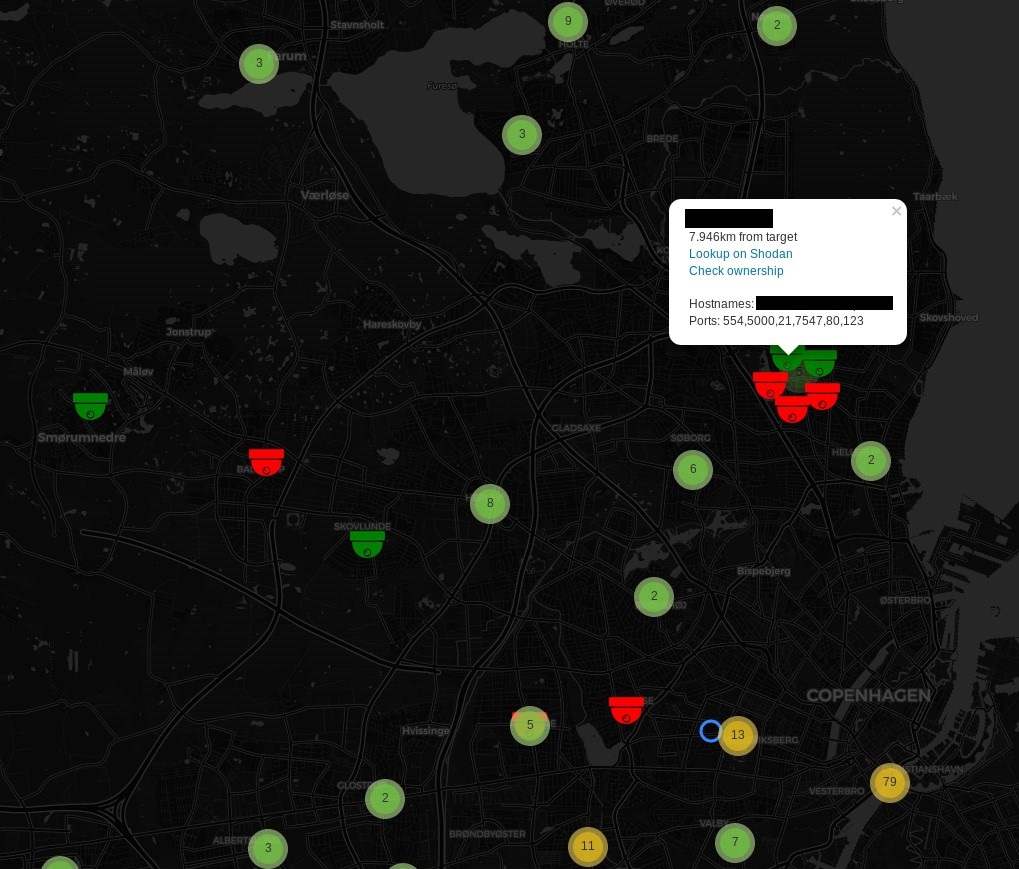 woj-ciech/kamerka
Build interactive map of cameras from Shodan
 certcc/trommel
TROMMEL: Sift Through Embedded Device Files to Identify Potential Vulnerable Indicators
 kevinherron/stack-overflow-poc
PoC for CVE-2018-12086 affecting various OPC UA stacks
 pmaynard/ics-testbed-framework
Deploys realistic virtual SCADA/ICS testbeds with IEC 60870-5-104 and OPC-UA nodes, enabling attack simulations, legitimate packet generation, and…
 can/cve-2015-5374-dos-poc
DoS exploit for CVE-2015-5374 targeting Siemens SIPROTEC 4 and Compact EN100 Ethernet modules via a crafted UDP packet to port 50000, with an…
 emreovunc/myscada-mypro-7-hardcoded-ftp-username-and-password
CVE-2018-11311 | mySCADA myPRO 7 Hardcoded FTP Username and Password Vulnerability
 emreovunc/myscada-mypro-7-projectid-disclosure
CVE-2018-11517 | mySCADA myPRO v7.0.46 has another vulnerability to discover all projects in the system.






