#1
Tools for assessing and securing Supervisory Control and Data Acquisition (SCADA) and Industrial Control Systems (ICS).
Kitploit recommended

 wallyschag/cve-2025-41656
This repository includes the code and files needed to test and execute a PoC for CVE-2025-41656
 tranquac/openplc_v3
To reproduce CVE-2021-31630
 hslatman/awesome-industrial-control-system-security
A curated list of resources related to Industrial Control System (ICS) security.
 userb1ank/cve-2021-31630
Exploit for CVE-2021-31630 in OpenPLC, providing a Python script and manual steps to achieve remote code execution via malicious ST file upload and…
 eyodav/cve-2025-34226
OpenPLC Runtime suffers from a persistent denial of service (DoS) vulnerability in the /upload-program-action endpoint.
 shoucheng3/yamcs__yamcs_cve-2023-45277_5-8-6
Java-based mission control framework with YAML configuration, supporting telemetry, commanding, and simulation for spacecraft operations. Includes…
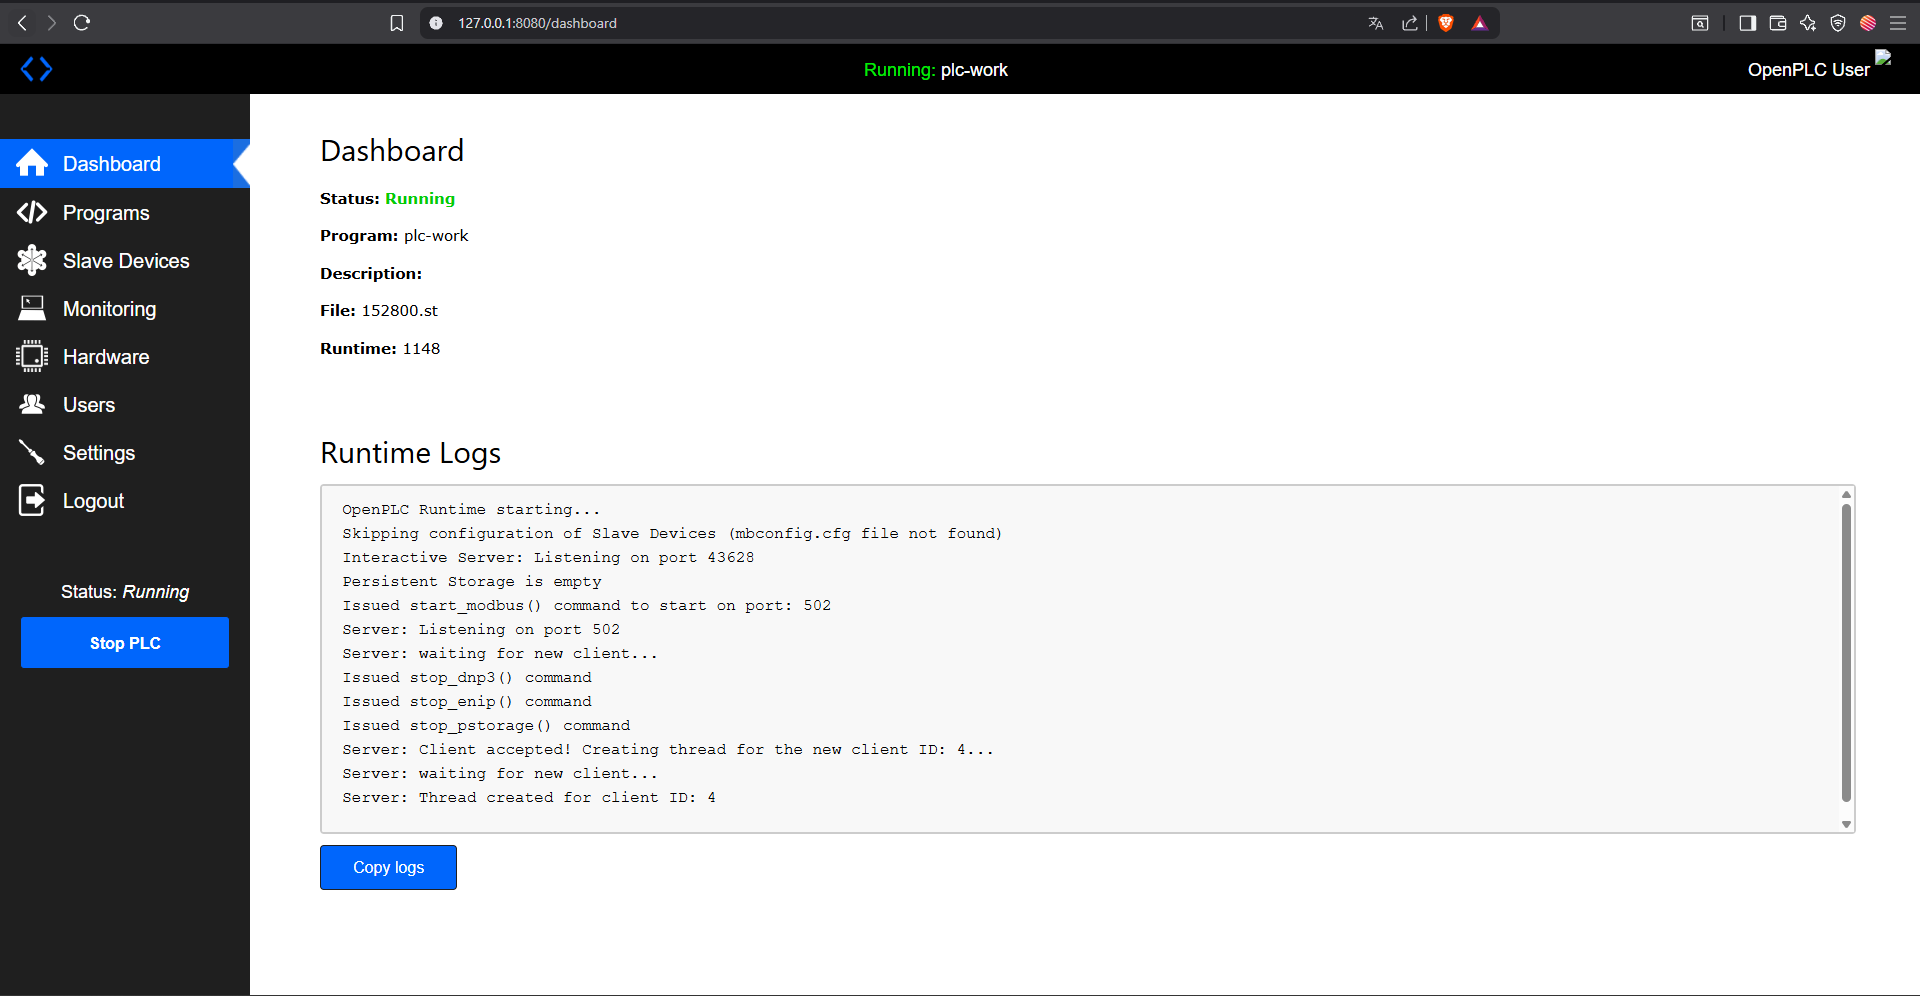 eyodav/cve-2025-54962
Authenticated users can upload arbitrary files (e.g. .html, .svg) as profile images in OpenPLC Runtime. These files are publicly accessible without…
 bhdresh/dejavu
DejaVU - Open Source Deception Framework
 greenforcenetworks/cve-2025-41646---critical-authentication-bypass-
CVE-2025-41646 - Critical Authentication bypass
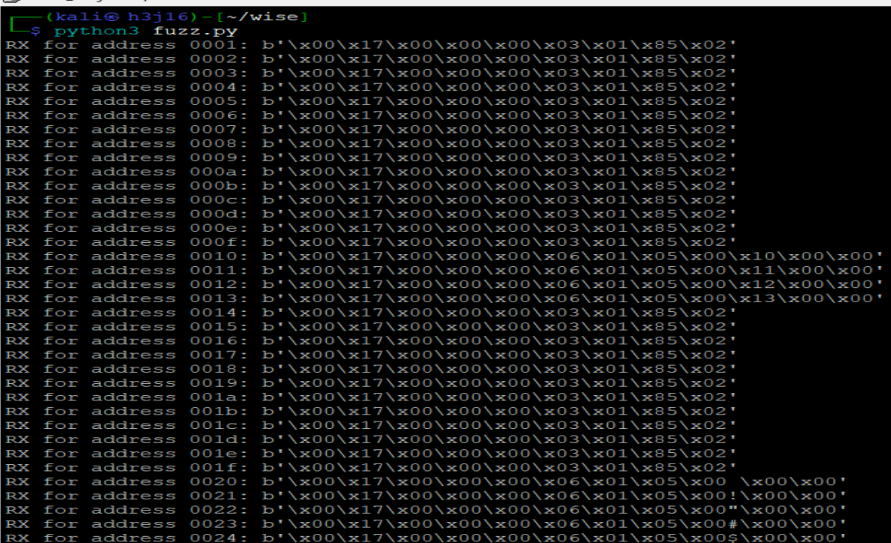 shipcod3/cve-2025-48466
Modbus Packet Injection on Advantech WISE 4060LAN / IoT Gateway for door control
 z3usx01/cve-2024-8232
SpiderControl SCADA Web Server File Upload Vulnerability
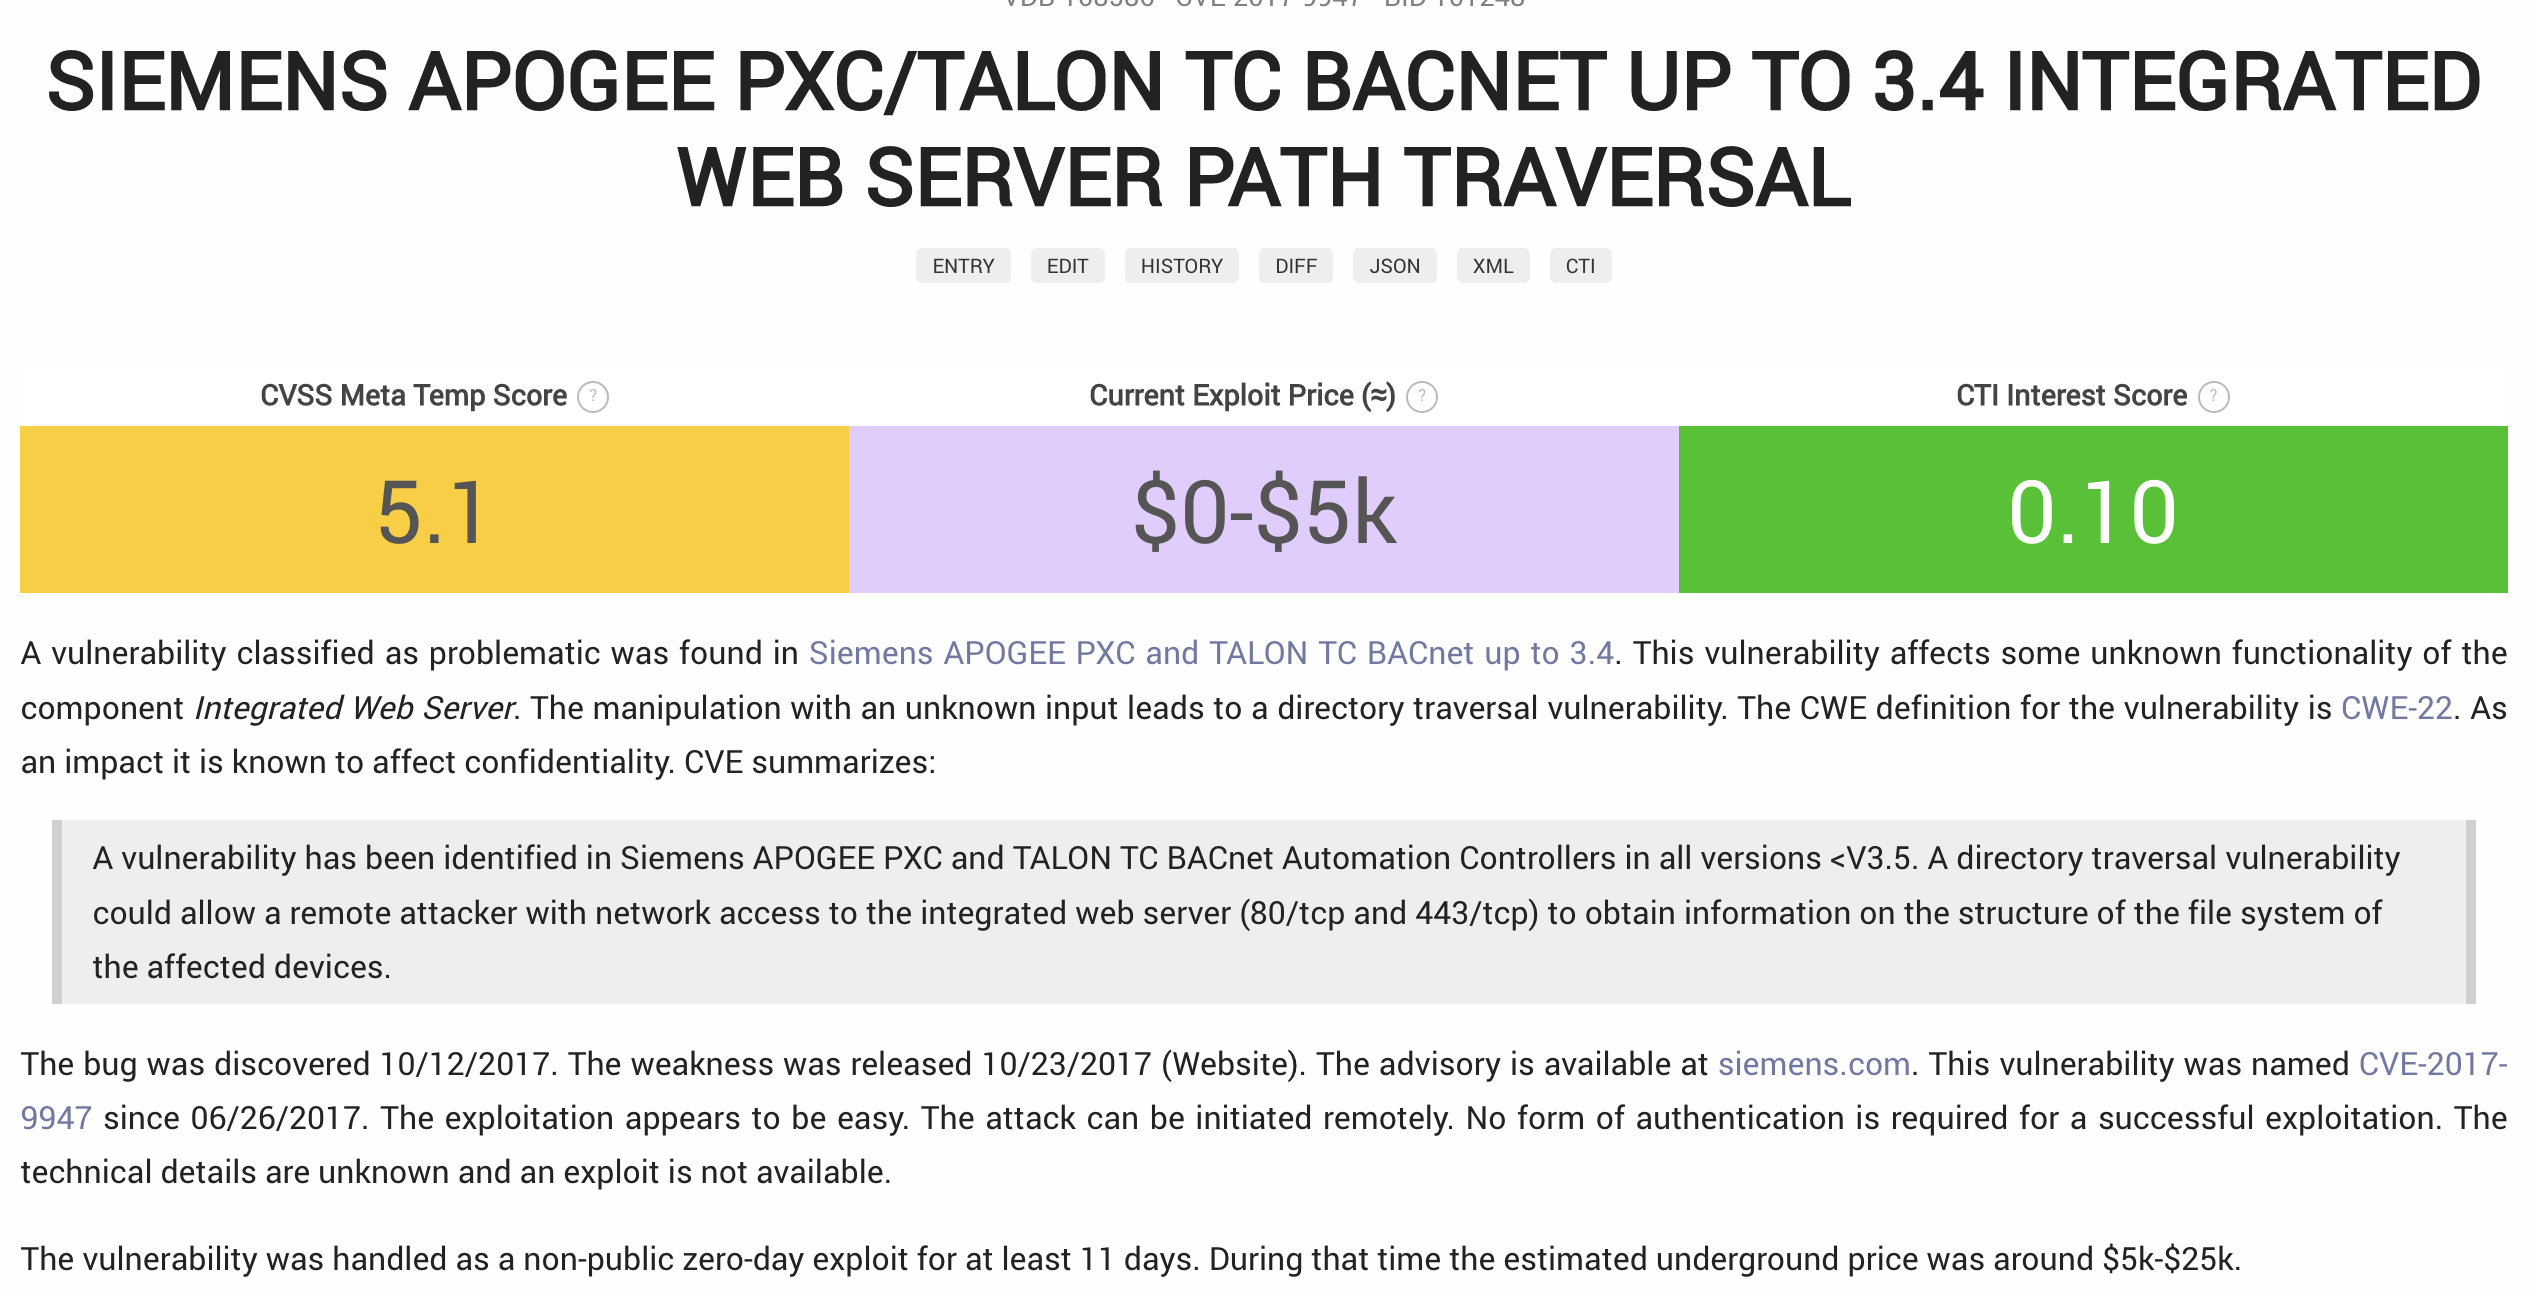 rosesecurity/apologee
APOLOGEE is a Python script and Metasploit module that enumerates a hidden directory on Siemens APOGEE PXC BACnet Automation Controllers (all…
iti/ics-security-toolsTools, tips, tricks, and more for exploring ICS Security.
 thehappydinoa/awesome-censys-queries
A collection of fascinating and bizarre Censys Search Queries
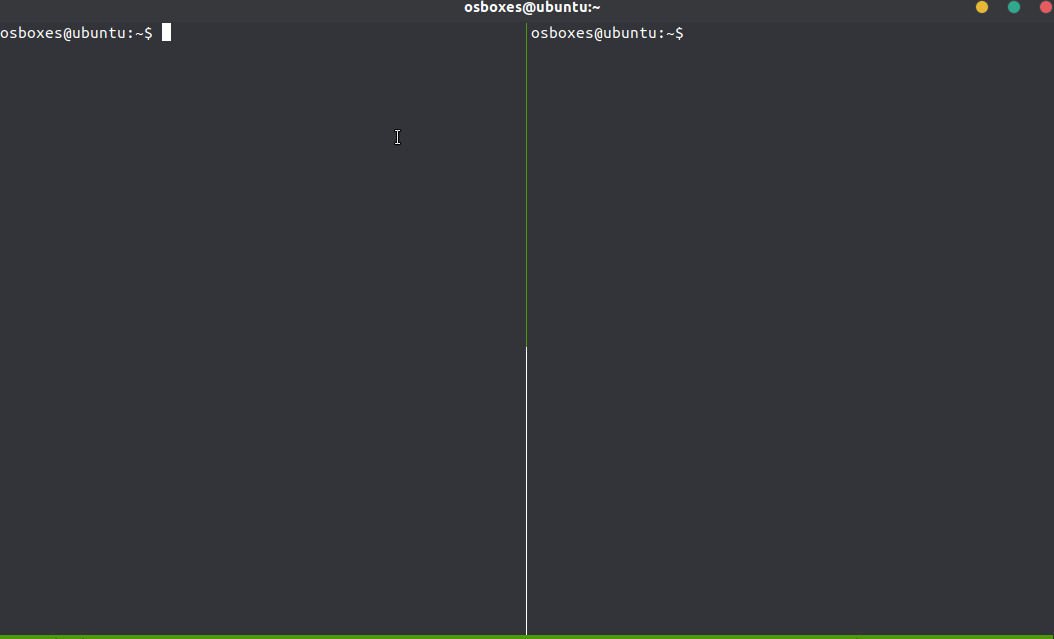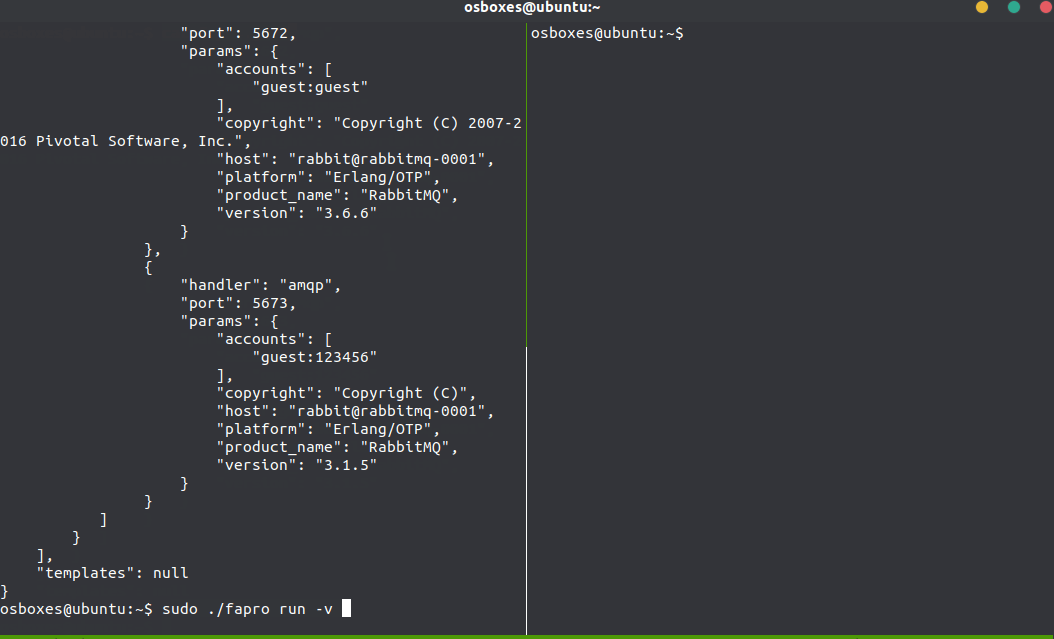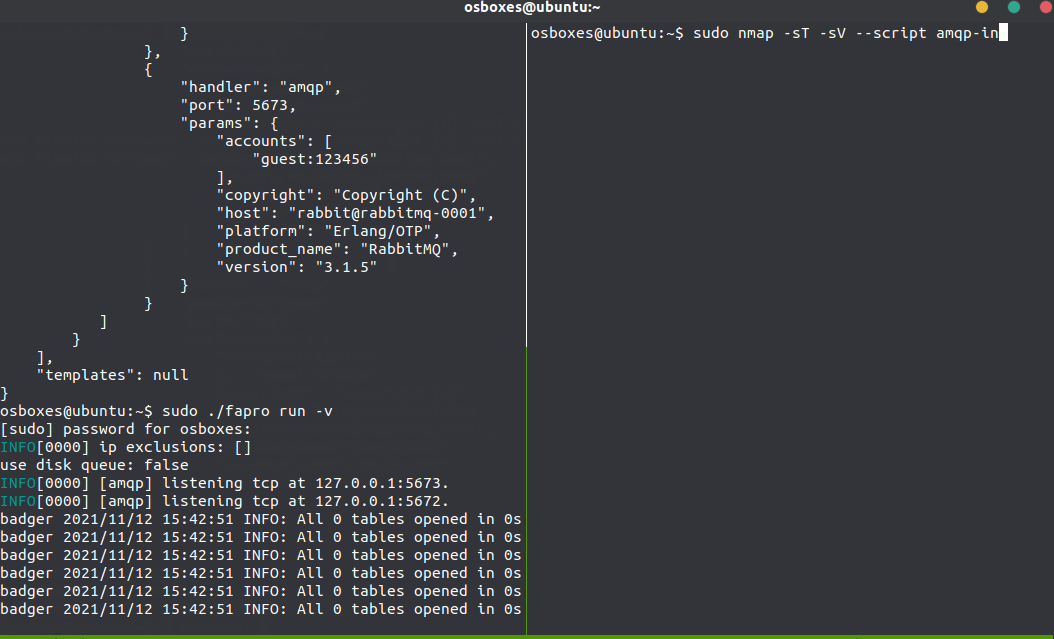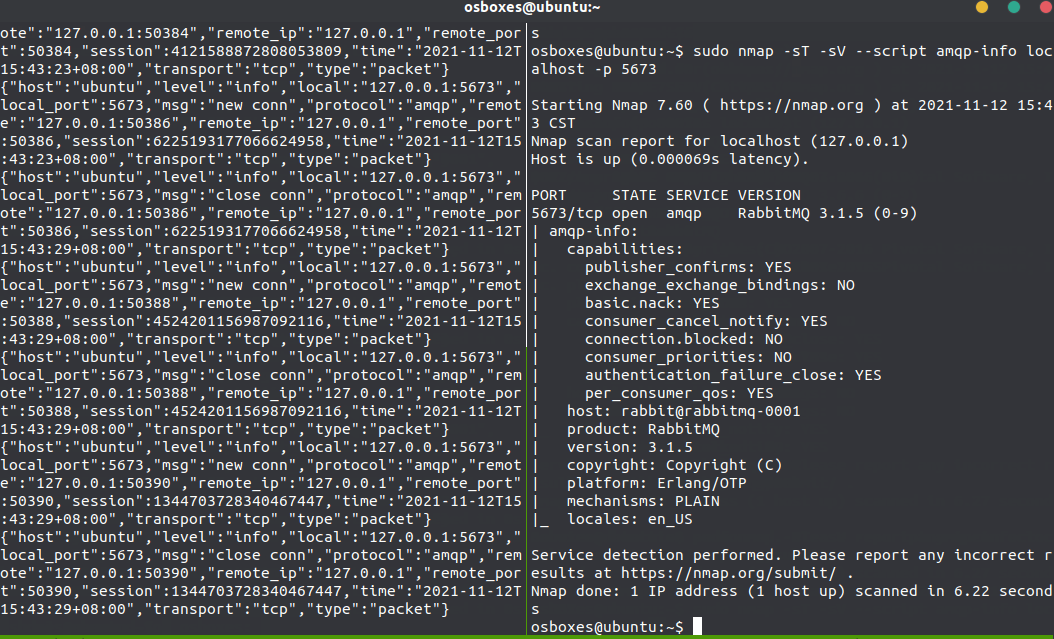 fofapro/fapro
Multi-protocol honeypot simulator supporting 50+ network services with deep interaction, TCP/UDP/ICMP logging, JA3 fingerprinting, and virtual…
 astrowmist/poc-cve-2012-1831
Proof Of Concept for the CVE-2012-1831 (Kingview Touchview 6.53). This is a Industrial Control Systems Vulnerability
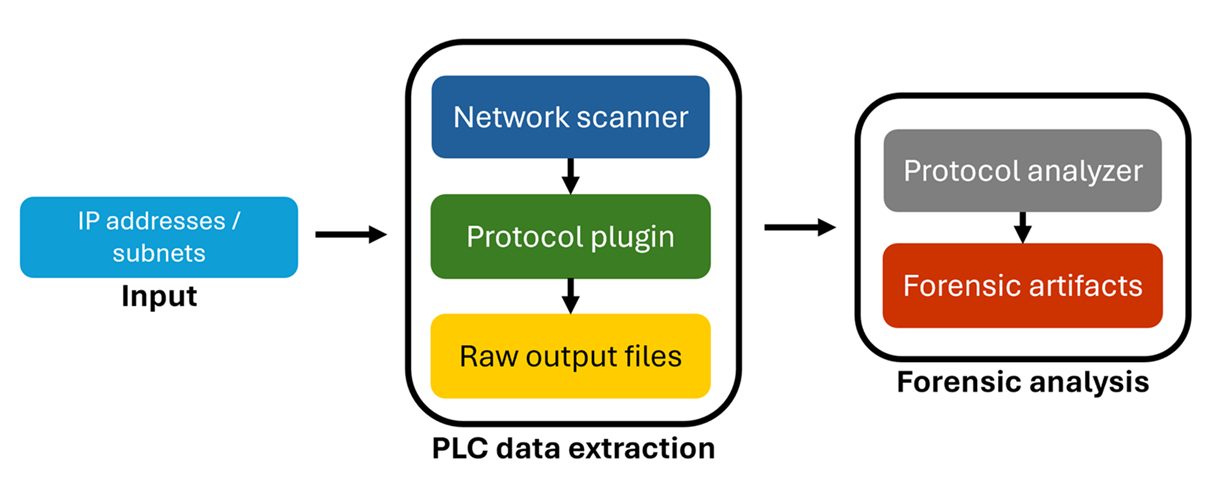 microsoft/ics-forensics-tools
Open-source forensics framework for analyzing Industrial PLC metadata and project files. Scans for suspicious artifacts in ICS environments to…