
 #1
Tools for decompiling, disassembling, and understanding malware internals and complex binaries.
Kitploit recommended

 aancw/sslpindetect
SSLPinDetect is a tool for analyzing Android APKs to detect SSL pinning implementations by scanning for known patterns in decompiled code. It helps…
 malpedia/malpedia-flossed
FLARE floss applied to all unpacked+dumped samples in Malpedia, pre-processed for further use.
 synacktiv/samsung-q60t-exploit
Exploit suite targeting Tizen-based Samsung Q60T TV, including v8 and kernel exploits, firmware decryption, and root shell access via payload…
 crissyfield/super-trouper
MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
 mainframed/dc30_workshop
DEFCON 30 Mainframe buffer overlow workshop container
 jir4vv1t/cve-2025-43529
Technical exploit for CVE-2025-43529, a WebKit DFG JIT compiler vulnerability enabling use-after-free via missing store barrier in concurrent GC,…
 1rhino2/fnprint
match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.
 x86byte/sbox
Compile-time AES string obfuscation for C++
 lunixbochs/revsync
realtime cross-tool collaborative reverse engineering
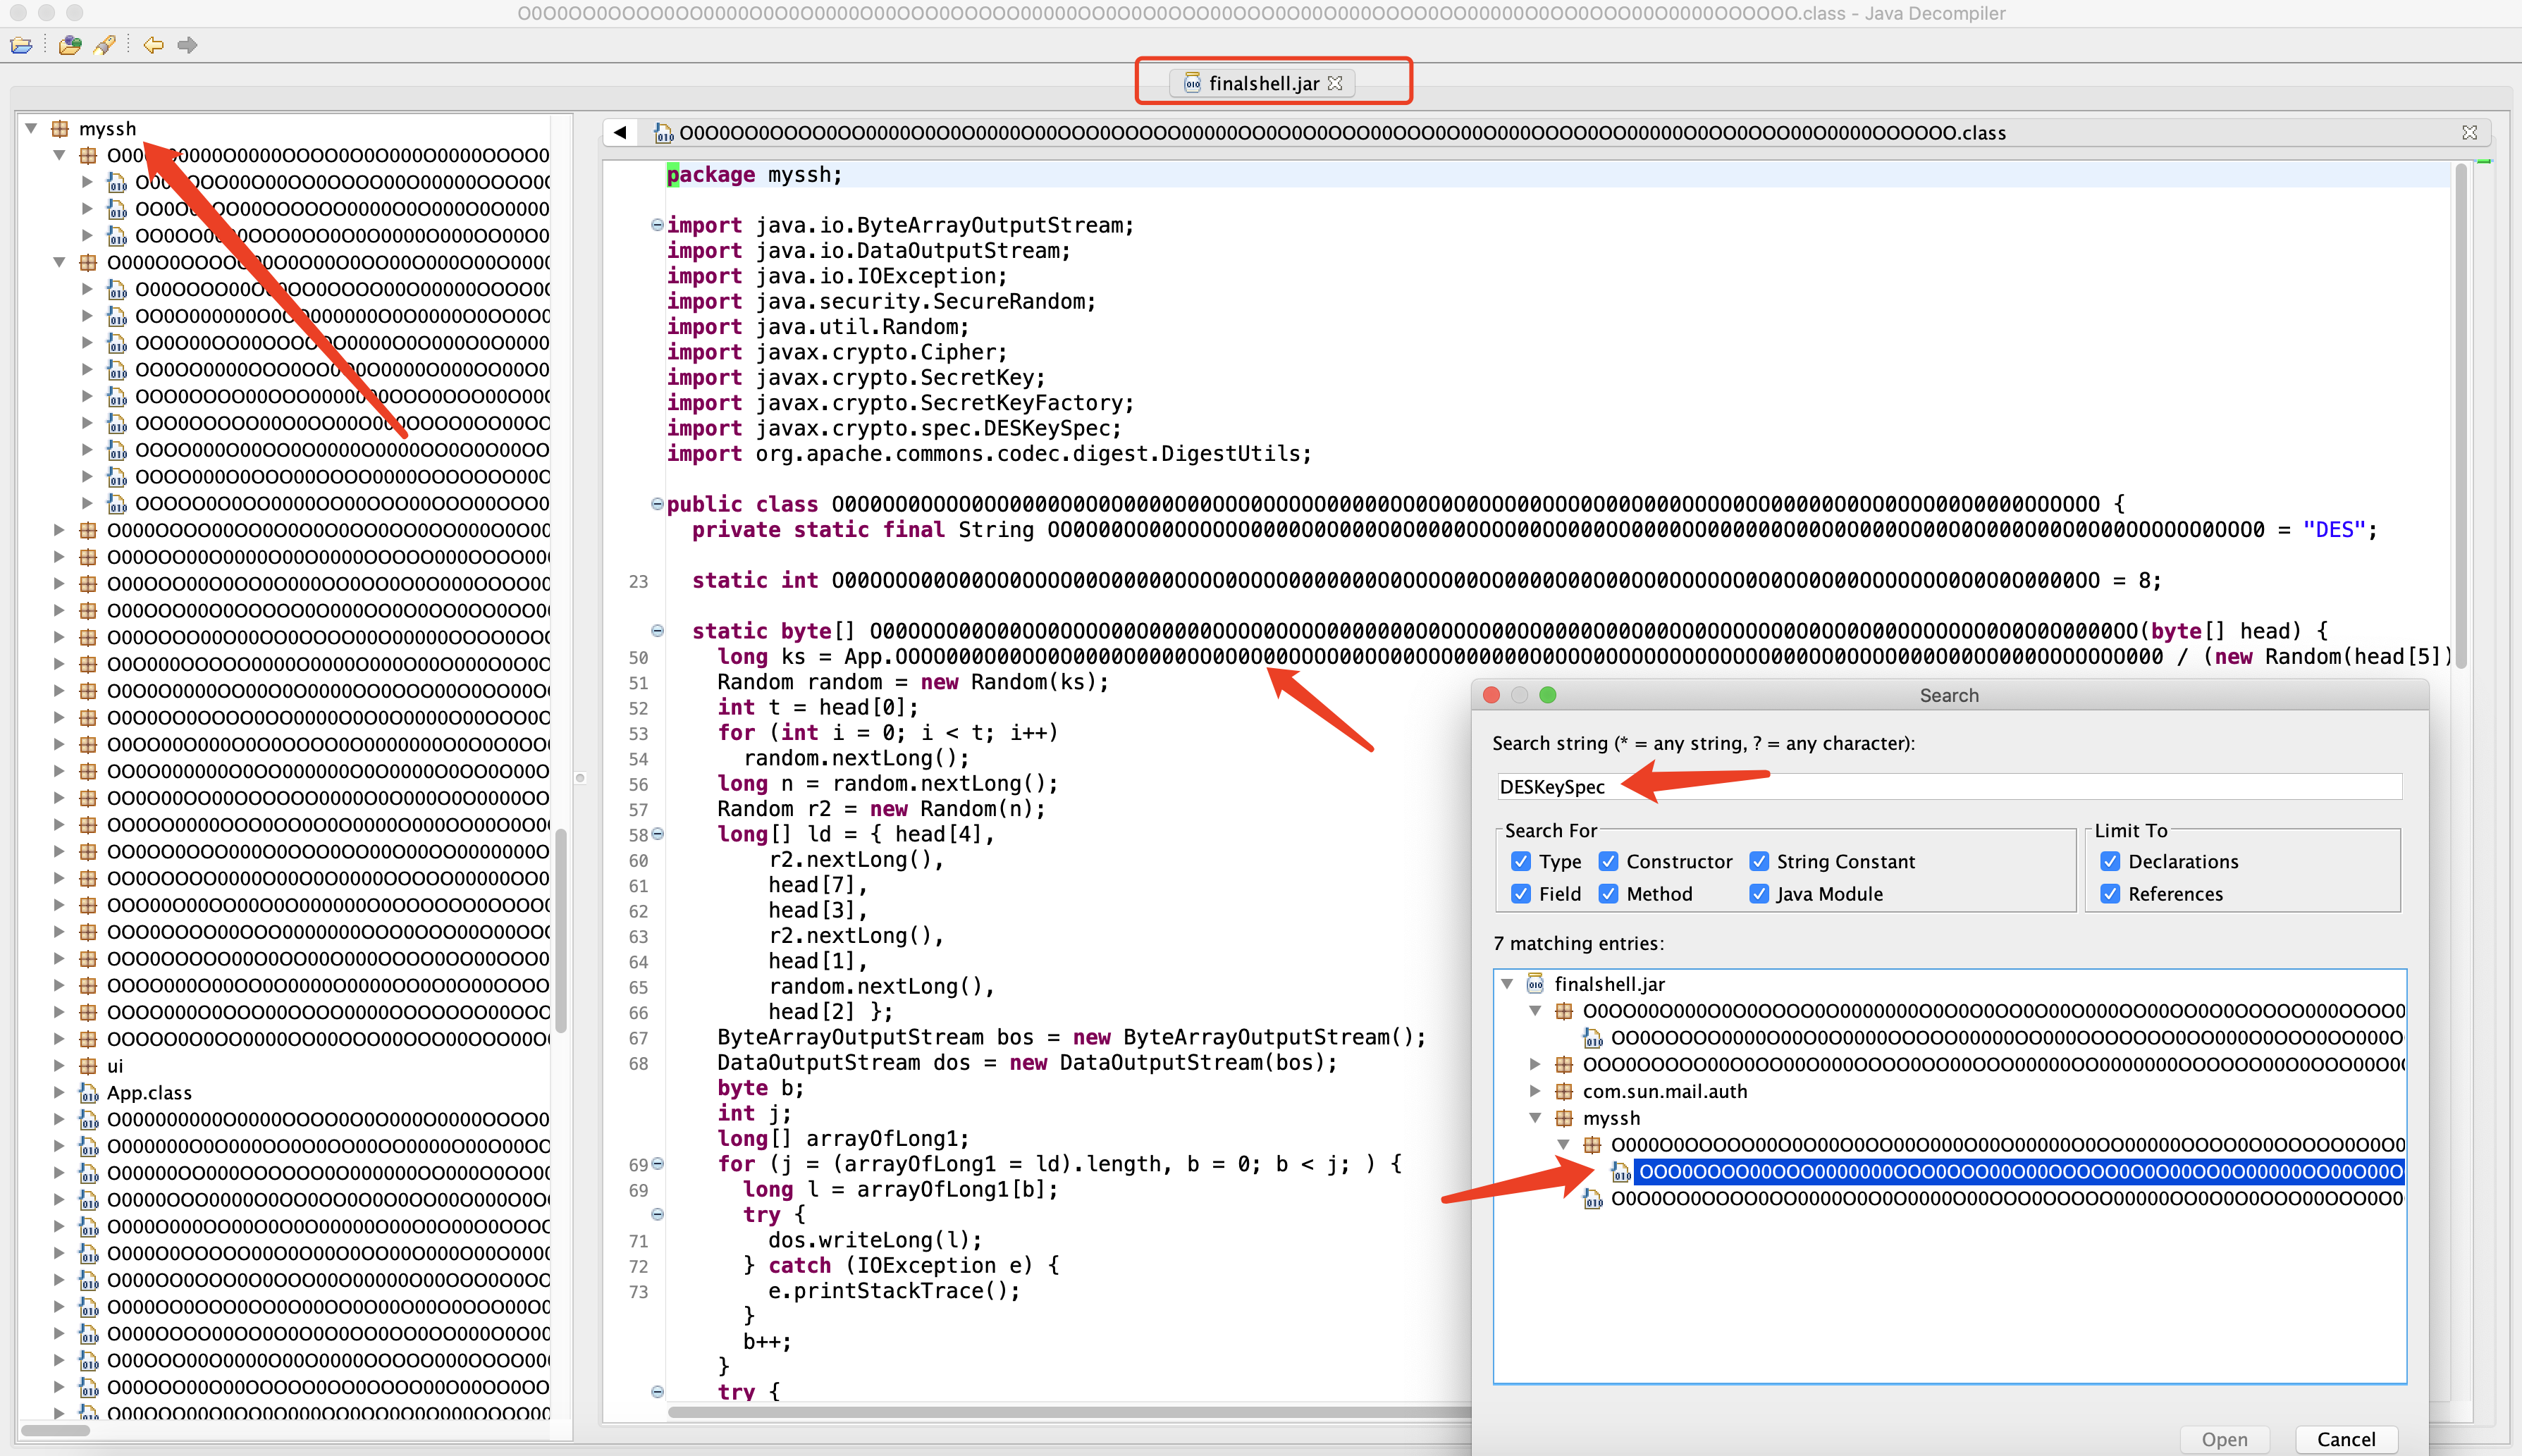 jas502n/finalshelldecodepass
FinalShellDecodePass 加密解密
 cdong1012/idapython-malware-scripts
Scripts for automating malware analysis and reverse engineering workflows in IDA Pro, covering binary inspection, static analysis, and code…
 dr4k0nia/xorstringsnet
Easy XOR string encryption for NET based binaries
 stefan2200/aparoid
Static and dynamic Android application security analysis
 cq674350529/pocs_slides
my advisory, poc, slides and scripts related to IoT/protocol security
 brnpl/flutter-reverse-engineering-labs
Hands-on challenges for learning how to reverse engineer Flutter applications.
 binsec/xyntia
Xyntia, the black-box deobfuscator
 akatorich/kernelflirt
Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…
 trou/cpu_rec_rs
Determine which CPU architecture is used in a binary file.








