
 #1
Tools for decompiling, disassembling, and understanding malware internals and complex binaries.
Kitploit recommended

 tanprathan/mobileapp-pentest-cheatsheet
The Mobile App Pentest cheat sheet was created to provide concise collection of high value information on specific mobile application penetration…
 avast/retdec
RetDec is a retargetable machine-code decompiler based on LLVM.
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
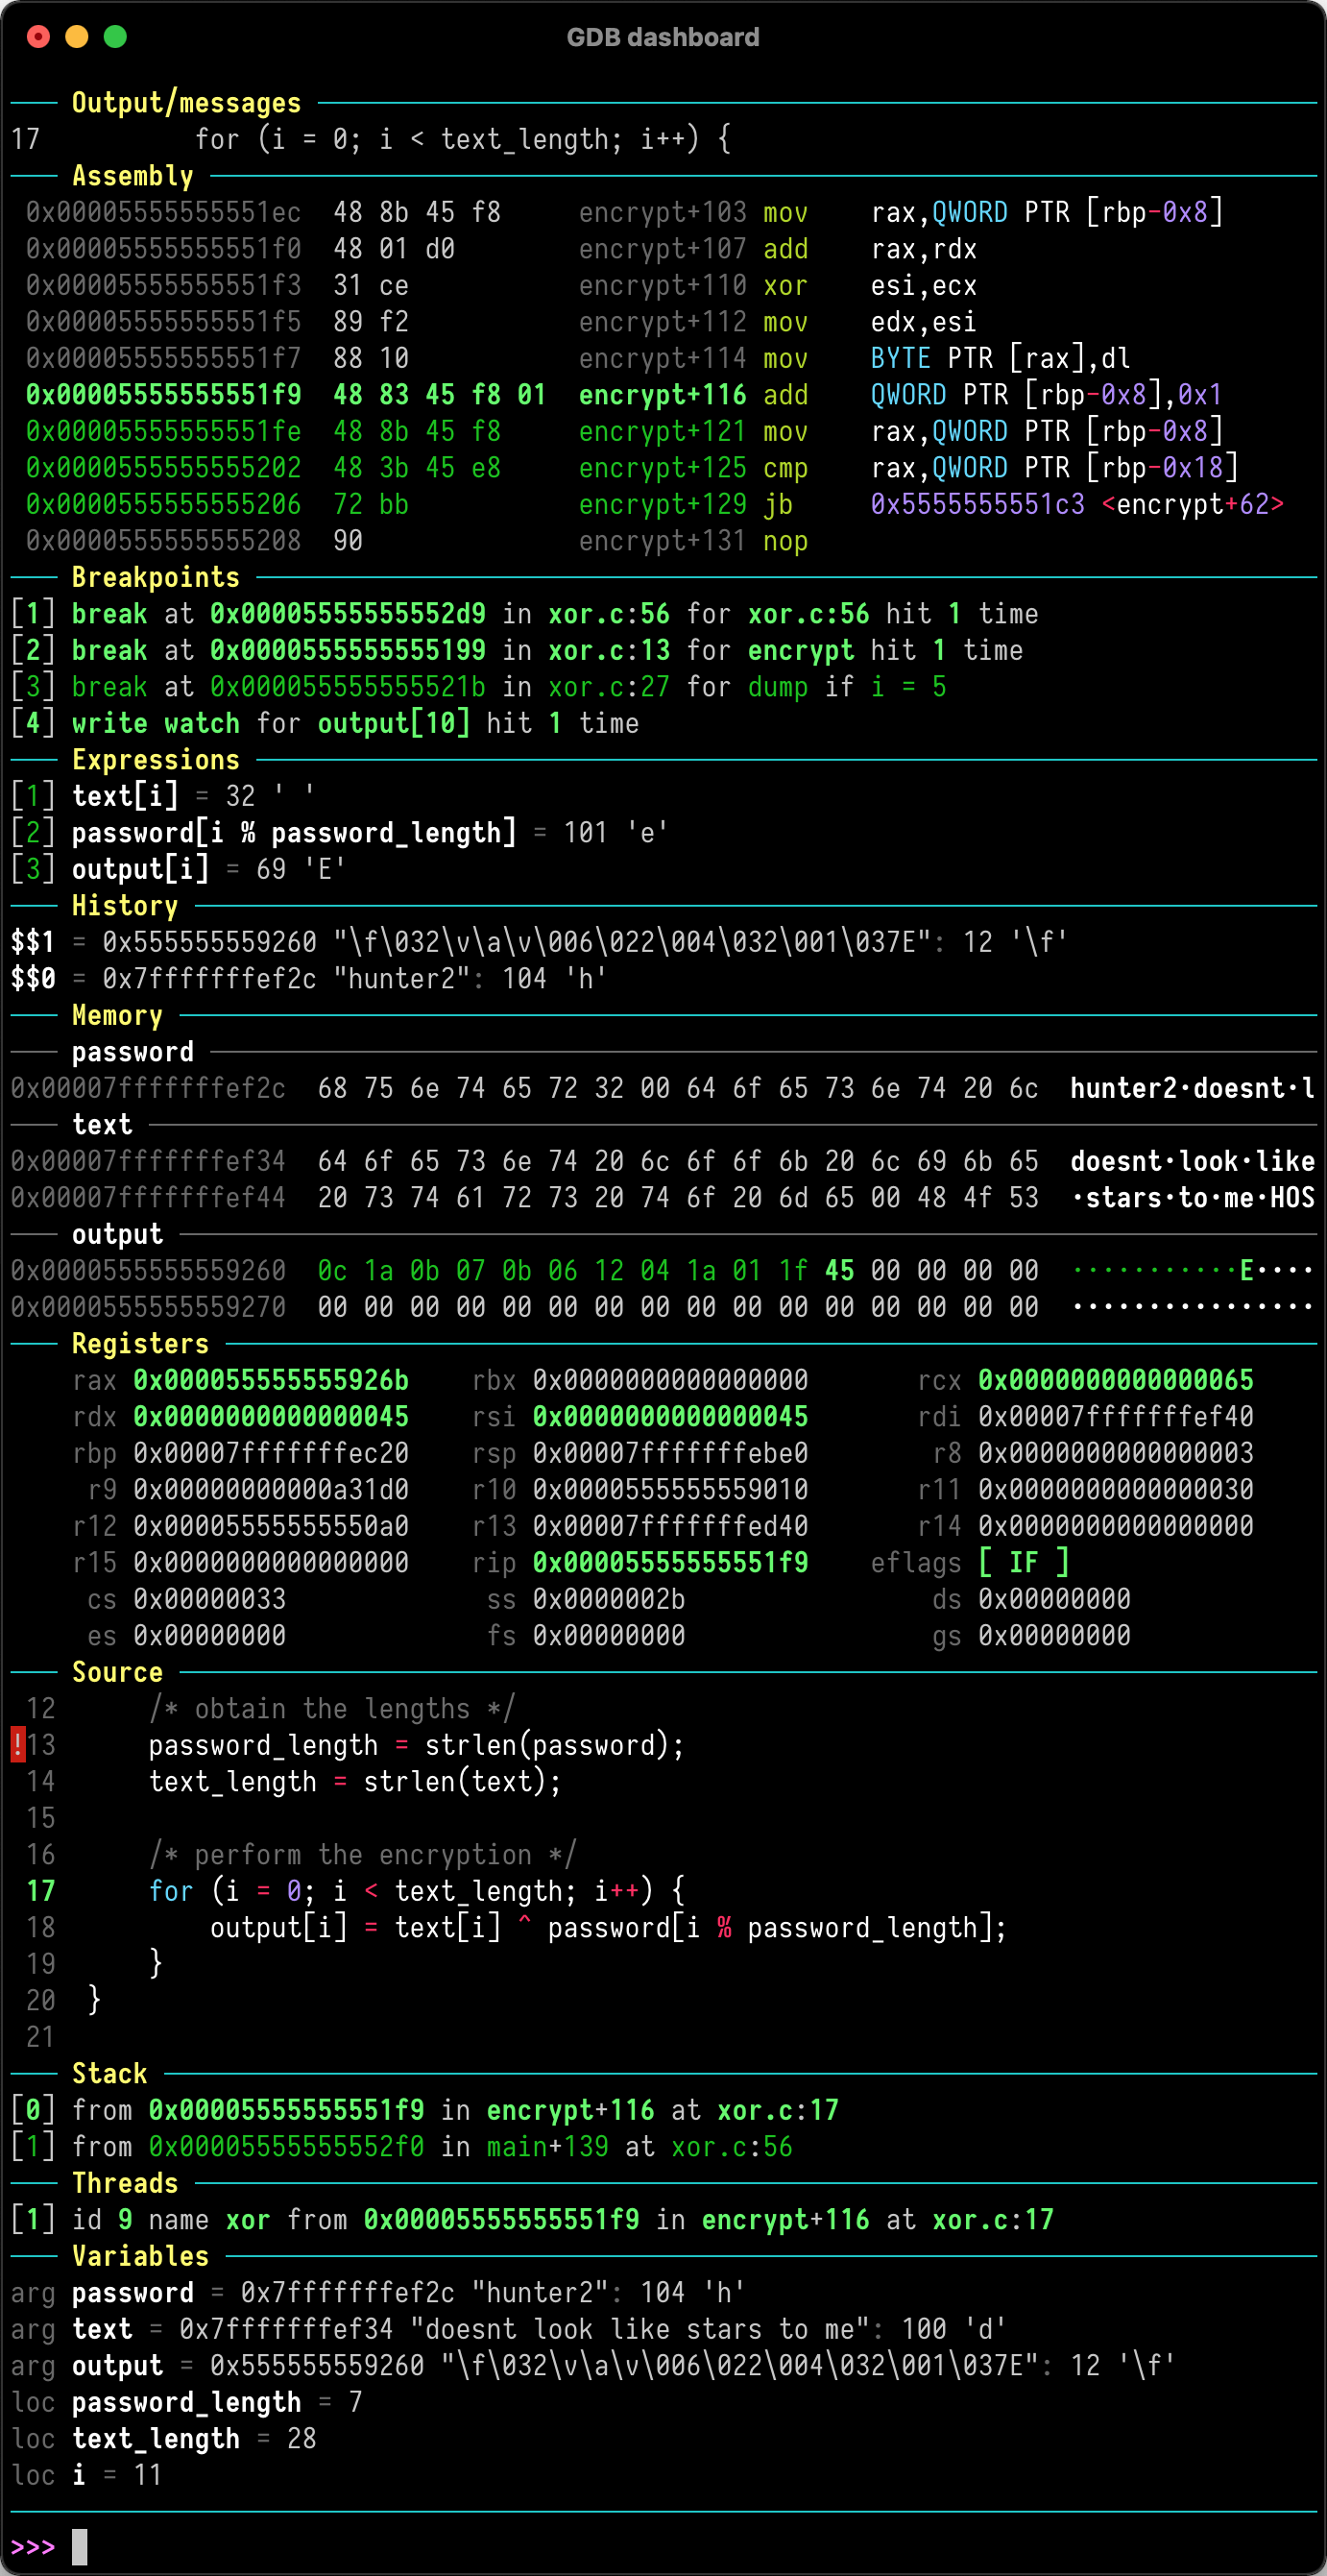 cyrus-and/gdb-dashboard
Modular GDB interface providing a visual dashboard with customizable panels for inspecting registers, source code, assembly, and program state during…
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
 ffffffff0x/1earn
ffffffff0x 团队维护的安全知识框架,内容包括不仅限于 web安全、工控安全、取证、应急、蓝队设施部署、后渗透、Linux安全、各类靶机writup
 zrax/pycdc
C++ python bytecode disassembler and decompiler
 idoka/awesome-canbus
:articulated_lorry: Awesome CAN bus tools, hardware and resources for Cyber Security Researchers, Reverse Engineers, and Automotive Electronics…
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 mandiant/flare-floss
FLARE Obfuscated String Solver - Automatically extract obfuscated strings from malware.
 ljagiello/ctf-skills
Agent skills for solving CTF challenges - web exploitation, binary pwn, crypto, reverse engineering, forensics, OSINT, and more
 burrowers/garble
Obfuscates Go builds by wrapping the Go toolchain, replacing identifiers, package paths, and position data with hashes and stripping debug and build…
 riscv-software-src/riscv-isa-sim
Functional RISC-V ISA simulator supporting multiple extensions (RV32/64, V, cryptography) with interactive debug mode, GDB integration, and…

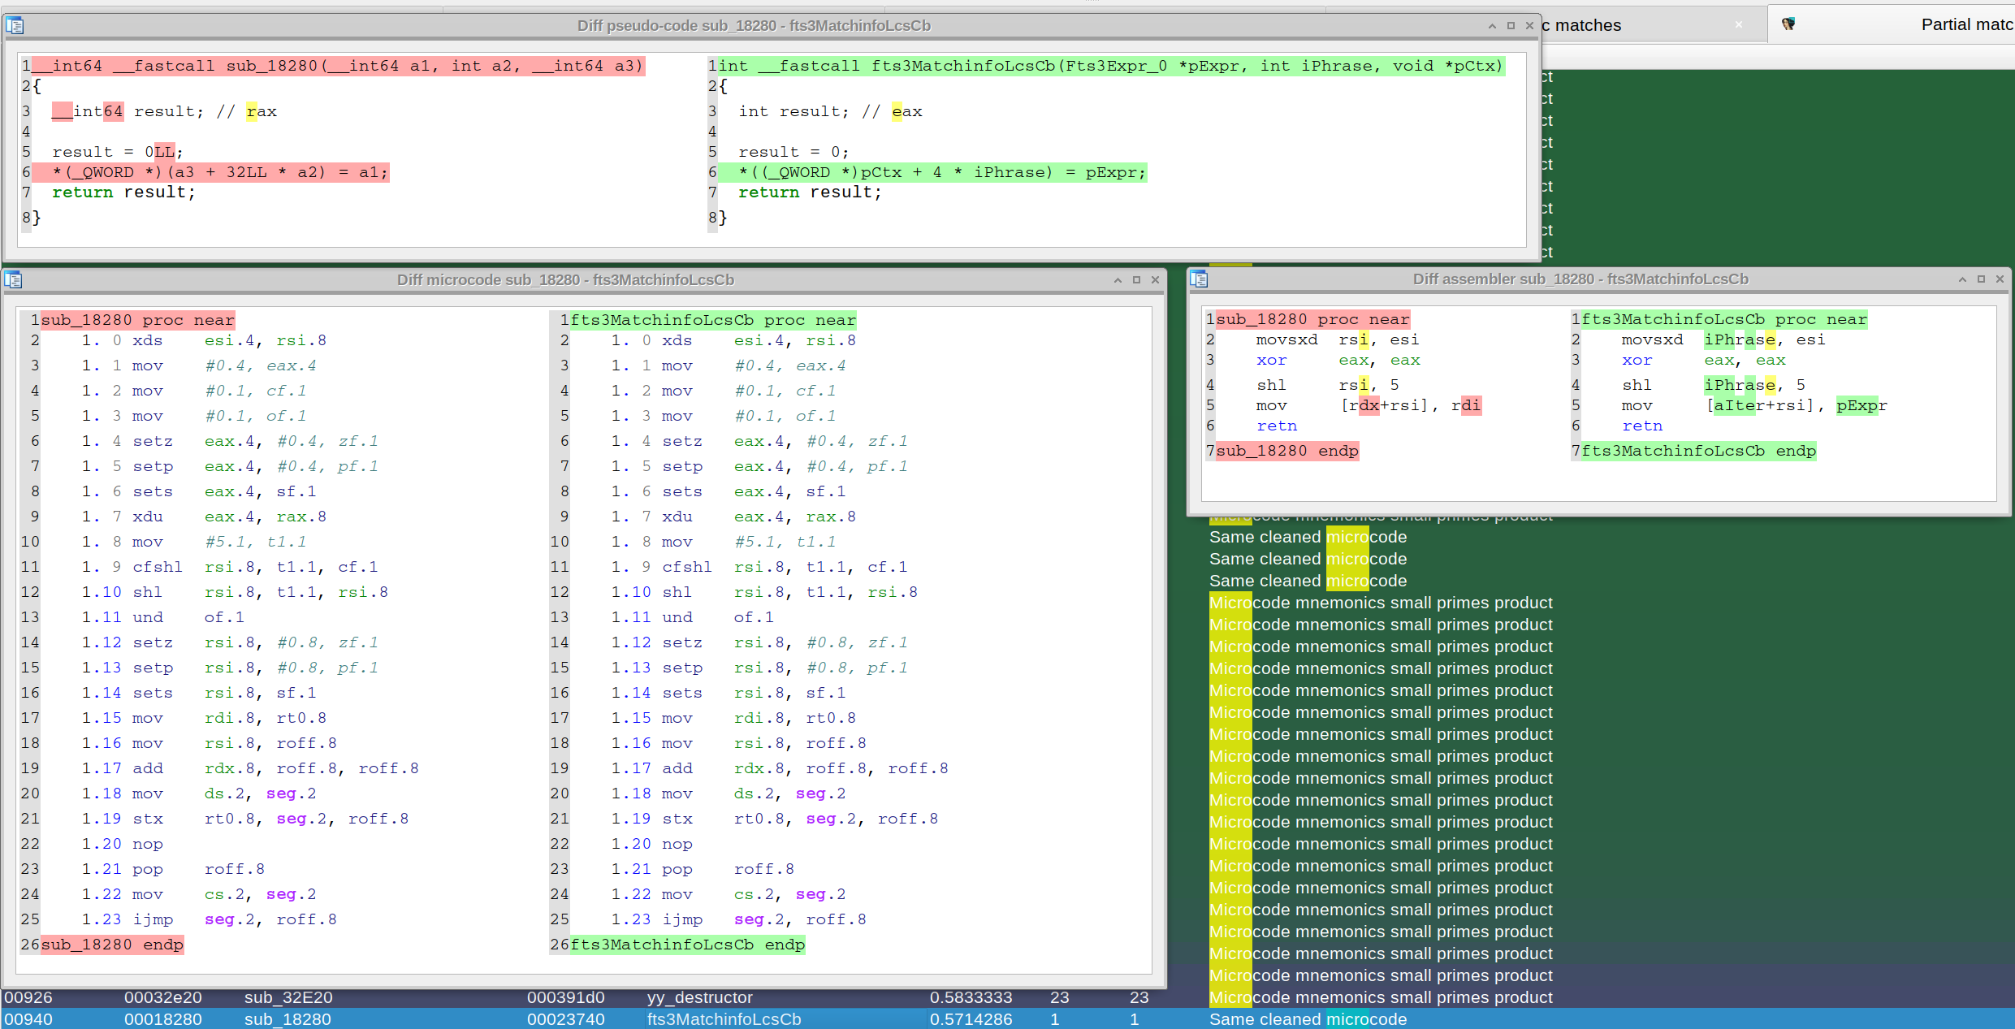 joxeankoret/diaphora
Diaphora, the most advanced Free and Open Source program diffing tool.
 bethington/ghidra-mcp
MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…
 rocky/python-uncompyle6
A cross-version Python bytecode decompiler
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…






