
 #1
Tools for gathering information about targets and identifying attack surfaces.
Kitploit recommended

 a-poc/blueteam-tools
Tools and Techniques for Blue Team / Incident Response
 daffainfo/allaboutbugbounty
All about bug bounty (bypasses, payloads, and etc)
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
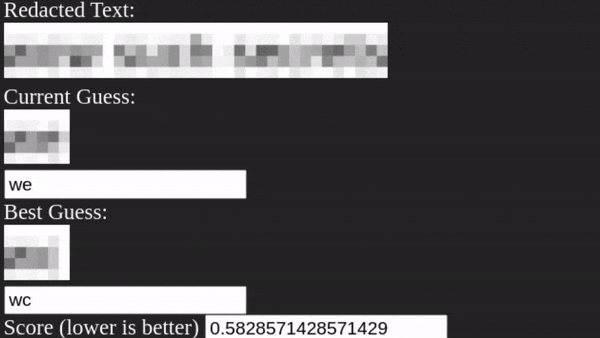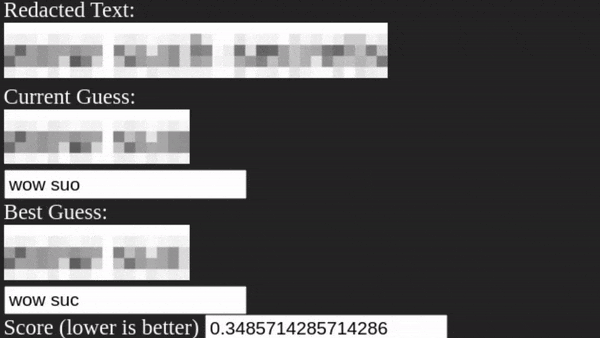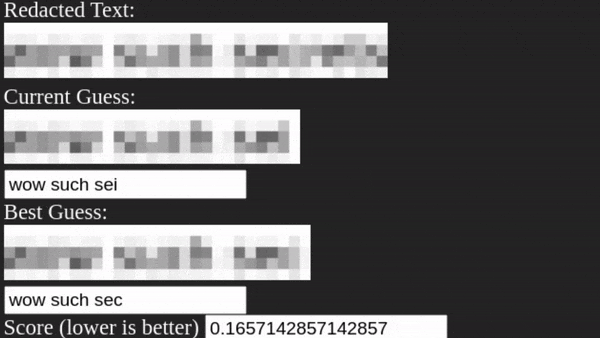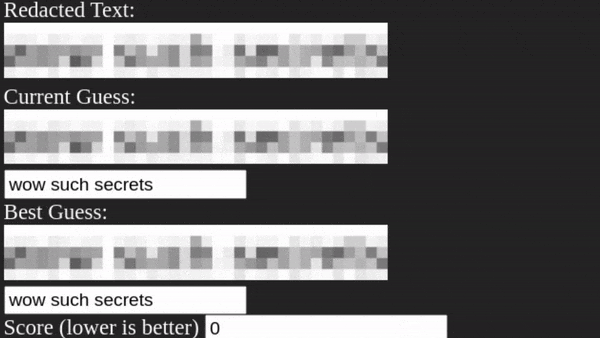 bishopfox/unredacter
Never ever ever use pixelation as a redaction technique
 aboul3la/sublist3r
Fast subdomains enumeration tool for penetration testers
 kingofbugbounty/kingofbugbountytips
Our main goal is to share tips from some well-known bughunters. Using recon methodology, we are able to find subdomains, apis, and tokens that are…
 autorecon/autorecon
Multi-threaded network reconnaissance tool that automates service enumeration, port scanning, and information gathering for penetration testing and…
 w00t3k/awesome-cellular-hacking
Awesome-Cellular-Hacking
 alessandroz/lazagne
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
 shmilylty/oneforall
Multi-source subdomain enumeration tool with 50+ collection modules, DNS brute-force, passive DNS analysis, certificate transparency, search engine…
 ntop/ndpi
Open Source Deep Packet Inspection Software Toolkit
 samratashok/nishang
Nishang - Offensive PowerShell for red team, penetration testing and offensive security.
 efforg/rayhunter
Rust tool to detect cell site simulators on an orbic mobile hotspot
 projectdiscovery/naabu
A fast port scanner written in go with a focus on reliability and simplicity. Designed to be used in combination with other tools for attack surface…
 ihebski/defaultcreds-cheat-sheet
One place for all the default credentials to assist the Blue/Red teamers identifying devices with default password 🛡️
 webbreacher/whatsmyname
Community-maintained dataset of 700+ websites for finding accounts by username — powers OSINT and digital footprint tools.
 olivierlaflamme/cheatsheet-god
Penetration Testing Reference Bank - OSCP / PTP & PTX Cheatsheet
 osintbrazuca/osint-brazuca
Repositório criado com intuito de reunir informações, fontes(websites/portais) e tricks de OSINT dentro do contexto Brasil.







