
 #1
Tools for gaining higher-level permissions or unauthorized access on compromised systems.
Kitploit recommended
 gtworek/priv2admin
Exploitation paths allowing you to (mis)use the Windows Privileges to elevate your rights within the OS.
 intelisecurelabs/linux_exploit_suggester
Linux Exploit Suggester; based on operating system release number
 s3cur3th1ssh1t/winpwn
Automation for internal Windows Penetrationtest / AD-Security
 daem0nc0re/privfu
Kernel mode WinDbg extension and PoCs for token privilege investigation.
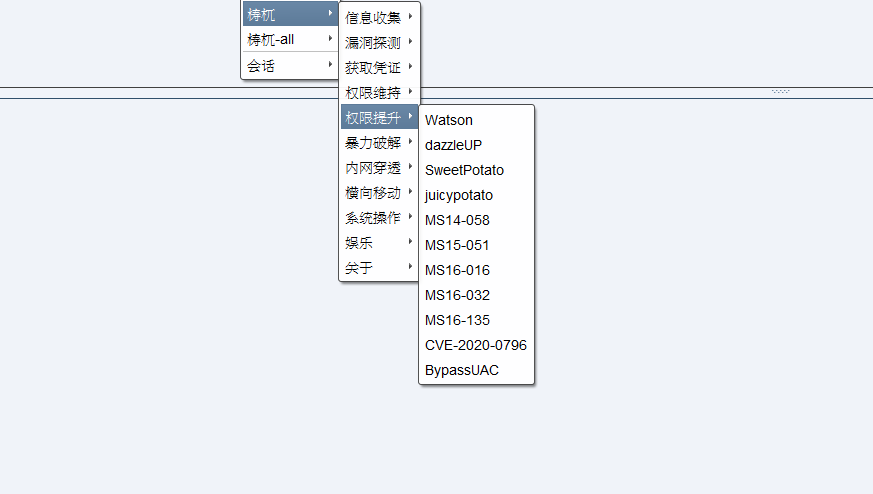 pandasec888/taowu-cobalt_strike
Red team automation framework built on Cobalt Strike, integrating exploit modules, post-exploitation tools, and lateral movement capabilities for…
 specterops/sharphound
Collects Active Directory object metadata, group memberships, sessions, ACLs, and trusts to feed BloodHound attack-path mapping for security…
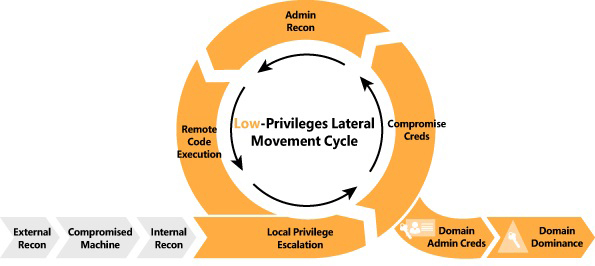 ihebski/a-red-teamer-diaries
RedTeam/Pentest notes and experiments tested on several infrastructures related to professional engagements.
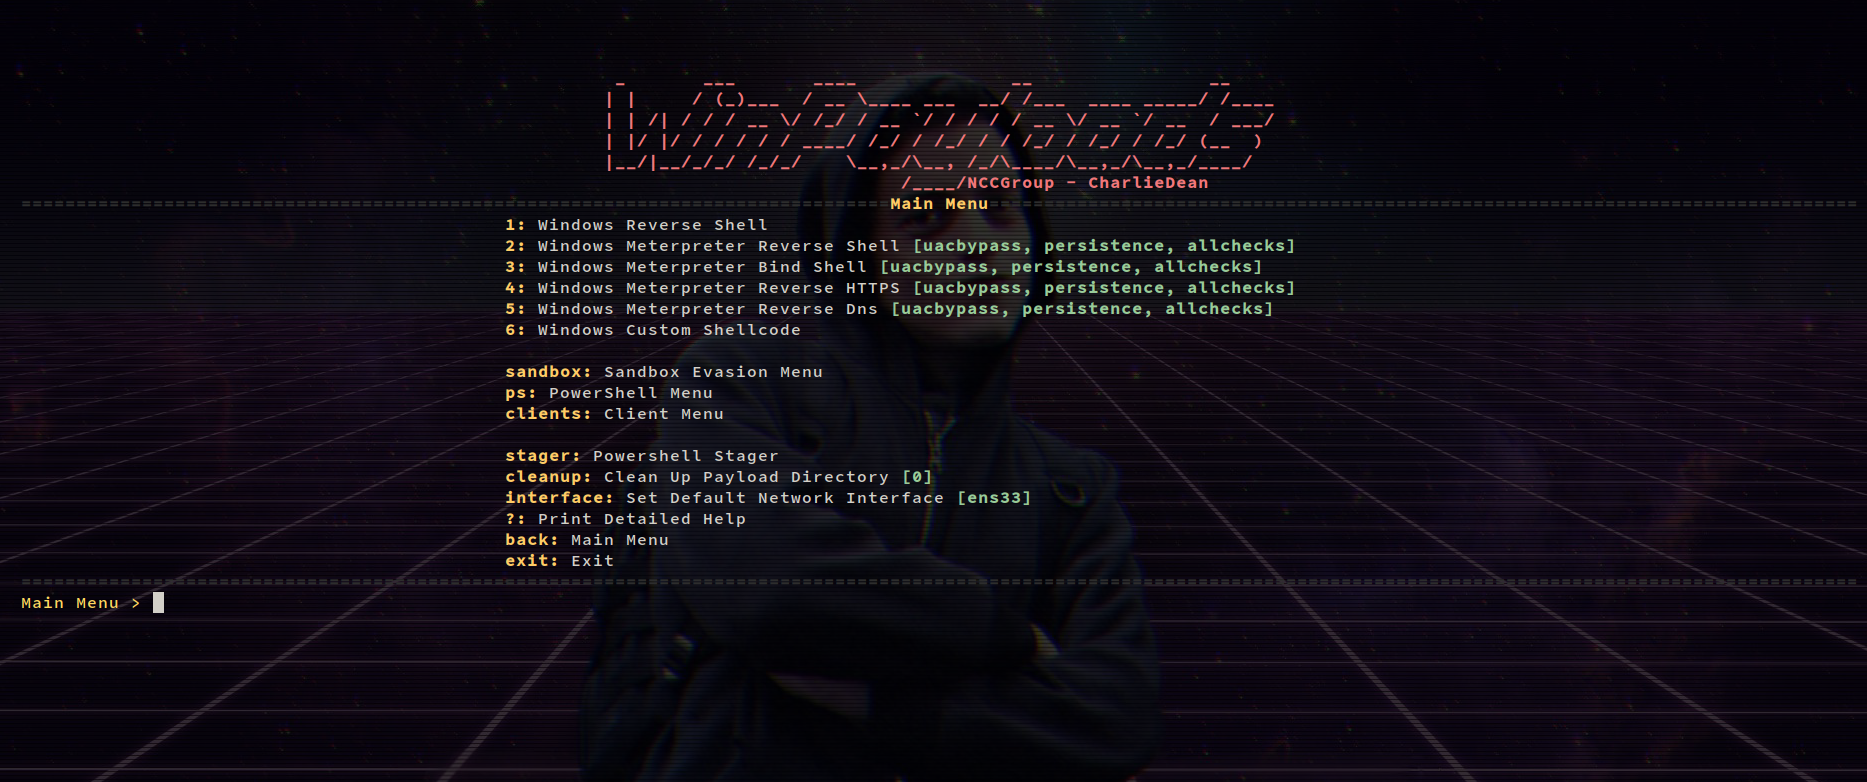 nccgroup/winpayloads
Undetectable Windows Payload Generation
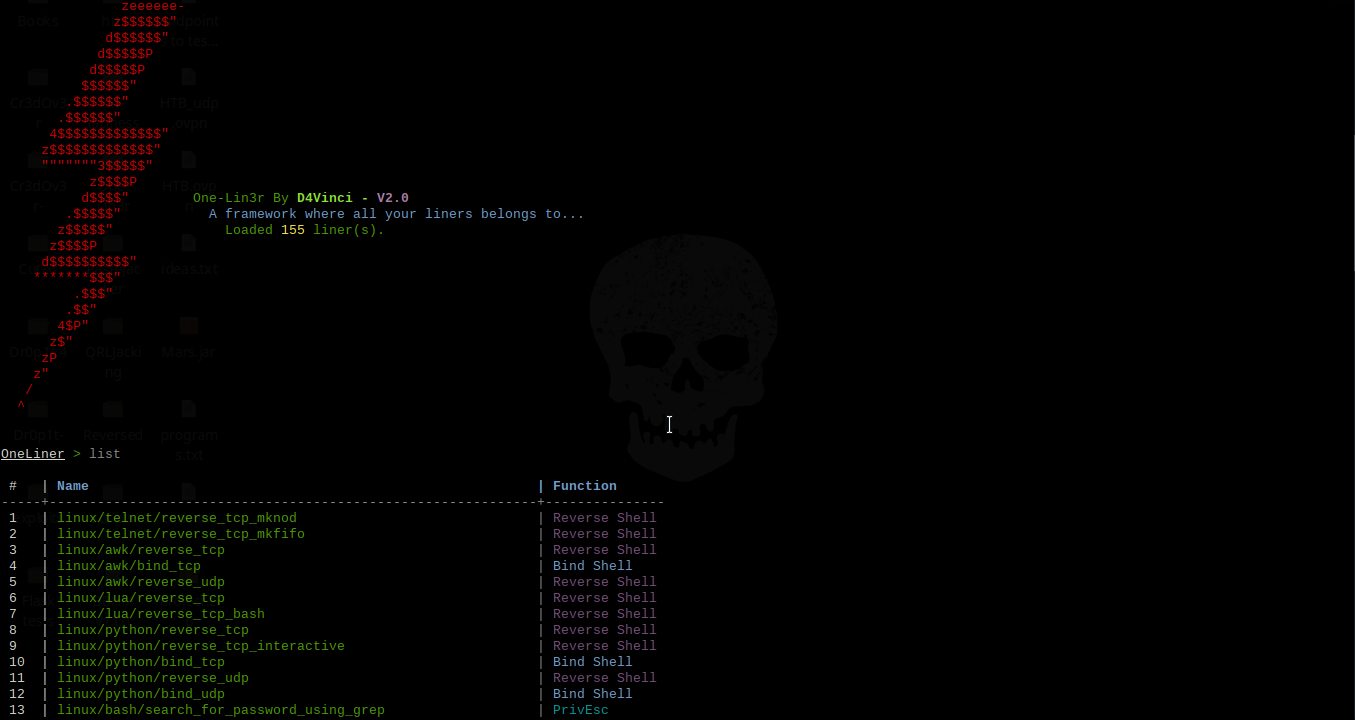 d4vinci/one-lin3r
Gives you one-liners that aids in penetration testing operations, privilege escalation and more
 sleventyeleven/linuxprivchecker
Local Linux enumeration script that identifies privilege escalation vectors including misconfigurations, world-writable files, clear-text passwords,…
 busung-dev/root-my-galaxy
KSU installer for supported Samsung Galaxy firmware with CVE-2026-43499
 wavestone-cdt/edrsandblast
Weaponizes vulnerable signed drivers to bypass EDR kernel callbacks, object callbacks, ETW TI provider, and userland hooks for LSASS memory dumping…
 inguardians/peirates
Peirates - Kubernetes Penetration Testing tool
 ascotbe/kernelhub
:palm_tree:Linux、macOS、Windows Kernel privilege escalation vulnerability collection, with compilation environment, demo GIF map, vulnerability…
 cn33liz/p0wnedshell
PowerShell Runspace Post Exploitation Toolkit
 fortra/nanodump
The swiss army knife of LSASS dumping
 xairy/kernel-exploits
My proof-of-concept exploits for the Linux kernel
 bytecode77/r77-rootkit
Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.







