
 #1
Tools for gaining higher-level permissions or unauthorized access on compromised systems.
Kitploit recommended
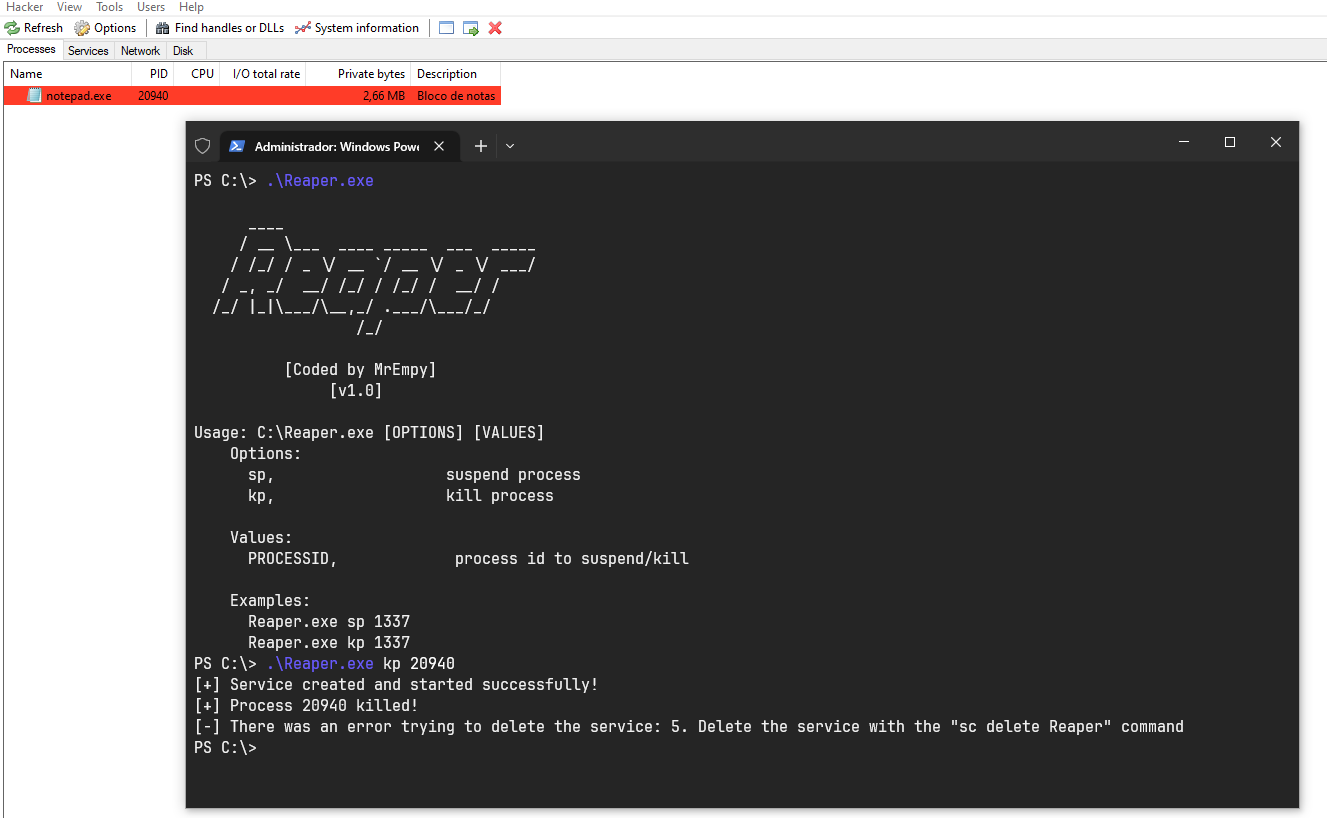
 brosck/reaper
Proof-of-concept BYOVD exploit targeting kprocesshacker.sys driver to kill or suspend processes with kernel-level privileges on Windows systems.
 rwfpl/rewolf-msi-exploit
MSI NTIOLib/WinIO Local Privilege Escalation exploit
 kyxiaxiang/360wfp_exploit
BYOVD: Use 360 WFP driver to block EDR/XDR network connection.
 t0thkr1s/gtfobins-cli
Search for Unix binaries that can be exploited to bypass system security restrictions.
 mhaskar/fsquirtcplpoc
PoC for generating bthprops.cpl module designed to be loaded by Fsquirt.exe LOLBin
 vozec/cve-2026-41651
Exploits a TOCTOU race in PackageKit's transaction handler to install arbitrary packages as root, achieving local privilege escalation and a SUID…
 dor00tkit/cve-2024-30090
CVE-2024-30090 - LPE PoC
 gdbinit/mach_race
Local privilege escalation exploit for macOS (CVE-2016-1757) using Mach IPC race condition to bypass SIP and SUID protections, targeting multiple OS…
 fortalice/modifycerttemplate
ADCS cert template modification and ACL enumeration
 exodusintel/cve-2019-0808
Win32k Exploit by Grant Willcox
 sndav/cve-2026-31431-advanced-exploit
Exploit for CVE-2026-31431, a Linux kernel AF_ALG AEAD page-cache write vulnerability enabling unprivileged arbitrary 4-byte writes to readable files…
 trustedsec/pplfaultdumpbof
Cobalt Strike BOF that exploits a Windows Protected Process Light bypass to dump protected processes, enabling credential access from LSASS.
 tamirzb/cve-2021-1961
Exploit code for CVE-2021-1961
 lithium876/controll_remote_access_trojan
Created a VERY SIMPLE remote access Trojan that will establish administrative control over any windows machine it compromises.
 supersonic/tlpe
CVE-2026-49881, using insecure context creation in Android 17's Telecom service to execute arbitrary code as UID 1000 system_server from an…
 sec-consult/msiscan
Scanning tool for identifying local privilege escalation issues in vulnerable MSI installers
 tyranid/exploitdotnetdcom
A tool to exploit .NET DCOM for EoP and RCE. Is fixed in latest versions of the .NET.
 itaymigdal/lolspoof
An interactive shell to spoof some LOLBins command line








