
 #1
Tools for maintaining access, exploring, and expanding control within compromised systems and networks.
Kitploit recommended
 sv3nbeast/cve-2020-1472
CVE-2020-1472复现时使用的py文件整理打包
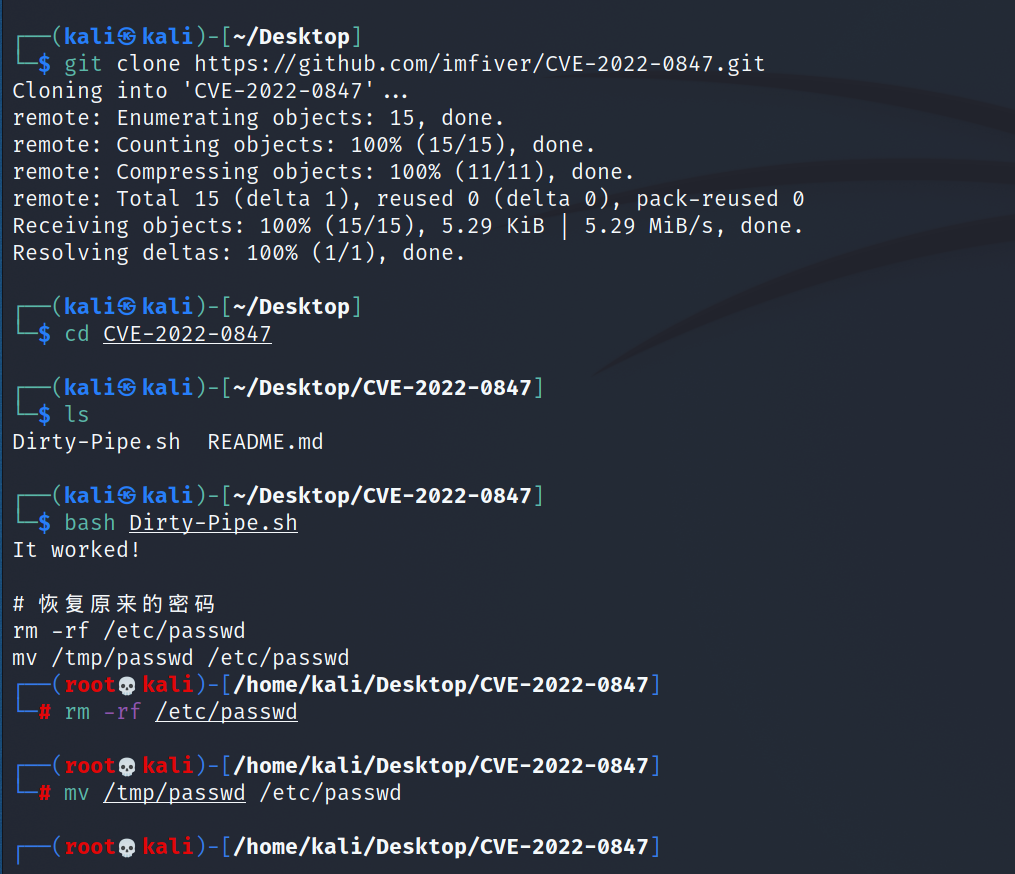 r1is/cve-2022-0847
CVE-2022-0847-DirtyPipe-Exploit CVE-2022-0847 是存在于 Linux内核 5.8 及之后版本中的本地提权漏洞。攻击者通过利用此漏洞,可覆盖重写任意可读文件中的数据,从而可将普通权限的用户提升到特权 root。 CVE-2022-0847…
 ph4ntonn/cve-2017-16995
👻CVE-2017-16995
 thinkycx/cve-2017-8890
CVE-2017-8890 exploit implementation with detailed analysis documents for privilege escalation on Ubuntu 16.04 and Nexus 6P kernels.
 darabium/cve-2024-28987
**CVE-2024-28987** is a critical vulnerability in SolarWinds Web Help Desk (WHD) that allows remote attackers to access sensitive ticket information…
 tc4dy/cve-2026-53921-poc-exploit
CVE-2026-53921 – odhcpd Stack Overflow (CVSS 9.8) 🛡️ Vuln detailed and comprehensive Write-Up and Verifier & Multi-exploit for OpenWrt DHCPv6 RCE.…
 skorpion96/cve-2026-40000
A poc for a vulnerability in ZTE File Manager (zte.com.cn.filer) which allows to read arbitrary files from other apps as the privileges of this file…
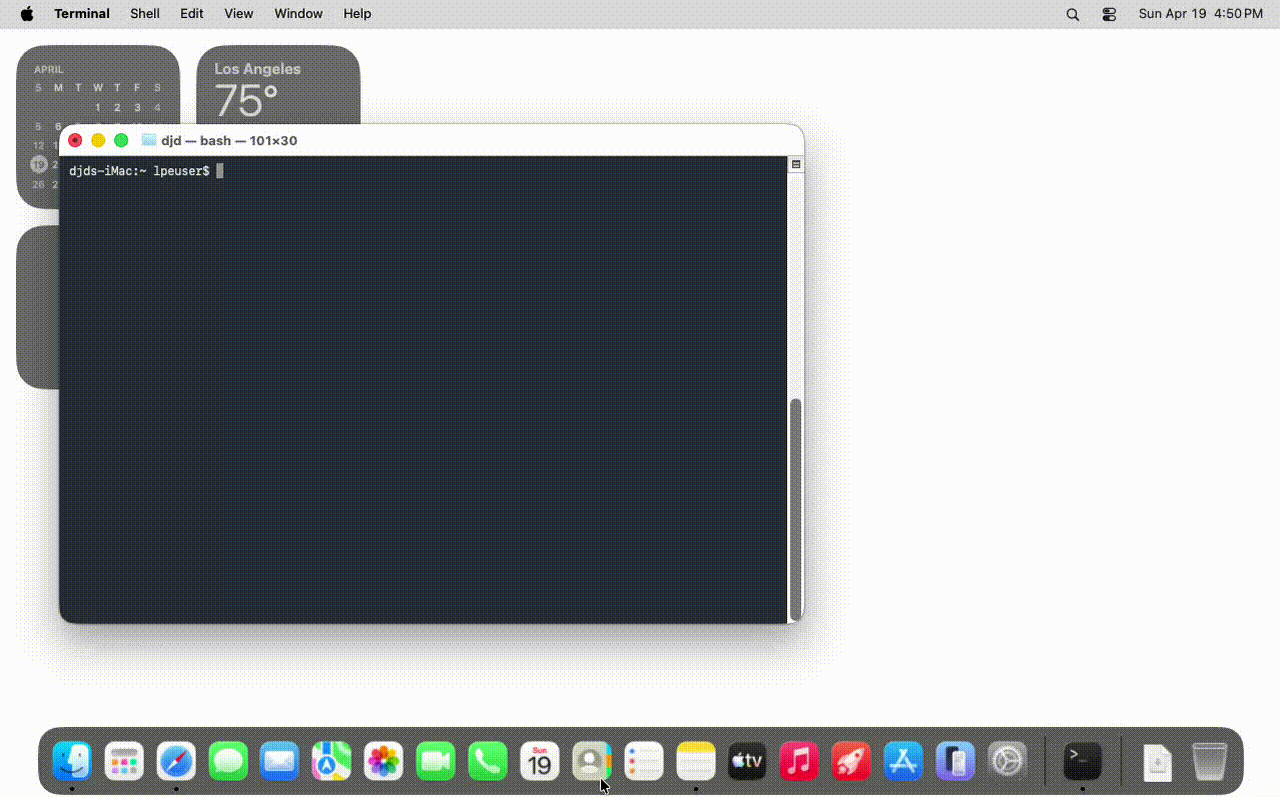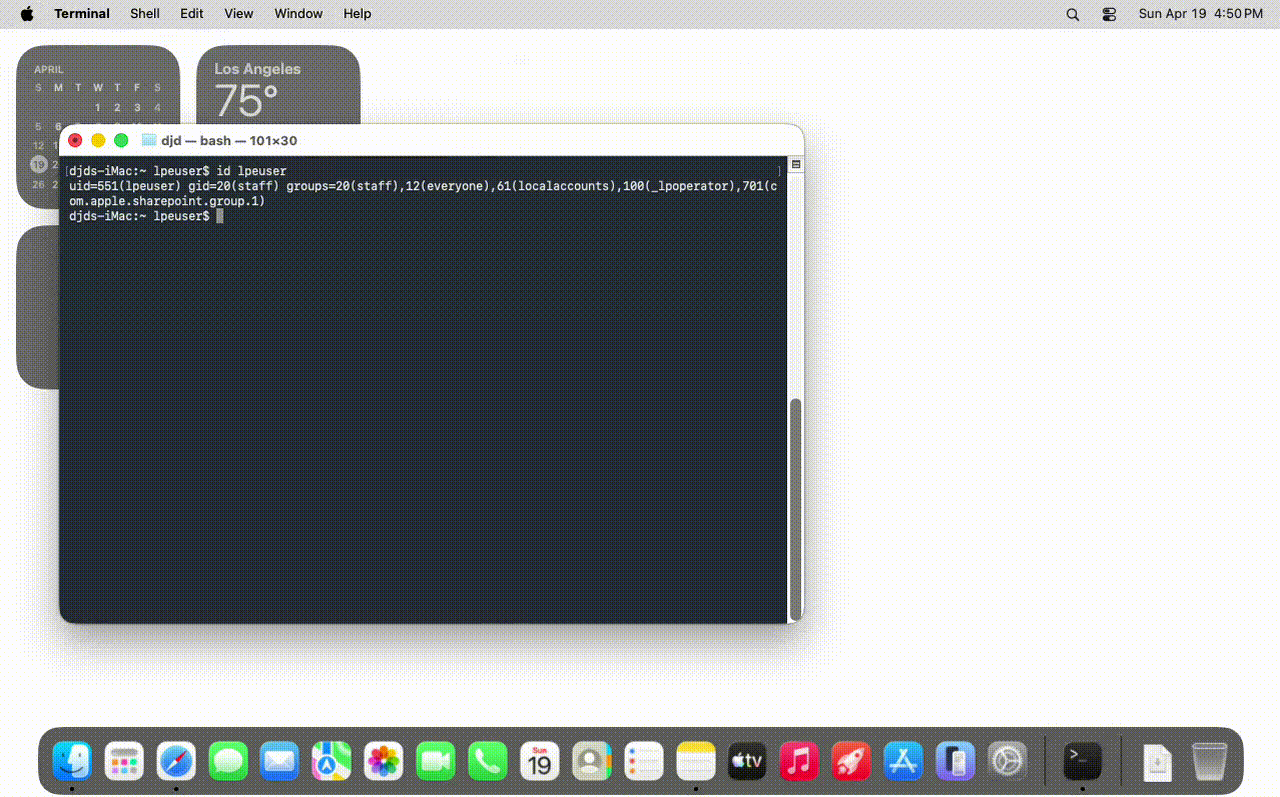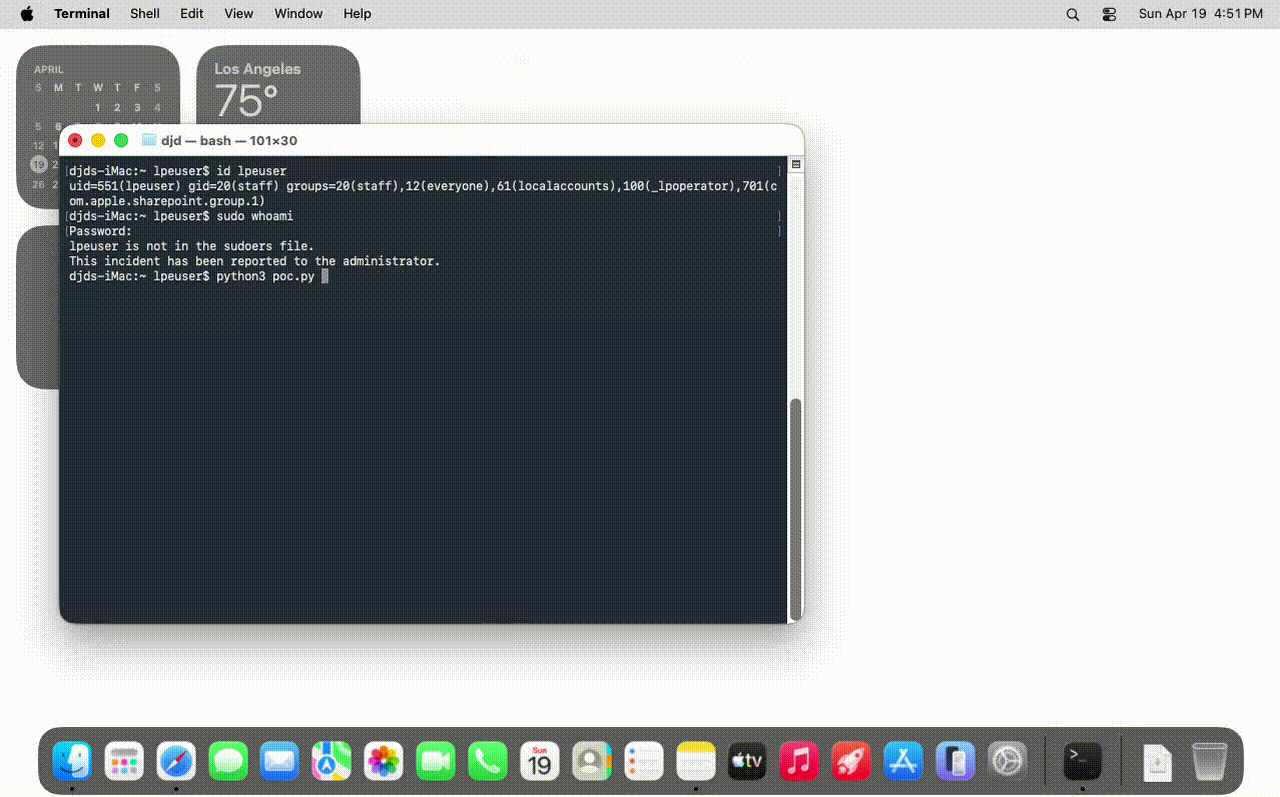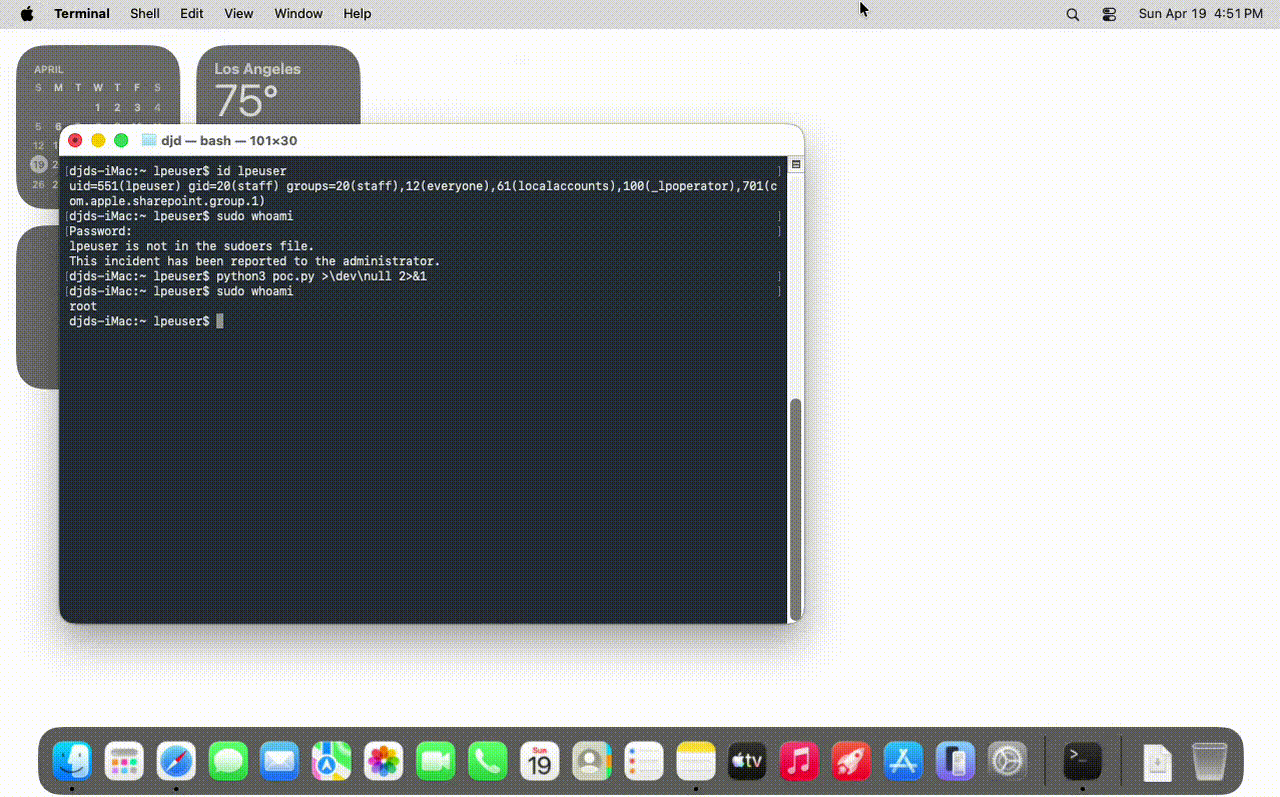 mac-123456789-lab/cve-2026-39875-macos-cups-lpe
Unprivileged user to root on macOS Sonoma, Sequoia, and Tahoe. Patched in macOS 26.6 / 15.7.8 / 14.8.8.
 camsshaft/selinux-permissive-only-cve-2025-21479
This is an SELinux permissive version of the Cheese exploit also known as CVE-2025-21479 which affected the adreno kgsl on many devices including…
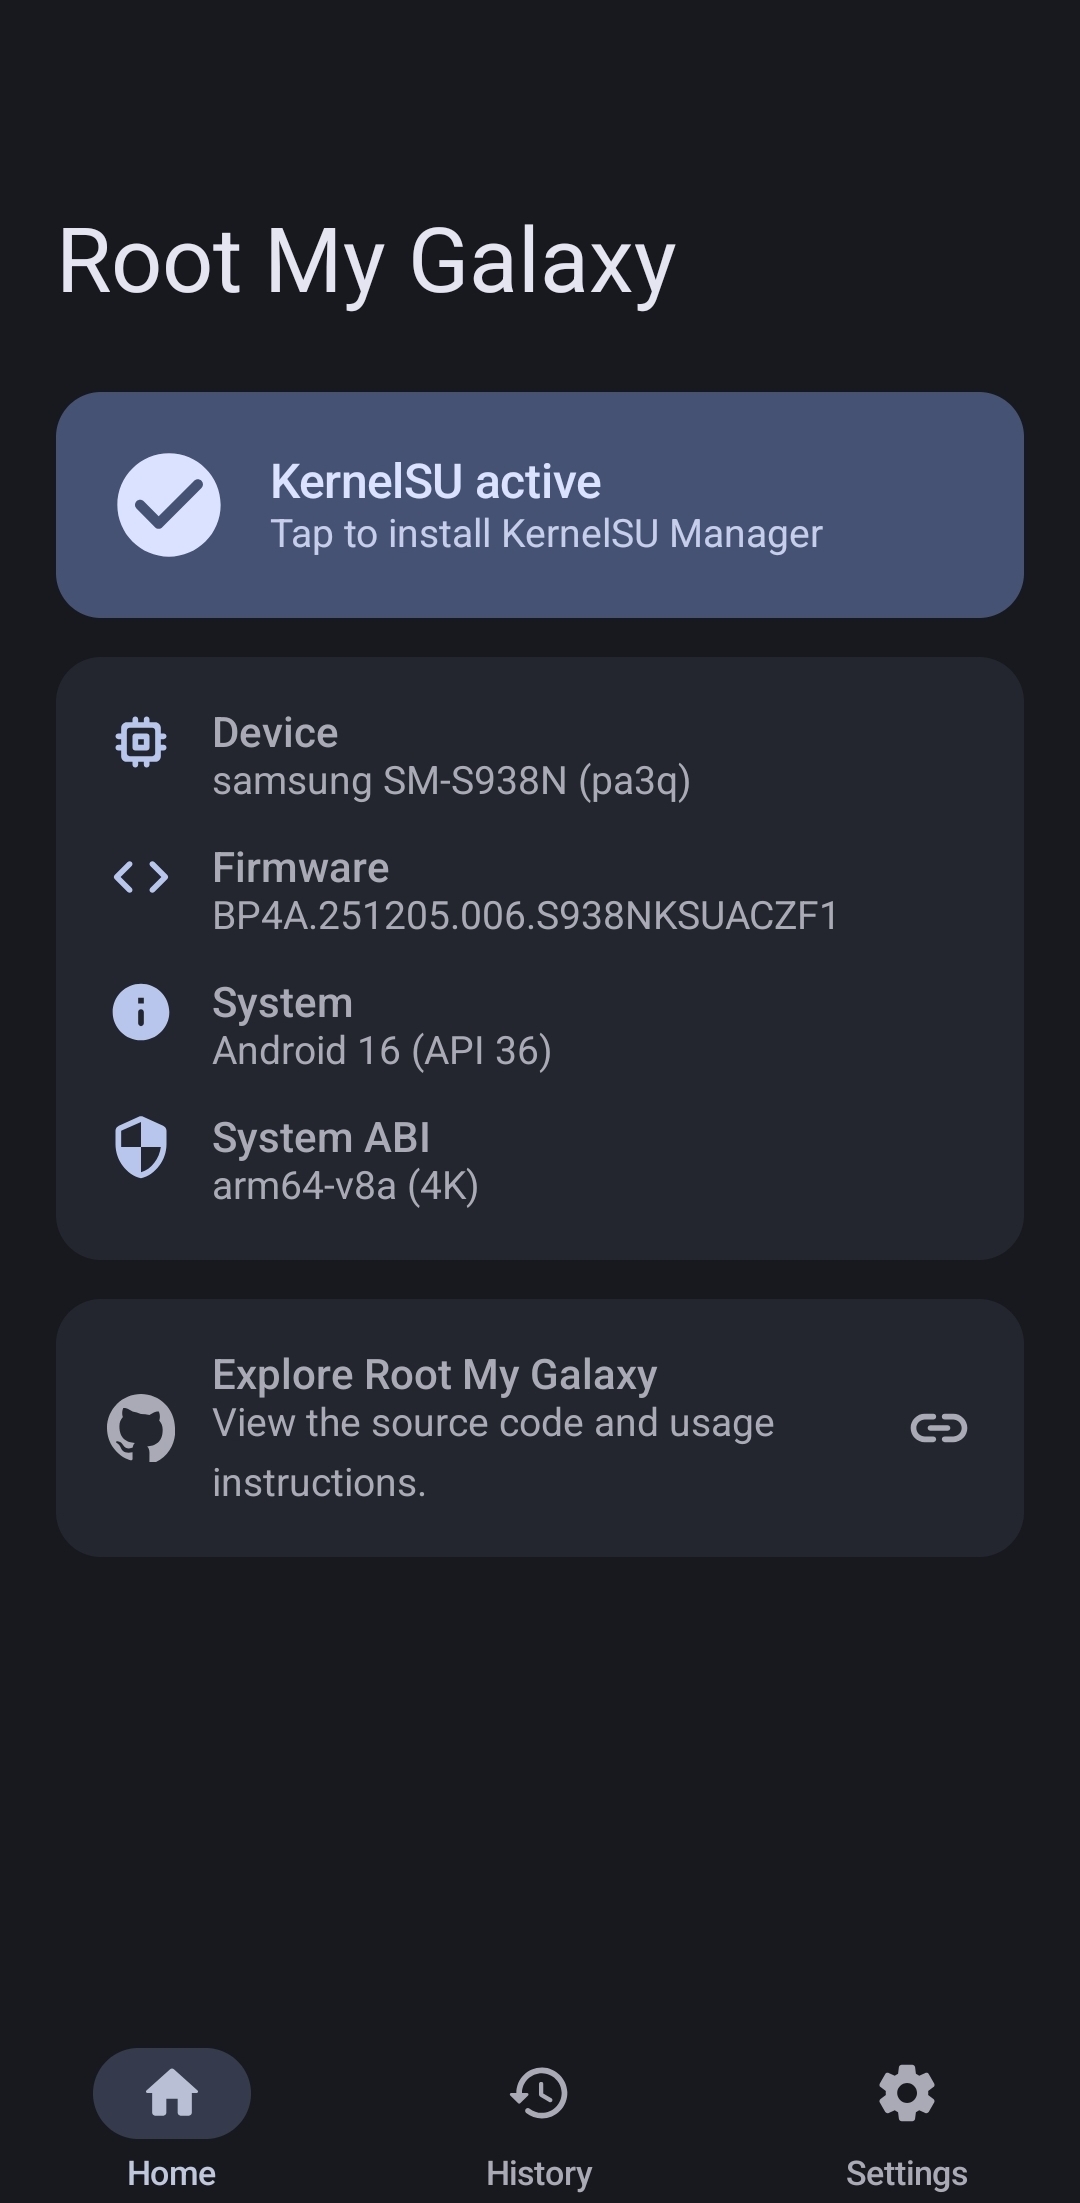 witaqua-tools/root-my-device
KSU installer for supported firmware with CVE-2026-43499
 letsr00t/refluxfs_cve-2026-64600
Technical analysis of CVE-2026-64600, a Linux kernel local privilege escalation in RefluxFS via memory corruption, with mitigation and references for…
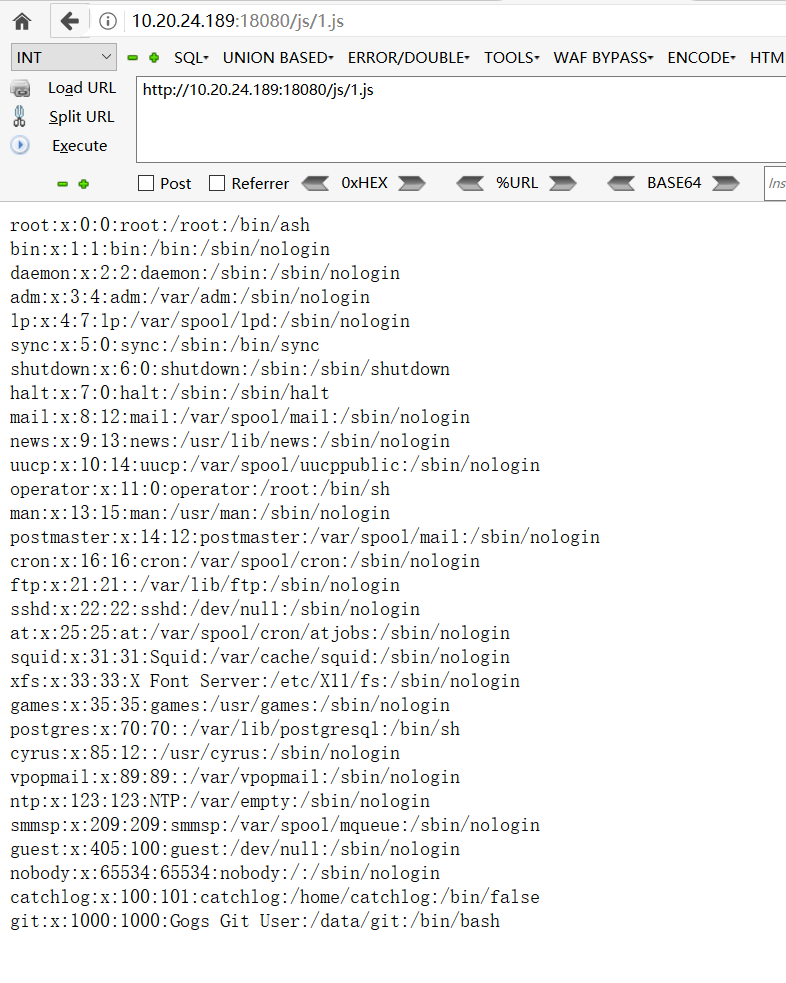 jas502n/gogs_rce
Exploit for Gogs RCE (CVE-2018-18925) leveraging session forgery and Git hook injection to achieve arbitrary command execution with root privileges.
 jas502n/mssql-command-tool
mssql 终端连接工具|命令执行
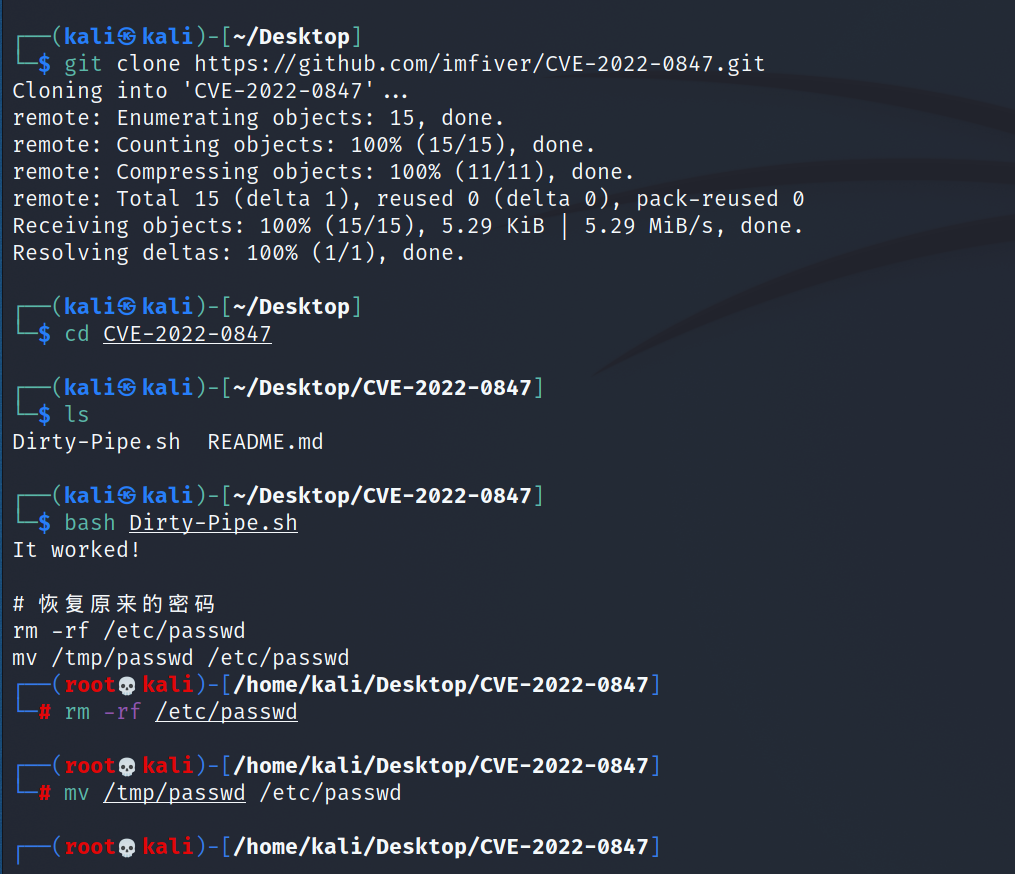 xsxtw/cve-2022-0847
Proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe), a Linux kernel vulnerability enabling local privilege escalation via overwriting read-only…
 vinh0212/cve-2024-23700
PoC for CVE-2024-23700, Android slient privilege escalation allow to read/write contacts, SMS, calendar, call log and voicemail, make outgoing calls…
 xcanwin/cve-2021-4034-uniontechos
统信UOS 桌面操作系统,存在CVE-2021-4034漏洞(Linux Polkit本地权限提升漏洞)。
 mkv4/cve-2018-8453-exp
cve-2018-8453 exp
 meeeeing/cve-2024-36587
Proof-of-concept exploit for CVE-2024-36587 demonstrating local privilege escalation in dnscrypt-proxy via binary planting, with Docker-based…








