
 #1
Tools for discovering open ports, services, and potential entry points on network devices.
Kitploit recommended
 xdavidhu/portspider
🕷 A lightning fast multithreaded network scanner framework with modules.
 isgroup/openmagic
OpenSSL TLS heartbeat read overrun (CVE-2014-0160)
 nhpt/weblogic-ssrf_cve-2014-4210
Weblogic SearchPublicRegistries SSRF(CVE-2014-4210) Exploit Script based on Python3
 internon/inter-recon
Script to perform automatic initial web and vulnerability recon
 nurdilin/cve-2018-16706
Or how I turn off my TV via a cronjob
 znakar/sharktooth
Port Scanner with Docker & Prometheus + Grafana integration. A tool for network auditing with multithreading support and real-time monitoring.
 r4tw1z/cve-2024-6387
This script, created by R4Tw1z, is designed to scan IP addresses to check if they are running a potentially vulnerable version of OpenSSH. The tool…
 cyberdudebivash/cyberdudebivash-fortisiem-cve-2025-64155-scanner
Authorized high-impact tool from CYBERDUDEBIVASH ECOSYSTEM to detect CVE-2025-64155 (FortiSIEM phMonitor Command Injection). Scans for open ports and…

 rek2/goenumerator
A personal tool in GO for my usual first enumeration steps on a target
 sairson/yasso
强大的内网渗透辅助工具集-让Yasso像风一样 支持rdp,ssh,redis,postgres,mongodb,mssql,mysql,winrm等服务爆破,快速的端口扫描,强大的web指纹识别,各种内置服务的一键利用(包括ssh完全交互式登陆,mssql提权,redis一键利用,mysql数据库…
 blindfuzzy/lhf
A modular recon tool for pentesting
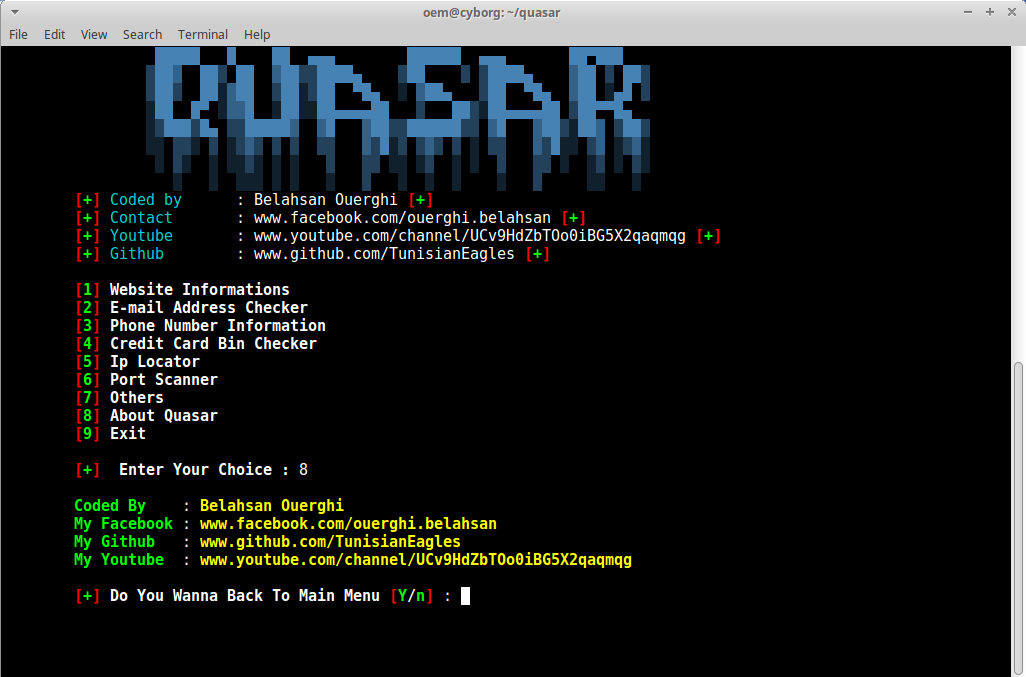 cyb0r9/quasar
Modular information gathering framework for penetration testers, featuring website analysis, email/phone lookup, credit card BIN checking, IP…
 thegenetic/cve-2024-6387-exploit
CVE-2024-6387 exploit
 hackersonlineclub/hocig1_2
HOCig- Automatic HOC Information Gathering Tool V 1.2
 rickgeex/cve-2024-6387-checker
CVE-2024-6387-Check is a streamlined and efficient tool created to detect servers operating on vulnerable versions of OpenSSH.
 slsteff/cve-2020-0688-scanner
Scans for Microsoft Exchange Versions with masscan
 parbatzone/reconvault
🔍 Recon notes organizer for bug bounty hunters and CTF players — subdomains, ports, endpoints, vulns, all in one place.
 rishabh-kumar-cyber-sec/cve-2023-27163-ssrf-to-port-scanning
It is a simple script to automate internal port scanning dueto SSRF in requests-baskets v 1.2.1. this script can also assisst in solving 'SAU'…








