
 #1
Tools for discovering open ports, services, and potential entry points on network devices.
Kitploit recommended

 eldraco/domain_analyzer
Analyze the security of any domain by finding all the information possible. Made in python.
 chvancooten/bugbountyscanner
A Bash script and Docker image for Bug Bounty reconnaissance. Intended for headless use.
 nullt3r/jfscan
JF⚡can - Super fast port scanning & service discovery using Masscan and Nmap. Scan large networks with Masscan and use Nmap's scripting abilities to…
 ginjachris/pentmenu
A bash script for recon and DOS attacks
 reddyyz/astsu
A network scanner tool, developed in Python 3 using scapy.
 enenumxela/ps.sh
A bash script that automates port scanning on specified target host(s). The aim of the scripts is reducing scan time, increasing scan efficiency and…
 j0ey17/exploit_cve-2023-27163
Proof of Concept exploit for Server Side Request Forgery vulnerability in Requests Basket v1.2.1 and before.
 nonosticisiguzo-command/nmap-scan-results
Found 200+ vulnerabilities on scanme.nmap.org including CVE-2023-38408 (9.8 critical)
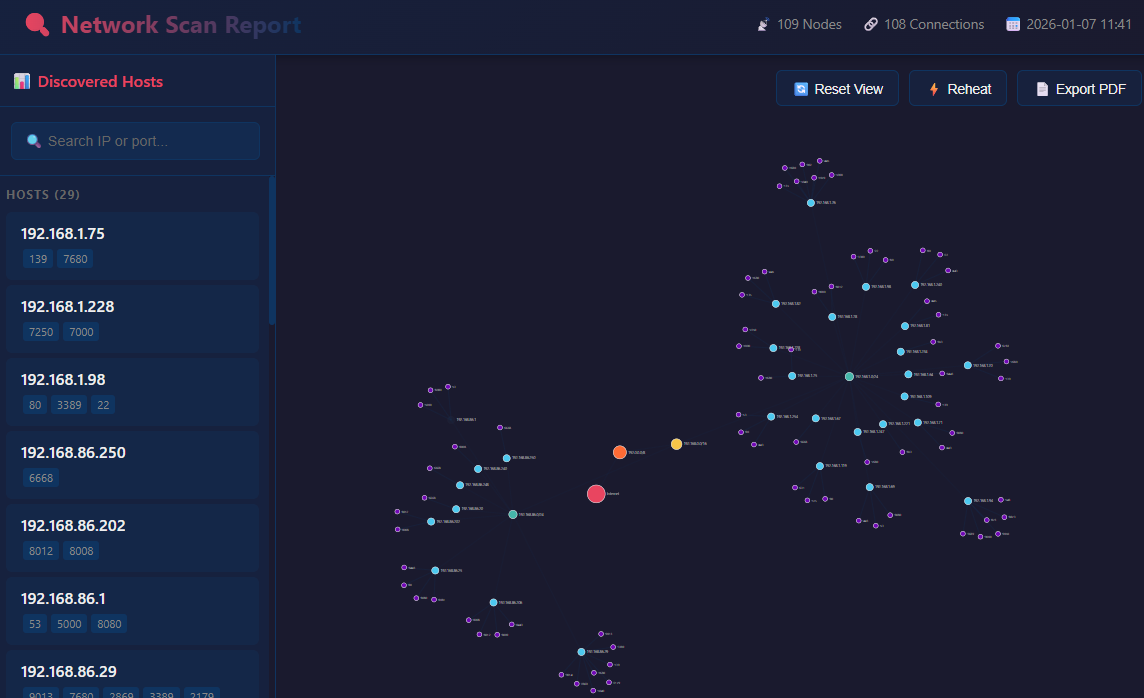 artofscripting/masscan-report
A Python tool that generates interactive React-based HTML visualizations from masscan JSON output, featuring a D3.js force-directed network graph.
 besimorhino/powercat
netshell features all in version 2 powershell
 ekultek/zeus-scanner
Advanced reconnaissance utility
 infosecmatter/minimalistic-offensive-security-tools
A repository of tools for pentesting of restricted and isolated environments.
 zyylhn/zscan
Zscan a scan blasting tool set
 milesrichardson/docker-onion-nmap
Scan .onion hidden services with nmap using Tor, proxychains and dnsmasq in a minimal alpine Docker container.

 flipkart-incubator/rta
Red team Arsenal - An intelligent scanner to detect security vulnerabilities in company's layer 7 assets.
 spyboy-productions/omnisci3nt
Omnisci3nt is an open-source web reconnaissance and intelligence tool for extracting deep technical insights from domains, including subdomains, SSL…
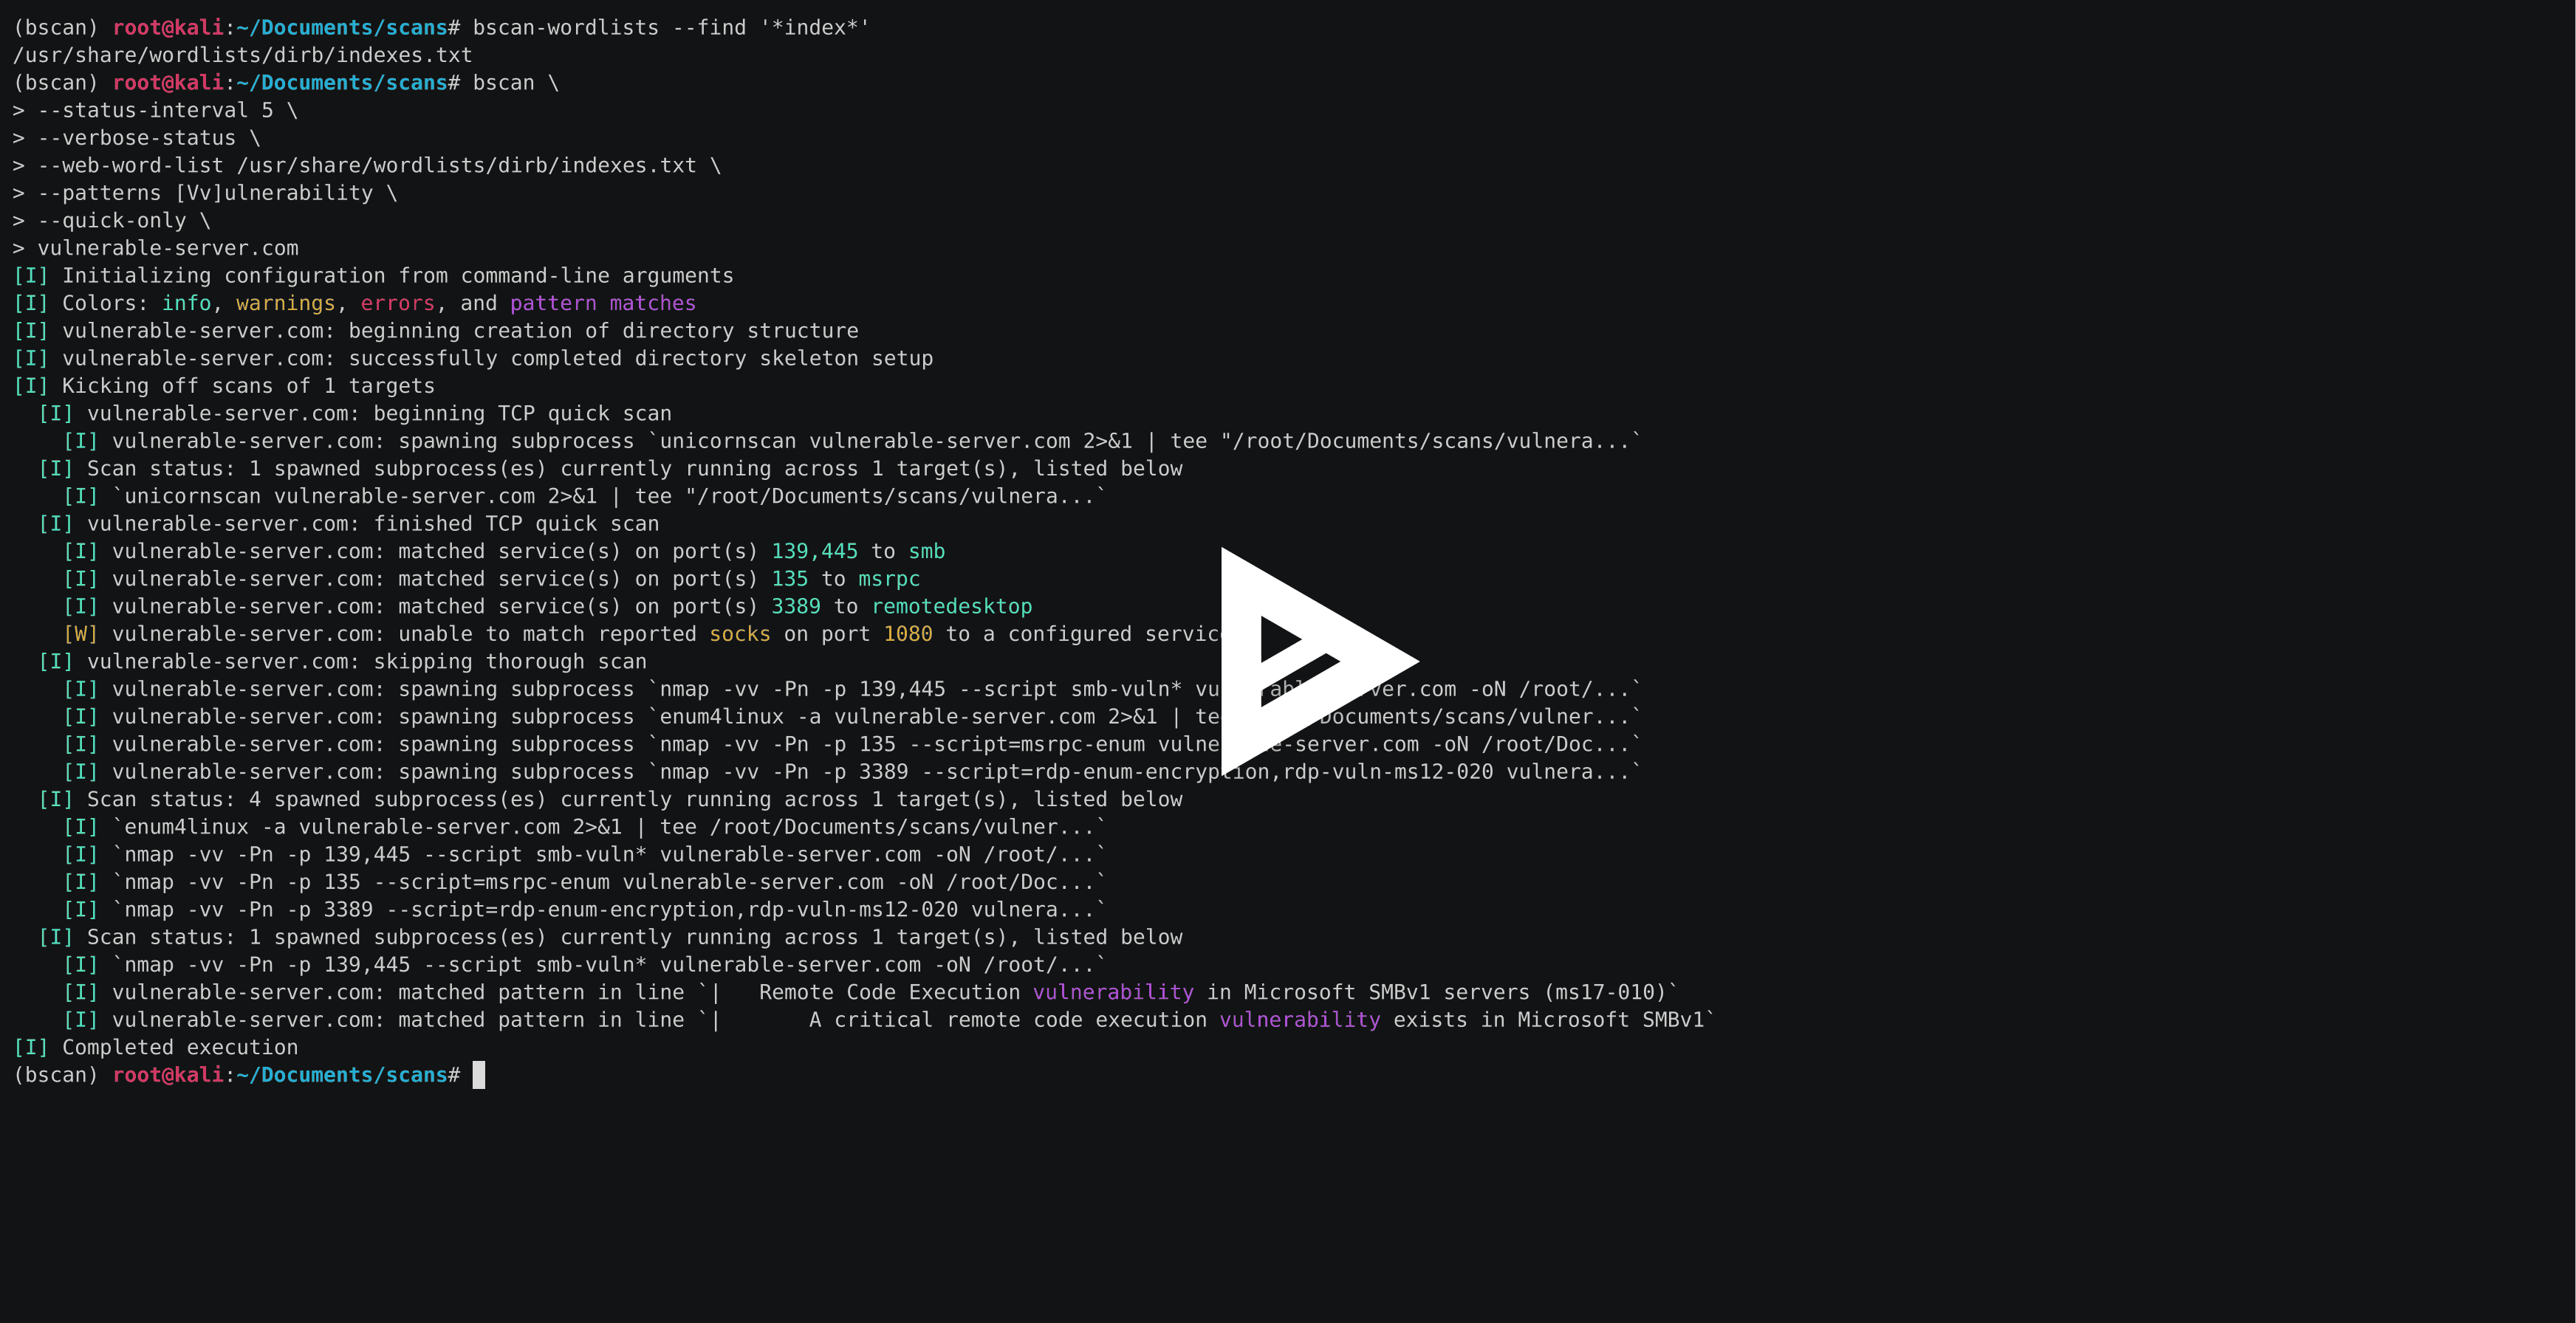 welchbj/bscan
an asynchronous target enumeration tool








