
 #1
Phishing simulation, detection, analysis, and security awareness training tools.
Kitploit recommended
 rpgsec/roundcube-cve-2024-42008-poc
Proof-of-concept exploit for CVE-2024-42008, a Cross-Site Scripting vulnerability in RoundCube webmail. Delivers XSS payloads via contact forms to…
 muhammad-ali007/outlookntlm_cve-2023-23397
Exploit for CVE-2023-23397 Outlook NTLM hash leak via malicious calendar invitations. Includes PowerShell weaponization, Responder integration, and…
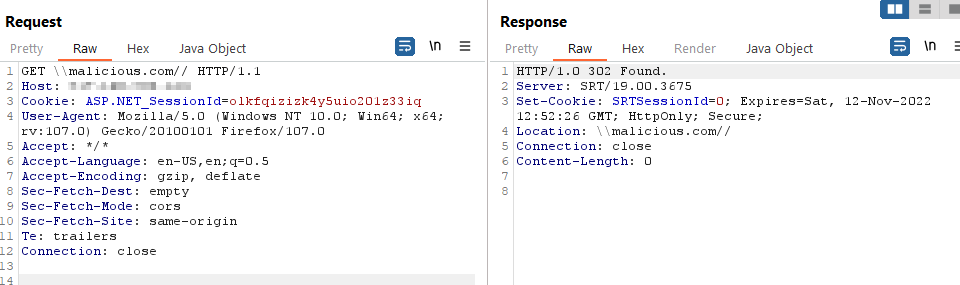 jbalanza/cve-2022-44215
Public disclosure of TitanFTP 19.X Open Redirection vulnerability
 mqkgithub/moniker-link-cve-2024-21413
Step-by-step walkthrough of exploiting CVE-2024-21413 in Microsoft Outlook to bypass Protected View and leak NTLM credentials via Moniker Links,…
 k9-modz/cve-2023-38873-g1
Proof-of-concept demonstrating a Clickjacking vulnerability on the G1 website, with a malicious iframe overlay and social engineering popup for…
 rahultb-sec/cve-2026-33829-writeup
Vulnerability Case Study: CVE-2026-33829 (Windows Snipping Tool NTLM Coercion)
 imthecopilotnow/cve-2025-4102025
Security advisory detailing a critical CVE in Copilot AI where RAG-based citation links are forged to a third-party domain, enabling source…
 shellkraft/cve-2025-3568
A security vulnerability has been identified in Krayin CRM <=2.1.0 that allows a low-privileged user to escalate privileges by tricking an admin into…
 devbuihieu/cve-2025-33053-proof-of-concept
CVE-2025-33053 Proof Of Concept (PoC)
 mlniumm/cve-2025-28073
Proof-of-concept for a reflected XSS vulnerability in phpList 3.6.15 via the /lists/dl.php endpoint, enabling session hijacking and arbitrary…
 nxploited/cve-2025-25101
WordPress Munk Sites plugin <= 1.0.7 - CSRF to Arbitrary Plugin Installation vulnerability
 pescada-dev/cve-2025-22381
Discovering CVE-2025-22381: Host Header Injection in the Aggie Open-Source Project
 0n1con3/fluxer
FluxER - The bash script which installs and runs the Fluxion tool inside Termux. The wireless security auditing tool used to perform WPA/WPA2…
 sanupl/cve-2024-34568
In LetterPress plugin <= 1.2.1 is vulnerable to Cookie Stealing Vulnerability. An attacker can able to steal the cookies by injecting the JavaScript…
 dhananjayasj/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Proof-of-concept exploit for CVE-2024-21413, a critical Outlook RCE vulnerability that leaks NetNTLMv2 hashes via crafted file:// links, enabling…
 polarisxsec/cve-2024-21413
Educational lab demonstrating CVE-2024-21413 exploitation in Outlook to leak NTLM hashes via malicious UNC links, with custom SMTP/POP3…
 vlad-a-man/cve-2023-23397
CVE-2023-23397 PoC
 g37sys73m/cve-2022-46087
CloudSchool v3.0.1 is vulnerable to Cross Site Scripting (XSS). A normal user can steal session cookies of the admin users through notification…








