
 #1

 corvralabs/evilneko
Automated container orchestration tool for Browser-in-the-Browser (BITB) phishing attacks, enabling red teams to scale multi-target infrastructure…
 chrismaddalena/cooper
A Python tool for ingesting HTML and producing HTML source suitable for phishing campaigns.
 dshabani96/cve-2024-21413
Proof-of-concept exploit for Microsoft Outlook RCE (CVE-2024-21413) with SMTP email delivery, malicious RTF attachment generation, and optional…
 fdzdev/cve-2024-50962
Documented Cross-Site Scripting (XSS) vulnerability in Ferozo Webmail v1.1, enabling session hijacking and phishing via insufficient input validation…
 dhananjayasj/cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Proof-of-concept exploit for CVE-2024-21413, a critical Outlook RCE vulnerability that leaks NetNTLMv2 hashes via crafted file:// links, enabling…
 cmadhushanka/wordpress-rce-vapt-cve-2020-25213
Educational cybersecurity project demonstrating exploitation and mitigation of CVE-2020-25213 (WordPress File Manager Plugin RCE). Includes malware…
 1h3ll/cve-2025-50363_bxss_cve
Proof-of-concept for a blind XSS vulnerability in Maid Hiring Management System v1.0, capturing admin session cookies via a crafted application form…
 brmkit/toastnotify-bof
abusing windows toast notifications for fun and user manipulation
 devbuihieu/cve-2025-33053-proof-of-concept
CVE-2025-33053 Proof Of Concept (PoC)
 vlad-a-man/cve-2023-23397
CVE-2023-23397 PoC
 polarisxsec/cve-2024-21413
Educational lab demonstrating CVE-2024-21413 exploitation in Outlook to leak NTLM hashes via malicious UNC links, with custom SMTP/POP3…
 sanupl/cve-2024-34568
In LetterPress plugin <= 1.2.1 is vulnerable to Cookie Stealing Vulnerability. An attacker can able to steal the cookies by injecting the JavaScript…
 security-avs/cve-2020-16270
Proof-of-concept for CVE-2020-16270, an XSS vulnerability in OLIMPOKS under 3.3.39, demonstrating remote injection of malicious JavaScript to steal…
 v35hr4j/cve-2021-24563
The plugin does not prevent HTML files from being uploaded via its form, allowing unauthenticated user to upload a malicious HTML file containing…
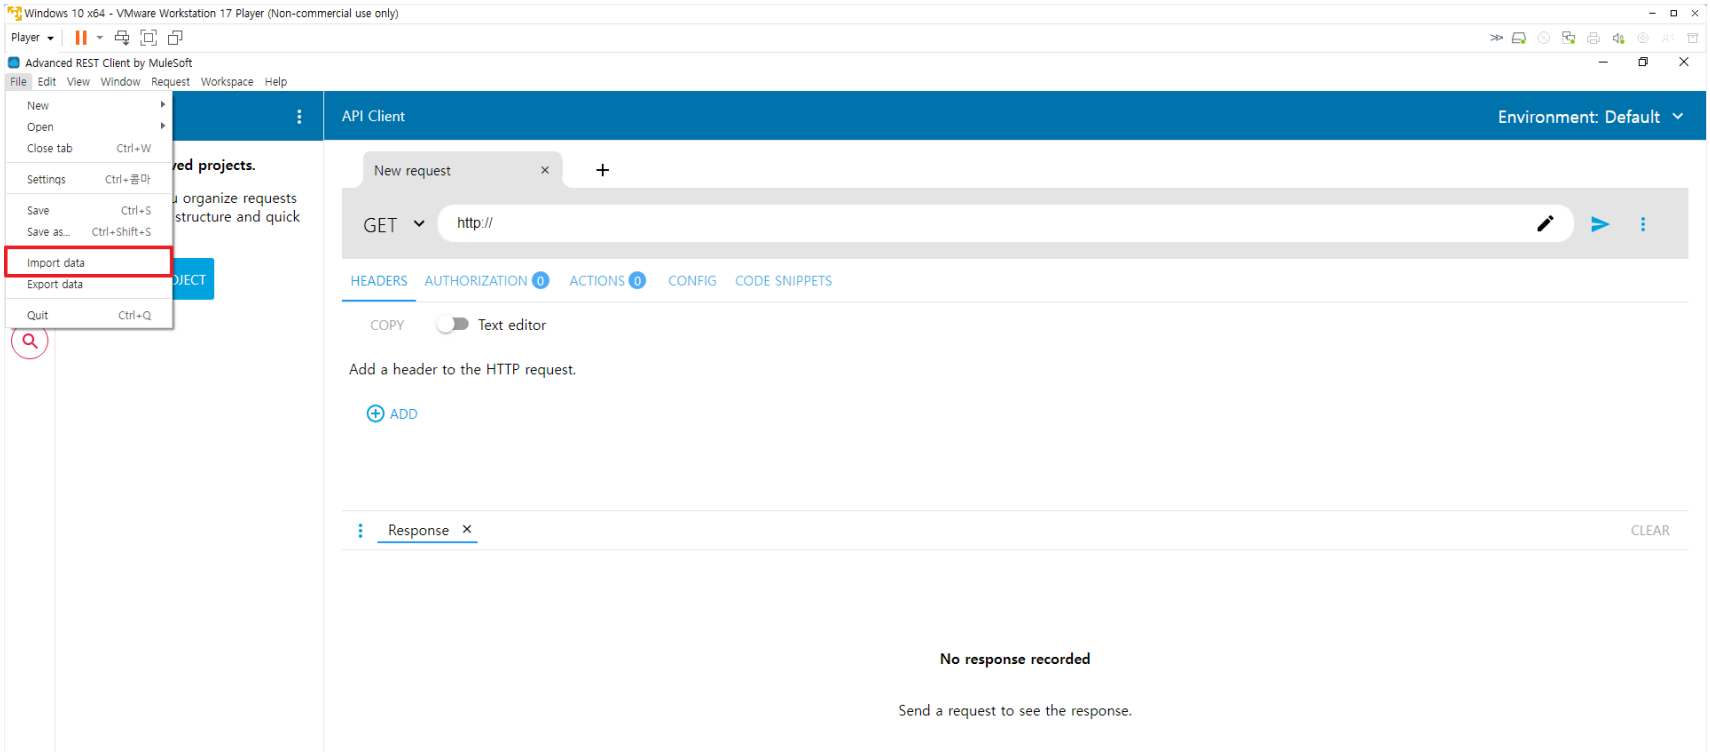 eqstlab/cve-2024-25503
Cross-Site Scripting vulnerability in Advanced REST Client v.17.0.9 exploit
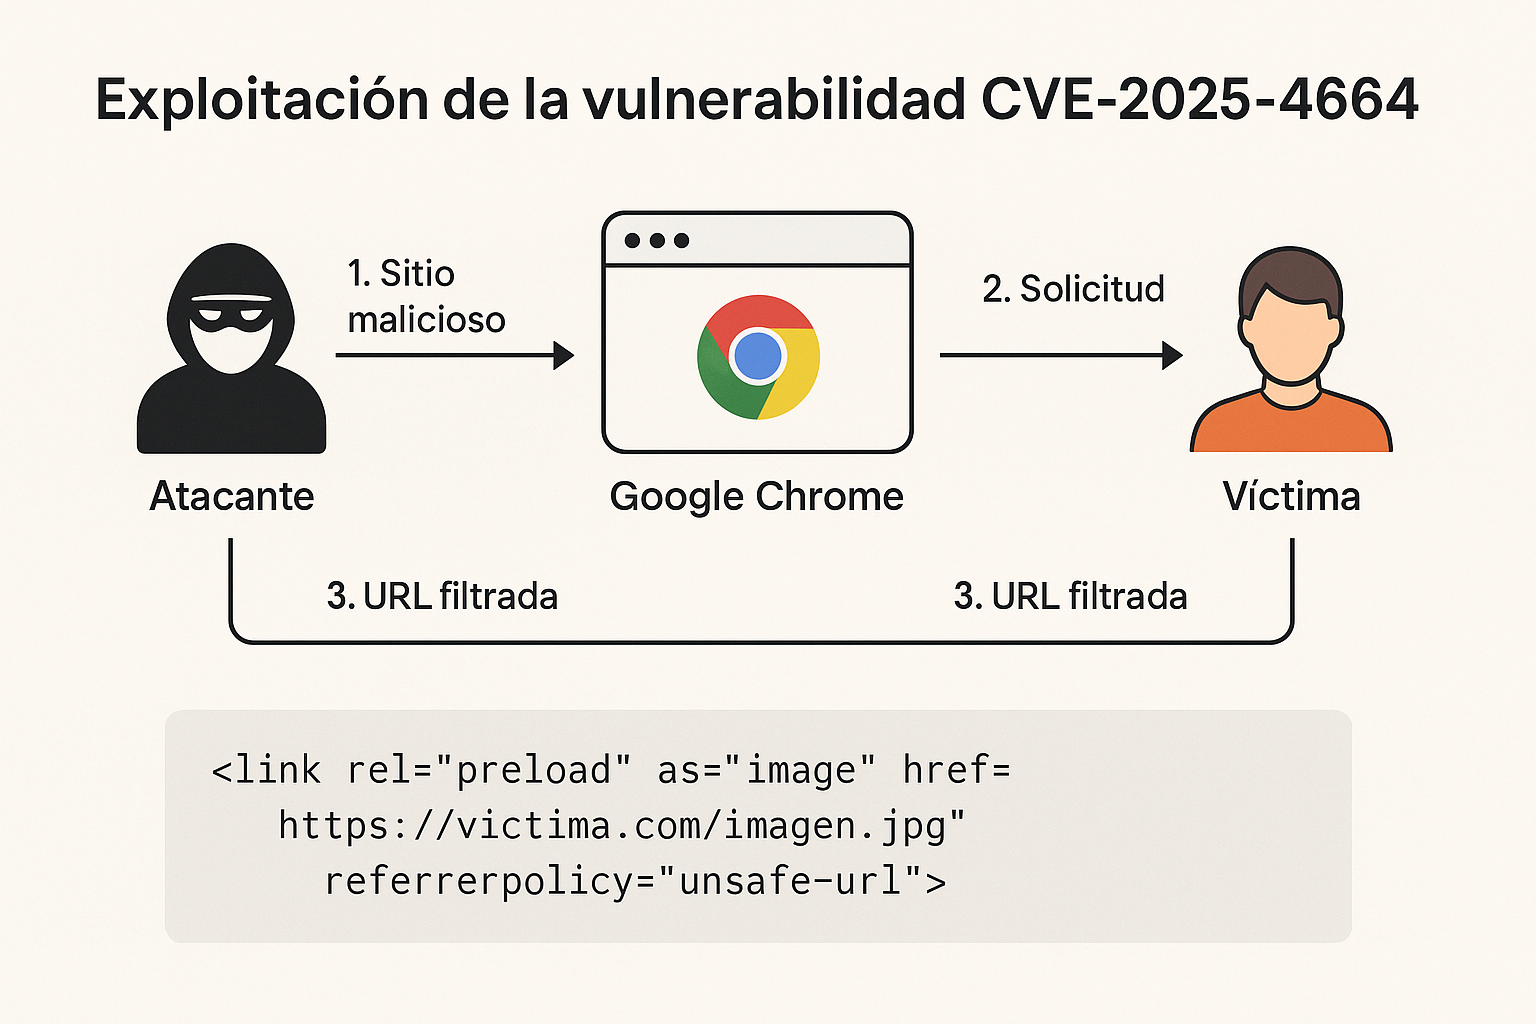 speinador/cve-2025-4664
Educational demo of CVE-2025-4664, a Chrome Loader vulnerability enabling cross-origin data leakage via referrer-policy manipulation. Includes a…









