#1
Tools for maintaining long-term access to compromised systems, even after reboots.
Kitploit recommended
 gianlucaborello/libprocesshider
LD_PRELOAD shared library that hides a Linux process from tools like ps and lsof by intercepting readdir and proc filesystem calls.
 powershellmafia/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
 empireproject/empire
Empire is a PowerShell and Python post-exploitation agent.
 es3n1n/no-defender
A slightly more fun way to disable windows defender + firewall. (through the WSC api)
 mandiant/sharpersist
C# toolkit for establishing and managing Windows persistence via registry keys, scheduled tasks, services, startup folders, KeePass configs, and…
 d4vinci/dr0p1t-framework
A framework that create an advanced stealthy dropper that bypass most AVs and have a lot of tricks
 oddcod3/phantom-evasion
Python antivirus evasion tool
 zerx0r/kage
Kage is Graphical User Interface for Metasploit Meterpreter and Session Handler
 loseys/blackmamba
C2/post-exploitation framework
 nyan-x-cat/lime-rat
LimeRAT | Simple, yet powerful remote administration tool for Windows (RAT)
 luantak/torat
ToRat is a Remote Administation tool written in Go using Tor as a transport mechanism and RPC for communication
 qwqdanchun/dcrat
A simple remote tool in C#.
 xaff-xaff/cronos-rootkit
Cronos is Windows 10/11 x64 ring 0 rootkit. Cronos is able to hide processes, protect and elevate them with token manipulation.
 tiagorlampert/saint
👁️ (s)AINT is a Spyware Generator for Windows systems written in Java. [Discontinued]
 facebookarchive/weasel
DNS covert channel implant for Red Teams.
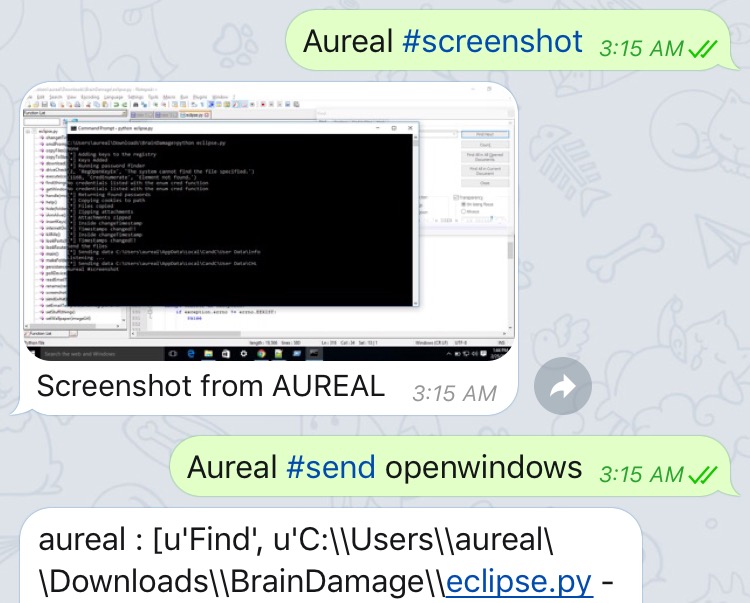 mehulj94/braindamage
Remote administration service which uses twitter as a command and control server
 mvrozanti/rat-via-telegram
Windows Remote Administration Tool via Telegram