
 #1
Tools for maintaining long-term access to compromised systems, even after reboots.
Kitploit recommended

 user696/mrrat
:mouse: This is a cross-platform Python 2.x Remote Access Trojan (RAT)
 mwsrc/schwarze-sonne-rat
SS-RAT (Schwarze-Sonne-Remote-Access-Trojan)
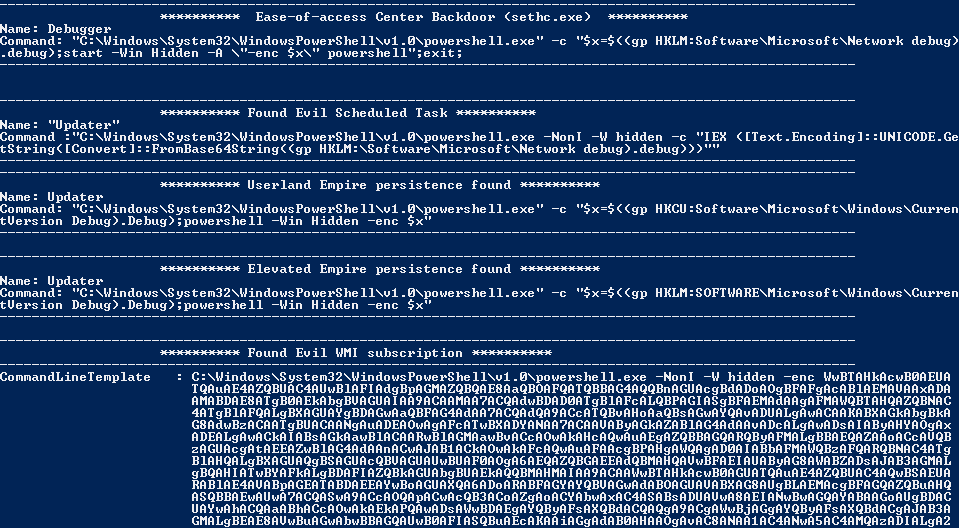 n00py/norknork
Powershell Empire Persistence finder
 egebalci/egesploit
EGESPLOIT is a golang library for malware development
 d4vinci/wormy
some python3 functions to add spreading features to any python backdoor
 malwares/remote-access-trojan
Windows Remote-Access-Trojan
 mwsrc/plasmarat
Remote Access Trojan(RAT), Miner, DDoS

 mwsrc/betterrat
Better Remote Access Trojan
 mwsrc/betterandrorat
Android Remote Access Trojan
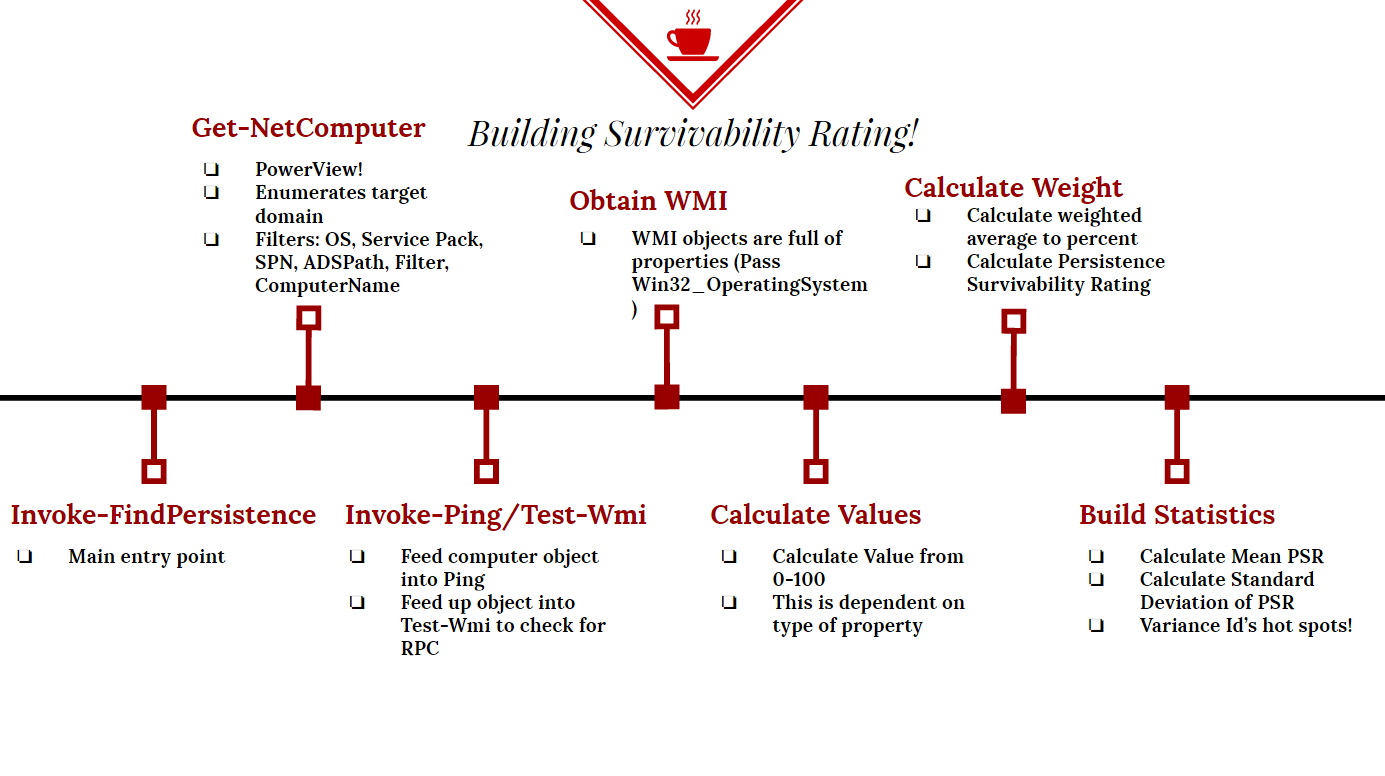 killswitch-gui/persistence-survivability
Powershell Persistence Locator
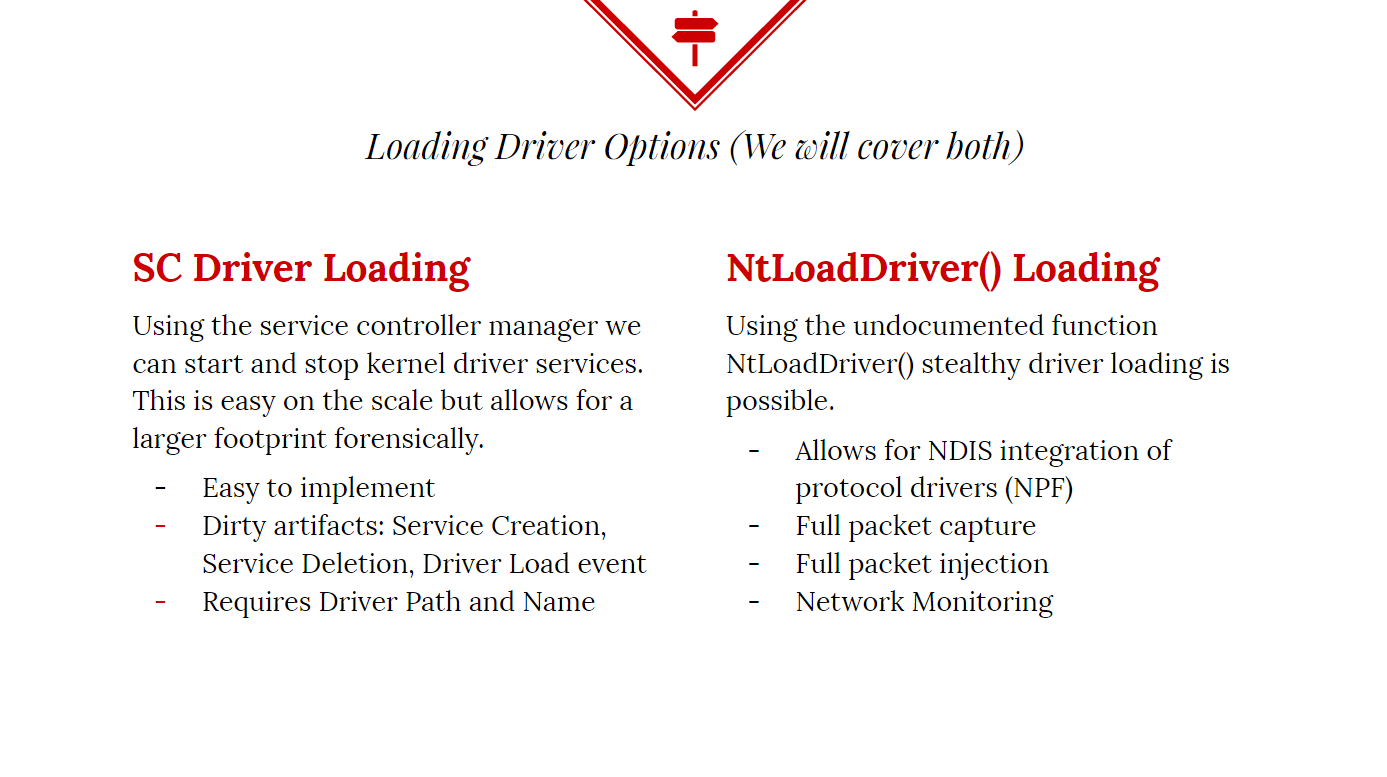 killswitch-gui/hotload-driver
C++
 m00nrise/processhider
Post-exploitation tool for hiding processes from monitoring applications
 sw4mpf0x/powerlurk
Malicious WMI Events using PowerShell
 d4vinci/palsy-virus
Python virus that will make your pc paralyzed once it opened :D
 5alt/zerorat
ZeroRAT是一款windows上的一句话远控
 catatonicprime/tospovirus
A WiFi Pineapple infecting worm.
 malwaretech/fakembr
TDL4 style rootkit to spoof read/write requests to master boot record








