
 #1
Tools for collecting and analyzing publicly available information from online sources.
Kitploit recommended
 hackinglz/saas_enum
Command-line tool for discovering SaaS platforms a company uses via DNS enumeration

 jul10l1r4/getrails
Get trails lib: Get all urls indexed of target
 gmh5225/logineo-scraper
Quick script to scrape personal information from Logineo instances
 cyberbibs/soc274---palo-alto-networks-pan-os-command-injection-vulnerability-exploitation-cve-2024-3400-
Step-by-step SOC analyst walkthrough for investigating and remediating CVE-2024-3400 (PAN-OS command injection). Covers detection, log analysis,…
 drskelebones/go-sherlock
High-performance username search engine written in Go. Scans hundreds of social networks and websites to discover accounts associated with a given…
 shadowguardai/ti-a-ti-cveexploitchecker
Determines if public exploits are available for a given CVE. Uses APIs like exploit-db or NVD to ide
 gmh5225/disclosure-check
Tool to identify the best mechanisms for privately disclosing a security vulnerability for a package/project.
 sh1katagana1/threatintelligence
A repo for all things cyber threat intel
 spiralbl0ck/cve-2024-31320-
Get GeoLocation of Exploited Device using CVE-2024-31320& bluetooth
 randomrobbiebf/elastic-search-email-extractor
Searches Elasticsearch database for email addresses
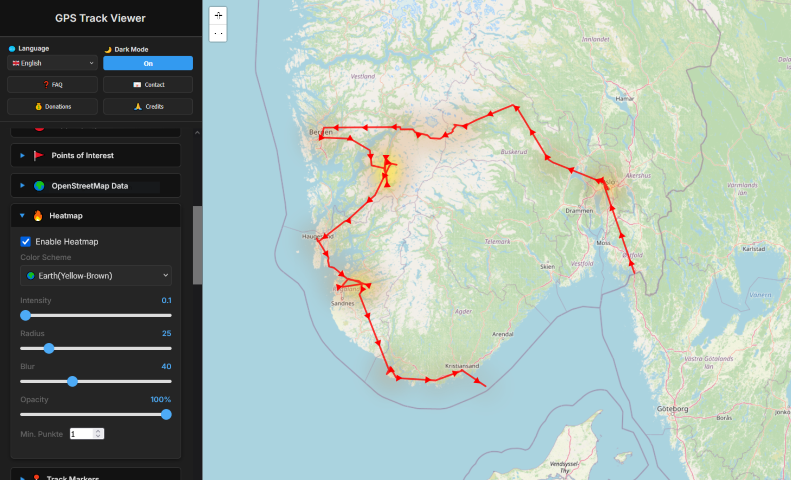 lukawe/localexifgeomap
A powerful, privacy-focused, browser-based tool to visualize and analyze GPS data from your photos. Simply drag and drop images to generate…
 sunny-kathuria/exploit_cve-2022-26134
CVE-2022-26134, an OGNL injection vulnerability exists that would allow an unauthenticated attacker to execute arbitrary code on a Confluence Server…
 mohwahyudi/cve-2021-41773
Python script that uses Shodan to discover Apache HTTP Server 2.4.49 instances vulnerable to CVE-2021-41773 path traversal and file disclosure.
 artemcyberlab/project-ntlm-hash-capture-and-phishing-email-exploitation-for-cve-2024-21413
Demonstrates capturing NTLM hashes via Responder and executing phishing emails exploiting CVE-2024-21413 to compromise systems.
 elzerjp/nuclei-ciscorv320dump-cve-2019-1653
Automated Nuclei template and Shodan workflow to detect and exploit Cisco router configuration exposure (CVE-2019-1653) for security auditing.
 dream434/cve-2017-5487
Exploit for CVE-2017-5487 to enumerate WordPress user accounts via the REST API, extracting sensitive information from vulnerable 4.7 installations.
 anldori/cve-2021-41773-scanner
CVE-2021-41773 Shodan scanner
 tadash10/detect-cve-2024-0762
Detecting vulnerabilities like CVE-2024-0762, particularly in UEFI firmware, is quite challenging due to the low-level nature








