#1
Tools for collecting and analyzing publicly available information from online sources.
Kitploit recommended
 rival420/cve-2020-14181
POC For CVE-2020-1481 - Jira Username Enumerator/Validator
 tonejito/check_cve-2019-3462
Check @Debian and @Ubuntu #GNU / #Linux for CVE-2019-3462 in APT
 p4b3l1t0/confusploit
This is a python script that can be used with Shodan CLI to mass hunting Confluence Servers vulnerable to CVE-2022-26134
 9lyph/cve-2021-45901
Proof-of-concept Python script that enumerates valid ServiceNow user accounts by exploiting the password-reset response discrepancy in CVE-2021-45901.
 halencarjunior/cve-2023-36845
Scanner for CVE-2023-36845 with Shodan and Censys integration for automated host discovery and exploitation of Juniper devices.
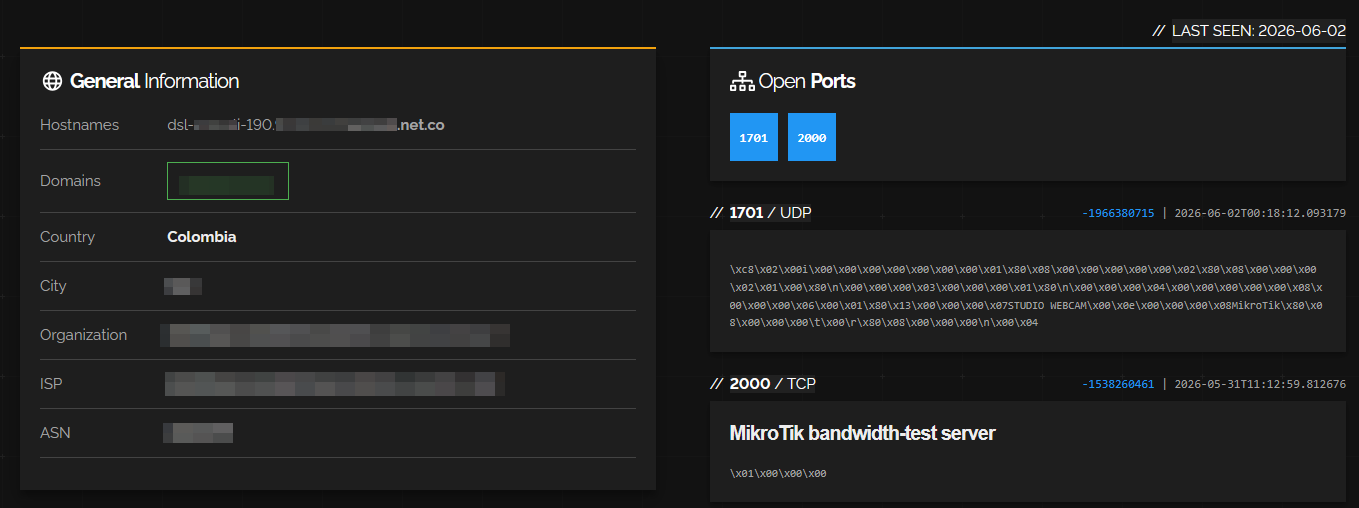 jonathaninfinity01/soc-l1-osint-investigation-mikrotik-cve-2018-1156
L1 SOC Analysis: OSINT detection and risk validation of publicly exposed MikroTik RouterOS vulnerable to RCE | Tools: Shodan, NIST NVD
 mad3e7cat/cve-2023-5612
Nmap NSE to check for CVE-2023-5612
 jul10l1r4/getrails
Get trails lib: Get all urls indexed of target
 kahunalu/pwnbin
Python Pastebin Webcrawler that returns list of public pastebins containing keywords
 hazcod/claudleak
Hunt for AI coding artifacts containing secrets.
 besioo/hackerone
Brute-force scraper for HackerOne disclosed reports via their public API, collecting report IDs, links, titles, and states for security research and…
 0x4d31/cve-2024-6387_hassh
HASSH fingerprints for identifying OpenSSH servers potentially vulnerable to CVE-2024-6387 (regreSSHion).
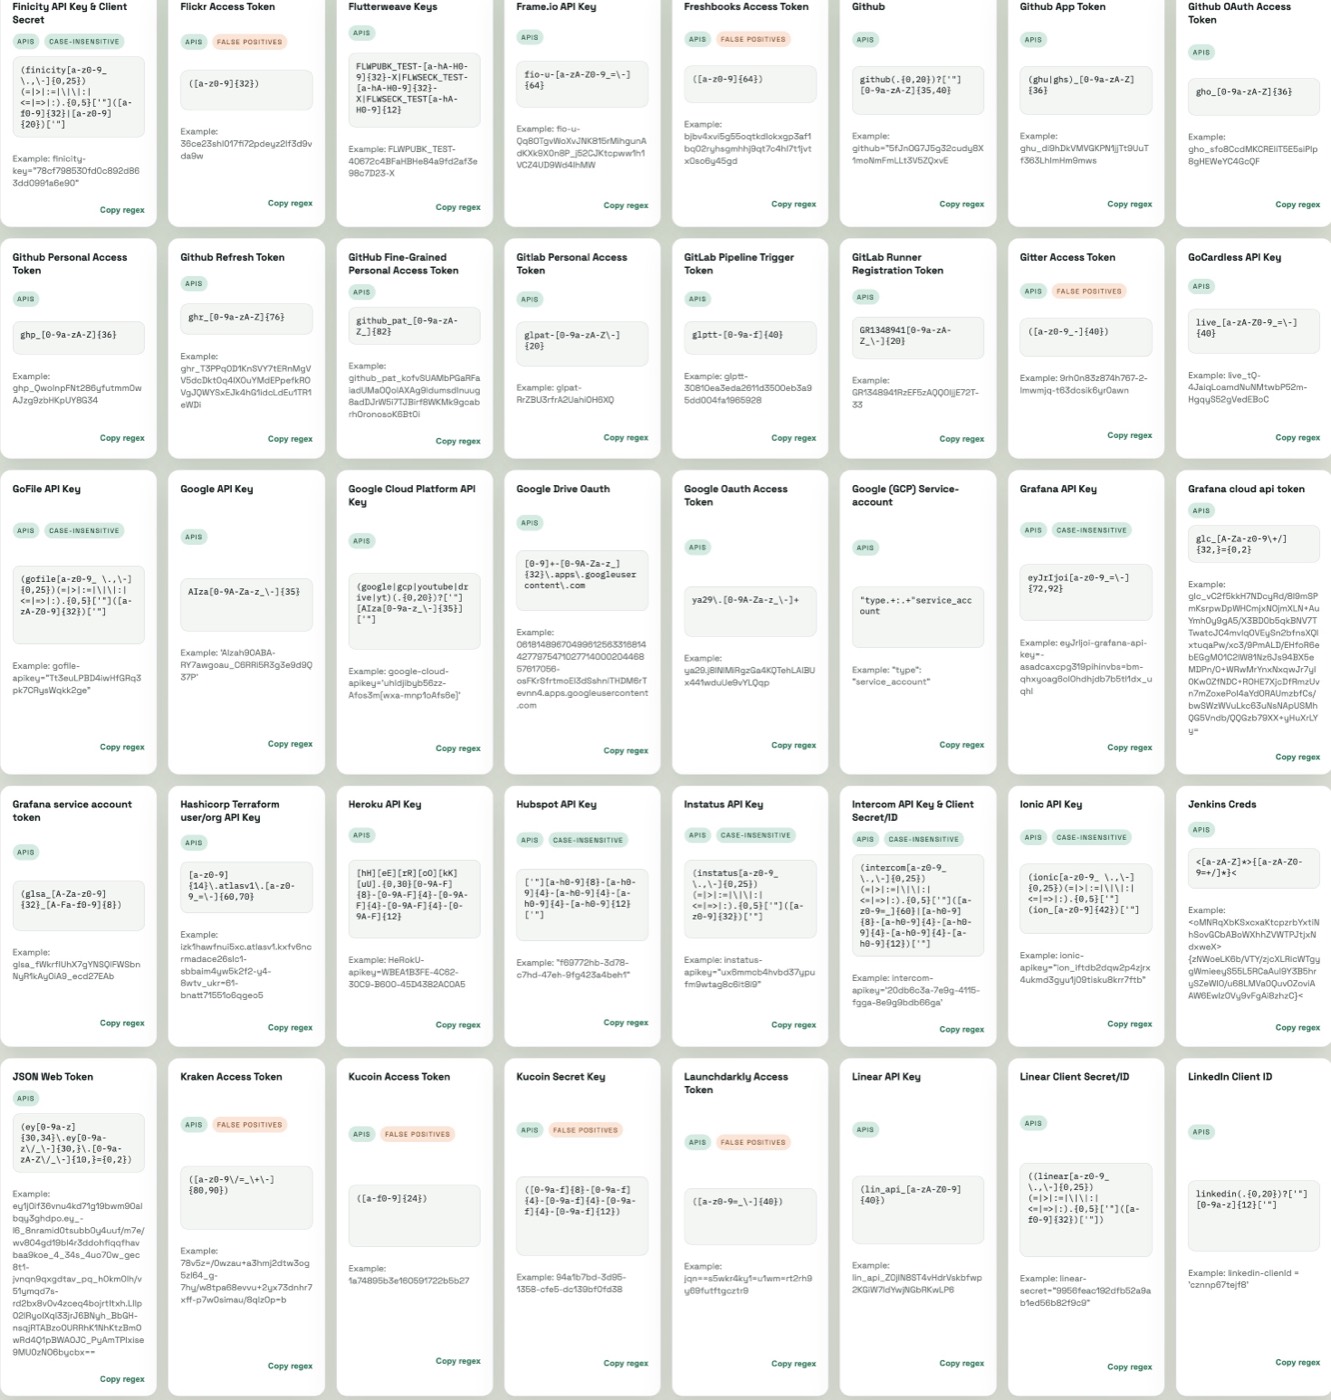 adversis/screenscrub
Find credentials in screenshots, save them to your secret manager, and irreversibly redact them from the image — local, offline, OCR-based.
 ricardojoserf/cve-2021-31159
Zoho ManageEngine ServiceDesk Plus MSP - Active Directory User Enumeration (CVE-2021-31159) - https://ricardojoserf.github.io/CVE-2021-31159/
 techinsightspro/shodanfortios
Search vulnerable FortiOS devices via Shodan (CVE-2023-27997)
 zhazhalove/osquery_cve-2024-23443
Osqery extension HP BIOS WMI
 anldori/cve-2021-41773-scanner
CVE-2021-41773 Shodan scanner