
 #1
Tools for assessing, testing, and exploiting mobile applications and devices (Android, iOS).
Kitploit recommended

 lyravoid/kernelpatch
Patches and hooks the Linux kernel using only a stripped kernel image, extracting symbols and injecting code for inline and syscall hooking on arm64.
 webldix/cve-2024-31317-poc-deployer
Automated deployment tool for CVE-2024-31317 PoC on Android 9-13, enabling privilege escalation via Zygote injection and reverse shell execution.
 cybersecsi/robodroid
Manage Android machines with pre-defined behaviors for Cyber Range environments.
 yijiacloud/ghostlock-cve-2026-43499-4.19-k40
CVE-2026-43499 (GhostLock) rtmutex remove_waiter() UAF local-root PoC adapted for Qualcomm Android 4.19 kernels (Redmi K40 / Snapdragon 870 class),…
 hadesscs/artemis
Extracts and investigates infrastructure (IPs, domains) from APK files, with manifest parsing and WHOIS lookup for mobile application reconnaissance.
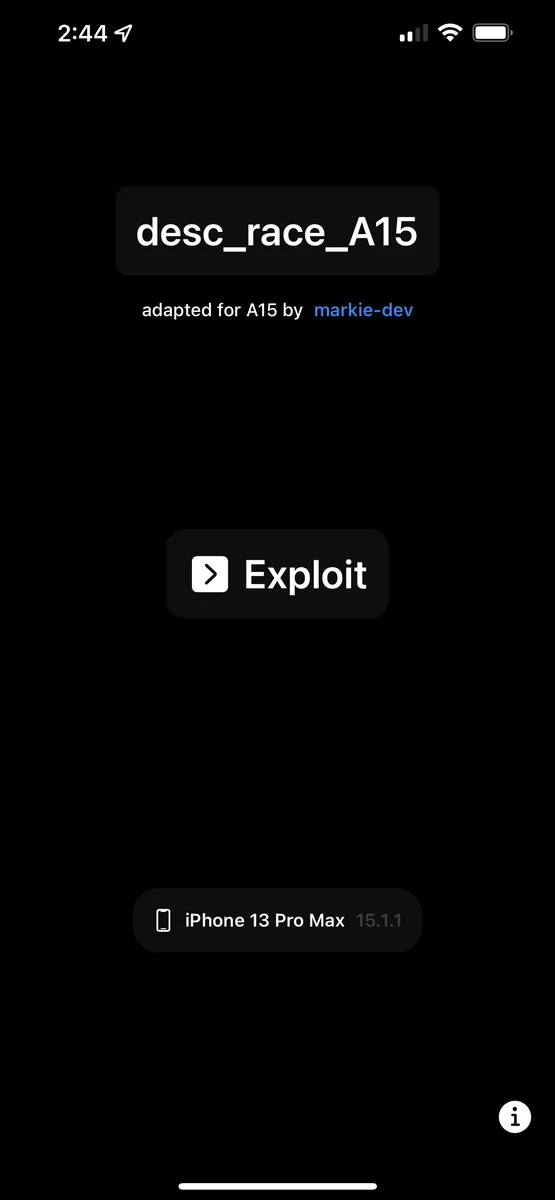 markie-dev/desc_race_a15
CVE-2021-30955 iOS 15.1.1 POC for 6GB RAM devices (A14-A15)
 ashujaiswal109/cve-2019-11932
Simple POC for exploiting WhatsApp double-free bug in DDGifSlurp in decoding.c in libpl_droidsonroids_gif
 alfa100001/-cve-2017-0785-blueborne-poc
CVE-2017-0785 BlueBorne PoC
 blacksnufkin/geckodroid
Android client for Adaptix C2 framework enabling remote agent management, interactive command shells, listener control, payload generation, and…
 valbrux/cve-2019-11932-supportapp
This native code file aims to be complementary to the published Whatsapp GIF RCE exploit by Awakened , by calculating the system() function address…
 owasp/mas-website
The OWASP Mobile Application Security Project website is the central hub for industry-leading standards, guides, and resources—helping developers and…
 quyicheng03-boop/xiaomi15-dada-cve-2026-64560
Device-bound CVE-2026-64560 adaptation for Xiaomi 15 dada OS4.0.0.8
 people-11/cve-2025-10184_poc
Android APK proof-of-concept for CVE-2025-10184, demonstrating SMS read permission bypass in OPPO/OnePlus telephony providers. Includes source code,…
 xtiankisutsa/twiga
A tool that enumerates Android devices for information useful in understanding its internals and for exploit development. It supports android 4.2 to…

 theshinigami/mafrida
A Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…
 cellebrite-labs/pplorer
IDA plugin that resolves PPL calls to the actual underlying PPL function.
 dimitrifourny/cve-2019-2215
Android privilege escalation via an use-after-free in binder.c








