Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Log Analysis — Page 34 | Kitploit
Categories

Log Analysis

Log parsing, SIEM, centralized logging, forensic timeline, and security event correlation tools.

Kitploit recommended
Top tools

10 selected
wazuh preview#1

wazuh

GitHubwazuh/wazuh
16.5k16h 27m ago
graylog2-server preview#2

graylog2-server

GitHubgraylog2/graylog2-server
8.2k7h 7m ago
loki preview#3

loki

GitHubgrafana/loki
29.0k5h 20m ago
osquery preview#7

osquery

GitHubosquery/osquery
23.4k13h 45m ago
securityonion preview#8

securityonion

GitHubsecurity-onion-solutions/securityonion
4.9k1 month ago
zeek preview#9

zeek

GitHubzeek/zeek
7.8k16h 39m ago
suricata preview#10

suricata

GitHuboisf/suricata
6.5k5 days ago
sigma preview#11

sigma

GitHubsigmahq/sigma
10.9k1 day ago
detection-rules preview#12

detection-rules

GitHubelastic/detection-rules
2.7k1 day ago
logparser preview#13

logparser

GitHublogpai/logparser
2.0k1 year ago
NewestRelevanceMost popularRecently updated
684 results
etl-parser preview

etl-parser

GitHubairbus-cert/etl-parser

Event Trace Log file parser in pure Python
reverse-engineeringforensicsdigital-forensics+1
1565 months ago
laurel preview

laurel

GitHubthreathunters-io/laurel

Transform Linux Audit logs for SIEM usage

defensive-toolslog-analysis
8512 days ago
Ox4Shell preview

Ox4Shell

GitHubox-eye/ox4shell

Deobfuscate Log4Shell payloads with ease.

vulnerability-analysislog-analysis
1674 years ago
matano preview

matano

GitHubmatanolabs/matano

Open source security data lake for threat hunting, detection & response, and cybersecurity analytics at petabyte scale on AWS
cloud-securitythreat-intelligenceincident-response+1
1.7k1 year ago
latma preview

latma

GitHubsilverfort-open-source/latma

Collects and analyzes AD and Azure AD authentication logs to detect lateral movement attacks using graph-based anomaly detection, visualizing…
lateral-movementinformation-gatheringpenetration-testing+5
803 years ago
Get-AppLockerEventlog preview

Get-AppLockerEventlog

GitHubromaissaadjailia/get-applockereventlog

This is a repo for fetching Applocker event log by parsing the win-event log

forensicsthreat-intelligenceincident-response+1
294 years ago
aftermath preview

aftermath

GitHubjamf/aftermath

Swift-based macOS incident response framework for collecting and analyzing host artifacts, including filesystem timestamps, browser data, unified…
memory-forensicsforensicsdigital-forensics+3
5941 year ago
winevt_logs_analysis preview

winevt_logs_analysis

GitHubgeorgi-i/winevt_logs_analysis

Parses Windows .evtx logs to identify remote connections and public IPs by analyzing EventIDs related to remote logins and sessions.

forensicsdigital-forensicslog-analysis
243 years ago
ThreatHound preview

ThreatHound

GitHubmazx0p/threathound

Automated threat hunting and incident response tool for Windows Event Logs with Sigma rule integration, real-time detection, and forensic artifact…
digital-forensicsthreat-intelligenceincident-response+1
1602 years ago
CVE-Vulnerability-Information-Downloader preview

CVE-Vulnerability-Information-Downloader

GitHubtrinitor/cve-vulnerability-information-downloader

Downloads and aggregates CVSS, EPSS, and CISA known exploited vulnerability data into unified JSON/CSV files and a SQLite database. Enriches…

vulnerability-scannersvulnerability-analysisutilities-frameworks+2
1433 years ago
IPBan preview

IPBan

GitHubdigitalruby/ipban

Automated IP ban service that detects failed login attempts from event logs and files, blocking attackers on Windows and Linux via firewall…
defensive-toolsnetwork-securityintrusion-detection+1
2.2k3 months ago
MacOSThreatTrack preview

MacOSThreatTrack

GitHubab2pentest/macosthreattrack

Bash tool used for proactive detection of malicious activity on macOS systems.
information-gatheringdigital-forensicsincident-response+1
391 year ago
reportly preview

reportly

GitHubsap8899/reportly

AzureAD/EntraID user activity reporter for blue teams. Input a suspicious user and time frame to receive a detailed report of user info, actions, and…
information-gatheringcloud-securityidentity-access-management+2
963 years ago
OSSEM preview

OSSEM

GitHubotrf/ossem

Community-driven project for documenting, standardizing, and modeling security event logs to improve detection analytics and data normalization…
threat-intelligenceeducationcurated-resources+1
1.3k3 years ago
LinuxCatScale preview

LinuxCatScale

GitHubwithsecurelabs/linuxcatscale

Incident Response collection and processing scripts with automated reporting scripts
scripting-automationforensicsdigital-forensics+2
3382 years ago
ssl-certificate-expiry-date-checker preview

ssl-certificate-expiry-date-checker

GitHubpassword123456/ssl-certificate-expiry-date-checker

Scans SSL/TLS certificates for expiry dates, issuer details, and OCSP status. Sends notifications via webhook, Telegram, or Slack. Supports proxy per…
vulnerability-scannersconfiguration-auditingnetwork-security+2
123 years ago
dnsmonster preview

dnsmonster

GitHubfenkohq/dnsmonster

Passive DNS Capture and Monitoring Toolkit
packet-sniffing-analysisinformation-gatheringnetwork-security+3
3601 day ago
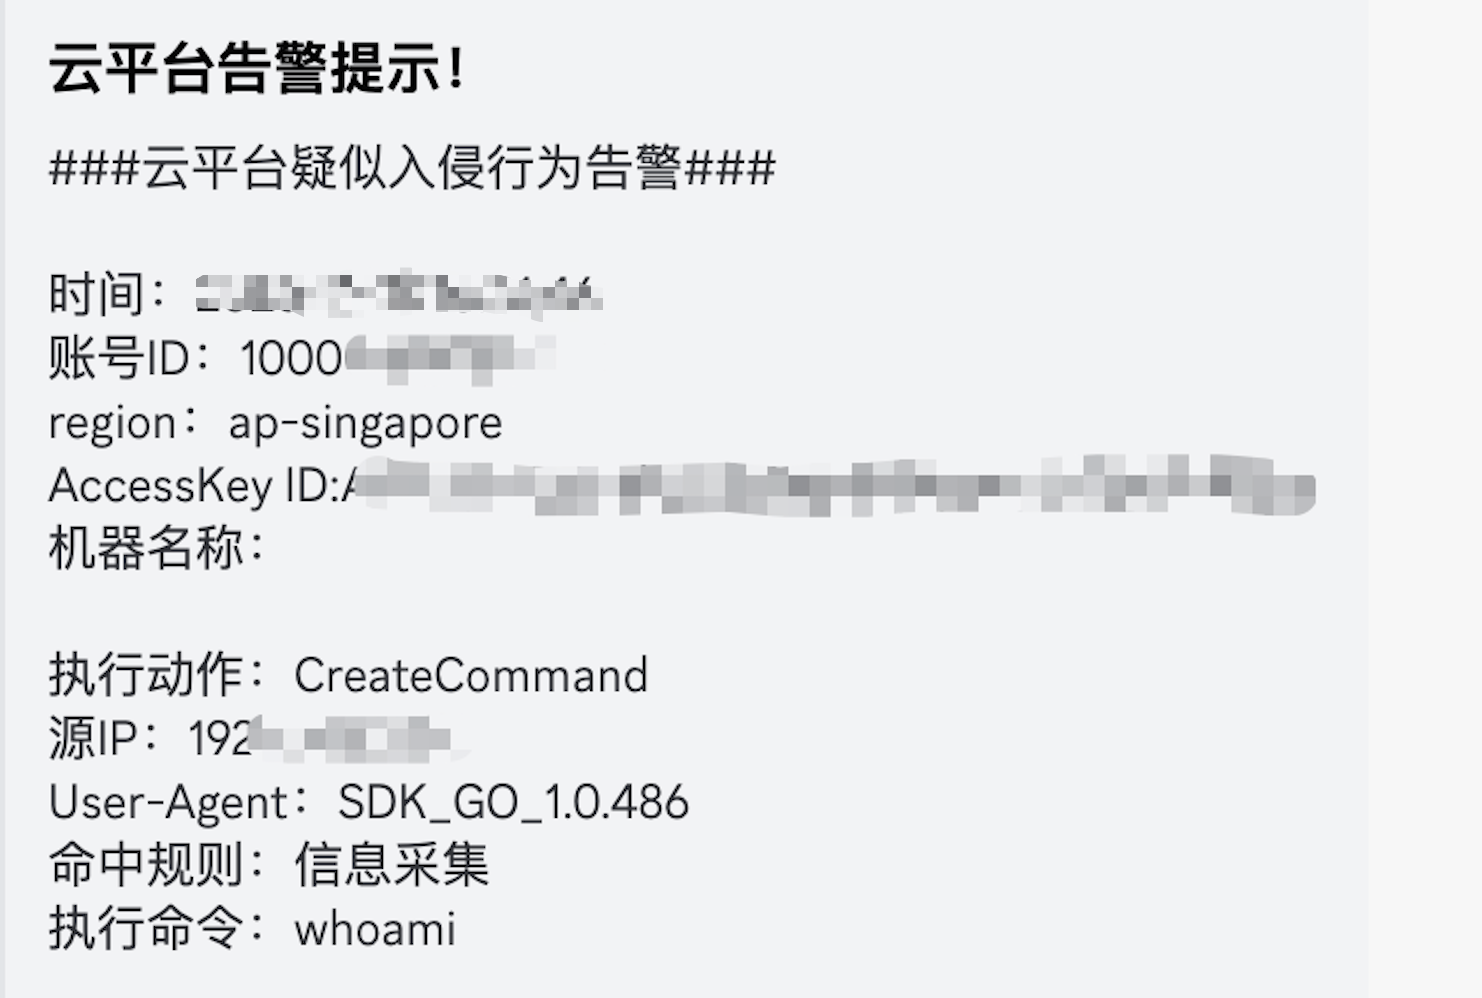
cloud-audit preview

cloud-audit

GitHubal0ne/cloud-audit

Automated cloud security auditing tool that detects AK/SK credential misuse by periodically auditing cloud platform logs using anomaly detection,…


cloud-securitythreat-intelligenceincident-response+2
442 years ago
Previous1…333435…38Next